
vulnsig-py
Render CVSS vulnerability vectors as expressive SVG glyphs. Each glyph encodes all base metrics visually with shape, color, rings, and texture, so vulnerabilities are recognizable at a glance.
Supports CVSS 4.0, 3.1, 3.0, and 2.0.
Visit vulnsig.io to interactively explore CVSS glyph configurations and recent or well-known CVE vector glyphs.
Install
pip install vulnsig
Usage
from vulnsig import render_glyph

svg = render_glyph("CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:H/SI:H/SA:H")

# override the score (e.g. if you already have it)
svg = render_glyph("CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H", score=10.0)

# control rendered size in pixels (default 120)
svg = render_glyph("CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N", size=64)
render_glyph returns an SVG string ready to embed in HTML or write to a file.
Examples
CVSS 4.0
| Glyph | Name | Vector | Score |
|---|---|---|---|
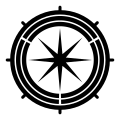 |
Log4Shell | AV:N AC:L AT:N PR:N UI:N VC:H VI:H VA:H SC:H SI:H SA:H |
10.0 |
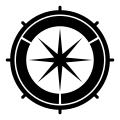 |
EternalBlue | AV:N AC:L AT:N PR:N UI:N VC:H VI:H VA:H SC:N SI:N SA:N |
9.3 |
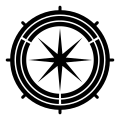 |
Heartbleed | AV:N AC:L AT:N PR:N UI:N VC:H VI:N VA:N SC:L SI:N SA:N |
8.7 |
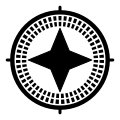 |
Spectre | AV:L AC:H AT:P PR:L UI:N VC:H VI:N VA:N SC:H SI:N SA:N |
5.6 |
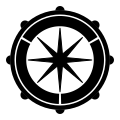 |
XSS Stored | AV:N AC:L AT:N PR:L UI:P VC:L VI:L VA:N SC:N SI:N SA:N |
5.1 |
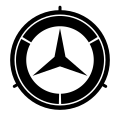 |
USB Drop | AV:P AC:L AT:N PR:N UI:N VC:H VI:H VA:H SC:N SI:N SA:N |
7.3 |
CVSS 3.x
| Glyph | Name | Vector | Score |
|---|---|---|---|
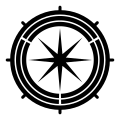 |
Log4Shell | AV:N AC:L PR:N UI:N S:C C:H I:H A:H |
10.0 |
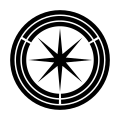 |
XSS Reflected | AV:N AC:L PR:N UI:R S:C C:L I:L A:N |
6.1 |
Visual encoding
Each metric maps to a distinct visual channel:
| Metric | Channel |
|---|---|
| Score | Hue — yellow (low) → orange → dark red (high) |
| AV | Star points — N=8, A=6, L=4, P=3 |
| AC | Star pointiness — L=sharp, H=blunt |
| AT | Ring segmentation — N=solid, P=cut pattern |
| PR | Star outline — N=none, L=thin, H=thick |
| UI | Perimeter — N=spikes, P=bumps, A=clean |
| VC/VI/VA | Inner ring brightness per sector |
| SC/SI/SA | Outer ring band (split when any > 0) |
Requirements
Python 3.10+
What Is New in VulnSig
2.0.0
Support for CVSS 2.0.
1.3.0
Added rendering of Exploit Maturity.
Improved rendering of PR.
1.2.0
Improved glyph rendering over diverse backgrounds.
Extension to the public interface.
1 maintainer

Metadata
1 maintainer
Release files for vulnsig 2.0.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| vulnsig-2.0.0.tar.gz | 12.8 kB | Without provenance | Details for vulnsig-2.0.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| vulnsig-2.0.0-py3-none-any.whl | Python 3 | none | any | Details for vulnsig-2.0.0-py3-none-any.whl |
Total release size: 23.3 kB
Release files / vulnsig-2.0.0.tar.gz
| Download URL | vulnsig-2.0.0.tar.gz |
|---|---|
| Size | 12.8 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
e4ec3513292f2596f32a9048284776d6d9db95acd6870ff6c0144341d391431a
|
|
BLAKE2b-256 checksum How to use checksums |
0be5a00086c770ba718c460371655f16e75b97cef810a0a9b5a3bbe43d6a6bb4
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Release files / vulnsig-2.0.0-py3-none-any.whl
| Download URL | vulnsig-2.0.0-py3-none-any.whl |
|---|---|
| Size | 10.4 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
690396048da1b020c01be0dd1158e45986ae9716fc3ef2227246f9b896a81131
|
|
BLAKE2b-256 checksum How to use checksums |
0edad9e04edca2ee340a2e89792f2132cf188b1a1ca10be403b283662ea7bb55
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Security for vulnsig 2.0.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














