
Wagtail Unsplash 


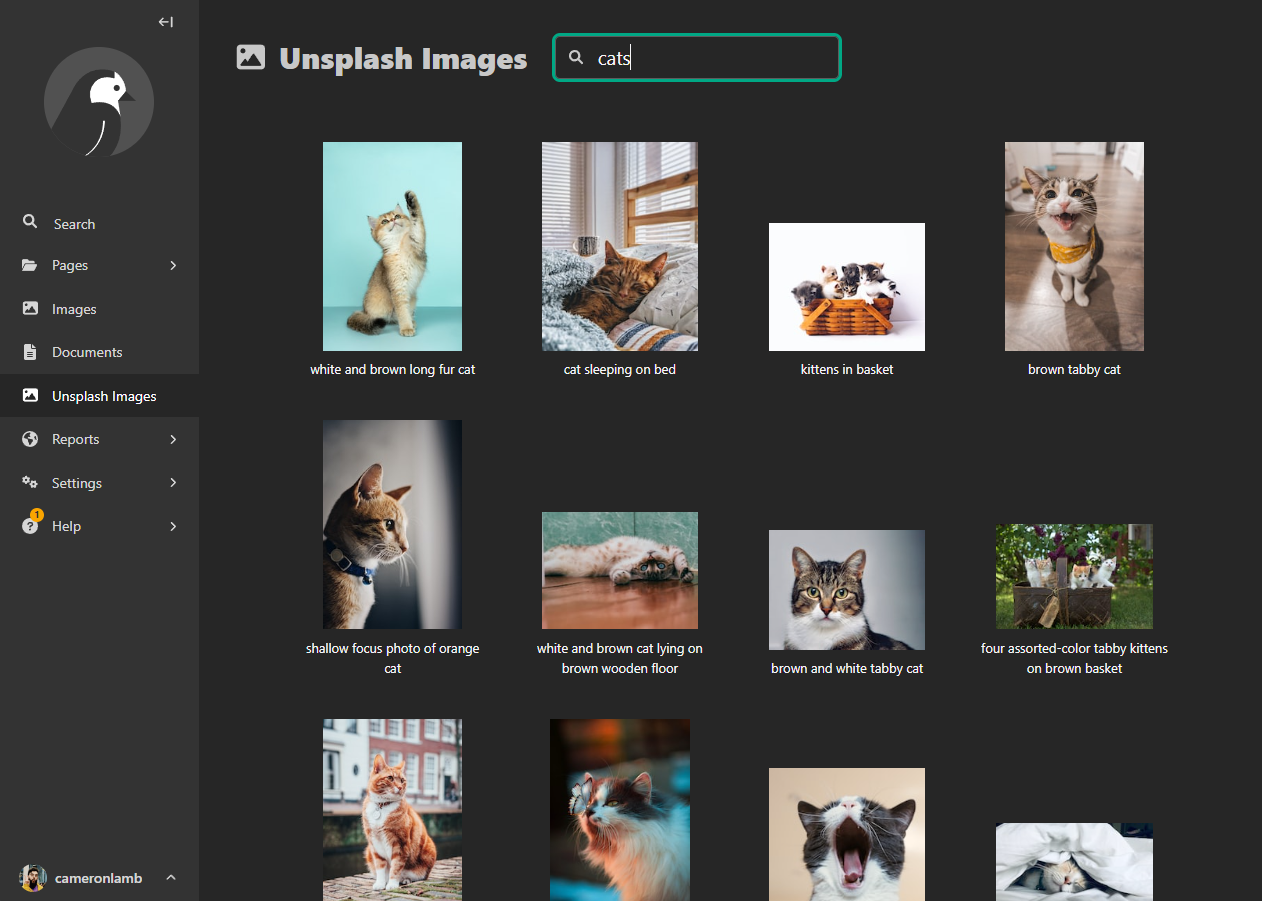
Search for Unsplash images and upload to the Wagtail image library.
This package uses the python-unsplash API wrapper
- Github repository: https://github.com/mintyPT/wagtail-unsplash/
- Documentation https://mintyPT.github.io/wagtail-unsplash/
Getting started
Install using pip:
pip install wagtail-unsplashed
After installing the package, add wagtail_unsplashed to installed apps in your settings file:
# settings.py

INSTALLED_APPS = [
    ...
    'wagtail_unsplashed',
    ...
]
and add the API credentials:
# settings.py
WAGTAIL_UNSPLASHED = {
    "CLIENT_ID": "",
    "CLIENT_SECRET": ""
}
You can get the needed information by creating an application at https://unsplash.com/developers
Getting started (development)
Pull the repo
git clone git@github.com:mintyPT/wagtail-unsplash.git
Set Up Your Development Environment
Then, install the environment and the pre-commit hooks with
make install
This will also generate your uv.lock file
Run the pre-commit hooks
Initially, the CI/CD pipeline might be failing due to formatting issues. To resolve those run:
uv run pre-commit run -a
After pushing
You are now ready to start development on your project! The CI/CD pipeline will be triggered when you open a pull request, merge to main, or when you create a new release.
To finalize the set-up for publishing to PyPI, see here. For activating the automatic documentation with MkDocs, see here. To enable the code coverage reports, see here.
Releasing a new version
- Create an API Token on PyPI.
- Add the API Token to your projects secrets with the name
PYPI_TOKENby visiting this page. - Create a new release on Github.
- Create a new tag in the form
*.*.*.
For more details, see here.
Repository initiated with fpgmaas/cookiecutter-uv.
1 maintainer

Metadata
1 maintainer
Release files for wagtail-unsplashed 1.0.11
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| wagtail_unsplashed-1.0.11.tar.gz | 9.5 kB | Without provenance | Details for wagtail_unsplashed-1.0.11.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| wagtail_unsplashed-1.0.11-py3-none-any.whl | Python 3 | none | any | Details for wagtail_unsplashed-1.0.11-py3-none-any.whl |
Total release size: 18.5 kB
Release files / wagtail_unsplashed-1.0.11.tar.gz
| Download URL | wagtail_unsplashed-1.0.11.tar.gz |
|---|---|
| Size | 9.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
5d816774e97298de83ba351c082321bfde22e053020c787e2e696994e135f7a9
|
|
BLAKE2b-256 checksum How to use checksums |
d9eb71275c8e7d5e430c203e878e3d6f142f9f88804309b1347d64fa7ae64ab2
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/6.0.1 CPython/3.12.7
|
Release files / wagtail_unsplashed-1.0.11-py3-none-any.whl
| Download URL | wagtail_unsplashed-1.0.11-py3-none-any.whl |
|---|---|
| Size | 9.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
85d9babf765621924b13ac1cf38a8b5e2fdc9c4b23ffc149143f162458b2fd65
|
|
BLAKE2b-256 checksum How to use checksums |
3aa206468131becf50bce9225c88472a52011b1d17b45ed329d8b98a7464f6cf
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/6.0.1 CPython/3.12.7
|
Security for wagtail-unsplashed 1.0.11
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














