
wazuhscatune
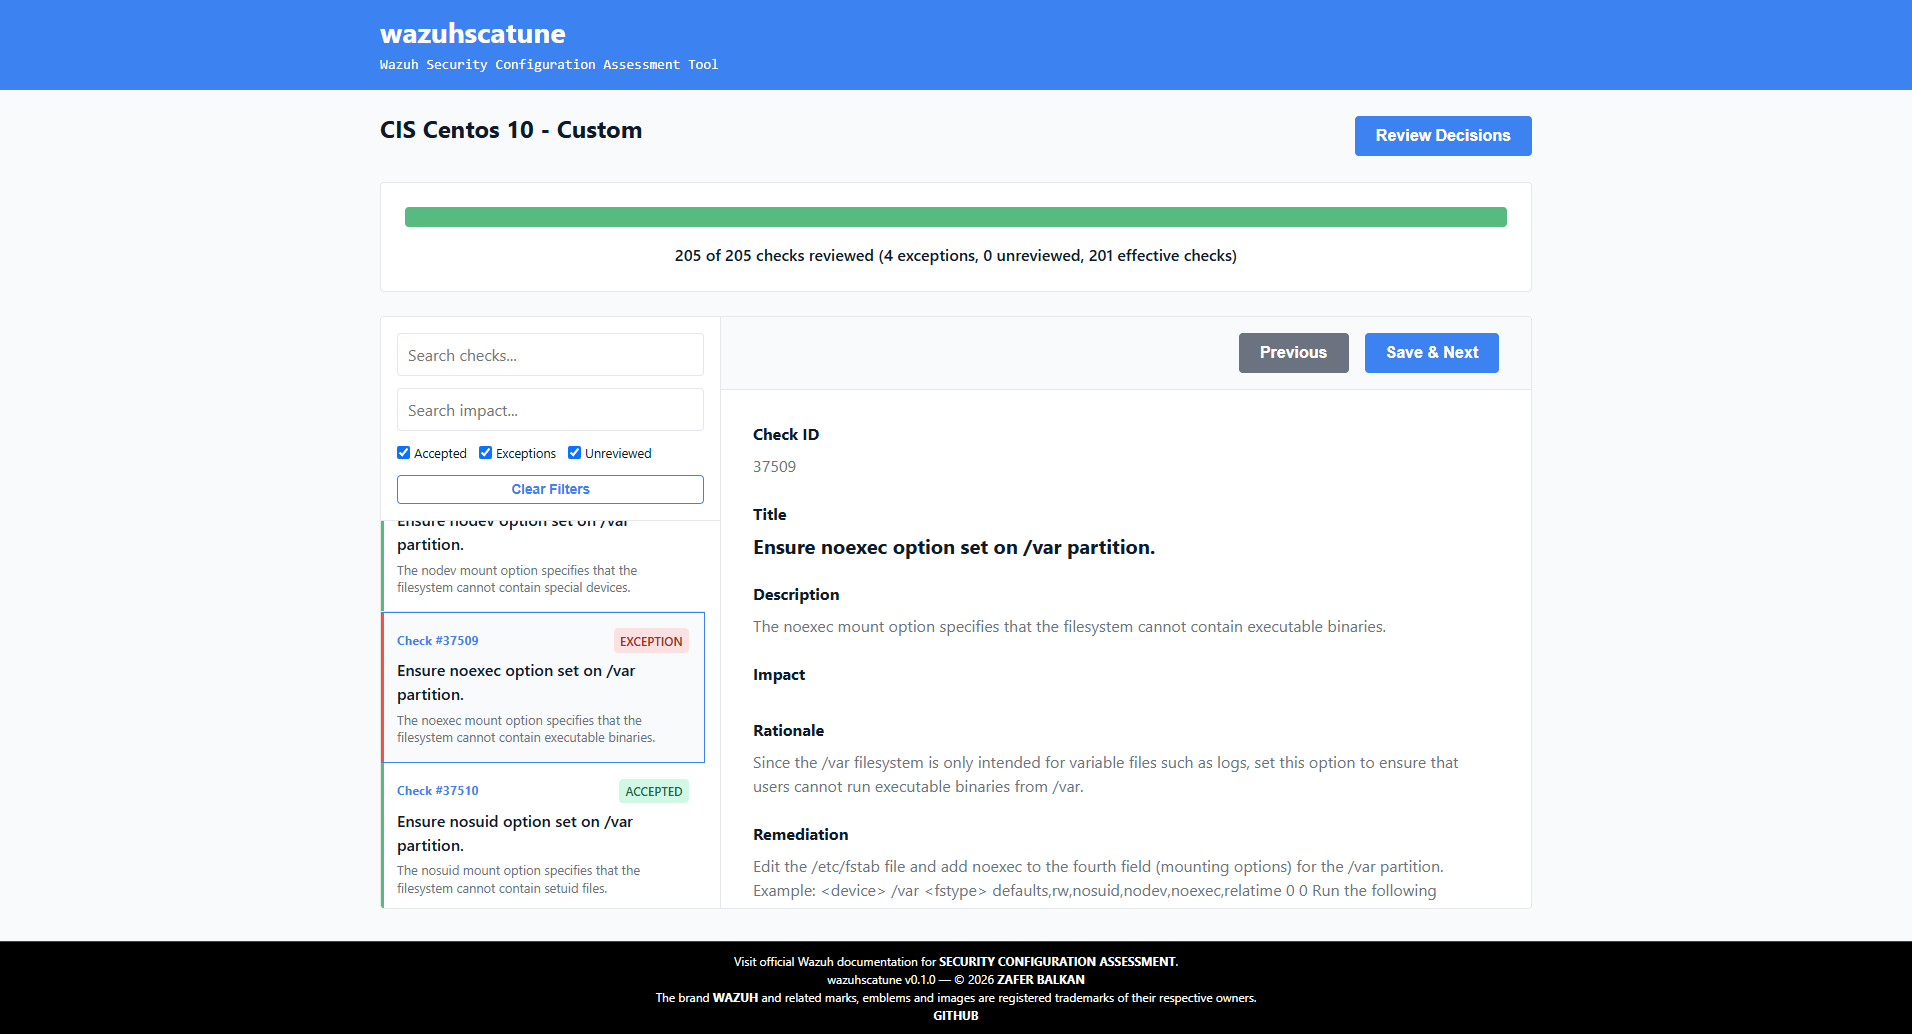
wazuhscatune is a local application for tailoring a trusted Wazuh Security Configuration Assessment (SCA) baseline. It opens a browser-based review UI where every check is explicitly accepted, recorded as an exception, or marked as not applicable.
Review states:
- Unreviewed — not yet explicitly reviewed.
- Accepted — retained in the tailored policy.
- Exception — removed with a justification because the check applies but the deviation is intentionally accepted, for example because risk is accepted or an alternative control is used.
- Not Applicable — removed with a justification because the check does not apply to the target system or role.
Requirements
Python 3.11 or newer. Python 3.11, 3.12, and 3.13 are tested on Windows, macOS, and Linux.
wazuhscatune is a local single-user application. Server deployment, multi-user operation, and use of the internal sca package as a Python library are not supported.
Install
Install with pipx:
pipx install wazuhscatune
From a local checkout:
pipx install .
Run
wazuhscatune
The application listens on http://127.0.0.1:5000 and opens the local browser. If the browser does not open automatically, open that address manually.
Workflow
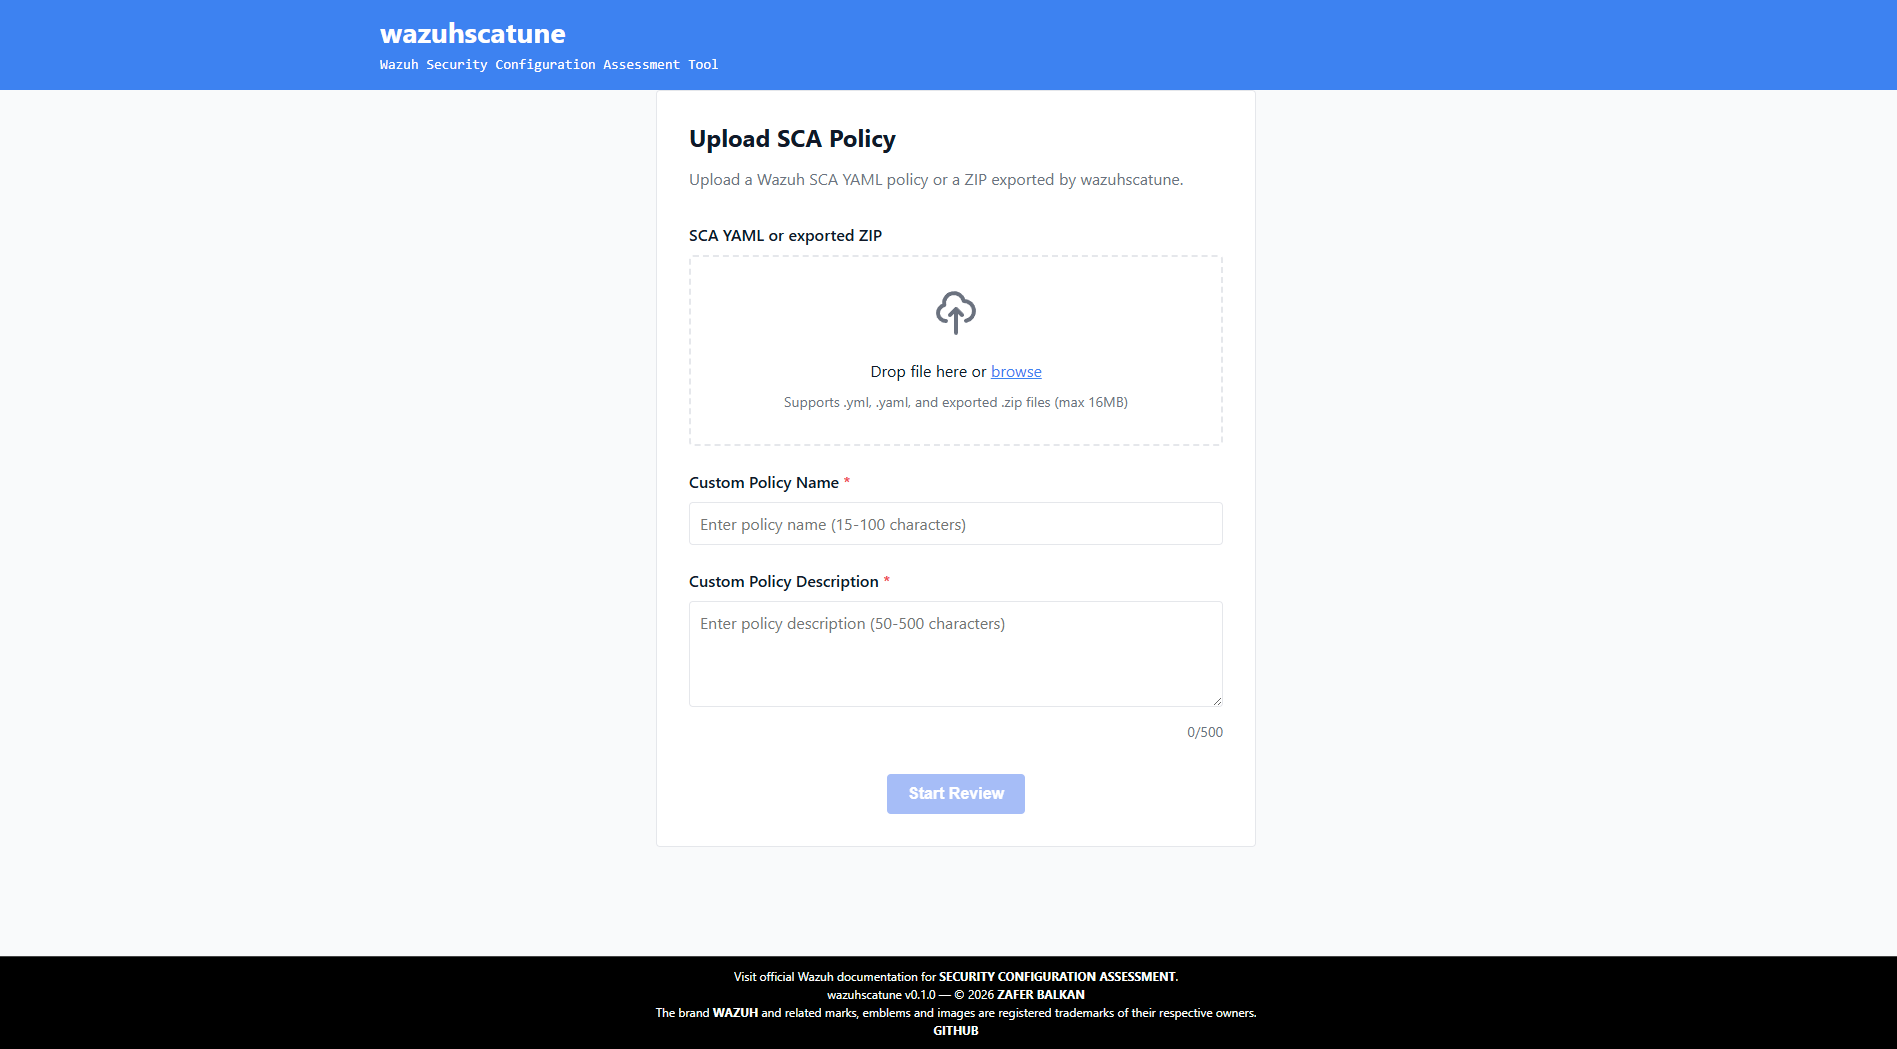
- Upload a Wazuh SCA
.yml,.yaml, or a ZIP previously exported bywazuhscatune. - Name and describe the tailored policy.
- Review every check as accepted, as a justified exception, or as justified Not Applicable.
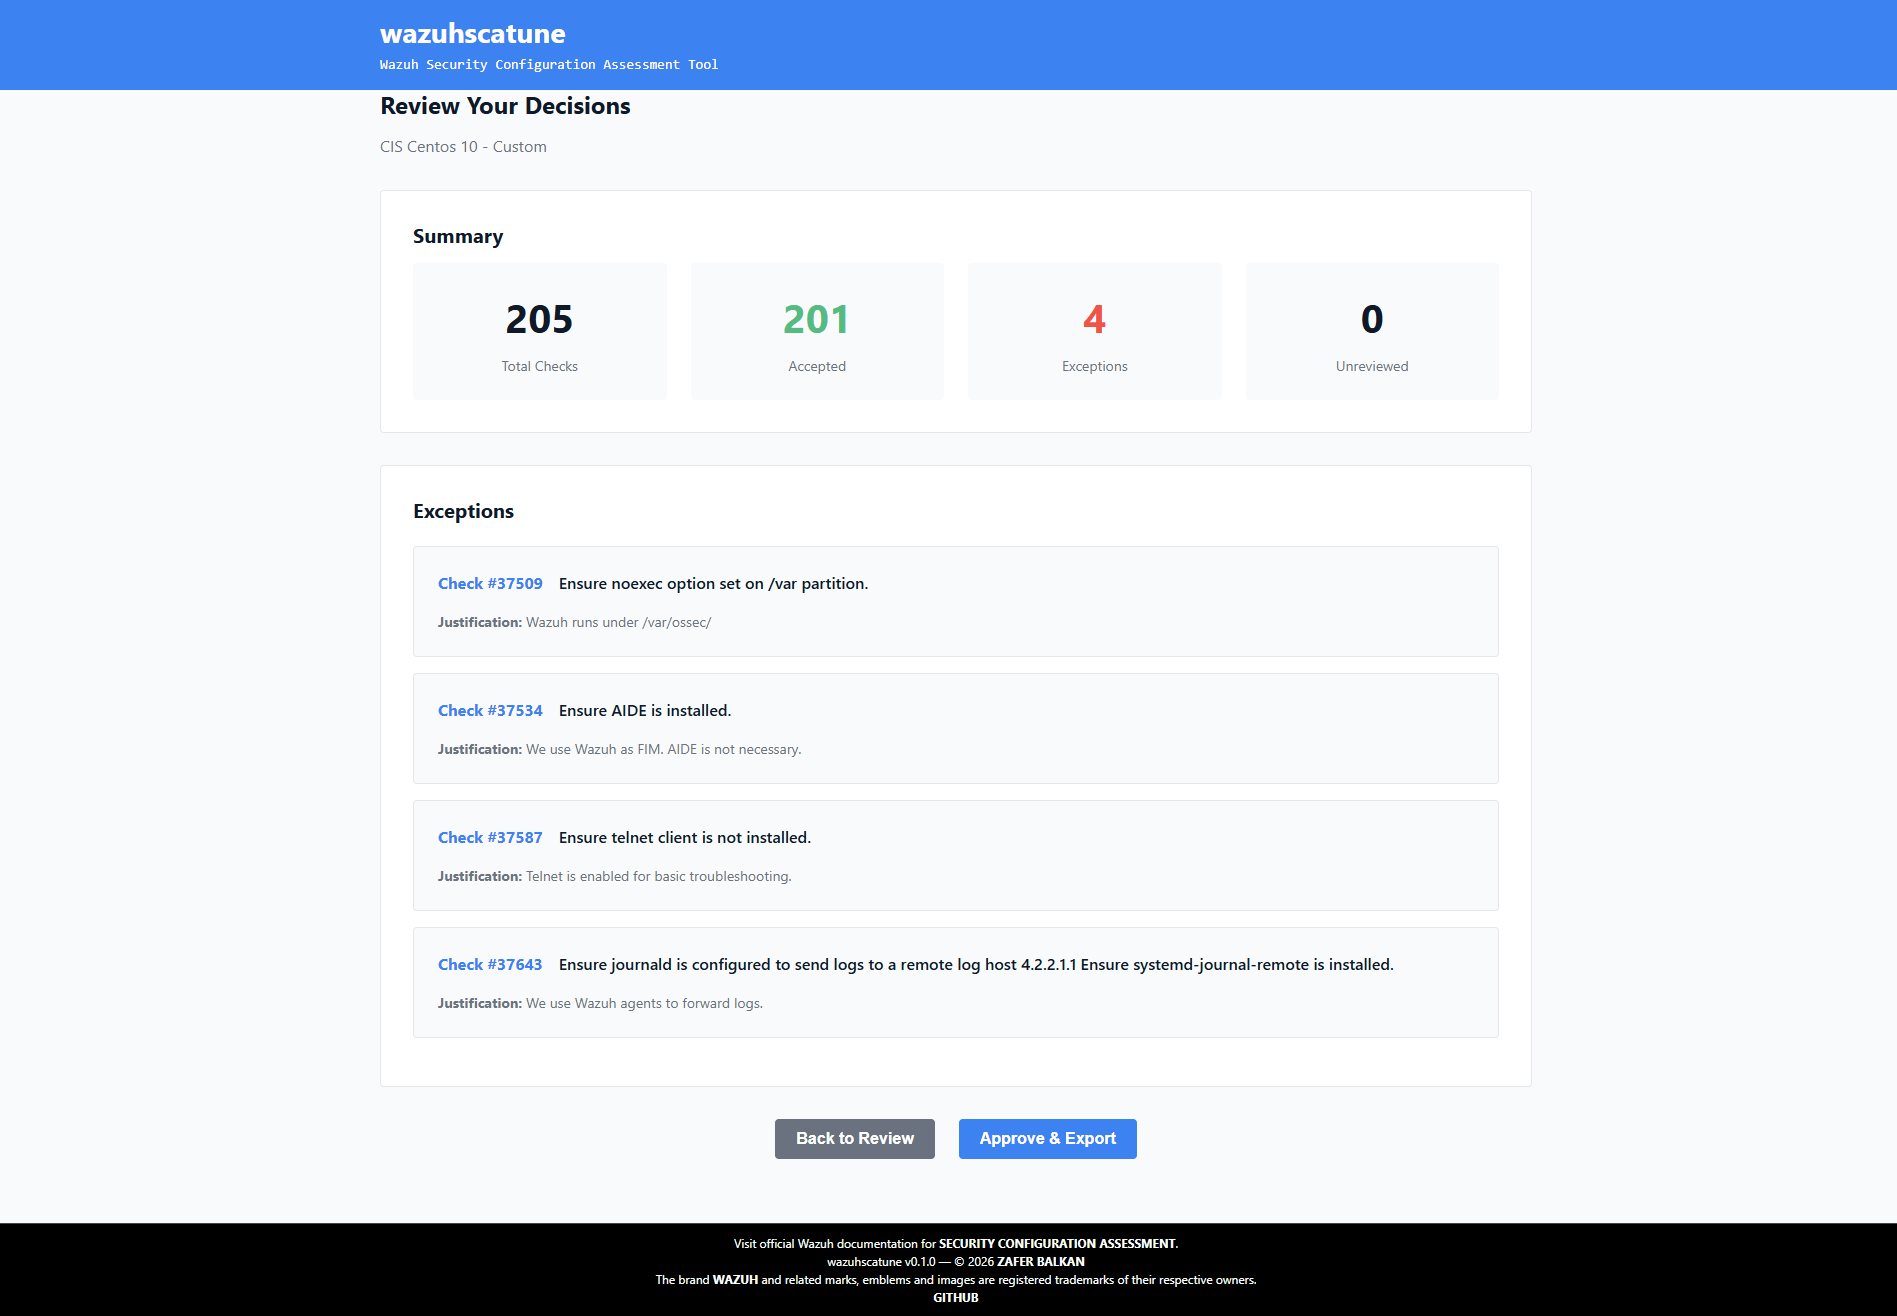
- Review the final decisions.
- Export a ZIP containing:
<policy>.yml— tailored SCA policy;<policy>_exceptions.yml— machine-readable removal record, split between accepted-risk exceptions and not-applicable checks;<policy>_exceptions.md— human-readable report with the same categories and baseline compliance mappings.
Exception and Not Applicable decisions both remove the check from the tailored policy. Export is blocked until every check has been reviewed, and at least one check must remain included. The uploaded baseline is never modified.
Local data
Review state is saved locally after each decision. Drafts can be recovered while their uploaded baseline remains available. Application-created temporary files expire after 48 hours by default; configure this with WAZUHSCATUNE_FILE_TTL_HOURS.
The browser session lifetime is 24 hours. Uploads, drafts, session files, exports, and logs remain on the local machine.
Validation
Input validation covers YAML syntax and expected Wazuh SCA structure, including policy metadata, requirements, checks, rule lists, compliance mappings, variables, and unique integer check IDs. ZIP imports are bounded by upload, member-count, and extracted policy-size limits. The application does not execute SCA checks or emulate the Wazuh SCA engine.
Development
For development and testing:
python -m pip install -e '.[dev]'
python -m pytest
python -m pycodestyle sca
python -m mypy sca
python -m compileall -q sca
python -m build
python -m twine check --strict dist/*
Python 3.11 is the compatibility floor. pyproject.toml is the authoritative package and dependency declaration.
Release history is kept in CHANGELOG.md.
License
GNU General Public License v3 or later. See LICENSE.
1 maintainer

Release files for wazuhscatune 0.2.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| wazuhscatune-0.2.1.tar.gz | 45.8 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| wazuhscatune-0.2.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 98.9 kB
Release files / wazuhscatune-0.2.1.tar.gz
| Download URL | wazuhscatune-0.2.1.tar.gz |
|---|---|
| Size | 45.8 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
01aa293a003e233e3a58e3139a20ac6b7dba6967ae218c6213c9d4efdfa1f4bb
|
|
BLAKE2b-256 checksum How to use checksums |
09ef7b840f6fd4017e8bf47221995d697c3bc5387920e93a6713ebf64d29973e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 7, 2026.
Transparency logRelease files / wazuhscatune-0.2.1-py3-none-any.whl
| Download URL | wazuhscatune-0.2.1-py3-none-any.whl |
|---|---|
| Size | 53.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
c4a016462e3d225dea1a4d8d90b323367aea91f389ca959aa332d37f832677bb
|
|
BLAKE2b-256 checksum How to use checksums |
4500d78b588a559794dfe8d02717acd5e83cdb48f979c7d2693be4b5f1ae9f06
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 7, 2026.
Transparency log













