



weave-compose
Platform-aware skill composition layer for AI coding tools.
"Everyone's building skills. Weave makes them work together."
How It Works
Weave ingests skills from AI coding tools (Claude Code, Cursor, Codex, Windsurf) and normalises them into a universal schema — a single Skill object with a name, platform, capabilities, and semantic embedding. At query time it embeds your task description and selects the best skill(s) by cosine similarity against every loaded skill, with no manual routing required. When a task spans multiple skills, Weave composes their contexts into a single merged string ready for injection into any AI coding tool.
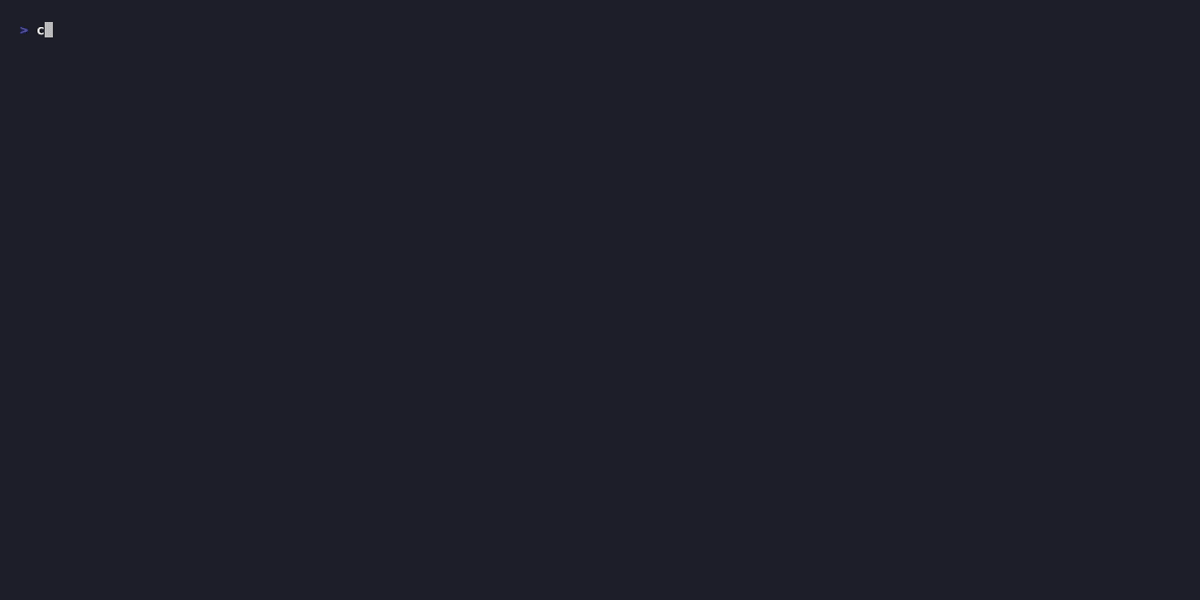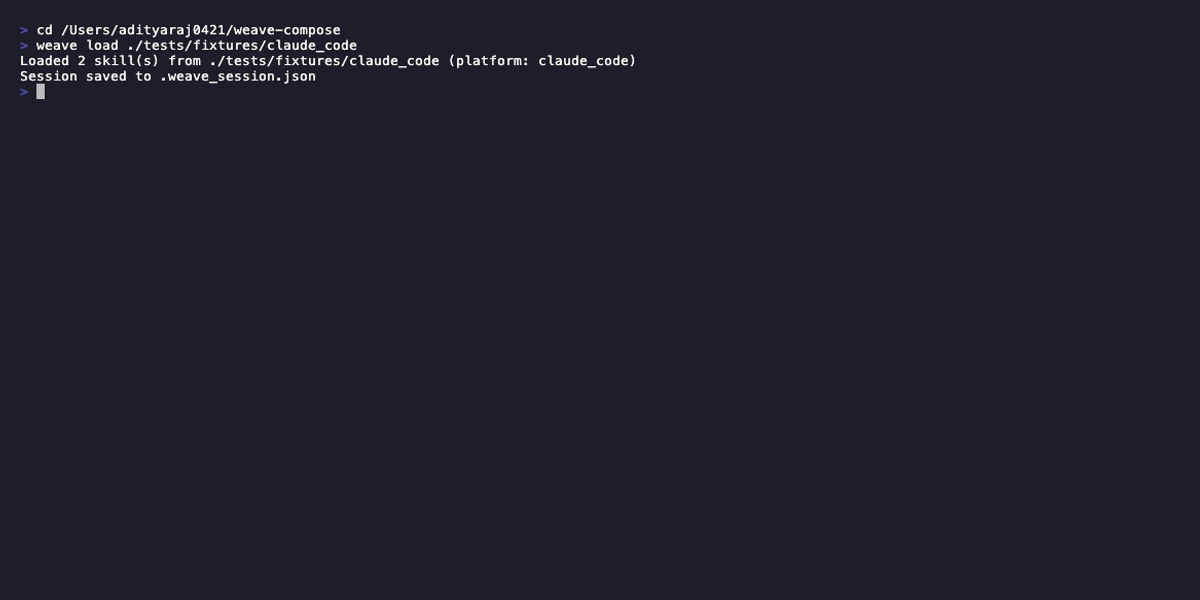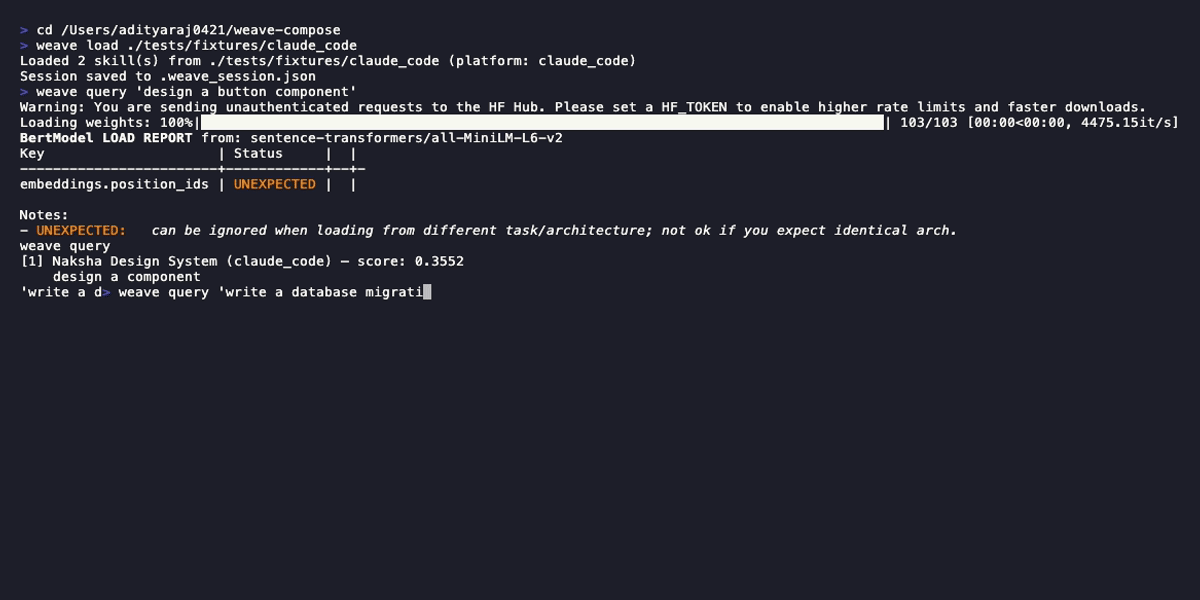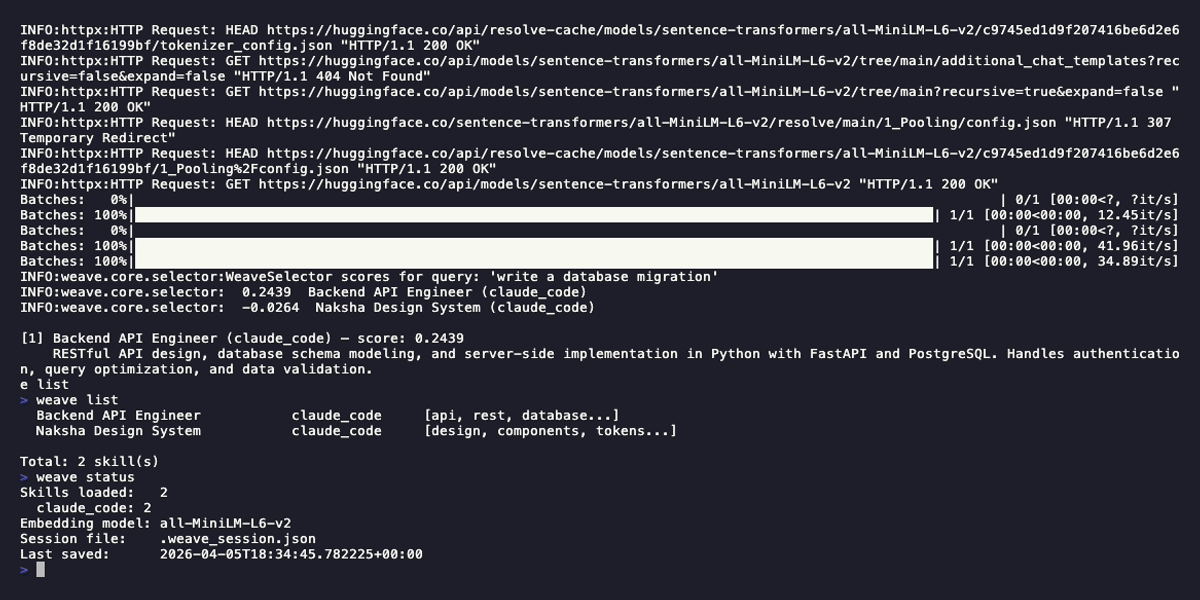
Demo
Record your own:
brew install vhs && vhs demo.tape
Installation
pip install weave-compose
Requires Python 3.11+. All embeddings run locally — no API key, no cloud dependency.
Quickstart
# 1. Create a minimal SKILL.md file
mkdir my-skills
cat > my-skills/SKILL.md << 'EOF'
---
description: React component design with Tailwind CSS and accessibility best practices.
capabilities: [react, tailwind, components, accessibility]
---
Always use semantic HTML. Never hardcode colours — use Tailwind tokens only.
EOF

# 2. Load and query
weave load ./my-skills
# Loaded 1 skill(s) from ./my-skills (platform: claude_code)
# Session saved to .weave_session.json

weave query "design a button component"
# [1] my-skills (claude_code) — score: 0.61
#     React component design with Tailwind CSS and accessibility best practices.

# 3. Explore further
weave list    # see all loaded skills
weave status  # session info and embedding model in use
CLI Reference
| Command | Description |
|---|---|
weave load <path> [--platform] [--verbose] |
Load skills from a directory and save the session |
weave query "<text>" [--explain] [--top N] |
Query loaded skills and return the best match(es) |
weave list [--platform] |
List all skills in the current session |
weave status |
Show skill count, platform breakdown, and session info |
weave clear |
Clear all loaded skills and delete the session file |
weave detect <path> |
Auto-detect the platform of a skill directory |
weave run [--config <path>] |
Load skills from weave.yaml and start an interactive query loop |
weave serve [--port <n>] |
Start the local FastAPI server on localhost (default port: 7842) |
Session state is stored in .weave_session.json in your current working directory. Run weave load once; all subsequent query, list, and status calls restore the session automatically — no re-embedding required.
How Weave Selects Skills
Weave uses all-MiniLM-L6-v2 (runs on CPU, ~80 MB, cached after first use) to embed both your query and each skill's context. It returns the top match by default. If the confidence gap between the first and second result is less than 0.1, both skills are returned for composition — Weave assumes the task spans both domains.
Use --explain to see the full score table:
weave query "design a REST API" --explain
Use --top N to request at least N results:
weave query "build a feature" --top 2
Contributing
Contributions are welcome at every layer — new platform adapters, composition strategies, CLI improvements, and documentation.
- Contributor guide: docs/contributing.md
- Writing a new adapter: docs/adapters.md
- Architecture overview: docs/architecture.md
All code must pass pytest, ruff check ., and mypy --strict . before merging.
License
MIT — see LICENSE.
1 maintainer

Metadata
1 maintainer
Release files for weave-compose 1.0.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| weave_compose-1.0.1.tar.gz | 43.2 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| weave_compose-1.0.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 85.4 kB
Release files / weave_compose-1.0.1.tar.gz
| Download URL | weave_compose-1.0.1.tar.gz |
|---|---|
| Size | 43.2 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
23387de469f3dc22184174ca1b0aa6eec3ef14d812081e15a2d6bc2d399f2a4b
|
|
BLAKE2b-256 checksum How to use checksums |
5d1a069fc8eef472f36c774cfc0deb887e1fd319ac2f64f6134da53019489815
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Apr 5, 2026.
Transparency logRelease files / weave_compose-1.0.1-py3-none-any.whl
| Download URL | weave_compose-1.0.1-py3-none-any.whl |
|---|---|
| Size | 42.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
0b7d597bd5075f3b6060cfb4547ec0eeb06bbf808e2ecaabb3b1191e0189b98c
|
|
BLAKE2b-256 checksum How to use checksums |
05c41625352e817c33df9727f0c3a55cf342c9d8512069c4f6e73205474394c6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Apr 5, 2026.
Transparency logSecurity for weave-compose 1.0.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for weave_compose-1.0.1.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Apr 5, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














