
weftgate
A local second brain for coding agents. Understand the code. Remember decisions. Verify changes.




Give your agent compact source context, durable decisions and verification gates through one install, one MCP server and one local memory store. Weftgate brings Mnemo’s local memory workflow into the verification engine. You do not need to install or configure a second project for everyday use.
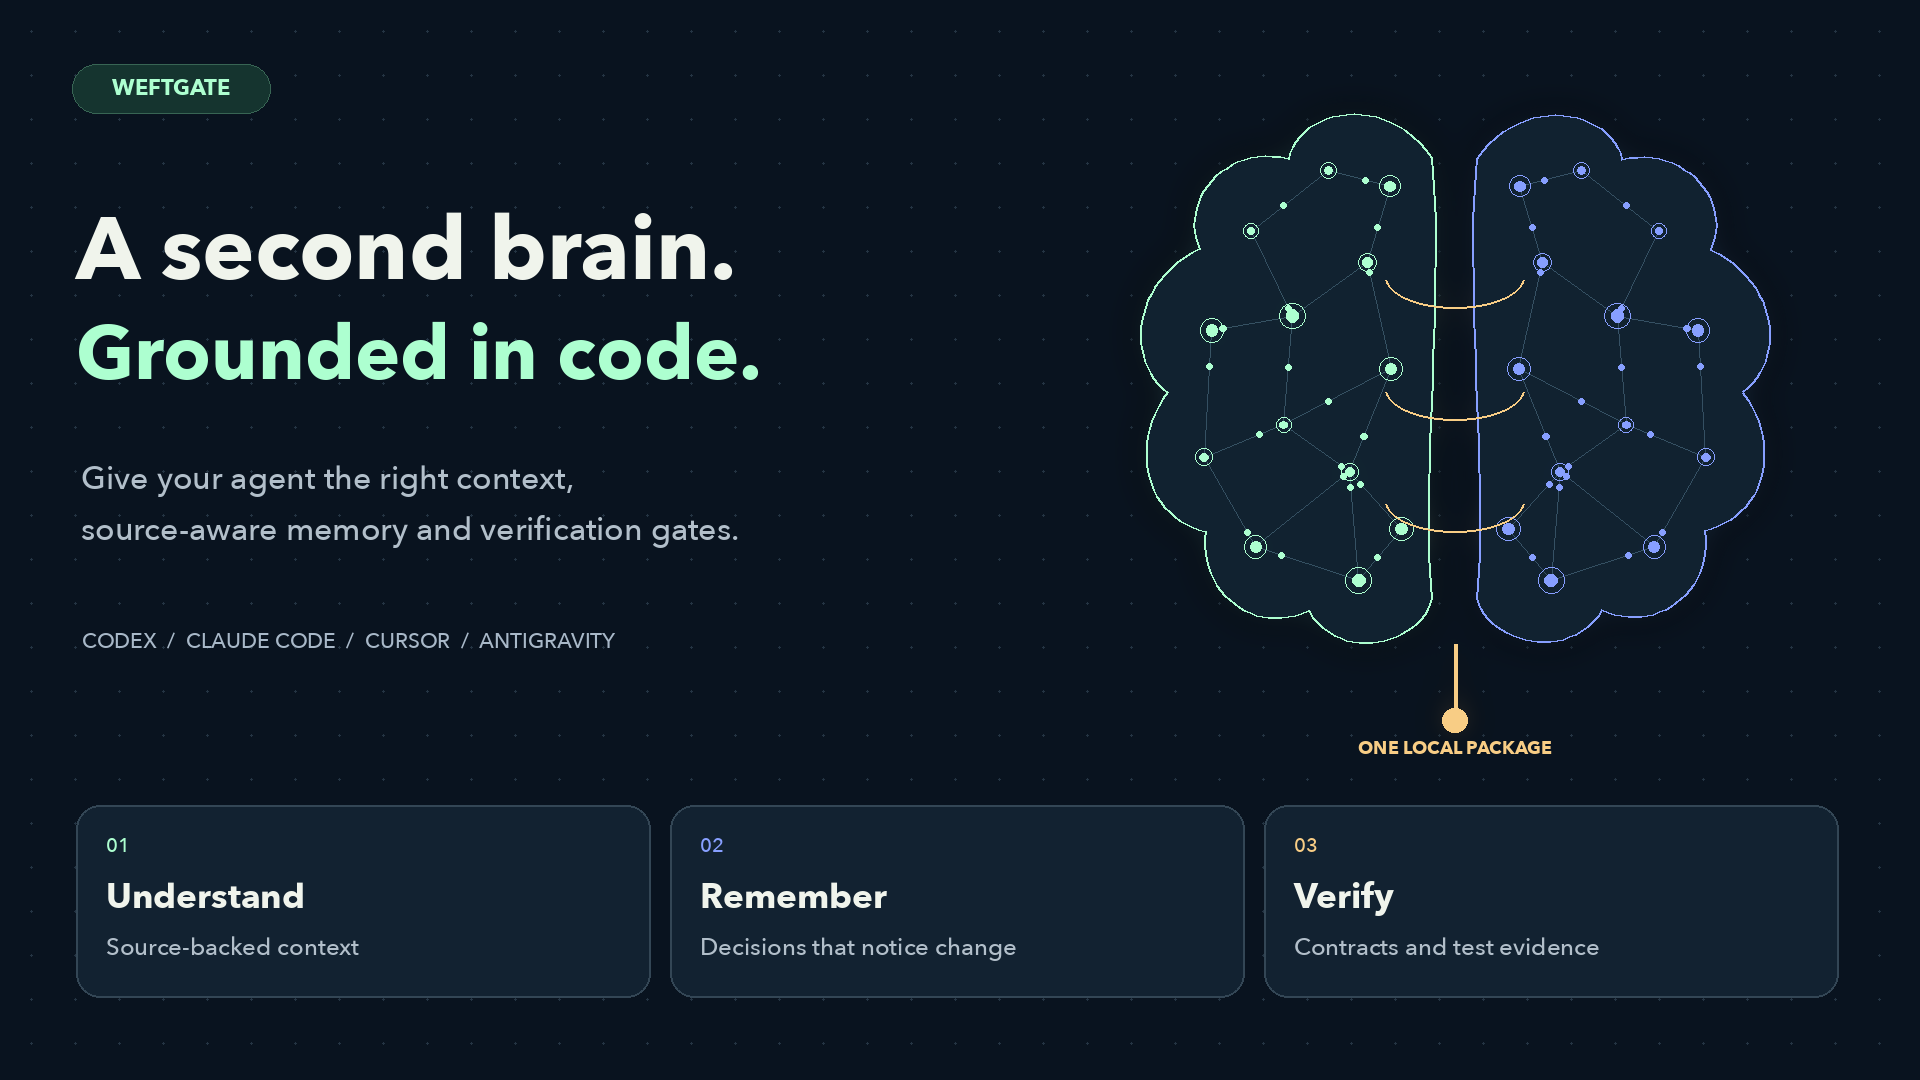
| Understand | Remember | Verify |
|---|---|---|
| Start with relevant memories and current source references. | Check explicit memory claims; hide stale notes; resume in another agent. | Check code connections and save a handoff with observed test evidence. |
weftgate brief "order retries" |
weftgate remember ... --env DATABASE_URL |
weftgate handoff ... --run |
No API key. No runtime dependencies. Local storage. No automatic transcript capture. Context, recall and default verification make no network calls. Explicitly enabled test commands run your repository's code and can have their own side effects.
Watch the v0.2 foundation demo · Transcript and reproducible evidence · How to write an oracle
Try it
pip install weftgate
cd /path/to/your/repo
weftgate setup --agents codex,claude,cursor,antigravity --hooks --instructions
weftgate doctor                   # inspect coverage and configured integrations
weftgate audit                    # find existing broken connections
weftgate brief "your next task"   # memories + current source context
weftgate memory stats             # one local notebook and freshness counts
weftgate checkpoint               # changed code + evidence still needed
From source: pip install git+https://github.com/Avinash-Amudala/weftgate.git.
For development, bash scripts/bootstrap.sh installs the extras and runs the offline self-test.
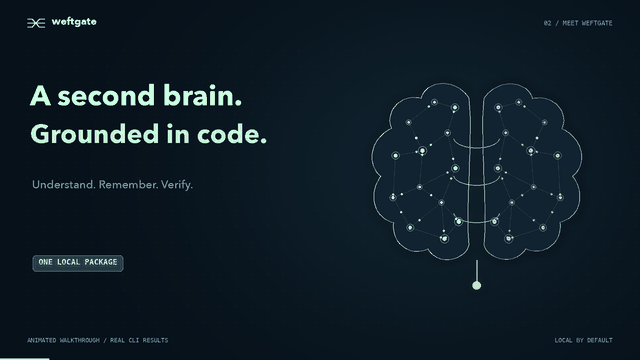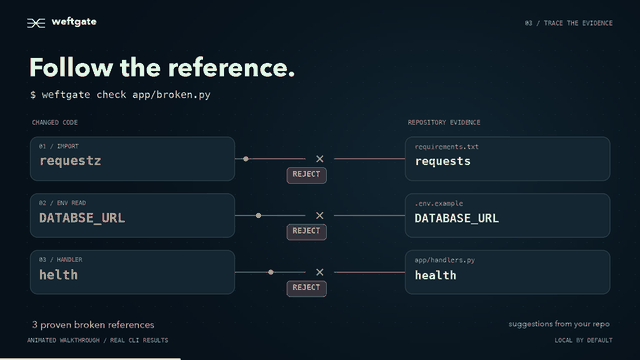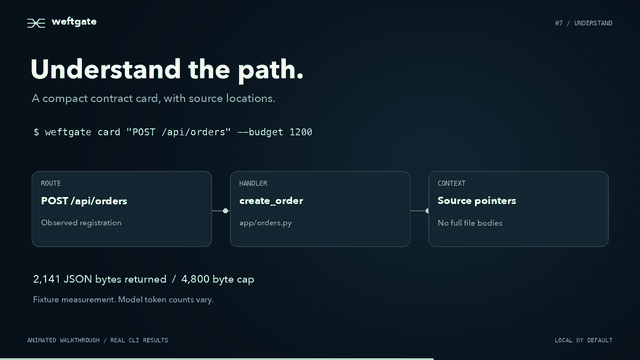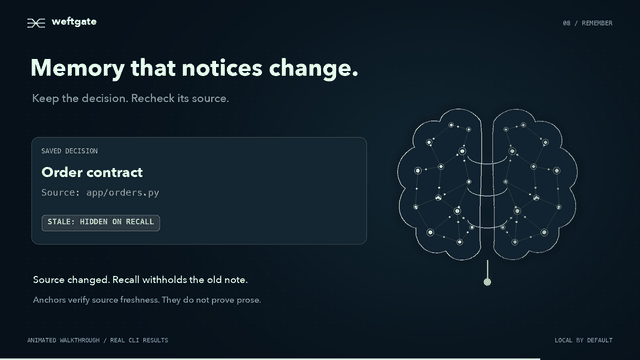
The demo uses an intentionally broken fixture, not a field benchmark:
REJECT  import 'requestz'       → did you mean requests?
REJECT  env var 'DATABSE_URL'   → did you mean DATABASE_URL?
REJECT  handler 'helth'         → did you mean health?
Fix the three names and the fixture passes. A computed key such as os.environ[key]
returns review, because static analysis cannot establish its value.
To reproduce: weftgate eval mutate --fixture --seed 13.
What the result means
| Result | Meaning | Blocks by default? |
|---|---|---|
accept |
The extracted reference resolves, or nothing checkable was found. | No |
review |
Evidence is incomplete or the reference is dynamic. | No |
reject |
A hard claim contradicts the indexed contract. | Yes |
unverifiable |
The relevant index or capability is unavailable. | No |
The rule is block only on a positive, machine-checkable falsehood. Suggestions
accompany findings when a nearby candidate exists. An accept verdict is not a test
suite result or proof that the application works; inspect coverage with weftgate doctor.
Supported verification contracts
| Oracle | Checks | Conservative limits |
|---|---|---|
| Environment variables | Reads against dotenv examples, settings schemas, Docker/Compose declarations, code defaults, and configured files. | Dynamic keys and absent declaration sources soften. Declare externally supplied variables in your contract. |
| Python and Node imports | Imports against dependency metadata, local packages, known package aliases, and supported path aliases. | A manifest alone cannot prove a complete dependency tree. Unknown mappings and optional imports review. |
| FastAPI / Starlette routes | Handler references, router includes, and route claims using a static AST index. | Computed registration, external modules, and unresolved prefixes cannot be fully verified. |
This is an early static analyzer with bounded parsers. It does not execute your app, replace tests or a security scanner, or cover every framework. Python, Node, and monorepo import resolution can depend on runtime configuration. Missing or ambiguous evidence must soften; please report a false block with a minimal reproduction. Historical field runs document methods and limitations, rather than a claim of zero false positives.
Use it with your agent
weftgate setup --agents all --hooks --instructions --dry-run
weftgate setup --agents codex,claude,cursor,antigravity --hooks --instructions
The standard-library MCP server requires no extra package. Example MCP configuration:
{"mcpServers": {"weftgate": {"command": "weftgate", "args": ["mcp"]}}}
Run the server with the repository as its working directory. weftgate setup --agents all
writes supported project configs and prints snippets for clients with global settings.
CLI and MCP use the same functions. Start with brief, save decisions with
remember, and use handoff for the next session. Focused context, recall,
checkpoints, memory transfer and the existing verification tools remain available.
| Client | Context and recall | Native gate installed by setup |
|---|---|---|
| Codex | Project MCP + AGENTS.md guidance | Stop hook requests one repair continuation. Trust via /hooks. |
| Claude Code | Project MCP + rules | Pre-edit gate for Edit/Write/MultiEdit; Stop check catches other writes. |
| Cursor | Project MCP + always-applied rule | Stop hook with up to two repair follow-ups. |
| Antigravity | Project MCP + workspace rule | Stop hook for an idle, normally completed run, with a bounded continuation. |
| VS Code / Copilot, Windsurf, Claude Desktop | MCP setup or printed configuration | Use the CLI, Git hook and CI for gating. |
Client versions, project trust and organization policy affect hook activation. MCP tools and rules alone do not force an agent to use the gate. Local hooks are guardrails; require the GitHub Action in branch protection to enforce merge checks. Integration paths, activation checks and official references.
A small agent workflow
weftgate brief "order retries" --reference app/orders.py --budget 1200
weftgate remember "Order idempotency" "Keep duplicate requests idempotent." --file app/orders.py
# Your coding agent makes the change. Then:
weftgate check app/orders.py
weftgate handoff "Order retries" "Added retry handling. Next: review timeout behavior." --file app/orders.py --run --require-ready
# In Codex, Claude Code, Cursor or another MCP client:
weftgate brief "order retries"
Use paths and routes that exist in your project. Configure the commands the last
step should observe in weftgate.toml:
[weftgate.workflow]
commands = ["python -m pytest -q"]
--run explicitly permits execution of configured, allowlisted commands. A checkpoint
distinguishes proven failures, review findings, missing test evidence and changes
during verification. --require-ready exits 3 when evidence is incomplete. A ready
checkpoint covers those contracts and commands only. Workflow details.
Context responses contain source pointers, not file bodies. The default budget is
1,500 estimated tokens with a hard cap of 6,000 UTF-8 JSON bytes. Actual model token
counts vary. weftgate ledger reports payload bytes and gate events; it does not
invent a savings percentage or equate every rejection with an avoided retry.
Context coverage and budgets.
CLI and CI
git diff | weftgate check -
weftgate check --staged
weftgate check --path app/main.py --content proposed.py
weftgate claim '[{"kind":"route","method":"POST","path":"/users"}]'
weftgate audit --format=json
weftgate index --show routes
Exit codes: 0 allows the change, 1 blocks according to policy, 2 means a
usage or configuration error. Use --format=github for workflow annotations.
name: Verify connections
on: [pull_request]
permissions:
  contents: read
jobs:
  verify:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v5
        with:
          fetch-depth: 0
      - uses: Avinash-Amudala/weftgate@v0.3.0
        with:
          mode: check             # or audit to inspect the repository
The Action supports base, paths (shell-quoted paths, no shell expansion),
block-on, and python-version. Use a full checkout for diff ancestry.
The pre-commit hooks use the same gate; pin rev: v0.3.0.
Configure the contract
# weftgate.toml
[weftgate]
oracles = ["env_vars", "imports_lockfile", "routes_fastapi"]
block_on = "reject"                 # reject | review | never
env_declared_in = [".env.example"]
Precedence: WEFTGATE_* environment variables, repository configuration, user
configuration, then defaults. The index lives in the user cache, outside the repo.
weftgate doctor explains the selected configuration and missing contracts.
Outcome claims such as “tests passed” need machine-checkable evidence. Re-running a
named test command or probing a URL requires explicit --run and the configured
allowlist. See security and execution boundaries.
Memory that notices changed code
Weftgate's notebook checks explicit file, environment, route, import and symbol claims before saving them. A proven false claim is refused with available suggestions. Uncertain claims stay available for review. Recall checks original source hashes, and notes with changed or missing evidence stay hidden by default. Source anchors support a claim about freshness; the note's prose remains unverified.
weftgate remember "Database access" "Use the declared connection." --env DATABASE_URL
weftgate recall "database"
weftgate recall "database" --include-stale
weftgate memory stats
handoff saves a summary and its scoped checkpoint in the same notebook. Another
agent can resume through brief; remembered test evidence is labeled historical
and changes to the current tree are detected. Obvious secret patterns are scrubbed
from note text, but do not treat this as permission to store credentials.
Already have Mnemo data? Preview and import selected memories without installing Mnemo or modifying its database:
weftgate memory import /path/to/mnemo.sqlite --limit 10
weftgate memory import /path/to/mnemo.sqlite --limit 10 --apply
The legacy repository remains compatible for existing transcript and team-hub users. Automatic capture, external embeddings and team federation are outside the public local workflow. They are not silently enabled by migration. Memory and trust · Migration and backup · Architecture and scope.
Contribute
bash scripts/bootstrap.sh
.venv/bin/ruff check .
.venv/bin/ruff format --check .
.venv/bin/mypy weftgate
.venv/bin/python -m weftgate.selftest
.venv/bin/python -m pytest -q --cov=weftgate --cov-fail-under=85
Start with CONTRIBUTING.md, the oracle guide, and AGENTS.md. New oracles need a real broken example, a correct example, and a dynamic case that reviews. Reproducible false blocks and missing-contract reports are especially useful.
Apache-2.0 · Changelog · Launch plan
1 maintainer

Metadata
1 maintainer
Release files for weftgate 0.3.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| weftgate-0.3.0.tar.gz | 909.3 kB | With provenance | Details for weftgate-0.3.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| weftgate-0.3.0-py3-none-any.whl | Python 3 | none | any | Details for weftgate-0.3.0-py3-none-any.whl |
Total release size: 1.1 MB
Release files / weftgate-0.3.0.tar.gz
| Download URL | weftgate-0.3.0.tar.gz |
|---|---|
| Size | 909.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
aac00a027a703614734c70f86f56c9a791de6d589996f284c751ef3fbf48baef
|
|
BLAKE2b-256 checksum How to use checksums |
3fb31a8abce8197020fed7c4b1a544678a5325b11c913084f989f75104d8bd89
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 13, 2026.
Transparency logRelease files / weftgate-0.3.0-py3-none-any.whl
| Download URL | weftgate-0.3.0-py3-none-any.whl |
|---|---|
| Size | 142.8 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
6c7b9cad437a95b58237bf8662eb2049aa5052f2b247660bdc9b1a177b895bca
|
|
BLAKE2b-256 checksum How to use checksums |
fa93fa549fb1b112b0e28f47935c08eb088fed14357aeee43452da207d3451fb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 13, 2026.
Transparency logSecurity for weftgate 0.3.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for weftgate-0.3.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 13, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














