
Windows 11 Release Guard


Windows release policy guard for broad-fleet Windows 11 version checks.
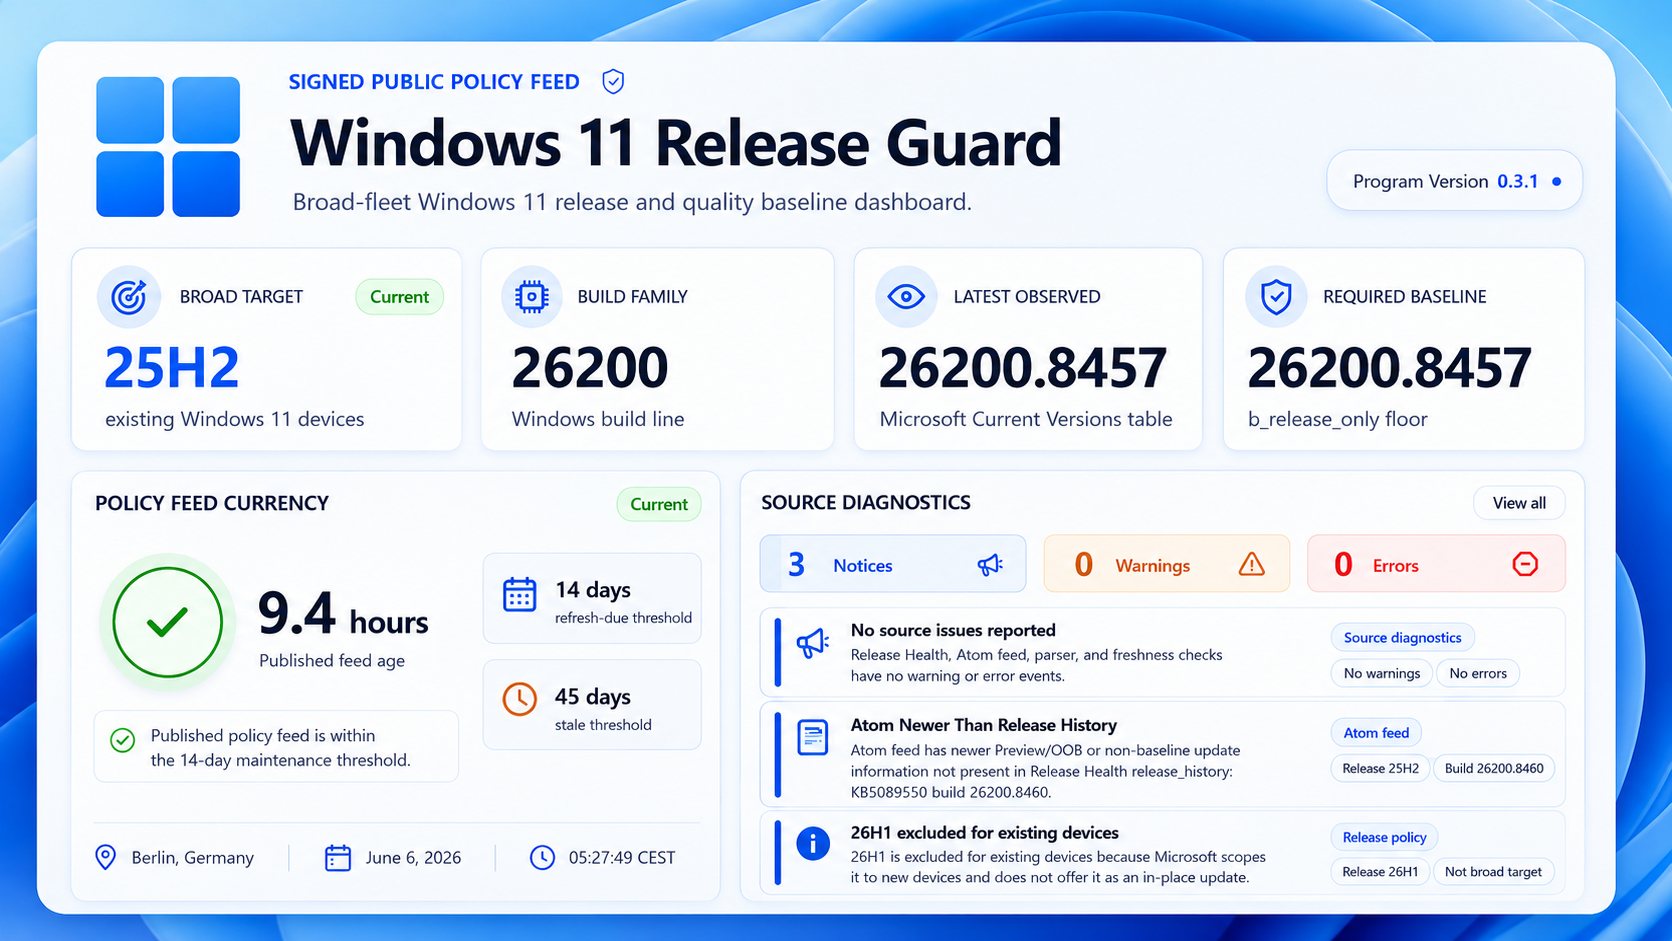
Windows 11 Release Guard tells administrators whether an existing Windows 11 device is on the current fleet release and quality baseline, using a signed JSON feed, build-first local evidence, a static GitHub Pages dashboard/API, and a PyPI package for sysadmin/RMM automation. The repository, distribution package, installed console command, and Python import package use the same win11_release_guard name.
| Fact | Value |
|---|---|
| Project / package | win11_release_guard |
| Version | 0.6.1 |
| Console script | win11_release_guard |
| Python entry point | python -m win11_release_guard |
| Repository | https://github.com/Avnsx/win11_release_guard |
| PyPI | https://pypi.org/project/win11-release-guard/ |
| Public feed | https://avnsx.github.io/win11_release_guard/windows-release-policy.json |
| License | MIT |
Quick Start
python -m pip install win11_release_guard
win11_release_guard --pretty
win11_release_guard --strict-production --json-pretty --no-wua
The last line is the usual production/RMM compliance job.
What It Checks
| Check | Rule |
|---|---|
| Verdict source | The signed public policy decides; local WUA diagnostics never override the policy verdict. |
| Installed release | Build-first local evidence; ProductName, WMI Caption, and DisplayVersion stay diagnostic. |
| Fleet target | The newest H2 release once it has its first monthly security (B) release; 26H1 is excluded for existing devices. |
| Output | Human, JSON, and JSON-pretty output with stable exit codes. |
Detail: Architecture, Local Windows Detection, FAQ.
Public Feed And Dashboard
| Public artifact | URL |
|---|---|
| Signed policy JSON | https://avnsx.github.io/win11_release_guard/windows-release-policy.json |
| Detached signature | https://avnsx.github.io/win11_release_guard/windows-release-policy.json.sig |
| Policy manifest | https://avnsx.github.io/win11_release_guard/policy-manifest.json |
/api/v1 mirrors these as stable aliases, kept backward compatible, with signing-key overlap, for at least 24 months.
Detail: GitHub Pages Dashboard, dashboard docs.
Safety And Trust Model
- Runtime clients do not authenticate to GitHub and do not need GitHub tokens, private repository access, or a paid signing certificate. The private signing key lives only in a GitHub Actions secret.
- The production generator may use public Microsoft Release Health HTML, the public Microsoft servicing table-of-contents JSON, public Microsoft servicing support articles, and unauthenticated public MSRC CVRF data for source diagnostics and informational enrichment; it does not use Microsoft Graph or token-authenticated Microsoft APIs.
- Badges are signals, not proof. Dependency freshness is checked by a scheduled workflow.
Dependency freshnessis a scheduled direct-dependency check over direct dependency specifiers, not an always-current dependency guarantee. The Pylint badge reports the workflow for the current--fail-under=8.0gate, not a permanent quality certificate.
Detail: Policy Feed and Trust Model, security automation.
Documentation
| Need | Link |
|---|---|
| Pages Wiki home | https://avnsx.github.io/win11_release_guard/wiki/ |
| First run | Quick Start |
| What changed | Pages changelog, v0.6.1 notes, CHANGELOG.md |
| Problems | Troubleshooting |
| Maintainers | Build, Test and Release, Tagged release lane |
| Contributors | Regression Chokepoints |
| GitHub internal Wiki (Markdown mirror) | https://github.com/Avnsx/win11_release_guard/wiki |
The generated Pages Wiki is the primary public, indexed documentation surface. The GitHub Wiki mirrors the same wiki/*.md source.
Deployment-affecting changes require the live Pages gate before merging. Use the full gate in AGENTS.md and Build, Test and Release when changing workflows, the policy generator, signing, Pages, manifest/API aliases, source URLs, or public-check CLI behavior.
Support The Project
If Windows 11 Release Guard saves you time or helps your fleet checks, please star the repository. Stars make the project easier for other Windows administrators to discover and help justify continued testing, documentation, release automation, and dashboard work.

Contribution, Support, License
Issues · Releases · MIT license, see LICENSE.txt
This project is independent open-source software and is not affiliated with Microsoft.
1 maintainer

Metadata
1 maintainer
Release files for win11-release-guard 0.6.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| win11_release_guard-0.6.1.tar.gz | 499.5 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| win11_release_guard-0.6.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 818.9 kB
Release files / win11_release_guard-0.6.1.tar.gz
| Download URL | win11_release_guard-0.6.1.tar.gz |
|---|---|
| Size | 499.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
828ec0159f561bfa08b226e7939ba8919924d25f02df9bd2ea157d80a2a5b861
|
|
BLAKE2b-256 checksum How to use checksums |
fb2742c029ff16bedeb266216b6f3f8fa6b79503f29cf9519eb8c92c62a70d87
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 9, 2026.
Transparency logRelease files / win11_release_guard-0.6.1-py3-none-any.whl
| Download URL | win11_release_guard-0.6.1-py3-none-any.whl |
|---|---|
| Size | 319.4 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
d38c02982c4c33bfe4978a77abbf1ab0cf212c342e4f84e208fcd94173f3e099
|
|
BLAKE2b-256 checksum How to use checksums |
786ce7b64d98d60a907abbd88fede79cd44f6c8f772db2a2b55e4f5a0bd685cb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 9, 2026.
Transparency log













