
XBSL
English · Русский
Documentation: docs.keyfire.ru/xbsl

The XBSL toolkit for 1C:Element: a linter with autofixes, an LSP server, a project index,
platform documentation search, metadata scaffolding, translation of sources into English
spellings and an MCP server for AI agents. Plus a VS Code extension on the same engine. It works
on pairs of files: Name.yaml describes an element, Name.xbsl holds its code. And it answers
long before the server-side compilation that runs on deploy.
Before 0.16 the project was named xbsl-lint, package
xbsllint. The old commands, imports, environment variables and entry-point groups keep working as aliases.
Not affiliated with 1C. "1C:Element", "1C:Fresh" and related names are trademarks of their respective owners. Language data is generated from your own distribution. See NOTICE.
Development notes and updates (in Russian): the 1C × AI: engineering workshop Telegram channel.
Why
1C:Element has no tooling outside the platform. The only check on the code is the server-side compilation on deploy, which is slow and knows nothing about a project's conventions. xbsl answers right away on your own machine, catches what the compiler never looks at, and takes over the metadata mechanics: creating objects, attributes and forms.
How it works
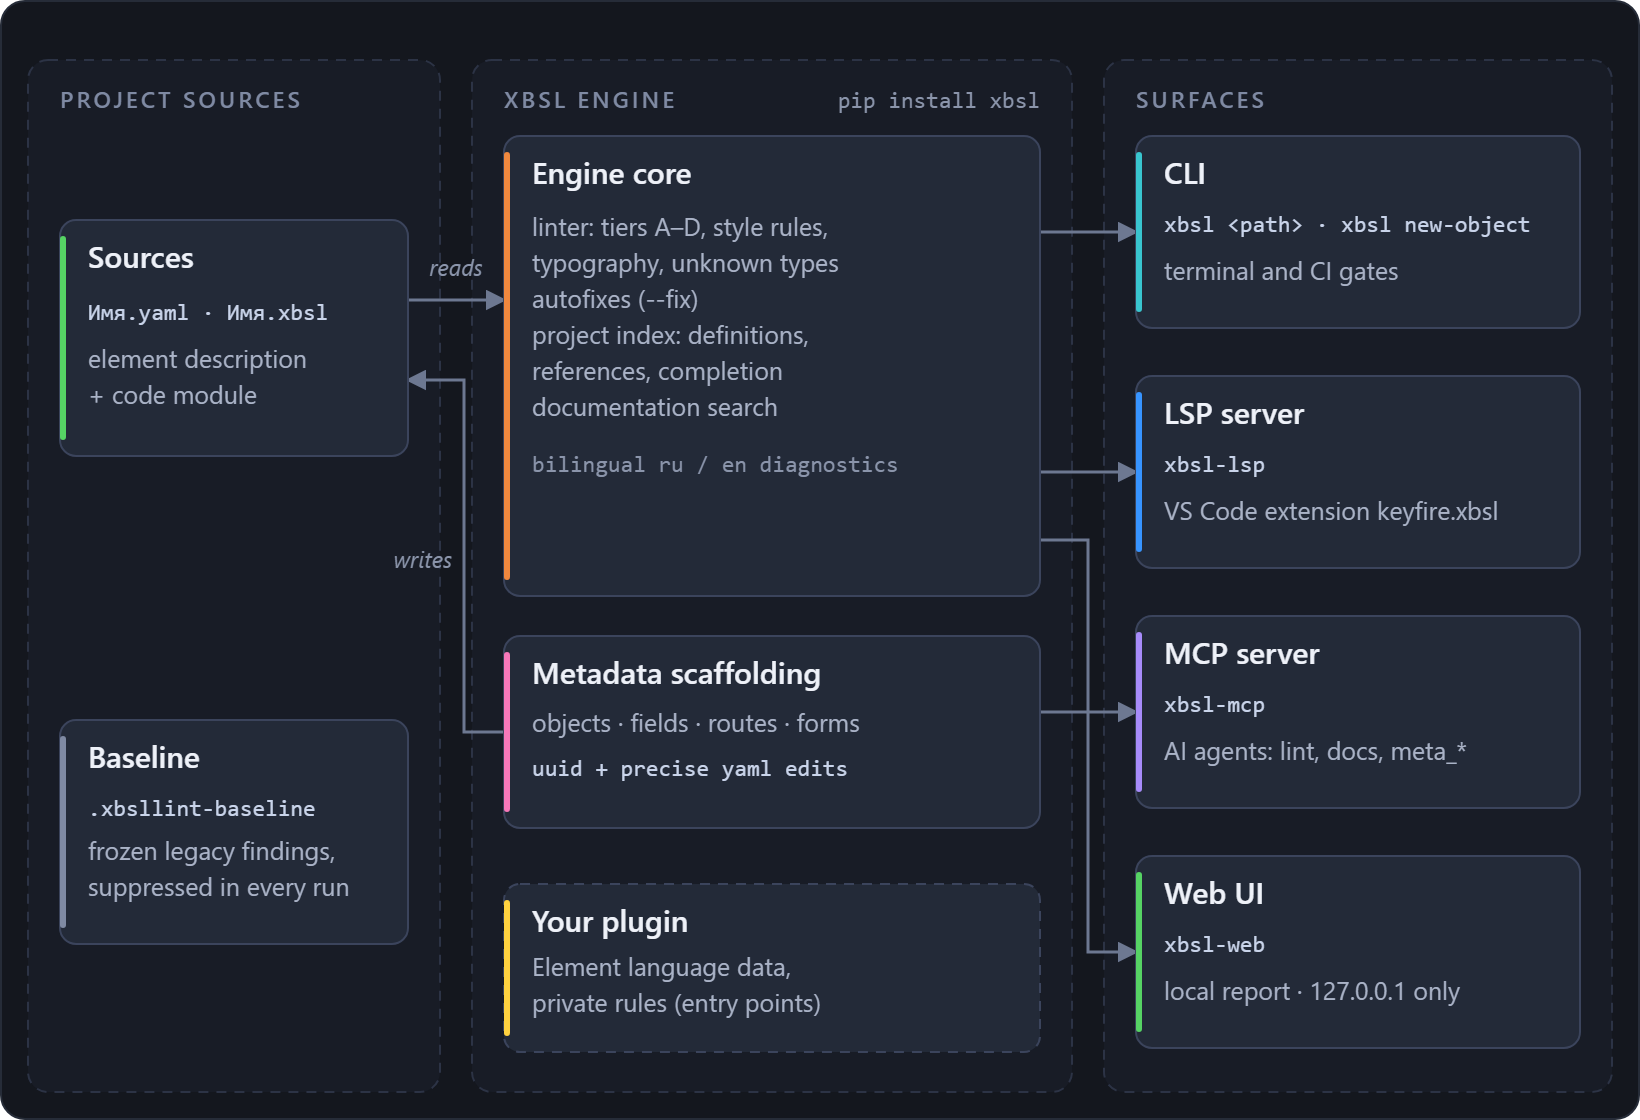
One engine, four surfaces. The core reads the <element>.yaml and <element>.xbsl pairs, and
the scaffolding writes them back. The CLI, the LSP server, the MCP server and the web UI are thin
adapters over that core, so all four see the same rules, data and templates:
Quick start
Step 1 – install.
pip install xbsl # or from a clone of the repository: pip install -e .
Step 2 – generate the language data. The linter judges by tables taken from your 1C:Element distribution: keywords, the stdlib type catalog, the configuration metamodel, terms, the documentation index, the component schema. None of that is bundled in this repository:
xbsl extract --dist "<path to the 1C:Element distribution>"
The command runs every extractor in one go. From a clone the same entry point is
python tools/extract.py, and --only picks a subset of the steps. It detects the platform
version itself and places the data under xbsl/data/element/, a folder listed in .gitignore.
Where the data lives and how a private package can ship it is covered in the
guide.
Step 3 – run.
xbsl path/to/sources        # or: python -m xbsl path/to/sources
xbsl data-diff              # what changed in the platform between two data versions
xbsl translate SOURCES      # rewrite a project into English spellings (a project dictionary)
xbsl self-update            # upgrade to the latest PyPI version, safe with busy exe stubs
The main flags: --list-rules, --fix, --select/--enable/--ignore,
--baseline/--write-baseline, --format text|json|codeclimate, --lang ru|en. The full flag
reference, the --stdin/--index editor modes, the native mypyc wheels and how self-update
works are all in the guide.
What it does
Rules. 235 rules in the base set, in four tiers. A covers structure and the yaml schema.
B covers text and typography conventions. C covers code structure: blocks, brackets,
unused locals, the style/ conventions. D covers semantics against the platform data and the
project itself: every type position in code and yaml, enumeration values, Query{...} block
tables, cross-file consistency, the types of attached .xlib libraries. The full list with
severities and documentation links is in
docs/RULES.md, and xbsl --list-rules
prints it on the spot. What tier D verifies in depth is in
the guide.
Autofixes. --fix applies available edits for the selected rules, including code fixes,
then reports remaining findings. With --baseline, accepted occurrences are protected and the
baseline file is not rewritten. Ambiguous or overlapping edits stay for manual review.
Baseline. You can adopt a rule on an old codebase without cleaning all of it first. Freeze the current findings once, and only new code answers to the rule. The same file records point exclusions with reasons. Details.
Metadata scaffolding. Objects, attributes, routes and forms are created without
hand-written yaml: 33 element kinds, forms generated with real content, a context-aware
rename-object, access-control editing. The same operations are available through the CLI, MCP
and LSP:
xbsl new-object vendor/App/Main Catalog Goods            # the kind in either language
xbsl add-field vendor/App/Main/Goods.yaml <section> Color --type <type>
xbsl add-form . --name Goods                            # object + list forms, registered
xbsl rename-object . Goods Products                     # rename files + update references
The platform is bilingual: an element kind has an English name and a Russian one for the same
thing, and the tool takes either spelling. It resolves the kinds through the term dictionary
extracted from your distribution. Section names of add-field still go in the project's own
language, and xbsl new-object --help lists the kinds it can create.
All subcommands with their options – the guide.
Editors. The VS Code extension
(Marketplace,
Open VSX) gives you syntax highlighting, live and
project-wide diagnostics, go-to-definition and completion, the form designer, a metadata tree and
a deploy button. It runs on xbsl-lsp, a Language Server any LSP-capable editor can spawn
(details).
Code templates. Type the first letters of a construct, press Ctrl+Space, and the whole
construct arrives with its edit points. There are 51 builtin templates, each one parsed by the
linter's own parser, so none of them can insert broken code. Your own live in
.xbsl-templates.json, with a management panel in VS Code. The mechanism and the file format
mirror 1C:EDT.
Details.
Documentation search. tools/extract_docs.py turns the distribution's Element reference
into a local full-text docs.sqlite; the xbsl.docs API and the MCP tools search it.
Details.
MCP server. claude mcp add xbsl -- xbsl-mcp gives an agent linting, documentation search,
type_members and every scaffolding operation as meta_* tools. The agent creates an object and
gets the lint of the written files in one round trip.
Details.
Web interface. xbsl-web – a local page over the same engine: rule toggles, filters,
themes. Details.
CI. The exit code is non-zero only on error-severity findings, so xbsl gates a pipeline
as it is. --format codeclimate feeds the GitLab Code Quality widget. Ready-made GitHub Actions
and GitLab CI jobs are in
the guide.
Extending. Entry points let a private package add rules, ship language data and override
severities without forking the linter. XBSL_NO_PLUGINS=1 turns every plugin off.
Details.
Output language (RU/EN), Element data versions and the order the data root is resolved in are covered in the same guide.
Tests
pip install -e ".[dev]"
pytest
Tests that need the data skip themselves when the data has not been generated.
License
MIT – see LICENSE. Trademarks and data provenance – NOTICE. How to add a rule – CONTRIBUTING.md. Release history – CHANGELOG.md.
1 maintainer

Release files for xbsl 0.110.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| xbsl-0.110.0.tar.gz | 1.9 MB | Details |
Built distributions (wheels)
Total release size: 37.6 MB
Release files / xbsl-0.110.0.tar.gz
| Download URL | xbsl-0.110.0.tar.gz |
|---|---|
| Size | 1.9 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
54cfe14cd90624b50af8e75ee60bb2f5a7737c7d9f41aeab5566a6c3146ae131
|
|
BLAKE2b-256 checksum How to use checksums |
09d328dc3298081ad6110703854312c8909ee5993ff359abfd134c063581b1b8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / xbsl-0.110.0-py3-none-any.whl
| Download URL | xbsl-0.110.0-py3-none-any.whl |
|---|---|
| Size | 1.4 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
e761fe7b8f8d0532be37c627234d6f30261ed3753df4081702ba19bbabcc44a1
|
|
BLAKE2b-256 checksum How to use checksums |
c8994753c8fc29d10286f76b23e7445b22ccdbf20a55c88a1713d04c3beb2e81
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / xbsl-0.110.0-cp314-cp314-win_amd64.whl
| Download URL | xbsl-0.110.0-cp314-cp314-win_amd64.whl |
|---|---|
| Size | 1.6 MB |
| Tags | CPython 3.14 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
3b28887f248b56e158f65ab743c23266e68ebba0baab9df2924069c0a5fe3df9
|
|
BLAKE2b-256 checksum How to use checksums |
e1dfc33d5b8e2a7a7d2d82e9764af6e62490366b4499ac5fdbca9a4bc1d8ba47
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / xbsl-0.110.0-cp314-cp314-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl
| Download URL | xbsl-0.110.0-cp314-cp314-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 1.9 MB |
| Tags | CPython 3.14 Linux glibc 2.17+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
ad4c5d95c588ec270e61c02ced3ed44cad585120a078bf2ea02ebd59a29f7207
|
|
BLAKE2b-256 checksum How to use checksums |
19dc689764bd6fa77c5d8c6cd945e884d3447948e16570cffca08b9e15804ff6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / xbsl-0.110.0-cp314-cp314-macosx_11_0_arm64.whl
| Download URL | xbsl-0.110.0-cp314-cp314-macosx_11_0_arm64.whl |
|---|---|
| Size | 1.7 MB |
| Tags | CPython 3.14 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
6bddee3f959b9f4bf247f03bd91f67fc32bafd27993d1b07dc706ea4cccf0562
|
|
BLAKE2b-256 checksum How to use checksums |
d8ffd122e56c9ca264d4ce2436040cd4c0a0260082e6eafc7f51b597d7cb76d9
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / xbsl-0.110.0-cp314-cp314-macosx_10_15_x86_64.whl
| Download URL | xbsl-0.110.0-cp314-cp314-macosx_10_15_x86_64.whl |
|---|---|
| Size | 1.7 MB |
| Tags | CPython 3.14 macOS 10.15+ x86-64 |
|
SHA-256 checksum How to use checksums |
2d6354f7c8a28021b40235725d05dbbb536a2b63097fe7d1fe47f8b890aaf16d
|
|
BLAKE2b-256 checksum How to use checksums |
adbcfb3e4c53c76ab202776780b45106463e25768af37f7b5d4880d2c026876b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / xbsl-0.110.0-cp313-cp313-win_amd64.whl
| Download URL | xbsl-0.110.0-cp313-cp313-win_amd64.whl |
|---|---|
| Size | 1.6 MB |
| Tags | CPython 3.13 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
44bcbda9d22a874205155fb5e2a4fd4dd443d0098d320277304f9a004b309a60
|
|
BLAKE2b-256 checksum How to use checksums |
e9655515e424f57abce481b85d6a7a422b9fc5b09186c07fb95b44e78cb4e743
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / xbsl-0.110.0-cp313-cp313-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl
| Download URL | xbsl-0.110.0-cp313-cp313-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 1.9 MB |
| Tags | CPython 3.13 Linux glibc 2.17+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
1a30e80d055135b459f31d5dd8e610b468a2343fb7bde7cfd111eaef96ae3504
|
|
BLAKE2b-256 checksum How to use checksums |
3cf382df71609f551723d8b80887f710368a5ef645e3edb5c361f48149cc59d2
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / xbsl-0.110.0-cp313-cp313-macosx_11_0_arm64.whl
| Download URL | xbsl-0.110.0-cp313-cp313-macosx_11_0_arm64.whl |
|---|---|
| Size | 1.7 MB |
| Tags | CPython 3.13 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
daedabeec4ab8a3a655375d515064cb90d9f5b11b3ab69c9fea6ca2b8edec906
|
|
BLAKE2b-256 checksum How to use checksums |
b60021041156d6424181288ee8381be0db9c0715b3facd4aa0b6b89f31e18a99
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / xbsl-0.110.0-cp313-cp313-macosx_10_13_x86_64.whl
| Download URL | xbsl-0.110.0-cp313-cp313-macosx_10_13_x86_64.whl |
|---|---|
| Size | 1.7 MB |
| Tags | CPython 3.13 macOS 10.13+ x86-64 |
|
SHA-256 checksum How to use checksums |
f2969560845aeb7469c1059e8994a5f9f38139f0ff5c126cbe7587a0491342f9
|
|
BLAKE2b-256 checksum How to use checksums |
43fd9d9acd867dd3f107009b642c712ed7dc581a42607068221b931636f26ce7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / xbsl-0.110.0-cp312-cp312-win_amd64.whl
| Download URL | xbsl-0.110.0-cp312-cp312-win_amd64.whl |
|---|---|
| Size | 1.6 MB |
| Tags | CPython 3.12 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
fd371ac7d181528103616efeebae331438e8b62c802961b0f68e1223ab168bb5
|
|
BLAKE2b-256 checksum How to use checksums |
f55169ac421c69214b552b35d65230cf75daa53319f57b465a3eff53caf99de4
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / xbsl-0.110.0-cp312-cp312-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl
| Download URL | xbsl-0.110.0-cp312-cp312-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 1.9 MB |
| Tags | CPython 3.12 Linux glibc 2.17+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
9346fa0075de10e2319fc8644d71cec74510e98b6c31f77e13d518798566daa1
|
|
BLAKE2b-256 checksum How to use checksums |
b463d1fab3387b4415d6e02bd6fdb45685e9d52a985472a80fc910a402bdb84c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / xbsl-0.110.0-cp312-cp312-macosx_11_0_arm64.whl
| Download URL | xbsl-0.110.0-cp312-cp312-macosx_11_0_arm64.whl |
|---|---|
| Size | 1.7 MB |
| Tags | CPython 3.12 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
11e8c7753e81d7faa5f5b366f480beb549510725364d5cf2ef740a372fafae95
|
|
BLAKE2b-256 checksum How to use checksums |
8b4da4b45bc4984a39683d8c409da4b6b4b6a578bf8a1b7af4fb3edb5c526714
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / xbsl-0.110.0-cp312-cp312-macosx_10_13_x86_64.whl
| Download URL | xbsl-0.110.0-cp312-cp312-macosx_10_13_x86_64.whl |
|---|---|
| Size | 1.7 MB |
| Tags | CPython 3.12 macOS 10.13+ x86-64 |
|
SHA-256 checksum How to use checksums |
bdd0ec0d140ce601a020014b9216de39a40deb39f029829382baeb37e1d38fea
|
|
BLAKE2b-256 checksum How to use checksums |
04bdbc229f4c104bcb5275be121d7625967aa5f9ce4bd2e481a1493ddc939a51
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / xbsl-0.110.0-cp311-cp311-win_amd64.whl
| Download URL | xbsl-0.110.0-cp311-cp311-win_amd64.whl |
|---|---|
| Size | 1.6 MB |
| Tags | CPython 3.11 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
0d3bca7e287fefb6c5f2a4cc3454802e62f8d23b52c8b07a5ea21189491912ba
|
|
BLAKE2b-256 checksum How to use checksums |
e793c4a996e138ae49d8fcf824a7e44de3d8d8cdee3932c151b37ab00fdf47ca
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / xbsl-0.110.0-cp311-cp311-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl
| Download URL | xbsl-0.110.0-cp311-cp311-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 1.9 MB |
| Tags | CPython 3.11 Linux glibc 2.17+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
01d8391044d72c4fbfb7ba4cb3b6f73f20f3e0d39e8d20f63bdda6566ab74c6a
|
|
BLAKE2b-256 checksum How to use checksums |
26d106a52a0efca56610bdcc01ec1fd0899ab8a88dc35468b522eabb8082e005
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / xbsl-0.110.0-cp311-cp311-macosx_11_0_arm64.whl
| Download URL | xbsl-0.110.0-cp311-cp311-macosx_11_0_arm64.whl |
|---|---|
| Size | 1.7 MB |
| Tags | CPython 3.11 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
aae20b986694832ba5b50ae2f8aa0e7bf9a2553ff4ee9f924ed3cdb42b29d70d
|
|
BLAKE2b-256 checksum How to use checksums |
0293abcdd9c4b303f7773d8fc37099031784bb593531f72b27fb66486ea87a04
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / xbsl-0.110.0-cp311-cp311-macosx_10_9_x86_64.whl
| Download URL | xbsl-0.110.0-cp311-cp311-macosx_10_9_x86_64.whl |
|---|---|
| Size | 1.7 MB |
| Tags | CPython 3.11 macOS 10.9+ x86-64 |
|
SHA-256 checksum How to use checksums |
7f98954e7cf25a389fbcee27a1b2f3a812bfba863d219c41a0a9df79817f410e
|
|
BLAKE2b-256 checksum How to use checksums |
339fb95a8cece2fb50117ea3e8fc135c9069d9344d9146682322132cd988e362
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / xbsl-0.110.0-cp310-cp310-win_amd64.whl
| Download URL | xbsl-0.110.0-cp310-cp310-win_amd64.whl |
|---|---|
| Size | 1.6 MB |
| Tags | CPython 3.10 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
bd46e7ba7dcb54c3aead38f878a530b85f53f7abc1f1cda61f3b96f9e49efa16
|
|
BLAKE2b-256 checksum How to use checksums |
7607f10798fc8fa026ed294e097a9acd997d539191af1fd3254a2d0dd38748af
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / xbsl-0.110.0-cp310-cp310-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl
| Download URL | xbsl-0.110.0-cp310-cp310-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 1.9 MB |
| Tags | CPython 3.10 Linux glibc 2.17+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
b1f6d8dec5c67365c332a146989464de86804fa8d3c08b895e04ee058638a242
|
|
BLAKE2b-256 checksum How to use checksums |
3d5c6eb204abba92b5dd82d591c85de9373e5a7bf49cdee59e884844b697f42b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / xbsl-0.110.0-cp310-cp310-macosx_11_0_arm64.whl
| Download URL | xbsl-0.110.0-cp310-cp310-macosx_11_0_arm64.whl |
|---|---|
| Size | 1.7 MB |
| Tags | CPython 3.10 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
8156a0d8a49b6f056b6e0d96ba5bb28b835a8433c6876459a6f6631f2515e2ff
|
|
BLAKE2b-256 checksum How to use checksums |
d3cde3add7a8038d68876c4e313e201d7f4e41af9d93d500d62ee880c51c666d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / xbsl-0.110.0-cp310-cp310-macosx_10_9_x86_64.whl
| Download URL | xbsl-0.110.0-cp310-cp310-macosx_10_9_x86_64.whl |
|---|---|
| Size | 1.7 MB |
| Tags | CPython 3.10 macOS 10.9+ x86-64 |
|
SHA-256 checksum How to use checksums |
9f30cabe997c3cf2c13b61a21cc4890e8b1102e99d4b06a9963e3d40c32464d2
|
|
BLAKE2b-256 checksum How to use checksums |
0be1356cc6a66c70041d9be86ab573063c086c0baff41fc27c62216972a97d9b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency log













