
yonder
your site, over yonder
Open the site running on your localhost from your phone, your iPad, or a friend's laptop on the same Wi-Fi. One command, one QR code, nothing to install on the other device.
Install
macOS / Linux, any distro
curl -fsSL https://raw.githubusercontent.com/dpologdvinity/yonder/master/install.sh | sh
Homebrew (macOS and Linux)
brew install dpologdvinity/tap/yonder
Debian / Ubuntu (apt)
sudo curl -fsSLo /usr/share/keyrings/yonder.gpg https://dpologdvinity.github.io/packages/yonder.gpg
echo "deb [signed-by=/usr/share/keyrings/yonder.gpg] https://dpologdvinity.github.io/packages/apt ./" | sudo tee /etc/apt/sources.list.d/yonder.list
sudo apt update && sudo apt install yonder
Fedora / RHEL (dnf)
sudo curl -fsSLo /etc/yum.repos.d/yonder.repo https://dpologdvinity.github.io/packages/yonder.repo
sudo dnf install yonder
Arch Linux (pacman)
curl -fsSL https://dpologdvinity.github.io/packages/yonder.asc | sudo pacman-key --add -
sudo pacman-key --lsign-key 282804EB5779EA7EFFCF8308097AF7F74B2F93E5
printf '\n[yonder]\nServer = https://dpologdvinity.github.io/packages/arch/$arch\n' | sudo tee -a /etc/pacman.conf
sudo pacman -Sy yonder
Windows (Scoop)
scoop bucket add yonder https://github.com/dpologdvinity/scoop-bucket
scoop install yonder
npm / yarn / pip
npm install -g yonder-cli     # or: yarn global add yonder-cli
pip install yonder-cli        # or: uv tool install yonder-cli
Go
go install github.com/dpologdvinity/yonder@latest
Or download a binary, .deb, .rpm or Arch package from Releases.
Usage
yonder <port>             share localhost:<port> on the LAN
yonder <path>             share a file or folder
yonder <folder> --upload  also let other devices send files into the folder
yonder <port> --listen N  use proxy port N
yonder <port> --open      share without the access token
yonder --version
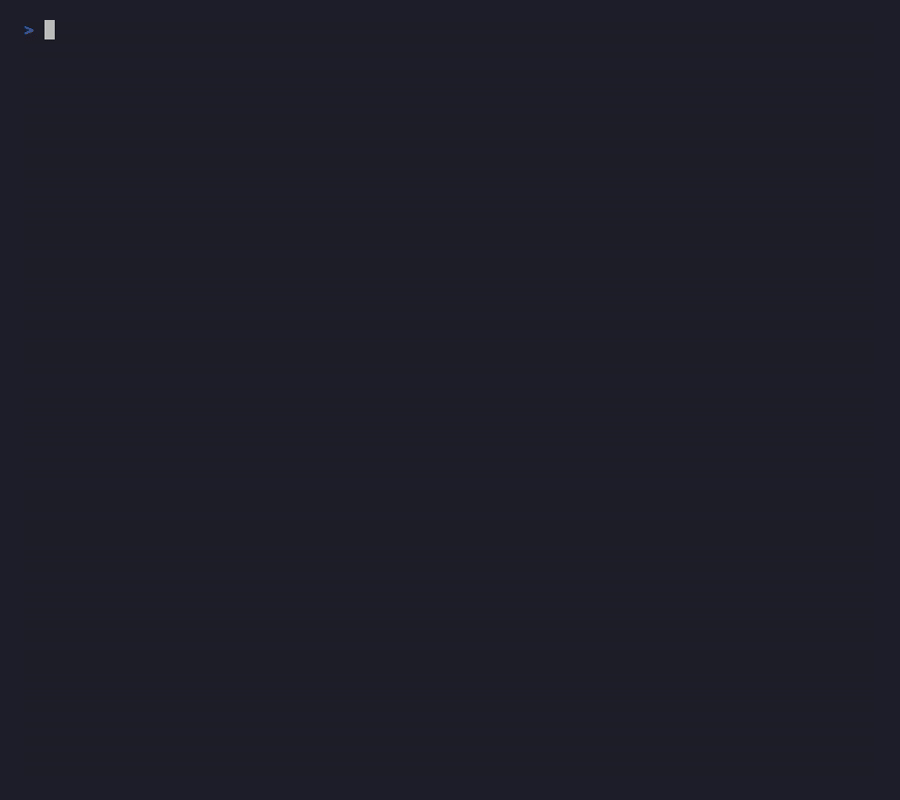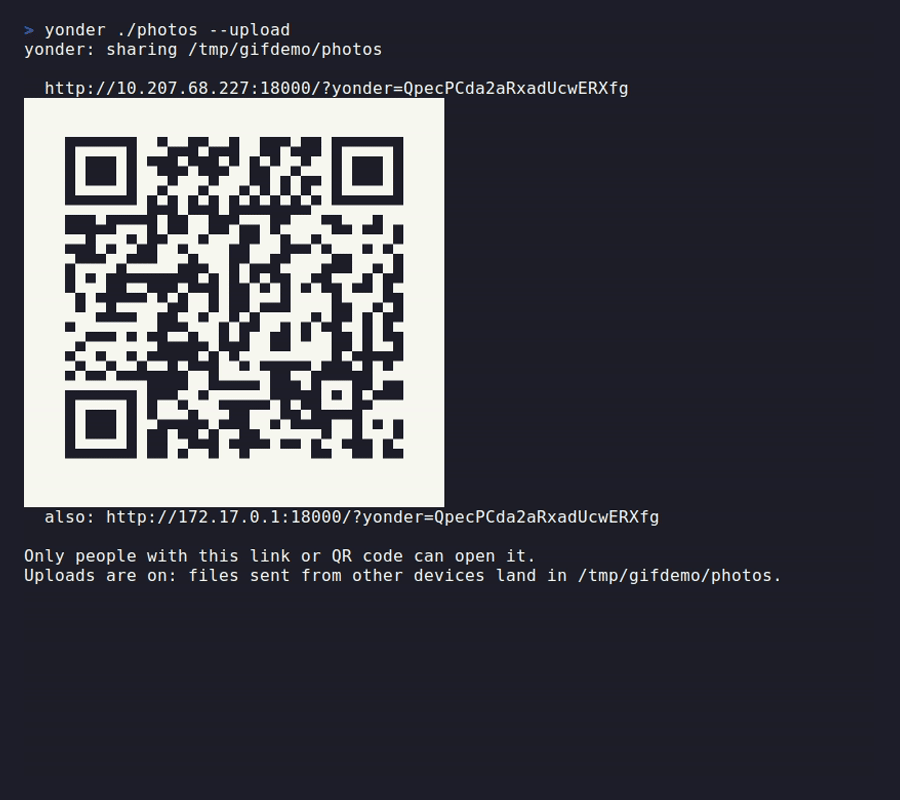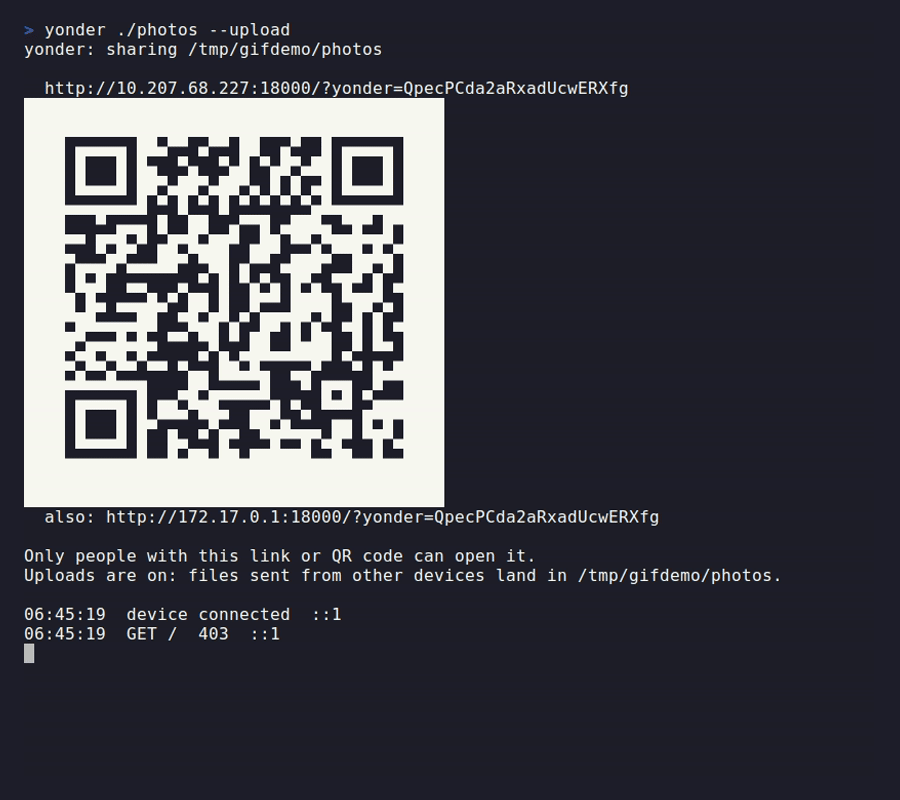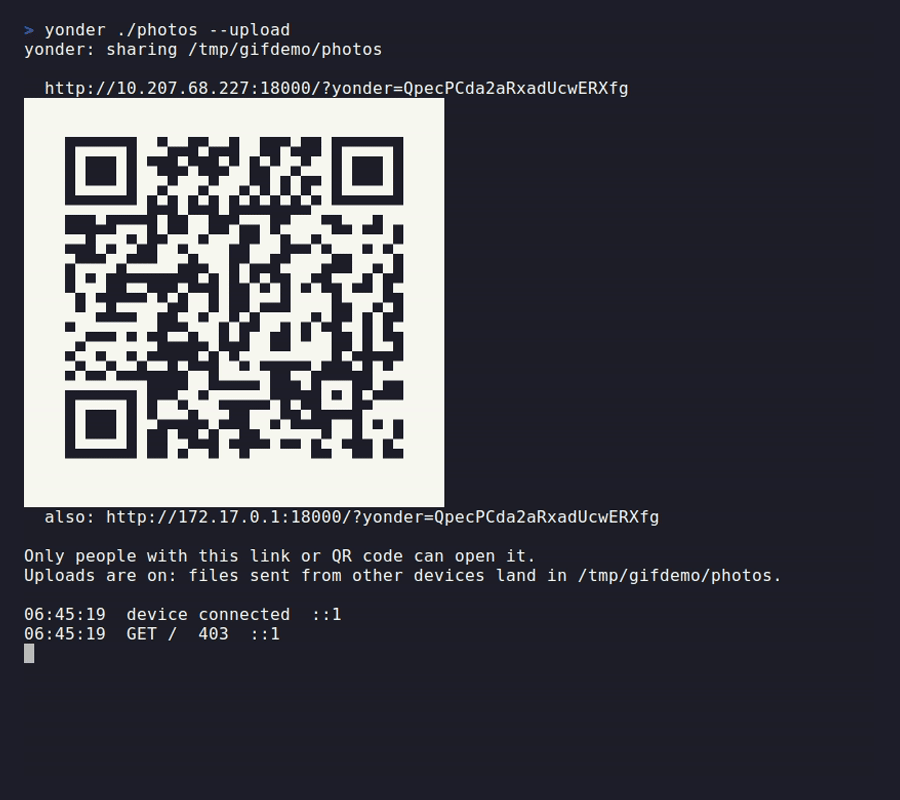
$ yonder 3000
yonder: sharing localhost:3000

  http://192.168.1.20:13000/?yonder=…
  <QR code>

Only people with this link or QR code can open it.
Scan the QR code or type the URL on the other device. Each request shows up as one log line.
yonder runs a small proxy in front of your dev server, so you don't need to change its config:
- It works with servers that only listen on
127.0.0.1or::1. - It rewrites the
HostandOriginheaders, so servers that check them (Vite, webpack, Next.js) accept the request. - Hot reload keeps working: WebSockets and server-sent events pass through.
- The proxy port is your port + 10000, so it stays the same across restarts (handy for firewall rules). The access token does not: after a restart, scan the new QR code.
Share files
yonder ./photos        # a folder: the phone gets a list of files to tap and download
yonder notes.pdf       # one file: nothing else in its folder is reachable
Same QR code and token as port sharing. The default port is 18000.
- Hidden files and folders (
.env,.git,.ssh, anything starting with.) are never listed or served. - Symlinks inside the shared folder are skipped, and
..can't reach outside it. - Share a dedicated folder, not your home directory.
- Add
--uploadto let the other device send files into the folder: the page gets an Upload button (on a phone it opens the photo picker or Files). Existing files are never overwritten (photo (1).jpg), hidden or path-like names are refused, and one upload is capped at 4 GB. Uploads are off unless you pass the flag. - A folder named like a number is a port to yonder: use
yonder ./3000.
Is it safe?
The link and QR code carry a secret token. Anyone without it gets a 403 and never reaches your app. The first visit swaps the token for a cookie, so it disappears from the address bar. Every restart makes a new token, which cuts off old links. Only the one port you name is shared.
--openturns the token off. Use it only on networks you trust.- yonder speaks plain HTTP. On open (passwordless) Wi-Fi, or on WPA2 Wi-Fi with a shared password, others on the network can capture traffic and copy the token or cookie. Avoid sharing private data there. Enterprise Wi-Fi with per-user logins and WPA3 protect each device's traffic.
- Stop sharing with Ctrl-C.
Known limitations
- Your app's own code may hardcode
localhost. A frontend calling an API athttp://localhost:8080fails on the phone, because therelocalhostis the phone. Use relative API URLs or your dev server's proxy. - Response bodies are not rewritten. Absolute
http://localhost:<port>links inside HTML or JS stay broken. http://localhostcounts as a secure context;http://192.168.x.xdoes not. Service workers, camera, geolocation, clipboard andcrypto.subtlewon't work on the other device yet.- Guest, campus and café networks often block device-to-device traffic. If the other device can't connect, try a phone hotspot.
Firewalls
The first time yonder listens for connections, your OS may block or ask:
- Windows: allow
yonder.exein the Windows Defender Firewall prompt. - macOS: allow incoming connections when the application firewall asks.
- WSL (mirrored mode): the Hyper-V firewall blocks inbound traffic to WSL by default, so the other device times out. See the WSL section below.
If the other device can't connect, watch yonder's output. No device connected line means the connection never reached yonder: a firewall or the network dropped it.
WSL
In WSL's default NAT mode, other devices can't reach WSL at all; yonder prints a hint when it detects this. Either set networkingMode=mirrored under [wsl2] in %UserProfile%\.wslconfig and run wsl --shutdown, or run the Windows build, yonder.exe.
In mirrored mode, open yonder's port once in an admin PowerShell. For yonder 8000 the port is 18000:
New-NetFirewallHyperVRule -Name yonder -DisplayName yonder -Direction Inbound -VMCreatorId '{40E0AC32-46A5-438A-A0B2-2B479E8F2E90}' -Protocol TCP -LocalPorts 18000
New-NetFirewallRule -DisplayName yonder -Direction Inbound -Protocol TCP -LocalPort 18000 -Action Allow -Profile Any
Remove them later with Remove-NetFirewallHyperVRule -Name yonder and Remove-NetFirewallRule -DisplayName yonder.
License
MIT
1 maintainer

Metadata
1 maintainer
Release files for yonder-cli 0.4.3
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Built distributions (wheels)
| File | Reset | |||
|---|---|---|---|---|
| yonder_cli-0.4.3-py3-none-win_arm64.whl | Python 3 | none | Windows ARM64 | Details |
| yonder_cli-0.4.3-py3-none-win_amd64.whl | Python 3 | none | Windows x86-64 | Details |
| yonder_cli-0.4.3-py3-none-manylinux_2_17_x86_64.manylinux2014_x86_64.musllinux_1_1_x86_64.whl | Python 3 | none | Linux musl 1.1+ x86-64, Linux glibc 2.17+ x86-64 | Details |
| yonder_cli-0.4.3-py3-none-manylinux_2_17_aarch64.manylinux2014_aarch64.musllinux_1_1_aarch64.whl | Python 3 | none | Linux glibc 2.17+ ARM64, Linux musl 1.1+ ARM64 | Details |
| yonder_cli-0.4.3-py3-none-macosx_12_0_x86_64.whl | Python 3 | none | macOS 12.0+ x86-64 | Details |
| yonder_cli-0.4.3-py3-none-macosx_12_0_arm64.whl | Python 3 | none | macOS 12.0+ ARM64 | Details |
Total release size: 23.6 MB
Release files / yonder_cli-0.4.3-py3-none-win_arm64.whl
| Download URL | yonder_cli-0.4.3-py3-none-win_arm64.whl |
|---|---|
| Size | 3.7 MB |
| Tags | Python 3 Windows ARM64 |
|
SHA-256 checksum How to use checksums |
5a25d283e3d4c9c5dc926333e305818a133d29ebbe6544928c5b662ae084a4ca
|
|
BLAKE2b-256 checksum How to use checksums |
1c9aac6cc34390504c97dc2fea37002dad9b18f7a6e8a5c7f9b151ff824eb90c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / yonder_cli-0.4.3-py3-none-win_amd64.whl
| Download URL | yonder_cli-0.4.3-py3-none-win_amd64.whl |
|---|---|
| Size | 4.2 MB |
| Tags | Python 3 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
bc778c1fc00111700391a2d0a0e6beb712e80f16d72117b7f1e2aeb0a30fc676
|
|
BLAKE2b-256 checksum How to use checksums |
011585962b0ebce86afb5288fcc2512c3bb6efd97a3ce7dbd8b355293a3372d0
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / yonder_cli-0.4.3-py3-none-manylinux_2_17_x86_64.manylinux2014_x86_64.musllinux_1_1_x86_64.whl
| Download URL | yonder_cli-0.4.3-py3-none-manylinux_2_17_x86_64.manylinux2014_x86_64.musllinux_1_1_x86_64.whl |
|---|---|
| Size | 4.1 MB |
| Tags | Linux glibc 2.17+ x86-64 Linux musl 1.1+ x86-64 Python 3 |
|
SHA-256 checksum How to use checksums |
3e0cecdc73747ea84deaaacf8f31c91b595c7c19ad787b907da8768191a80deb
|
|
BLAKE2b-256 checksum How to use checksums |
5a8bd3546a354860c54e7abbe12de7a122f786aca5937aedd50b40e96a0746d9
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / yonder_cli-0.4.3-py3-none-manylinux_2_17_aarch64.manylinux2014_aarch64.musllinux_1_1_aarch64.whl
| Download URL | yonder_cli-0.4.3-py3-none-manylinux_2_17_aarch64.manylinux2014_aarch64.musllinux_1_1_aarch64.whl |
|---|---|
| Size | 3.7 MB |
| Tags | Linux glibc 2.17+ ARM64 Linux musl 1.1+ ARM64 Python 3 |
|
SHA-256 checksum How to use checksums |
259d37393924fb49fc194d4b0b341b15f6d85ba00355aafcf41337e3e226183b
|
|
BLAKE2b-256 checksum How to use checksums |
c8fd5a95afada08315cf11521a6d70018b4d03f459accf70be7930117e0e8852
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / yonder_cli-0.4.3-py3-none-macosx_12_0_x86_64.whl
| Download URL | yonder_cli-0.4.3-py3-none-macosx_12_0_x86_64.whl |
|---|---|
| Size | 4.1 MB |
| Tags | Python 3 macOS 12.0+ x86-64 |
|
SHA-256 checksum How to use checksums |
11b76bd14639c25d66412c6fcc93c02486820be98e2223d9c01842ef3eb0b9bc
|
|
BLAKE2b-256 checksum How to use checksums |
799758c4ada2ca9b9ef1290bc669c5b0f12f424246eb0316ff4ba67883738845
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / yonder_cli-0.4.3-py3-none-macosx_12_0_arm64.whl
| Download URL | yonder_cli-0.4.3-py3-none-macosx_12_0_arm64.whl |
|---|---|
| Size | 3.8 MB |
| Tags | Python 3 macOS 12.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
a6fc7674ed04d313c025c53be7c7819775cf133a94901f11d61fa734b90441c2
|
|
BLAKE2b-256 checksum How to use checksums |
e16f63c1df8c6ce255913a2406a0ba103fc618cb7c065c0265c54b3ac9ad945d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logSecurity for yonder-cli 0.4.3
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 6 files in this release have been uploaded with provenance metadata.
Attestation for yonder_cli-0.4.3-py3-none-win_arm64.whl
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














