
zombieports
What's running on port 3000? zombieports shows every port listening on your machine, which project started it, how long it's been up, and which ones look forgotten. One key kills them.
uvx zombieports
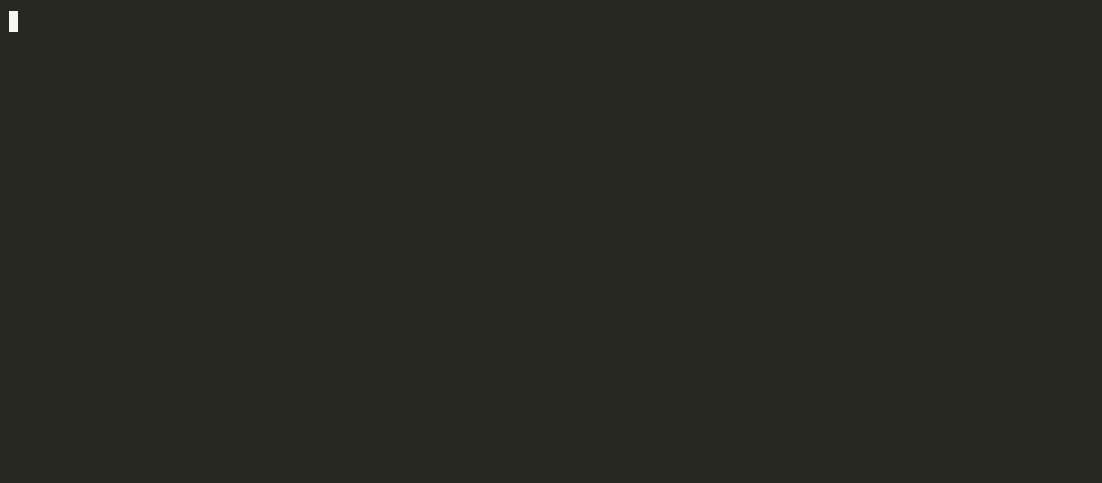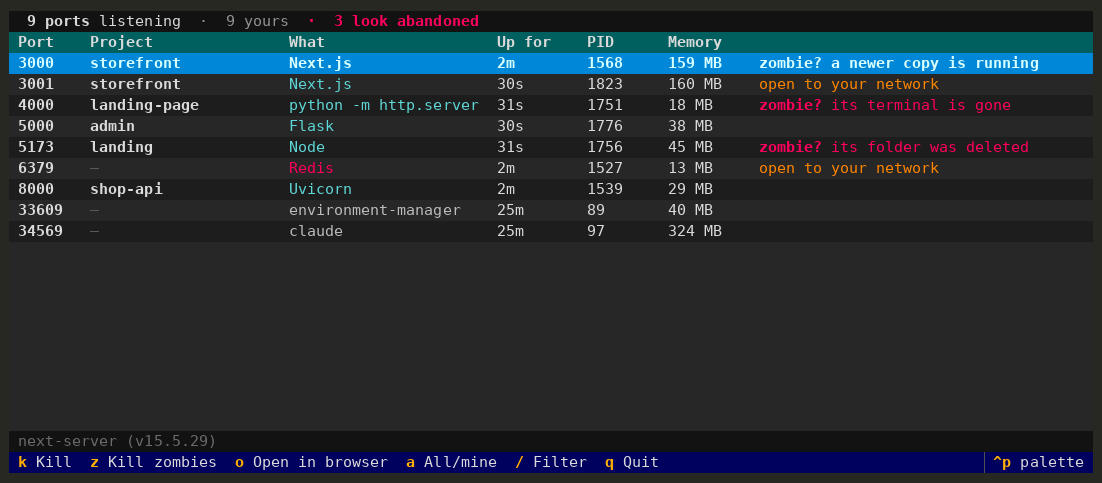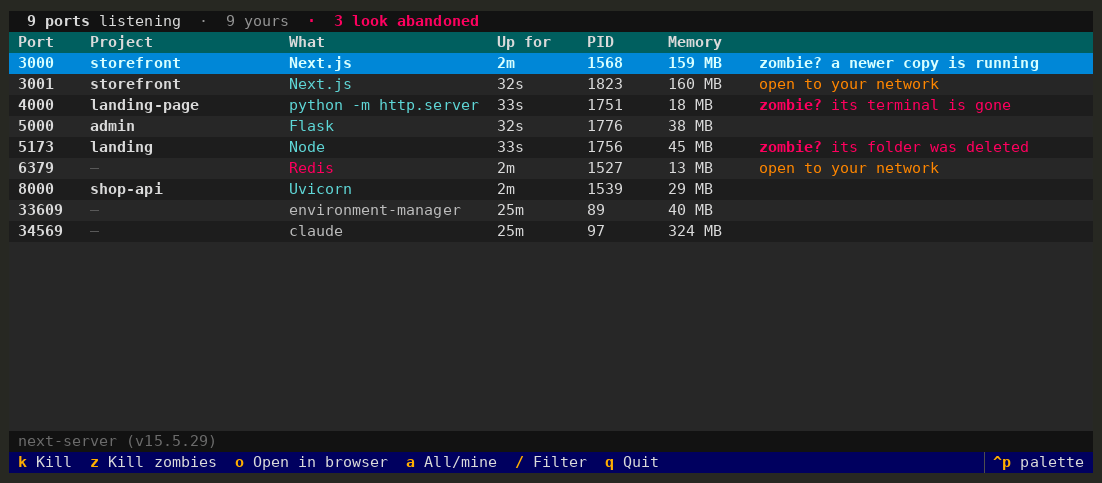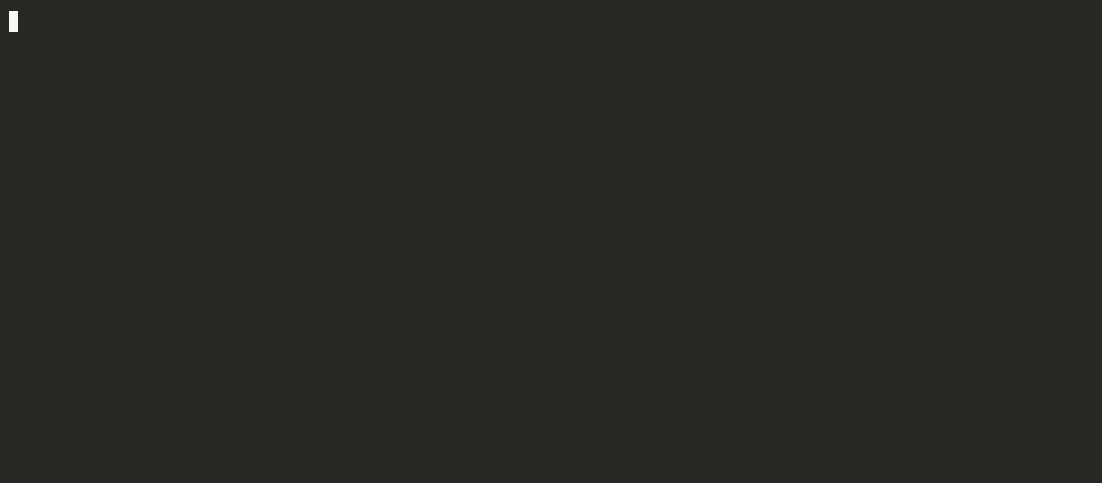
Real dev servers (Next.js, Flask, Uvicorn, Redis, a forgotten http.server) running on Linux. Pressing z kills the three that look abandoned.
You know the drill: Error: listen EADDRINUSE :::3000, then lsof -i :3000, then squinting at a PID, then kill -9. Or the Vite server from last Tuesday that's still holding 5173. zombieports puts all of it in one screen.
What it shows
| Column | |
|---|---|
| Port | Every TCP port in LISTEN state |
| Project | The project the server was started from: package.json's name, or the folder holding pyproject.toml, Cargo.toml, go.mod, .git… |
| What | Recognises 50+ things from the command line: Next.js, Vite, Nuxt, Astro, Storybook, Uvicorn, Django, Flask, Rails, Jupyter, Postgres, Redis, Docker, Ollama, AirPlay Receiver (the reason port 5000 is taken on a Mac)… |
| Up for / PID / Memory | How long it's been running and what it costs |
| Status | open to your network when a dev server or database listens on all interfaces, and zombie? when it looks abandoned |
What counts as a zombie
A dev server started from one of your projects is flagged when:
- its terminal is gone: the shell that started it exited and it got re-parented to
init/launchd - its folder was deleted: it's serving a project that no longer exists
- a newer copy is running: two
next devservers for the same project, the older one is almost certainly forgotten - it's been up for more than a day
Databases, Docker, and apps the OS launched are never flagged.
Keys
| Key | |
|---|---|
k / Delete |
Stop the selected server and its child processes (SIGTERM, then SIGKILL after 3 s) |
K |
Force kill straight away |
z |
Kill every zombie (asks first) |
o |
Open http://localhost:PORT in your browser |
a |
Show other users' and system listeners too |
/ |
Filter by port, project, or kind |
q |
Quit |
Without the UI
zombieports list                # print the table
zombieports kill 3000 5173      # free some ports
zombieports kill --zombies      # free every abandoned one
zombieports --json              # for scripts
Platforms
macOS, Linux and Windows, no sudo needed for your own processes. It uses psutil rather than parsing lsof/netstat. Other users' and system processes are listed with -a, but you can only kill your own.
Install
uvx zombieports          # run without installing
pipx install zombieports # or install it
Requires Python 3.9+. Built with Textual.
License
MIT
1 maintainer

Metadata
1 maintainer
Release files for zombieports 0.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| zombieports-0.1.0.tar.gz | 13.1 kB | With provenance | Details for zombieports-0.1.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| zombieports-0.1.0-py3-none-any.whl | Python 3 | none | any | Details for zombieports-0.1.0-py3-none-any.whl |
Total release size: 26.4 kB
Release files / zombieports-0.1.0.tar.gz
| Download URL | zombieports-0.1.0.tar.gz |
|---|---|
| Size | 13.1 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
a4c0492ebf4875d456e3a5061e67c345465da62aecea5aa4b11da1044d8ec747
|
|
BLAKE2b-256 checksum How to use checksums |
3feaec5fa7a27f949503a25651438fa8df74a526908bd1d73b57d77523b346fa
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logRelease files / zombieports-0.1.0-py3-none-any.whl
| Download URL | zombieports-0.1.0-py3-none-any.whl |
|---|---|
| Size | 13.3 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
7ec52b90bd6698843f7671d4b775db12919d14424a12917c08e9e9ff7e6f2c56
|
|
BLAKE2b-256 checksum How to use checksums |
4f31b95c596af1531b58c90b3705f0d7571a8831e809fc5b45dde0972af7eb38
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logSecurity for zombieports 0.1.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for zombieports-0.1.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













