
A11
Build AI applications like normal software.
A11 is the open-source runtime for connecting models, tools and interfaces while keeping your architecture. It gives ordinary asynchronous code named streams, concurrency, tools and local-to-remote execution, and exposes the running application to Studio.
The Python API runs on a native C++20 runtime. TypeScript, Kotlin, C++ and Flow use the same action boundary where an application needs another language or process.
- Named streams instead of mixed provider events. Read model text, reasoning, tool activity, progress, and durable interaction state from separate ports.
- The same action contract locally and remotely. Move a handler to a GPU host, browser, or service without changing its inputs and outputs.
- Deterministic runtime composition with Flow. Check and load compositions at runtime with defined concurrency, draining, deadlines, cancellation, and error propagation.
Run the first action · Try the live research agent · Read the documentation · Star A11
Try A11 live
The hosted parallel research agent plans a topic, searches the web for each brief, reviews the returned evidence concurrently, and streams a cited report to the browser. Its default model and search backends need no visitor account or API key.
Run your first streaming action
Install the core runtime on Python 3.11 or later:
python -m venv .venv
source .venv/bin/activate
pip install a11-kit
Save this as quickstart.py. The function signature becomes an action schema,
and its asynchronous iterator becomes a named streaming output:
import asyncio
from collections.abc import AsyncIterator

import a11


REGISTRY = a11.ActionRegistry()


@REGISTRY.action(name="split-words", output="words")
async def split_words(text: str) -> AsyncIterator[str]:
    """Emit the words in a line as they become available."""
    for word in text.split():
        yield word


async def main() -> None:
    action = REGISTRY.make_action("split-words")
    await action["text"].finalize("named streams arrive early")
    action.run()

    async for word in action["words"]:
        print(word)
    await action.wait()


asyncio.run(main())
Run it:
python quickstart.py
The output port streams four values and then closes successfully. The same
REGISTRY can be served over WebSocket, HTTP SSE, or WebRTC; callers still use
the text and words ports.
Add model providers when the application needs them. With Ollama already running locally:
pip install "a11-kit[llm]"
a11 chat --provider ollama --no-voice --no-shell-tools
a11 chat reuses a gateway at the default endpoint, or starts one for the
duration of the chat with the current directory as its coding workspace.
--cwd PATH selects another workspace for a new gateway. An explicit
--gateway URL must be reachable.
In a coding chat, /sandbox unrestricted grants host filesystem access and
disables kernel process confinement. /sandbox workspace-write or
/sandbox read-only restores confinement. Approval remains a separate setting
(/approval suggest|auto). Sandbox changes affect subsequent tool calls for
all clients of that gateway, not already-running processes.
Studio and IDE clients can call the UI-only configure_coding_agent action
with sandbox_mode (read-only, workspace-write, or unrestricted) and/or
approval_mode (suggest or auto). Omitted fields keep their current values;
the result contains approval_mode, sandbox_ceiling, and network. This
control is excluded from the coding agent's model-facing action list.
Input questions appear above the TUI composer. Use Up/Down to select and Enter
to answer, or type a response when free text is allowed. An output-area status
line shows Working during model calls and Waiting for input while a
question is pending.
Add capabilities incrementally
Streaming. An asynchronous iterator yields values before it finishes. Named outputs give model text, reasoning, progress and structured values their own interfaces. The caller reads those streams and checks the action's final status separately.
Concurrency. Use ordinary Python tasks or C++ runtime primitives for independent work. Use nested A11 actions when the runtime should understand a parent/child relationship and propagate cancellation.
Tools. Expose registered actions to model calls through the SDK, or serve the same registry through MCP. The application still owns validation, authorization and policy.
Remote execution. Serve a registry from another process or machine. The caller configures a connection and calls the action; the handler's input and output contract stays stable.
Flow is available when an application needs a composition expressed as data. It is optional: model APIs, MCP, LangGraph and existing application code can remain part of the stack.
Inspect the work with Studio
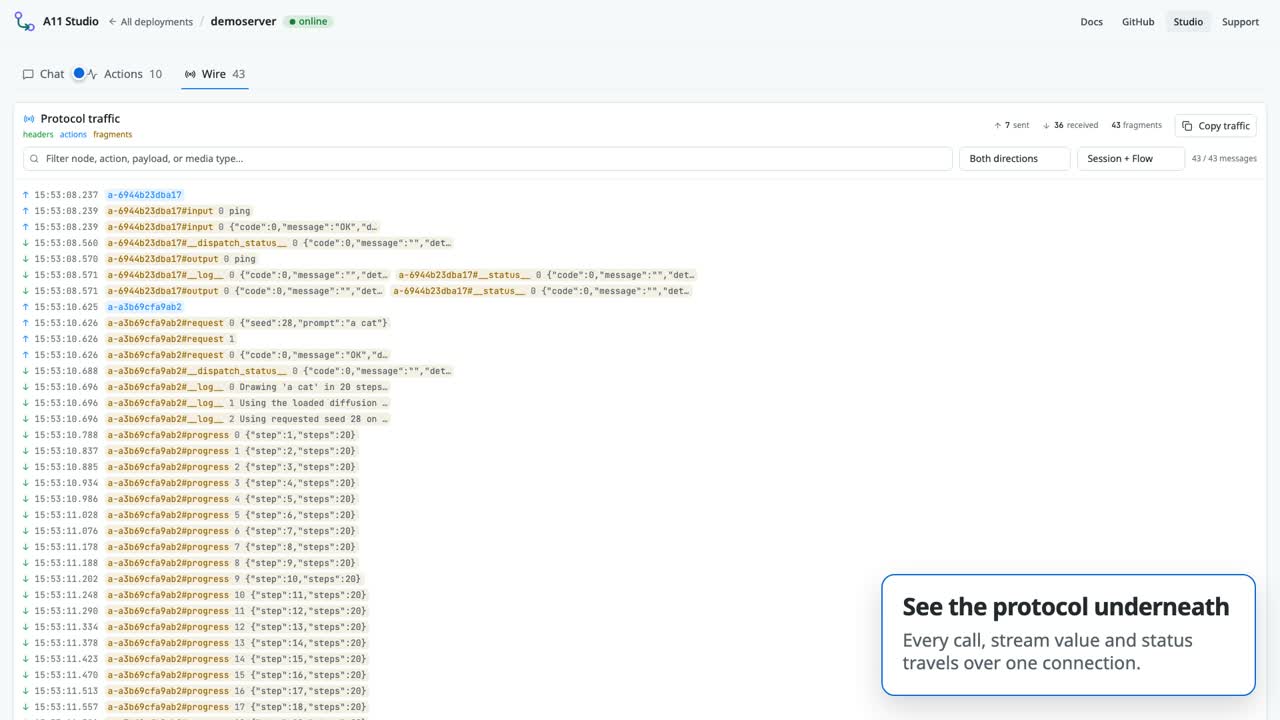
Open Studio to explore an endpoint's action schemas, run calls and inspect streamed outputs, logs, timings, failures and cancellation.
Explore complete applications
- Deep research plans a topic, searches the web in parallel and streams a cited synthesis.
- Model interactions present one streaming interface across Claude, Gemini, Ollama and OpenAI-compatible providers.
- The
a11 chat --voice-model ...path keeps audio capture, transcription and model interaction on separate streams. - Generative media streams progress independently from generated image bytes.
- Browser tools let a model call typed actions implemented inside an existing page.
Each guide names its provider, model and hardware prerequisites. Local actions and remote transports do not require a model.
Install only what the application needs
The Python distribution is a11-kit, imported as a11. Provider integrations
are optional extras such as a11-kit[ollama], a11-kit[claude] and
a11-kit[openai]. Browser and TypeScript applications use:
npm install @curiositystack/a11
The standalone C++20 runtime needs no Python installation. Build and link it through its exported CMake targets using the instructions below.
Go deeper
- Build a parallel research agent in Python.
- Stream one model interface across Claude, Gemini, and Ollama.
- Turn an application action into an LLM tool.
- Move a local action behind a remote service.
- Compose allowed actions safely at runtime.
Questions and rough edges are useful project signals: start a discussion, report friction, or tell us about an integration.
Building the C++ runtime
A11's runtime is a standalone C++20 library you can build and link without Python. The steps below are self-contained; for the editable Python build, wheel matrix, testing workflow, and architecture, see BUILDING.md.
1. Install the tools, then build the C++ libraries. A11 links a pinned set
of statically-built libraries (Boost, OpenSSL, libcurl, nghttp2, hiredis,
nlohmann-json, uvw) rather than system copies; scripts/bootstrap_wheel_deps.sh builds them
into a per-architecture prefix. From Homebrew you install only the tools (a C++20
compiler, CMake ≥ 3.28, Ninja; Linux tool package names vary):
brew install cmake googletest ninja pkg-config

export A11_DEPS_PREFIX="$HOME/.cache/a11-deps/$(uname -m)"
export CMAKE_PREFIX_PATH="$A11_DEPS_PREFIX"
export OPENSSL_ROOT_DIR="$A11_DEPS_PREFIX"
export PKG_CONFIG_PATH="$A11_DEPS_PREFIX/lib/pkgconfig"
export MACOSX_DEPLOYMENT_TARGET=14.4   # macOS only
scripts/bootstrap_wheel_deps.sh
CMake still fetches the pinned Abseil (and libdatachannel, for WebRTC) automatically. See BUILDING.md for the full rundown.
2. Configure, build, and install to a prefix (the exports above point CMake at the dependency prefix):
cmake -S . -B build -G Ninja \
  -DCMAKE_BUILD_TYPE=Release \
  -DA11_BUILD_PYTHON=OFF \
  -DCMAKE_OSX_DEPLOYMENT_TARGET=14.4 \
  -DCMAKE_INSTALL_PREFIX="$PWD/install"

cmake --build build -j
cmake --install build
On macOS, pass -DCMAKE_OSX_DEPLOYMENT_TARGET=14.4 as shown — it must match the
value the prefix was bootstrapped with. Setting it as a cache variable here (not
only via the MACOSX_DEPLOYMENT_TARGET environment export, which CMake may not
pick up) is what enables the Boost.Fiber futex spinlock; a lower target compiles
Boost.Fiber without futex support and fails with
"futex not supported on this platform". The flag is ignored on Linux.
3. Use it from your own CMake project. The install exports a CMake package
named a11 with per-component targets (a11::service links the whole runtime).
Point your consumer's CMAKE_PREFIX_PATH at both the install prefix and the
dependency prefix from step 1, so the transitive static Boost/OpenSSL/... resolve:
find_package(a11 CONFIG REQUIRED)

add_executable(my_agent main.cc)
target_link_libraries(my_agent PRIVATE a11::service)
target_compile_features(my_agent PRIVATE cxx_std_20)
#include <cstddef>
#include <iostream>
#include <memory>
#include <optional>
#include <string>
#include <vector>

#include <absl/log/log.h>
#include <absl/status/status.h>
#include <absl/status/status_macros.h>
#include <absl/strings/str_split.h>

#include "a11/actions/registry.h"
#include "a11/nodes/async_node.h"

namespace {

using a11::actions::Action;
using a11::actions::ActionPortSchema;
using a11::actions::ActionRegistry;
using a11::actions::ActionSchema;
using a11::nodes::AsyncNode;

ActionSchema SplitWordsSchema() {
  return ActionSchema{
      .name = "split-words",
      .inputs = {{"text", ActionPortSchema{
                             .name = "text", .type = "text/plain"}}},
      .outputs = {{"words", ActionPortSchema{
                               .name = "words", .type = "text/plain"}}},
  };
}

absl::Status SplitWords(std::shared_ptr<Action> action) {
  ABSL_ASSIGN_OR_RETURN(std::shared_ptr<AsyncNode> input,
                        action->GetInput("text"));
  ABSL_ASSIGN_OR_RETURN(
      std::optional<std::string> text,
      input->NextObject<std::string>().Await());
  if (!text.has_value()) {
    return absl::FailedPreconditionError("text input ended before a value");
  }

  ABSL_ASSIGN_OR_RETURN(std::shared_ptr<AsyncNode> output,
                        action->GetOutput("words"));
  std::vector<std::string> words =
      absl::StrSplit(*text, absl::ByAnyChar(" \t\n"), absl::SkipWhitespace());
  if (words.empty()) {
    return output->Finalize({.wait = true}).Await().status();
  }
  for (size_t index = 0; index + 1 < words.size(); ++index) {
    ABSL_RETURN_IF_ERROR(output->Put(words[index]).Await().status());
  }
  return output->Finalize(words.back(), {.wait = true}).Await().status();
}

absl::Status RunExample() {
  auto registry = std::make_shared<ActionRegistry>();
  ABSL_RETURN_IF_ERROR(registry->RegisterSync(
      "split-words", SplitWordsSchema(), SplitWords));
  ABSL_ASSIGN_OR_RETURN(std::shared_ptr<Action> action,
                        registry->MakeAction("split-words"));

  ABSL_ASSIGN_OR_RETURN(std::shared_ptr<AsyncNode> input,
                        action->GetInput("text"));
  ABSL_RETURN_IF_ERROR(
      input->Finalize(std::string("named streams arrive early"),
                      {.wait = true})
          .Await()
          .status());
  ABSL_RETURN_IF_ERROR(action->Run().status());

  ABSL_ASSIGN_OR_RETURN(std::shared_ptr<AsyncNode> output,
                        action->GetOutput("words"));
  while (true) {
    ABSL_ASSIGN_OR_RETURN(std::optional<std::string> word,
                          output->NextObject<std::string>().Await());
    if (!word.has_value()) break;
    std::cout << *word << '\n';
  }
  return action->Wait().Await().status();
}

}  // namespace

int main() {
  const absl::Status status = RunExample();
  if (!status.ok()) {
    LOG(ERROR) << status;
    return 1;
  }
  return 0;
}
This is the same split-words action as the Python quickstart: the registry
owns its schema and handler, the input carries one complete value, and the
output emits words as a stream. Reading the output before Wait() drains it
while the handler is running and preserves backpressure.
Configure your project with -DCMAKE_PREFIX_PATH=/path/to/install so
find_package locates it. The generated C++ API reference is published
alongside the docs.
1 maintainer

Metadata
1 maintainer
Release files for a11-kit 0.7.8
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| a11_kit-0.7.8.tar.gz | 2.5 MB | With provenance | Details |
Built distributions (wheels)
Total release size: 142.0 MB
Release files / a11_kit-0.7.8.tar.gz
| Download URL | a11_kit-0.7.8.tar.gz |
|---|---|
| Size | 2.5 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
b74234b187786a3f7d9b443c47cba550cf177de35b8dc1b716d1cc917e770f4b
|
|
BLAKE2b-256 checksum How to use checksums |
1cb04de99c33a30d3cab814174a376afdf7b5e3d19bb7c7fe094068653a88935
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logRelease files / a11_kit-0.7.8-cp314-cp314-manylinux_2_28_x86_64.whl
| Download URL | a11_kit-0.7.8-cp314-cp314-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 12.7 MB |
| Tags | CPython 3.14 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
debd803326f20bdc4148c7af48a2ddb62ec44112d8914156ca1cfd060eb33d04
|
|
BLAKE2b-256 checksum How to use checksums |
768e9a02ca9d9b6a4bef1a58965347c25cf8301ac30f02b2c71e8973d5a97158
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logRelease files / a11_kit-0.7.8-cp314-cp314-manylinux_2_28_aarch64.whl
| Download URL | a11_kit-0.7.8-cp314-cp314-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 12.1 MB |
| Tags | CPython 3.14 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
10d14b1d152f7a2b6bb1c301c9aaa3489f399355ef3b7f2258b9292be9b542b4
|
|
BLAKE2b-256 checksum How to use checksums |
8d93f2222090997c1b3987f74be6373acf29a1dee7fb6e17dfe4a5b926dec13f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logRelease files / a11_kit-0.7.8-cp314-cp314-macosx_14_0_arm64.whl
| Download URL | a11_kit-0.7.8-cp314-cp314-macosx_14_0_arm64.whl |
|---|---|
| Size | 10.1 MB |
| Tags | CPython 3.14 macOS 14.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
6413cc3cb50b699845412ff427c7f1db0ac765c1a40406dd70fcbd9ee2a4f34d
|
|
BLAKE2b-256 checksum How to use checksums |
b917e1639c3083a1358d01c3a46c2d28d1e0b493d0915243ac49601db9c5e06e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logRelease files / a11_kit-0.7.8-cp313-cp313-manylinux_2_28_x86_64.whl
| Download URL | a11_kit-0.7.8-cp313-cp313-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 12.7 MB |
| Tags | CPython 3.13 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
1259c37ad1d5a97218fb613fa2fb615a09f1ecf5c53dd0cb3a8b0fb09da20253
|
|
BLAKE2b-256 checksum How to use checksums |
ce1d107e8190eeb79db657d625346483450a51984f5a2951da8e17cf075bb225
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logRelease files / a11_kit-0.7.8-cp313-cp313-manylinux_2_28_aarch64.whl
| Download URL | a11_kit-0.7.8-cp313-cp313-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 12.1 MB |
| Tags | CPython 3.13 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
5893d17cf2a12aaf92c185746f8bd208eb56336c12b1bb112e9e8150e846aeb2
|
|
BLAKE2b-256 checksum How to use checksums |
2f07581c05663cce02b418a35e713ca1143cb5166e25629b5217718881b83f5c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logRelease files / a11_kit-0.7.8-cp313-cp313-macosx_14_0_arm64.whl
| Download URL | a11_kit-0.7.8-cp313-cp313-macosx_14_0_arm64.whl |
|---|---|
| Size | 10.1 MB |
| Tags | CPython 3.13 macOS 14.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
007f4af375d12cd439d21c9b899ff196ea1fff3ce7e9405bc4f9cccbe78c1b58
|
|
BLAKE2b-256 checksum How to use checksums |
18243d1daf48a6840975870a34899500d77b1af3ebab30b46692a8dbebf50bb6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logRelease files / a11_kit-0.7.8-cp312-cp312-manylinux_2_28_x86_64.whl
| Download URL | a11_kit-0.7.8-cp312-cp312-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 12.7 MB |
| Tags | CPython 3.12 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
56124a7fe5eca71251d3ae35261d2b0a388802bde9be6f0e5d26fb366db9c392
|
|
BLAKE2b-256 checksum How to use checksums |
7f41c2e7d47fd64fa5b973c5ba0649ed9d08724899bd794968d4e9decc665702
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logRelease files / a11_kit-0.7.8-cp312-cp312-manylinux_2_28_aarch64.whl
| Download URL | a11_kit-0.7.8-cp312-cp312-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 12.1 MB |
| Tags | CPython 3.12 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
49b11512d709f93905dbc98f8f7f0750056e346c400552f989e42f1956a56125
|
|
BLAKE2b-256 checksum How to use checksums |
9222a475851f30651dfe06d83d970db27f325879550b7271181d8e9e964c6cab
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logRelease files / a11_kit-0.7.8-cp312-cp312-macosx_14_0_arm64.whl
| Download URL | a11_kit-0.7.8-cp312-cp312-macosx_14_0_arm64.whl |
|---|---|
| Size | 10.1 MB |
| Tags | CPython 3.12 macOS 14.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
3f1dde13f6fcc545dc3c022afbb329e2fbb3111a79db85895c9ad71ab0c2642a
|
|
BLAKE2b-256 checksum How to use checksums |
2231dadfe9ae5f3ab837772588aad814514988a556d394e456b1c2763371a4c9
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logRelease files / a11_kit-0.7.8-cp311-cp311-manylinux_2_28_x86_64.whl
| Download URL | a11_kit-0.7.8-cp311-cp311-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 12.7 MB |
| Tags | CPython 3.11 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
762d96e4e6d0fd512d3213e14cc47949ea59ccda9cd7bf5a59df16ed20692c95
|
|
BLAKE2b-256 checksum How to use checksums |
b18c2c7e656542dd80e8dd8ccc54e6b530b0ca54717ffe32912974577737b5c9
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logRelease files / a11_kit-0.7.8-cp311-cp311-manylinux_2_28_aarch64.whl
| Download URL | a11_kit-0.7.8-cp311-cp311-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 12.1 MB |
| Tags | CPython 3.11 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
d187ff43eeafbb01d52a27e76c5130e5ebb36ccd2cc05cd19d5bd71831d5195c
|
|
BLAKE2b-256 checksum How to use checksums |
da9d3ce8eb2f5079b48e2d1d5a3069e9bf8e817dc2fd0ec14ba2a4b9715f5c3c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logRelease files / a11_kit-0.7.8-cp311-cp311-macosx_14_0_arm64.whl
| Download URL | a11_kit-0.7.8-cp311-cp311-macosx_14_0_arm64.whl |
|---|---|
| Size | 10.1 MB |
| Tags | CPython 3.11 macOS 14.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
2fe15fc6cc05473241643059a647014498d245a2cdce1948996115144c2530af
|
|
BLAKE2b-256 checksum How to use checksums |
675655d65b34ed06c06b56bfdf354bd3a9efb648ea56106f9c0c5e43f1a630cd
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logSecurity for a11-kit 0.7.8
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 13 files in this release have been uploaded with provenance metadata.
Attestation for a11_kit-0.7.8.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














