
agent-bom
Open security scanner and self-hosted control plane for AI, MCP, and cloud infrastructure.
Start with the repository in front of you, then choose the entrypoint that matches your next job: image scan, cloud posture, fix plan, dashboard, MCP tools, or runtime review.
better-sqlite3@9.0.0  (npm package)
  |── OSV/GHSA finding  (critical · advisory-backed)
  |── sqlite-mcp  (MCP Server · unverified · root)
       |── Cursor IDE  (Agent · 4 servers · 12 tools)
       |── ANTHROPIC_KEY, DB_URL, AWS_SECRET  (Credential env names visible)
       |── query_db, read_file, write_file, run_shell  (Reachable tools)

 Fix: upgrade better-sqlite3 → 11.7.0
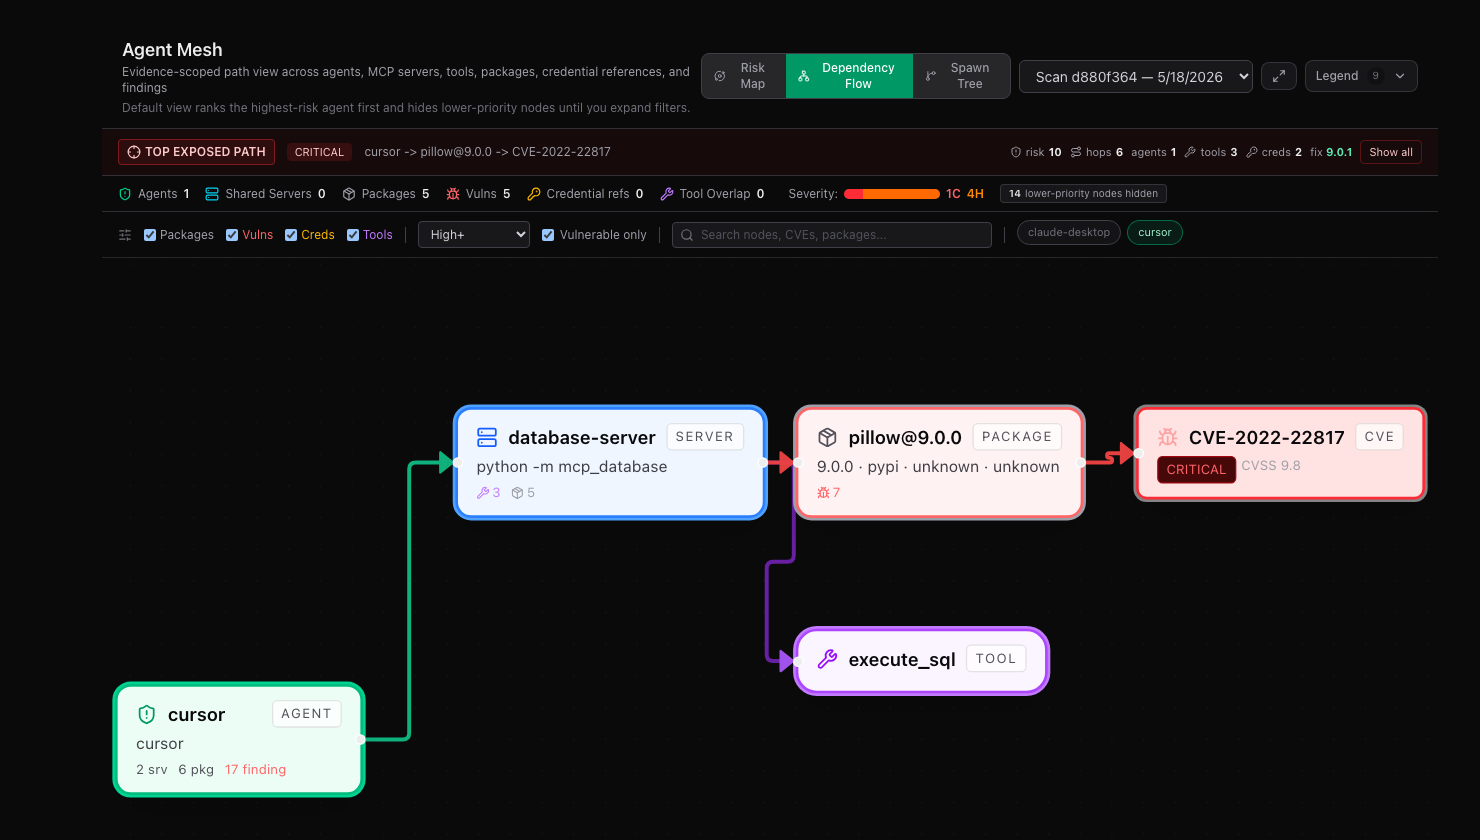
Blast radius is the core idea: package -> vulnerability finding -> MCP server (tools + credential env names) -> connected agents. This schematic explains the model; emitted findings are backed by the configured advisory sources.
Scan local agent configs, MCP servers, instruction files, lockfiles, containers, cloud estate, AI models/datasets, non-human identities, LLM cost, GPU surfaces, and runtime evidence.
pip install agent-bom
agent-bom scan .
The scan prints inventory, findings, reachable impact, evidence coverage, and
the next remediation step. Run agent-bom doctor if the first scan cannot
start.
For a deterministic sample, use the built-in offline demo. It deliberately
contains blocking findings, so status 1 is the expected security verdict;
the printed report is complete.
agent-bom scan --demo --offline
The demo uses a curated sample for reproducible output within a release; advisory and severity updates can change later releases.
If you want an inspectable sample before scanning your own repo:
agent-bom samples first-run
agent-bom scan --inventory agent-bom-first-run/inventory.json -p agent-bom-first-run --enrich
The bundled first-run stack includes agent inventory, MCP server definitions,
placeholder credential environment variable names, Python/npm manifests, and a
prompt file. See docs/FIRST_RUN.md in the repository for the guided flow.
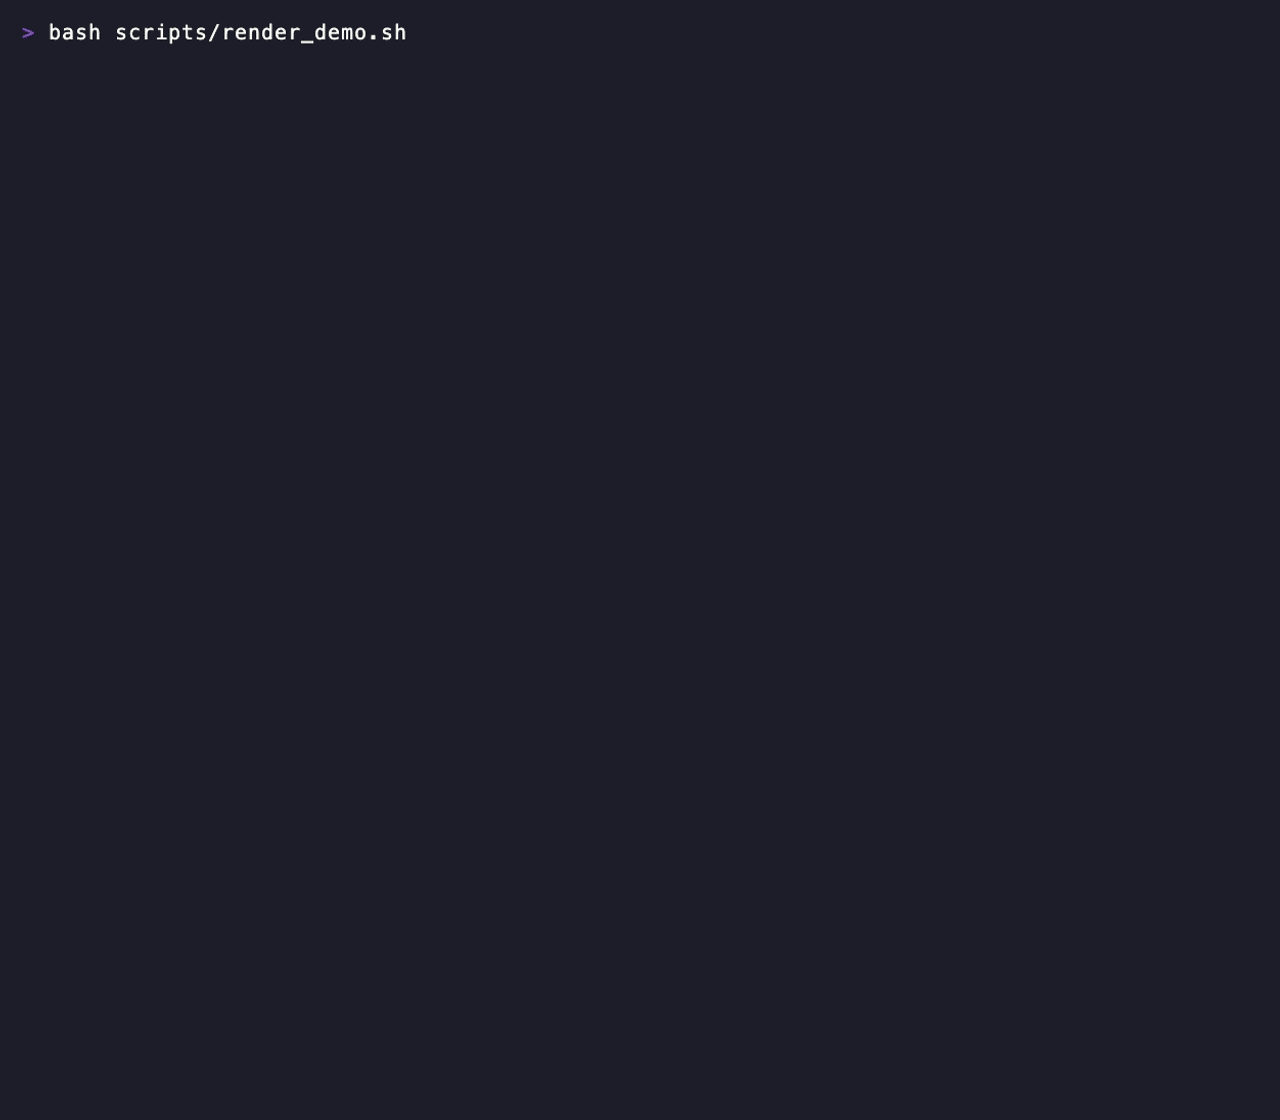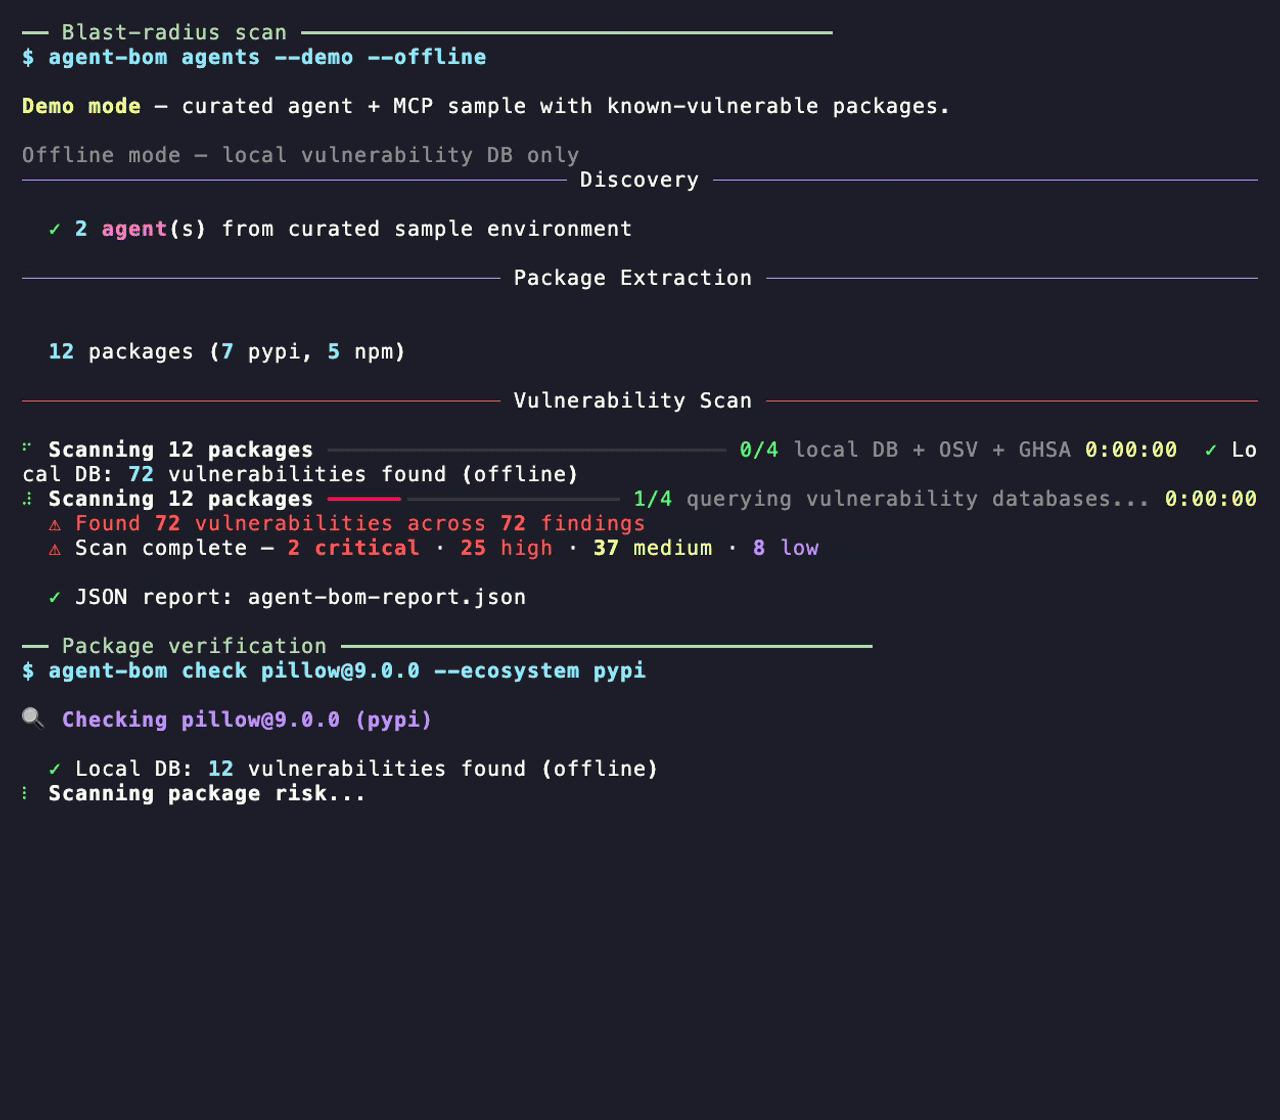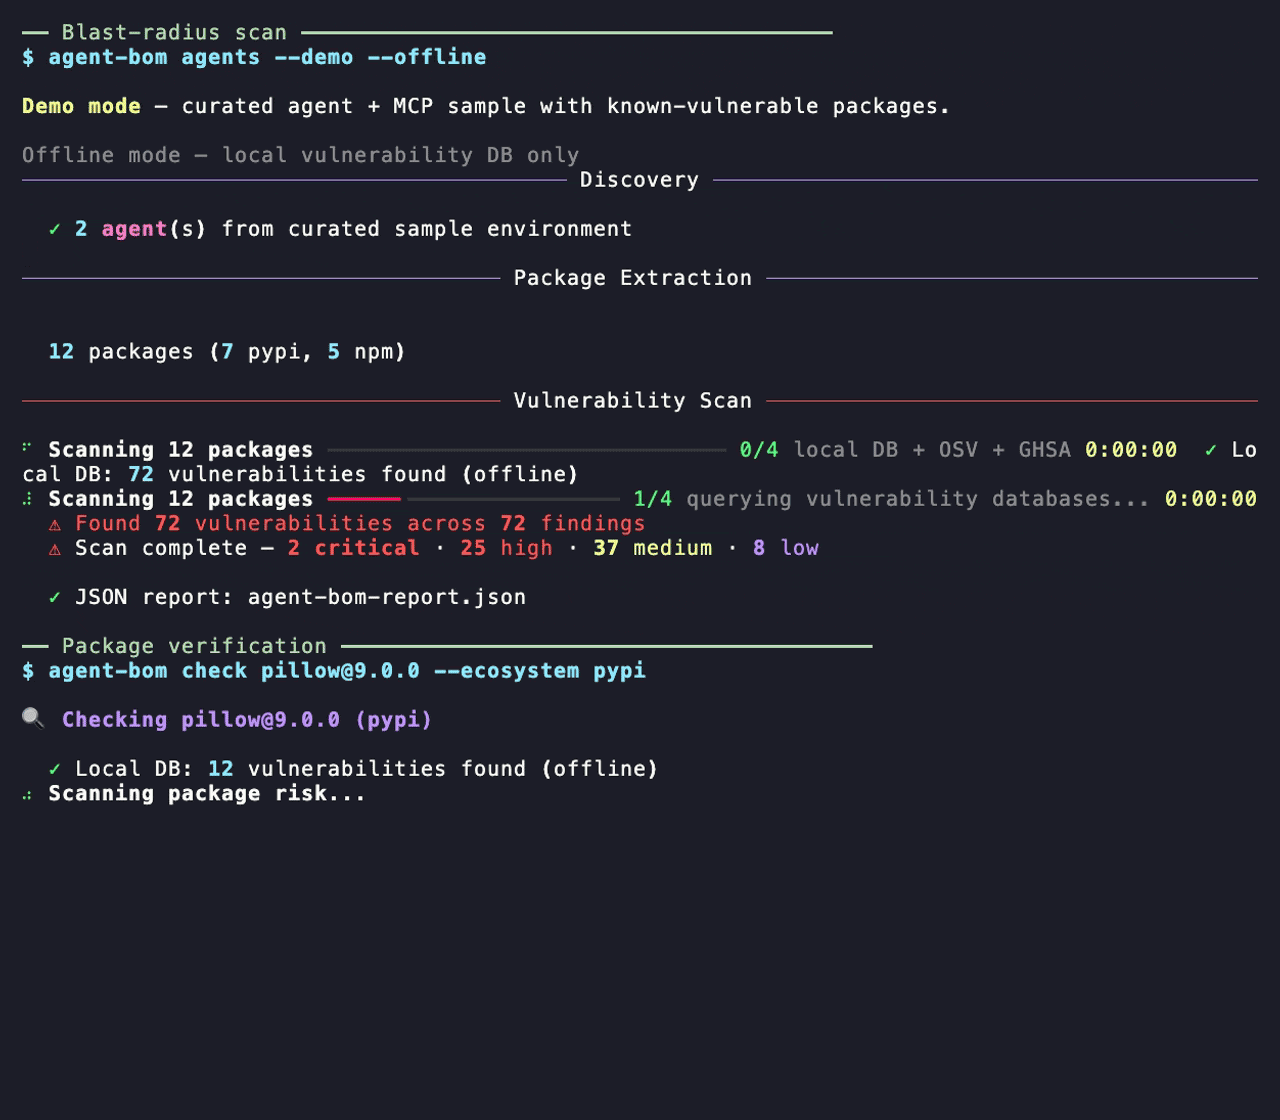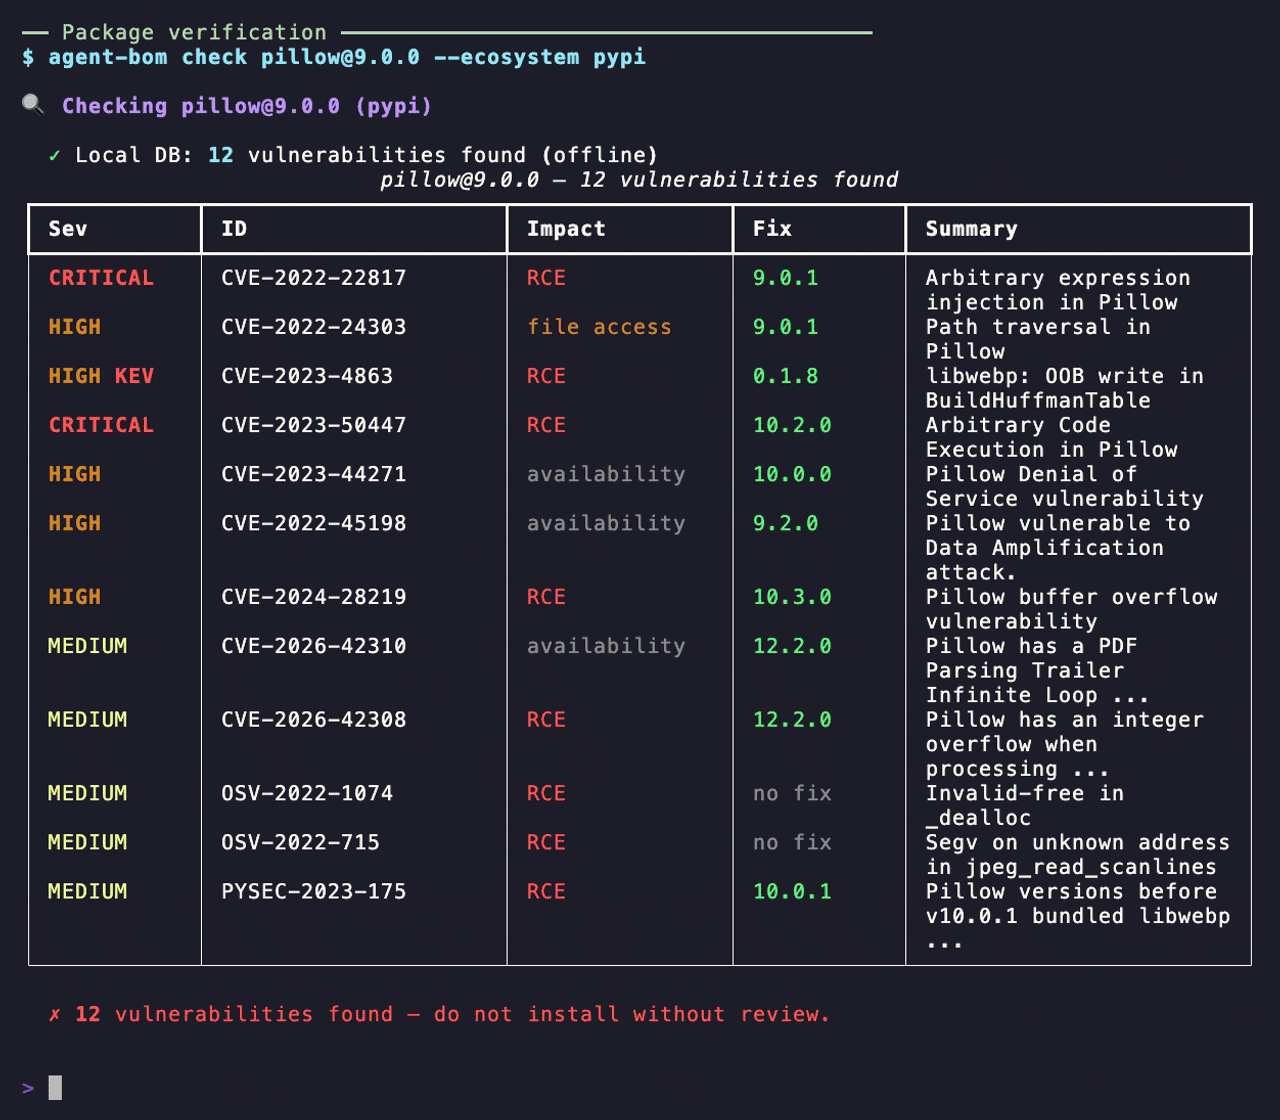
See the terminal demo
Follow one component
In the self-hosted dashboard, open Inventory → component → Findings → Compliance. The views retain the exact component and scan snapshot, expose recorded relationships and source evidence, and export loaded evidence with completeness receipts. Control mappings do not establish evaluated passes or certification.
From a source checkout, run the connected-BOM example. It retains before/after SQLite snapshots: a changed dependency input removes one pinned advisory finding while an unrelated synthetic cloud check remains failed. This bounded example does not change a deployment or qualify a cloud account.
Recommended starting points
pip install agent-bom

agent-bom scan .                                 # Repo + MCP + package blast radius
agent-bom quickstart --dry-run --offline          # Sample-data and API/UI next steps
agent-bom samples first-run                      # Inspectable sample AI stack
agent-bom check flask@2.2.0 --ecosystem pypi     # Pre-install package verdict
agent-bom image nginx:latest                     # Container image scan
agent-bom scan . --remediate remediation.md       # Fix-first remediation plan
pip install 'agent-bom[ui]'                      # once, if you want the dashboard
agent-bom serve --persist ~/.agent-bom/control-plane.db  # restart-safe local control plane
The base wheel is the scanner/CLI path and includes MCP server mode
(agent-bom mcp server). Install optional surfaces explicitly:
pip install 'agent-bom[ui]' for the local API/dashboard process. Use
pip install 'agent-bom[all]' for supported first-run extras; MLflow remains
separate until its upstream CVE backlog is fixed. If an extra is missing, the
command exits with the matching install hint.
Self-hosted pilot:
curl -fsSL https://raw.githubusercontent.com/msaad00/agent-bom/main/deploy/docker-compose.pilot.yml -o docker-compose.pilot.yml
docker compose -f docker-compose.pilot.yml up -d
# Dashboard -> http://localhost:3000
Production chart from a checked-out repo:
helm upgrade --install agent-bom deploy/helm/agent-bom \
  --namespace agent-bom --create-namespace \
  -f deploy/helm/agent-bom/examples/eks-production-values.yaml
Product views
Dashboard
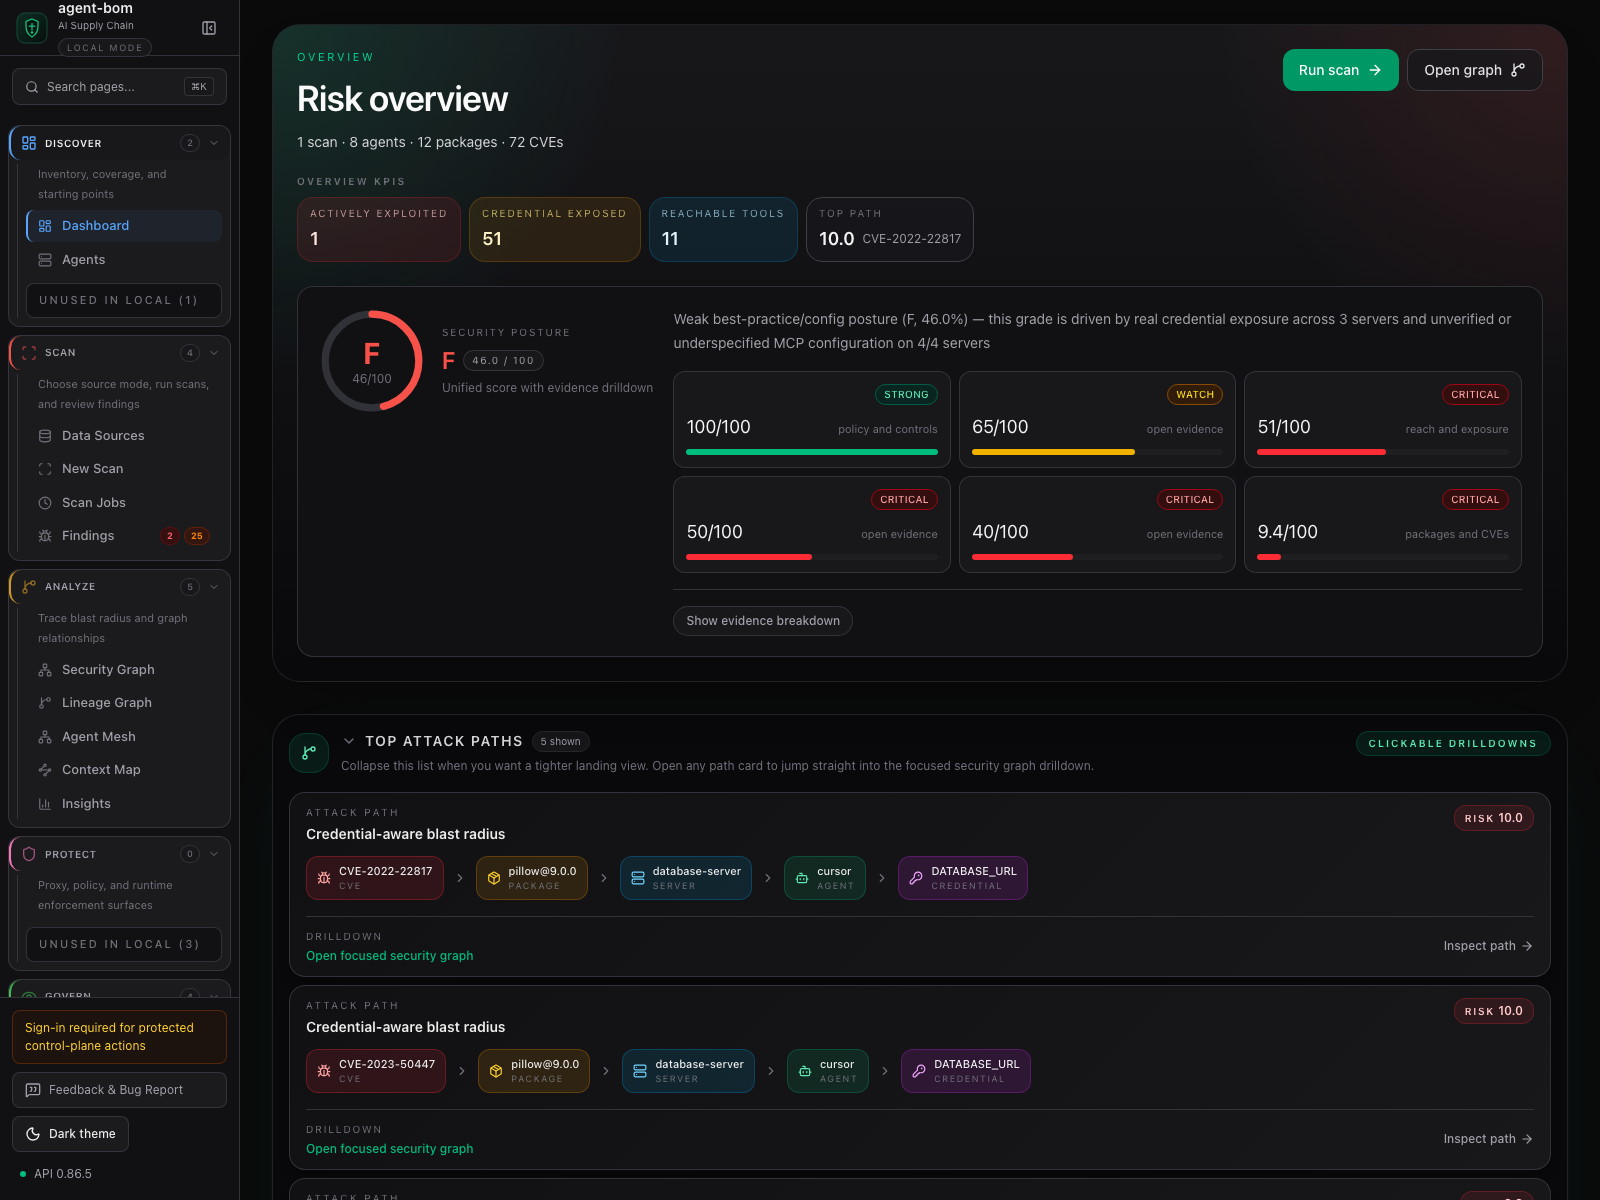
Agent mesh graph
What it scans
- Agents + MCP — MCP clients, servers, tools, transports, trust posture
- Skills + instructions —
CLAUDE.md,AGENTS.md,.cursorrules,.windsurfrules,skills/* - Package risk — supply-chain scanning across 15 package ecosystems (including
mix.lock/pubspec.lockfor Hex and Pub) with OSV/GHSA enrichment and blast radius - AI models + datasets — malicious-model detection via safe pickle-opcode disassembly (no execution), model/dataset cards, and target-scoped PII/PHI dataset-file scanning
- Container images + IaC — native OCI parsing plus Dockerfile, Terraform, CloudFormation, Helm, and Kubernetes coverage
- Cloud estate — read-only, gated asset inventory across AWS/Azure/GCP plus AI/GPU posture and CIS benchmarks
- Identity (NHI) — non-human identity discovery (Okta/Entra), credential-expiry posture, and access-review campaigns
- LLM cost — spend forecasting, budget runway, chargeback/allocation, and seasonal-aware spend-anomaly detection
- Secrets + runtime — MCP proxy/gateway, inline firewall enforcement, A2A/MCP auth posture, Shield SDK, secrets, and redaction surfaces
- Compliance + evidence — mapped governance plus ZIP evidence bundles for auditors
Key features
- Blast radius + attack-path fusion — multi-hop exposure paths over one
UnifiedGraph, from package → finding → MCP server → credentials → connected agents - CWE-aware impact — RCE shows credential exposure, DoS does not; symbol-level CVE reachability joins CWE/CVE/CPE advisory context when OSV/GHSA carry affected symbols (Python, npm, Go)
- Portable outputs — SARIF, CycloneDX, SPDX, OCSF, HTML, graph, JSON, ZIP evidence bundles, and more
- MCP server mode — start with 8 scan-profile tools; use
agent-bom mcp server --profile fullfor the complete catalog of 88 MCP tools, 7 resources, and 8 workflow prompts in Claude, Cursor, Windsurf, and Cortex CoCo / Cortex Code - Skill bundle identity — stable bundle hashes for skill and instruction file review
- Dependency confusion detection — flags internal naming patterns
- VEX generation — auto-triage with CWE/CVE/CPE-aware reachability (package + function-level when advisory symbols exist)
Discovery and static/cloud scanning are read-only and agentless. Proxy, gateway, Shield, and control-plane write tools are separate, explicit runtime or authenticated operations. No secrets leave your machine unless you explicitly enable an outbound integration.
How the data moves

Blast radius

Links
1 maintainer

Metadata
1 maintainer
Release files for agent-bom 0.108.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| agent_bom-0.108.2.tar.gz | 10.5 MB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| agent_bom-0.108.2-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 18.9 MB
Release files / agent_bom-0.108.2.tar.gz
| Download URL | agent_bom-0.108.2.tar.gz |
|---|---|
| Size | 10.5 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
af5ed006fe9447b316d2768f392f6ff689e9fa3ca5bdfa150ea8a6cede34277d
|
|
BLAKE2b-256 checksum How to use checksums |
9a90327ca6ffd053834d79b141cedd737fdd402d69715af58add18532c4f335d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 8, 2026.
Transparency logRelease files / agent_bom-0.108.2-py3-none-any.whl
| Download URL | agent_bom-0.108.2-py3-none-any.whl |
|---|---|
| Size | 8.4 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
6b2338a93907c6e37e5f71bfb9dc38fdab95b7ccfa49fa522b1ef84ab57cb78e
|
|
BLAKE2b-256 checksum How to use checksums |
536eff06dd6be288b84481630998baaf3e87edf53f65664bdc3ad363bf6ab30b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 8, 2026.
Transparency log













