



agentsec
Static configuration scanner and hardener for AI agent installations. Detects misconfigurations, credential leaks, supply-chain risks, and MCP tool poisoning — then maps every finding to the OWASP Top 10 for Agentic Applications (2026).
Supports OpenClaw, Claude Code, Cursor, Windsurf, Gemini CLI, and MCP server ecosystems.
Scope: agentsec performs static configuration and file analysis. It does not provide runtime protection, behavioral monitoring, or real-time threat detection. Use as one layer in a defense-in-depth strategy.
Quick Start
pip install agentsec-ai
agentsec scan
Scan a specific installation:
agentsec scan ~/.openclaw
What agentsec checks
| Module | Scope |
|---|---|
installation |
Gateway exposure, auth posture, DM/group policy, tool/sandbox settings, SSRF and safety checks, known CVE version checks, sensitive file/dir permissions |
skill |
Instruction malware, risky code patterns (eval/exec/subprocess) for Python and JS/TS, identity-file (MEMORY.md/AGENTS.md/SOUL.md) write detection, prompt-injection patterns, frontmatter capability risk, dependency/install-hook risk |
mcp |
Tool poisoning patterns, launch-command injection, known-CVE package detection, auth gaps and non-TLS transport on remote endpoints, dangerous schema/permissions, unverified npx usage |
credential |
detect-secrets engine (23 plugins) + 16 custom patterns (OpenAI, Anthropic, AWS, Databricks, HuggingFace, Groq, Mistral, etc.), base64/hex encoded-secret decoding, high-entropy detection, git credential leakage |
Reference catalog:
- Checks Catalog (36 named checks + dynamic credential findings)
- CLI Reference (full command/options guide)
Core Commands
# Full installation scan (all scanners, default target=. )
agentsec scan

# JSON report for CI parsing and pipelines
agentsec scan -o json -f report.json

# SARIF output for GitHub code scanning upload
agentsec scan -o sarif -f results.sarif

# Run only selected scanners for focused checks
agentsec scan -s installation,mcp

# Fail build only at/above selected severity
agentsec scan --fail-on critical
# Preview profile changes without writing config
agentsec harden -p workstation

# Apply profile and write hardened config values
agentsec harden -p workstation --apply

# Watch files and auto re-scan on security-relevant changes
agentsec watch ~/.openclaw -i 2

# Pre-install package gate (scan before install)
agentsec gate npm install express

# Pin MCP tool descriptions for rug-pull detection
agentsec pin-tools

# Generate shell hook wrappers for npm/pip install flows
agentsec hook --shell zsh
List available scanners (names + descriptions):
agentsec list-scanners
Hardening Profiles
| Profile | Intended use |
|---|---|
workstation |
Single-owner local usage |
vps |
Remote/self-hosted deployment |
public-bot |
Highest restriction for untrusted public input |
Use agentsec show-profile <name> to inspect exact changes before applying.
Output and Exit Codes
Output formats:
terminal(default)jsonsarif
Exit codes:
0: no findings at/above threshold1: findings found at/above threshold2: usage error (e.g., unknown scanner name)3: runtime error (e.g., file access failure)
GitHub Actions
Use the bundled composite action:
name: Agent Security
on: [push, pull_request]

jobs:
  agentsec:
    runs-on: ubuntu-latest
    permissions:
      contents: read
      security-events: write
    steps:
      - uses: actions/checkout@v4
      - uses: debu-sinha/agentsec@v0.5.0
        with:
          fail-on: high
          output: sarif
          upload-sarif: 'true'
Action definition:
Screenshots
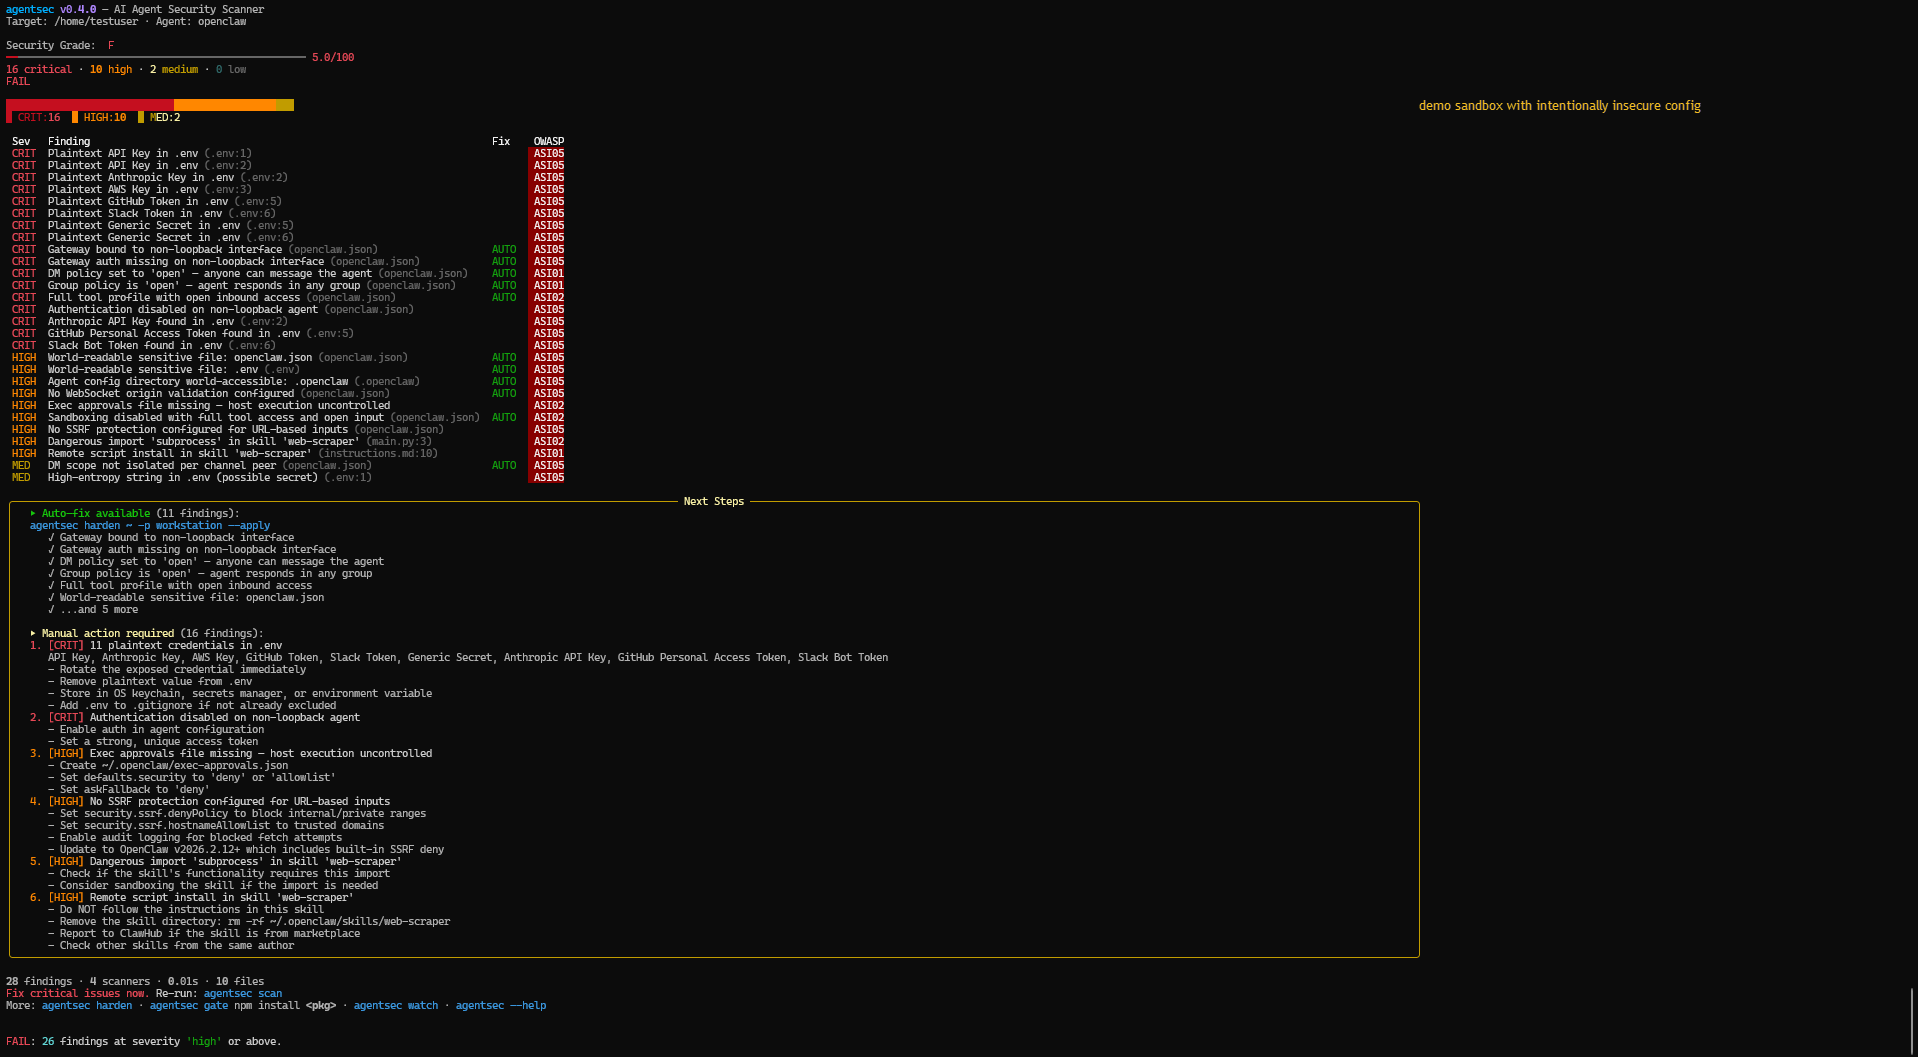
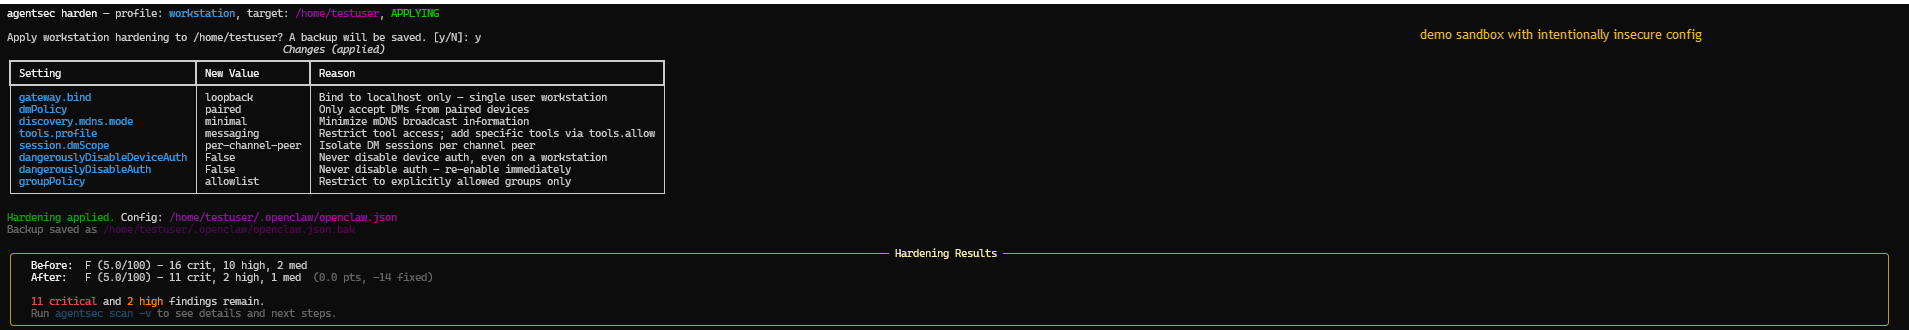
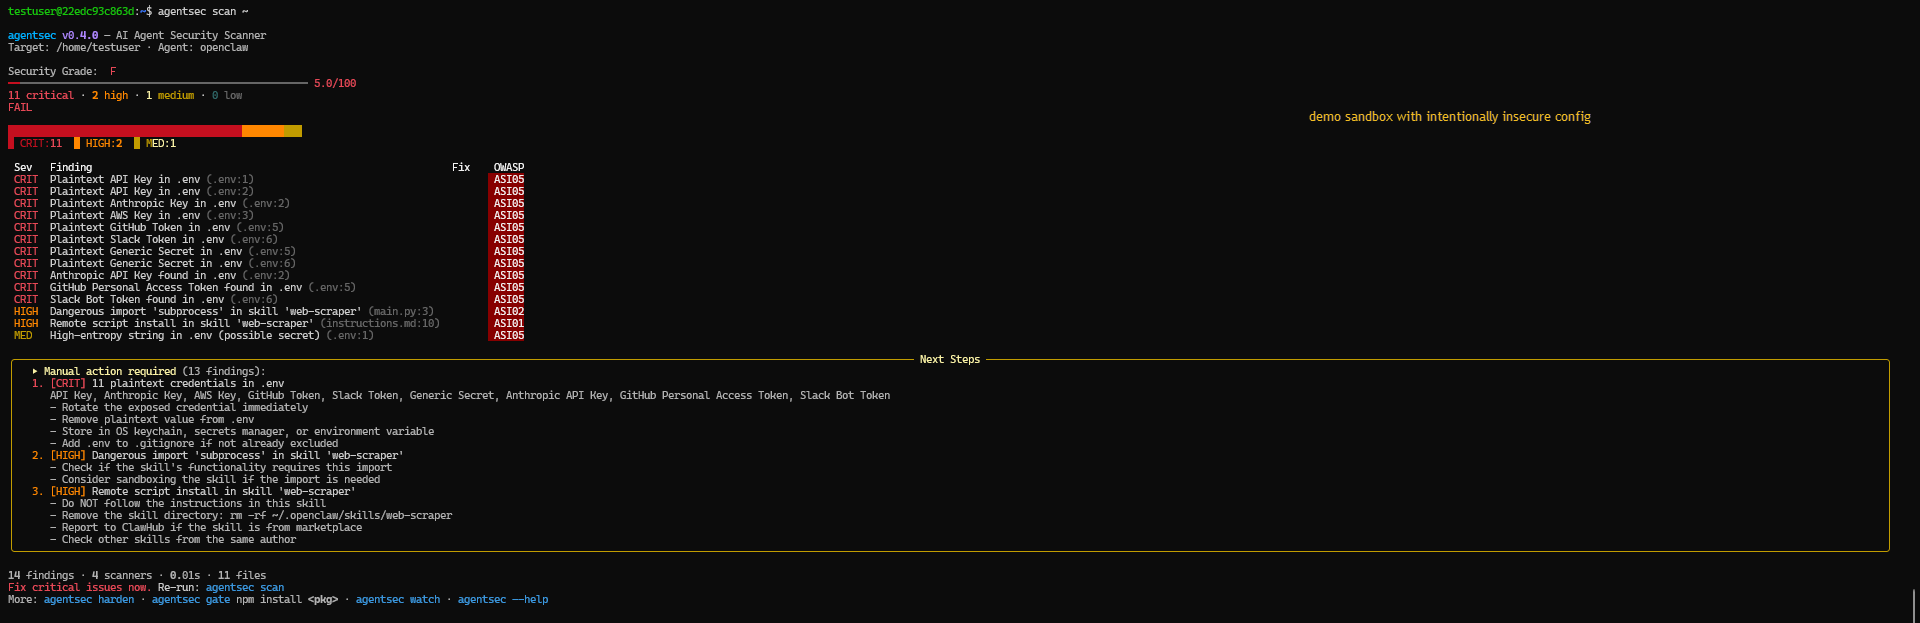
Screenshots below show the experimental demo sandbox flow (intentionally insecure configuration for detection and hardening demonstration). Gate and hook behavior are documented in docs/case-studies/003-preinstall-gate-blocked-malicious-package.md and docs/adr/ADR-0004-pre-install-gate.md.
Step 1: Initial scan on intentionally insecure demo config
Step 2: Apply workstation hardening profile
Step 3: Re-scan findings after hardening
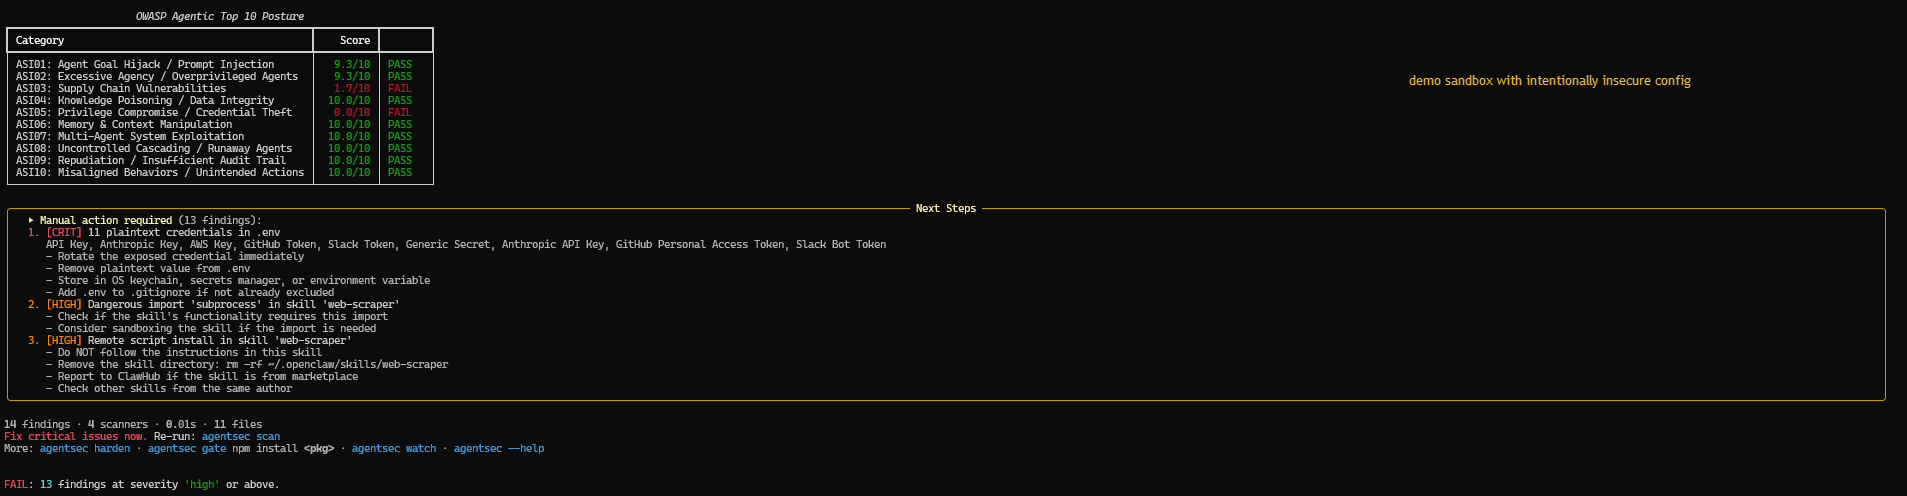
Step 4: OWASP posture view after hardening
MCP Ecosystem Security Dashboard
Weekly automated security scan of the top 50 MCP server repositories, graded A through F.
View the full dashboard - updated every Monday via GitHub Actions.
Benchmarks and Studies
- Fixture benchmark — precision/recall/F1 over a 20-fixture suite (self-authored fixtures, not independently validated).
- Top-50 MCP study — agentsec-only repro run with normalized findings output.
- Top-50 study kit — schema, selection CSV, JSONL findings, and summary JSON.
Current checked-in Top-50 summary data:
docs/benchmarks/top50/reports/top50_summary_20260215.jsondocs/benchmarks/top50/reports/top50_findings_20260215.jsonl
Reproducibility
Fixture benchmark:
python docs/benchmarks/run_benchmark.py
Top-50 study repro:
powershell -ExecutionPolicy Bypass -File scripts\reproduce_top50_study.ps1 -DateStamp 20260215
Note: semgrep and gitleaks baseline runs are optional in the PowerShell repro script and require those tools on PATH.
Adversarial consistency audit (docs vs artifacts):
python scripts/repo_consistency_audit.py
Case Studies
- 001: Insecure workstation remediation
- 002: Public bot hardening on VPS
- 003: Pre-install gate blocked malicious package
- 004: Malicious skill detection and block
Launch Evidence
Development
git clone https://github.com/debu-sinha/agentsec.git
cd agentsec
pip install -c requirements/constraints-dev.txt -e ".[dev]"
ruff check src tests
pytest
Contribution guide:
Security policy:
Governance
Issue intake is template-driven under .github/ISSUE_TEMPLATE/ to keep triage and reproduction quality high.
License
Apache-2.0
1 maintainer

Metadata
1 maintainer
Release files for agentsec-ai 0.5.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| agentsec_ai-0.5.1.tar.gz | 3.1 MB | With provenance | Details for agentsec_ai-0.5.1.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| agentsec_ai-0.5.1-py3-none-any.whl | Python 3 | none | any | Details for agentsec_ai-0.5.1-py3-none-any.whl |
Total release size: 3.3 MB
Release files / agentsec_ai-0.5.1.tar.gz
| Download URL | agentsec_ai-0.5.1.tar.gz |
|---|---|
| Size | 3.1 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
97a09faf3e063b44c72e1a8ca264041646b1d0f1738e02ff3a0f57fab5286a30
|
|
BLAKE2b-256 checksum How to use checksums |
76e4b1665e8f5a2c259da51ef0e18d21ac07f5b23539e953a458444fb445e749
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / agentsec_ai-0.5.1-py3-none-any.whl
| Download URL | agentsec_ai-0.5.1-py3-none-any.whl |
|---|---|
| Size | 144.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
2a2199e685f3278941399484852399c0c3945fde95a4f28031ad75ffd41f0e08
|
|
BLAKE2b-256 checksum How to use checksums |
787906e1a6d8072282162bc4670aea1f07cab1a8a7524a4ad1cde3378f598f37
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logSecurity for agentsec-ai 0.5.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for agentsec_ai-0.5.1.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














