
Appwrite Python SDK

This SDK targets Appwrite server version 2.6.x as shipped on Appwrite Cloud. Self-hosted releases can lag behind Cloud — if you run an older self-hosted build, use a matching older SDK from previous releases when APIs differ.
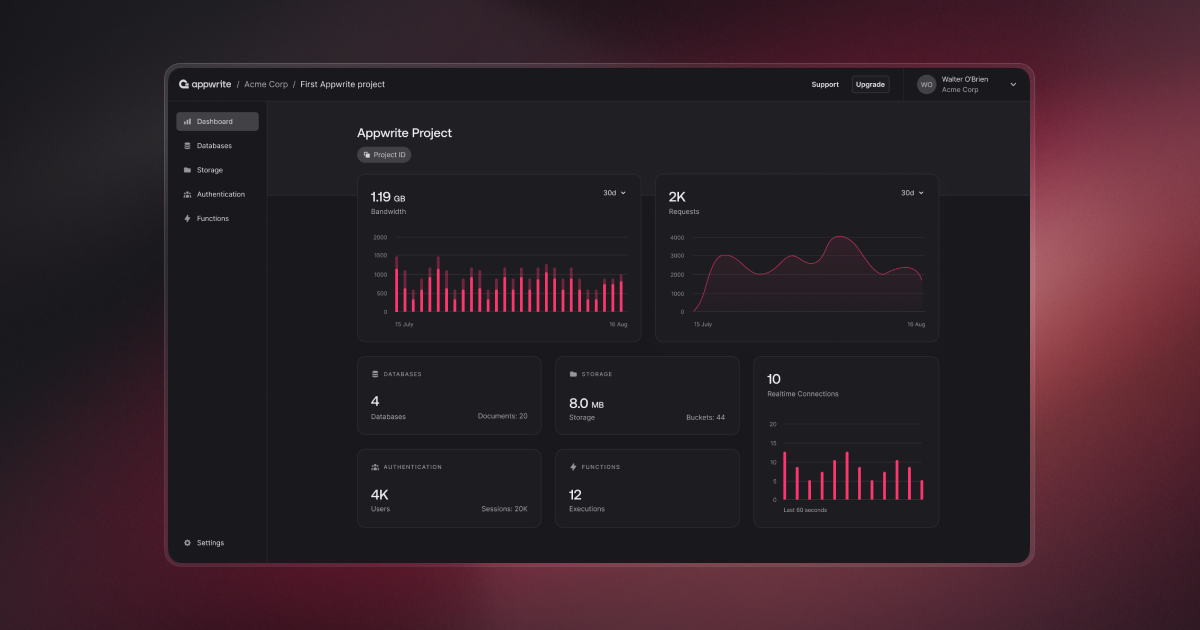
Appwrite is an open-source backend as a service server that abstracts and simplifies complex and repetitive development tasks behind a very simple to use REST API. Appwrite aims to help you develop your apps faster and in a more secure way. Use the Python SDK to integrate your app with the Appwrite server to easily start interacting with all of Appwrite backend APIs and tools. For full API documentation and tutorials go to https://appwrite.io/docs
Installation
Requires Python 3.10 or later. Install the appwrite package from PyPI:
pip install appwrite
Or with uv:
uv add appwrite
Getting started
Requirements and installation
Use Python 3.10 or later. Create and activate a virtual environment with that interpreter, then install the SDK:
python -m pip install --upgrade appwrite
The SDK requires requests>=2.34.2,<3 and urllib3>=2.8.0,<3. Update application pins or constraints that exclude these versions.
Initialize the client
Create a client with your Appwrite endpoint, project ID and an API key. Find the endpoint and project ID in your project's Settings page, and create an API key with only the scopes you need under API keys in the project sidebar.
from appwrite.client import Client

client = Client()
client.set_endpoint('https://<REGION>.cloud.appwrite.io/v1')
client.set_project('<PROJECT_ID>')
client.set_key('<API_KEY>')
API keys grant server-level access to your project. Keep them out of client-side code and version control.
Make a request
Create a service object with the client and call any of its methods. Every method returns a typed Pydantic model, so response fields are available as attributes.
from appwrite.id import ID
from appwrite.services.users import Users

users = Users(client)

user = users.create(
    user_id=ID.unique(),
    email='email@example.com',
    password='password',
    name="Walter O'Brien",
)

print(user.id)
print(user.name)
print(user.to_dict())
See the API reference for every service and method.
Work with rows
Use TablesDB to read and write rows. Pass a Pydantic model as model_type to get typed row data back; without it, row.data is a dict.
from typing import Optional

from pydantic import BaseModel

from appwrite.id import ID
from appwrite.query import Query
from appwrite.services.tables_db import TablesDB


class Post(BaseModel):
    title: str
    published: bool
    excerpt: Optional[str] = None


tables_db = TablesDB(client)

row = tables_db.create_row(
    database_id='<DATABASE_ID>',
    table_id='<TABLE_ID>',
    row_id=ID.unique(),
    data={'title': 'Hello, world', 'published': True},
    model_type=Post,
)

print(row.id)
print(row.data.title)

result = tables_db.list_rows(
    database_id='<DATABASE_ID>',
    table_id='<TABLE_ID>',
    queries=[Query.equal('published', True), Query.limit(25)],
    model_type=Post,
)

for row in result.rows:
    print(row.data.title)
Handle errors
Failed requests raise AppwriteException, which carries message, code, type and response.
from appwrite.exception import AppwriteException

try:
    user = users.get(user_id='<USER_ID>')
except AppwriteException as error:
    print(error.code, error.type, error.message)
Self-hosted Appwrite
Point the client at your own instance instead of Appwrite Cloud. Call set_self_signed() only in development, when the server uses a self-signed TLS certificate.
client.set_endpoint('https://appwrite.example.com/v1')
client.set_self_signed()
Learn more
Contribution
This library is auto-generated by Appwrite custom SDK Generator. To learn more about how you can help us improve this SDK, please check the contribution guide before sending a pull-request.
License
Please see the BSD-3-Clause license file for more information.
3 maintainers


Metadata
3 maintainers
Release files for appwrite 27.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| appwrite-27.1.0.tar.gz | 302.3 kB | With provenance | Details for appwrite-27.1.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| appwrite-27.1.0-py3-none-any.whl | Python 3 | none | any | Details for appwrite-27.1.0-py3-none-any.whl |
Total release size: 831.2 kB
Release files / appwrite-27.1.0.tar.gz
| Download URL | appwrite-27.1.0.tar.gz |
|---|---|
| Size | 302.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
46ef224de50138342cc27398e81e4beb9168c7121b6978c698b7bf8d2a1204f2
|
|
BLAKE2b-256 checksum How to use checksums |
4b1dedb160ef10d30f0f243c6a2d2dc105ea072f1764bd124b02812b7f782143
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 28, 2026.
Transparency logRelease files / appwrite-27.1.0-py3-none-any.whl
| Download URL | appwrite-27.1.0-py3-none-any.whl |
|---|---|
| Size | 528.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
00d60f403f15756a74c916609242522d6fa58aa4bc6a75bf73cca86bfe95bbb8
|
|
BLAKE2b-256 checksum How to use checksums |
b6f2fe8c522eaef7da2c05c137e7d79fcf2f0abd08160f126182175abfe63720
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 28, 2026.
Transparency logSecurity for appwrite 27.1.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for appwrite-27.1.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 28, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














