





atomview
A lightweight, standalone molecular structure viewer for Jupyter notebooks. Visualize biotite AtomArray structures interactively using py3Dmol (3Dmol.js) — with chain-coloured cartoons, ligand sticks, ion spheres, surfaces, and hover labels out of the box.
atomview extracts and refactors the excellent view() function from atomworks (atomworks.io.utils.visualize) into a focused, minimal package. If all you need is a quick way to render structures in a notebook, you no longer have to pull in atomworks and its full dependency tree (RDKit, ML tooling, dataset infrastructure, etc.).
Installation
pip install atomview
Or with uv:
uv add atomview
Quickstart
# from urllib.request import urlretrieve
# urlretrieve("https://files.rcsb.org/download/4HHB.cif", "4hhb.cif")

from atomview import load_structure, view

structure = load_structure("4hhb.cif")

view(structure)
Gallery
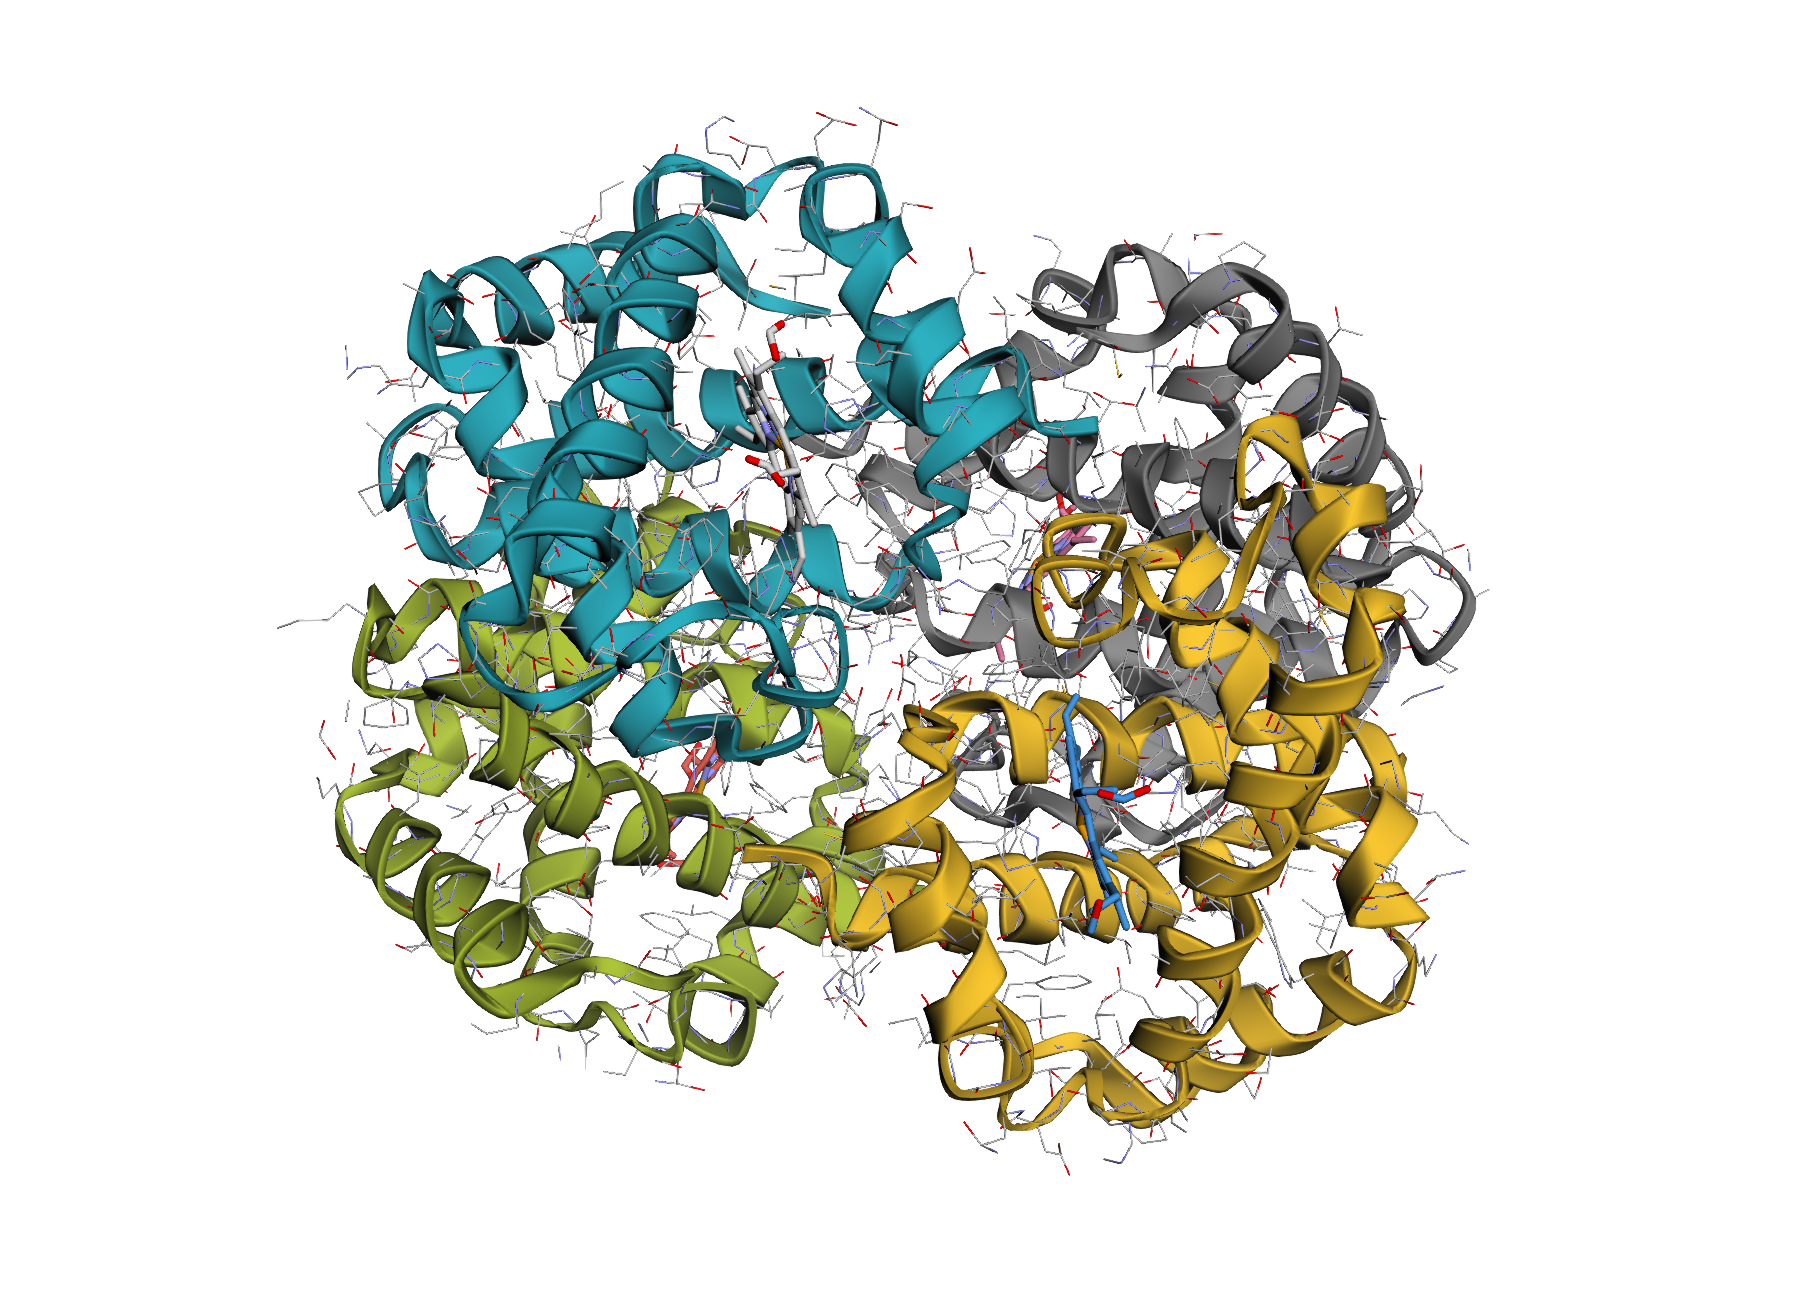
| Default protein view | Surface overlay |
|---|---|
 |
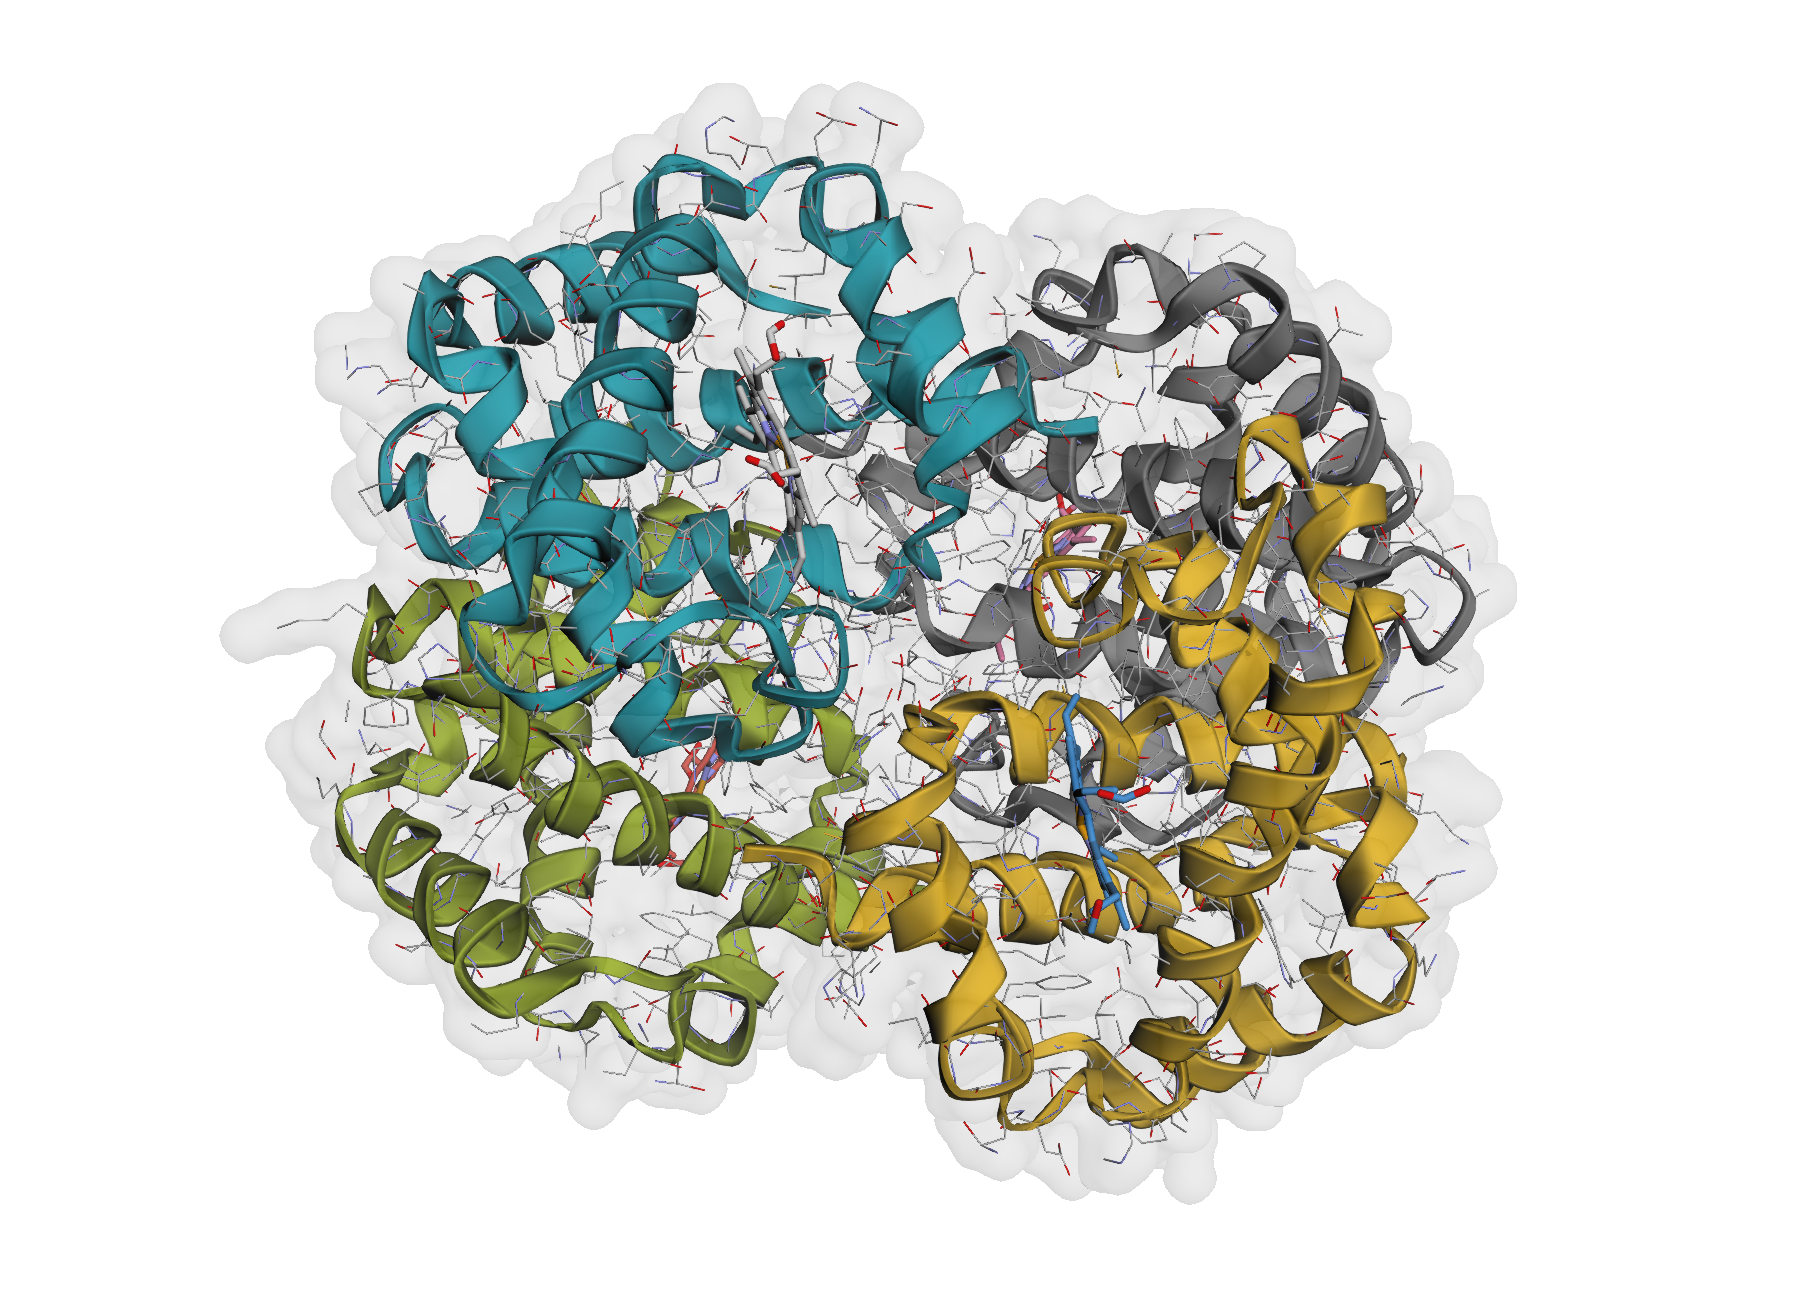 |
| One-line rendering with automatic chain colouring. | Optional translucent VDW surface for shape context. |
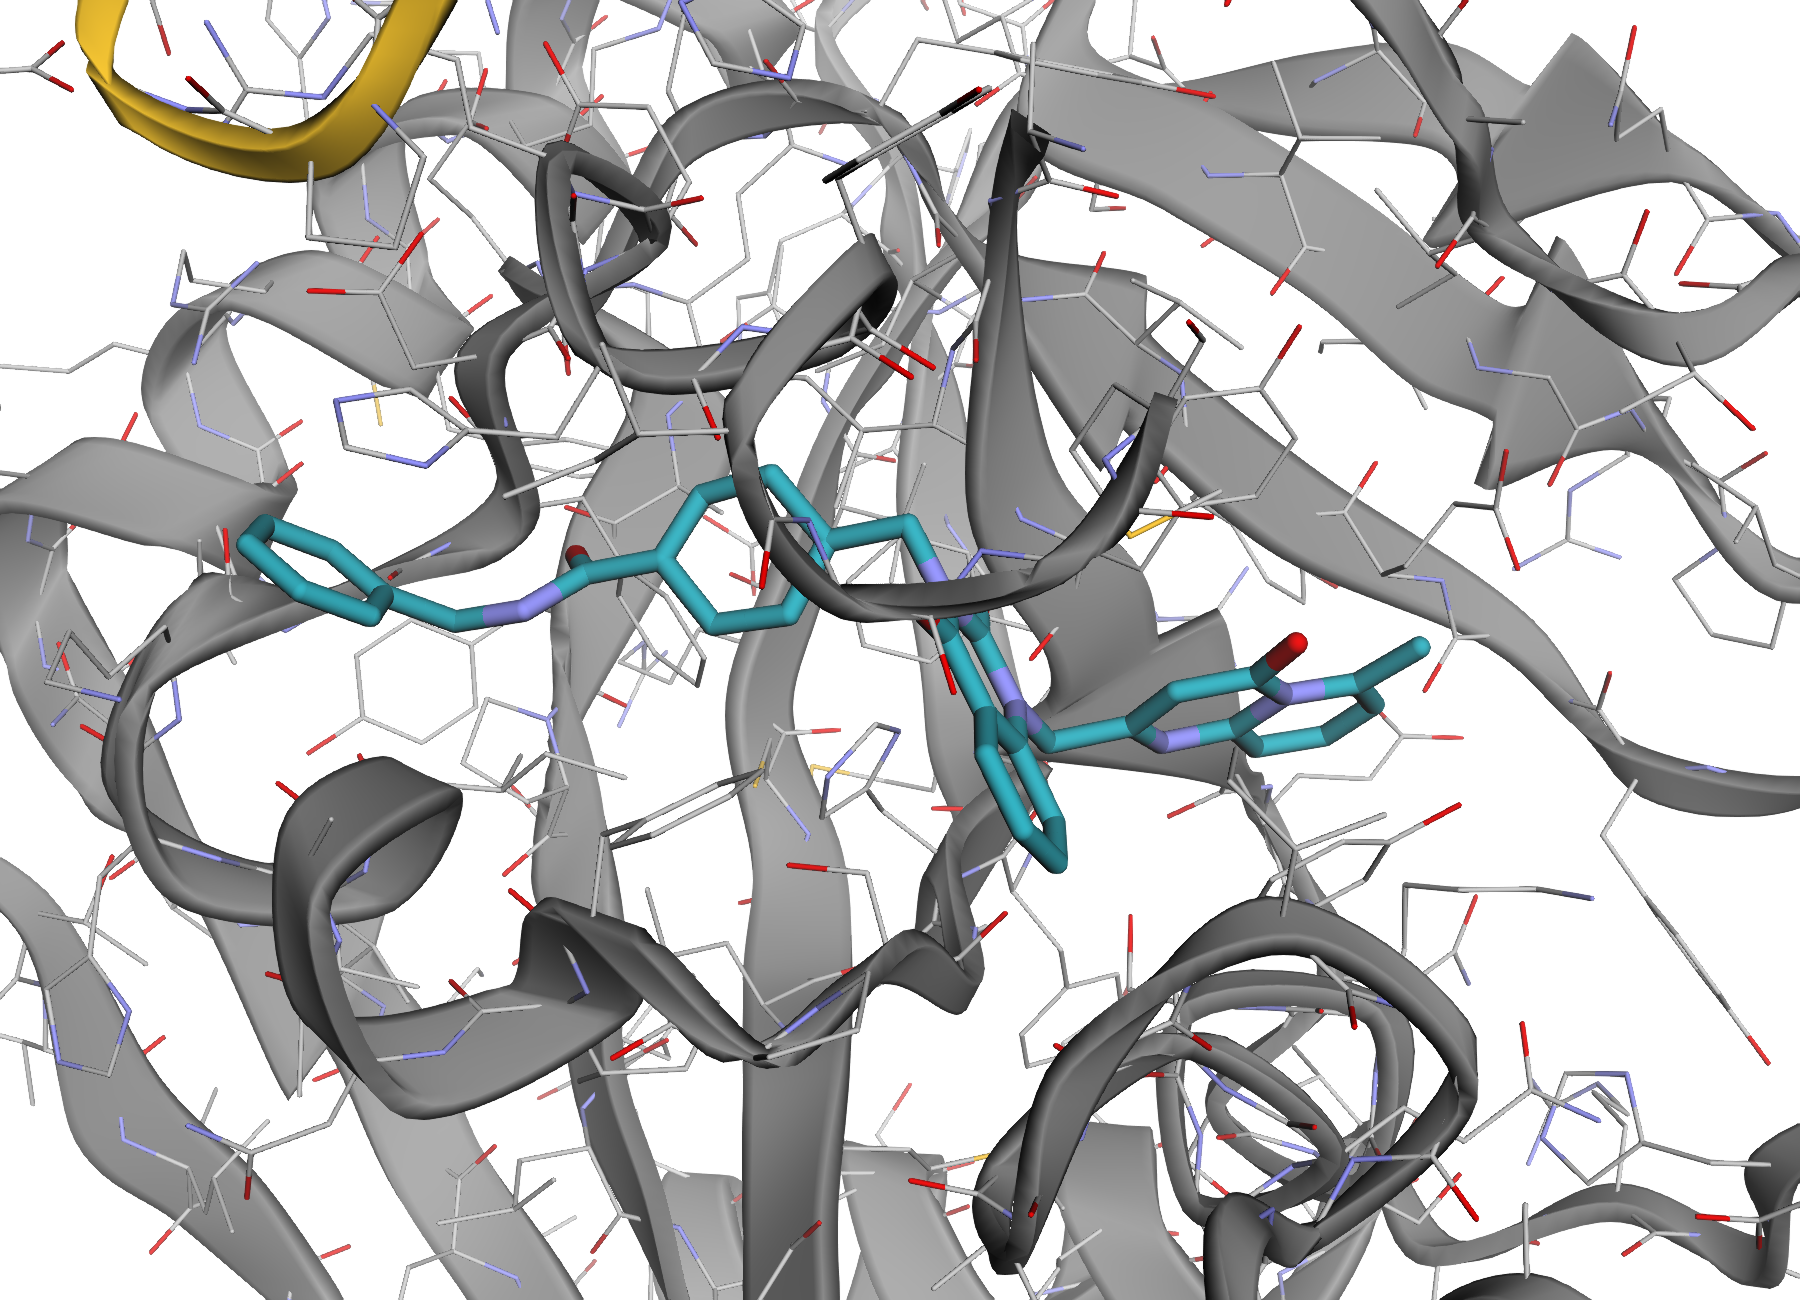
| Ligand focus | Mixed complex |
|---|---|
 |
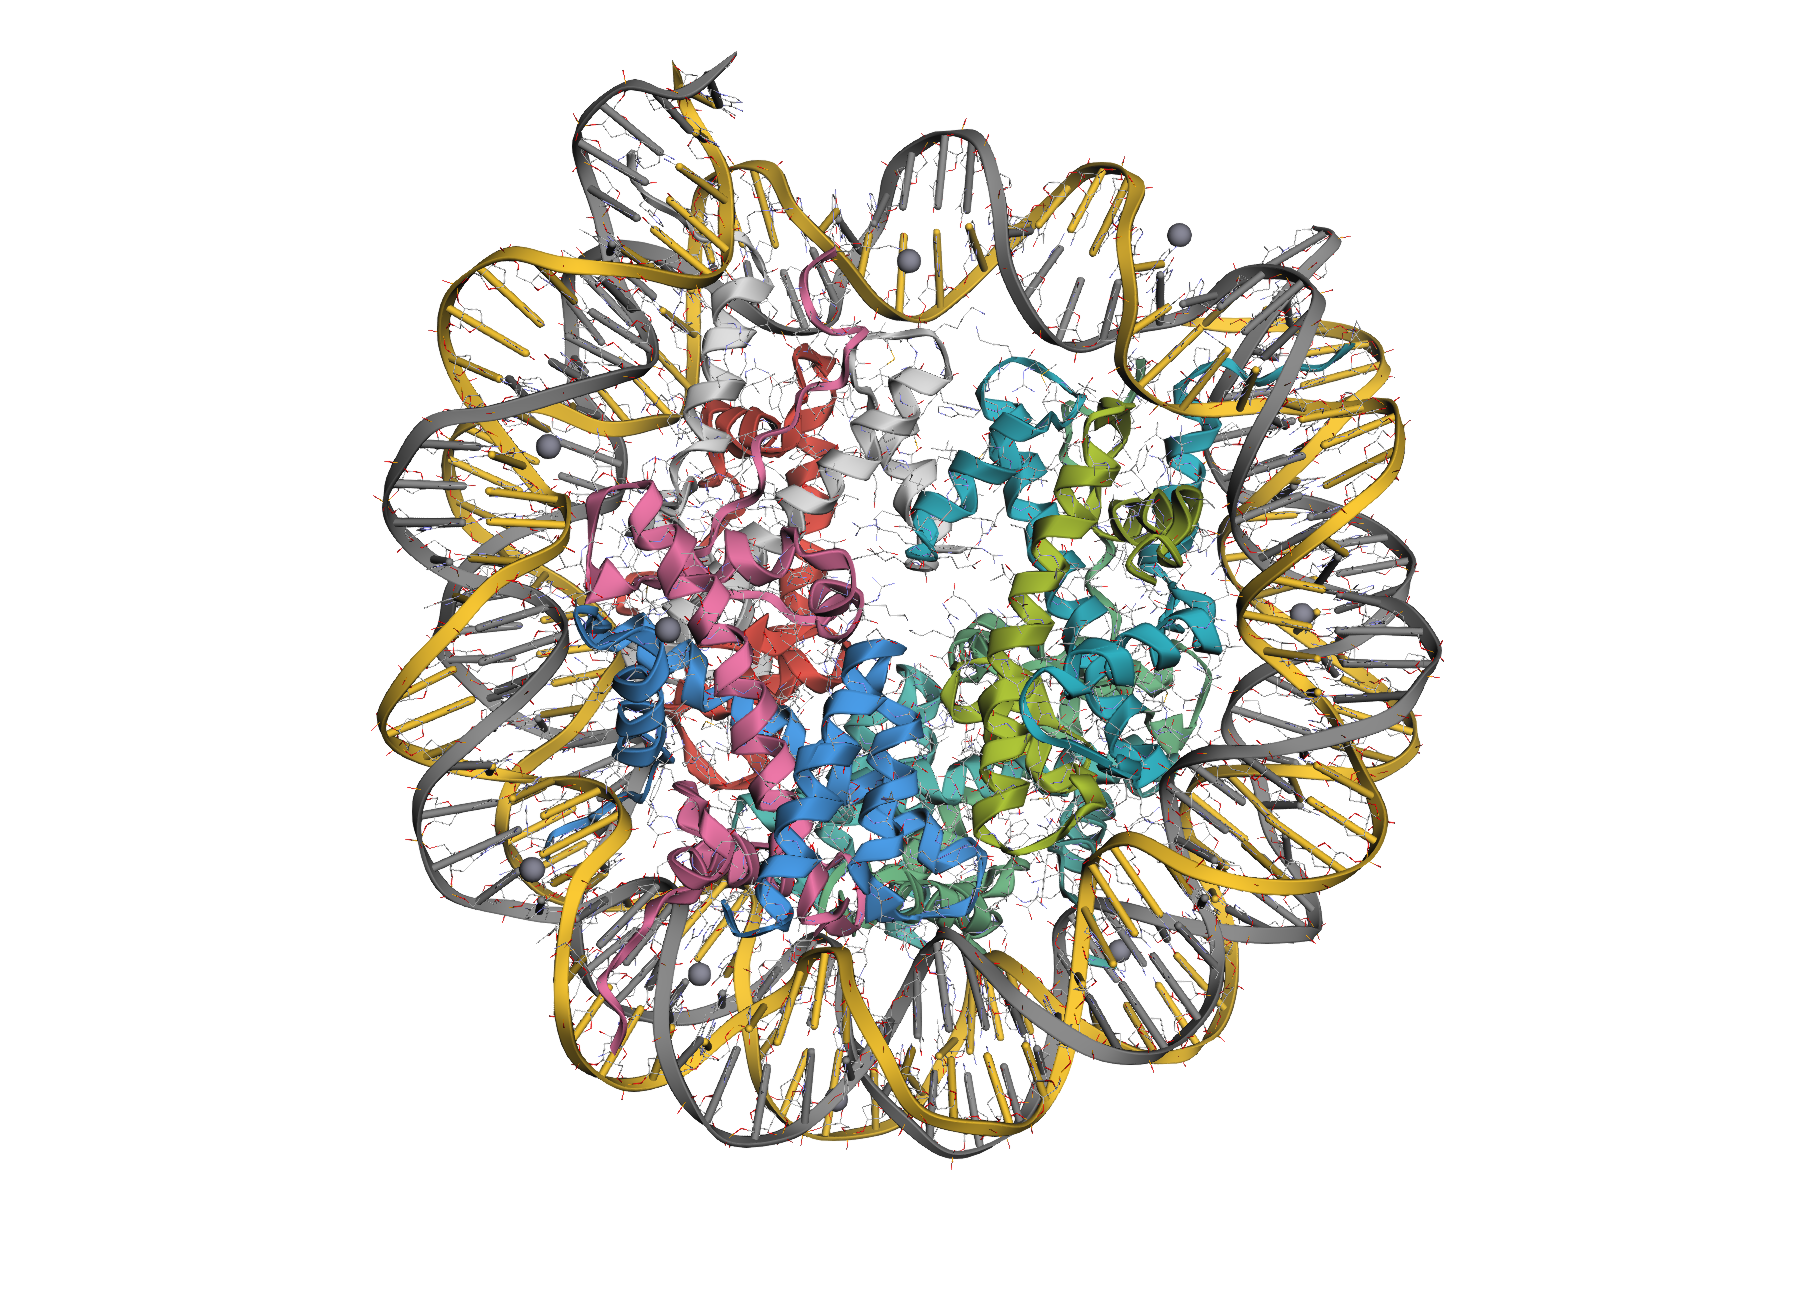 |
| Zoom to a ligand or binding-site selection. | Proteins, nucleic acids, ligands, and ions styled together. |
API
view()
The main entry point. Returns a py3Dmol.view object that renders inline in Jupyter.
from atomview import view

v = view(
    structure,
    show_cartoon=True,            # cartoon for polymers
    show_surface=False,           # VDW surface overlay
    show_hover=True,              # hover labels
    hide_solvent=True,            # remove water
    hide_crystallization_aids=True,
    zoom_to_selection=None,       # e.g. {"chain": "A", "resi": 35}
    width=600,
    height=400,
    colors=None,                  # custom colour list, or use defaults
)
Why not just use atomworks?
atomworks is a fantastic, comprehensive framework for biomolecular modelling maintained by RosettaCommons. But it's a big library — it bundles I/O, transforms, ML dataset tooling, RDKit integration, and more. If you just want to call view(structure) in a notebook, that's a lot of overhead.
atomview gives you exactly that one thing: a great molecular viewer with sensible defaults, in a package that installs in seconds.
License
MIT
1 maintainer

Metadata
1 maintainer
Release files for atomview 0.1.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| atomview-0.1.1.tar.gz | 8.5 kB | With provenance | Details for atomview-0.1.1.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| atomview-0.1.1-py3-none-any.whl | Python 3 | none | any | Details for atomview-0.1.1-py3-none-any.whl |
Total release size: 18.8 kB
Release files / atomview-0.1.1.tar.gz
| Download URL | atomview-0.1.1.tar.gz |
|---|---|
| Size | 8.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
e0a0a83535b35a5eb6201f4e29940cd99ac7de7ef02003351b900a27a3ab3852
|
|
BLAKE2b-256 checksum How to use checksums |
bbf637a434199d192af1a5128f7c2f1a313eec517609bc0e6026c4c9e313cb6b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on May 3, 2026.
Transparency logRelease files / atomview-0.1.1-py3-none-any.whl
| Download URL | atomview-0.1.1-py3-none-any.whl |
|---|---|
| Size | 10.3 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
f573739e311d90da4517d68e4e807a7e2a295833c8c54296d1b66bd84634f982
|
|
BLAKE2b-256 checksum How to use checksums |
cdaaf2c1de4ca835add4872faa589504944c9bd09c0842b729ac693b4fa7979e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on May 3, 2026.
Transparency logSecurity for atomview 0.1.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for atomview-0.1.1.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on May 3, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














