
This project has been archived by its maintainers, and is no longer receiving any updates.
aws fusion
Unified CLI tool for streamlined AWS operations, enhancing developer productivity


Installation
Install via pip install
pip install aws-fusion
Command line tool
To invoke the cli, there are 2 option
- Directly use
aws-fusioncommand - Use it via aws cli alias with
aws fusion
Usage
usage: aws-fusion [<flags>] <command> ...

Unified CLI tool for streamlined AWS operations, enhancing developer productivity

Flags:
  -h, --help    show this help message and exit
  -v, --version Display the version of this tool
  --debug       Turn on debug logging

Command:
  init [<flags>]
    Initialize fusion app with creation of aws fusion alias.

  open-browser [<flags>] [<args>]
    Open a web browser for graphical access to the AWS Console.

    -p, --profile PROFILE The AWS profile to create the pre-signed URL with
    -r, --region REGION   The AWS Region to send the request to
        --no-logout       Skip logging out of the existing AWS console session before signing in (needed for AWS multi-session)
        --clip            Don't open the web browser, but copy the signin URL to clipboard
        --stdout          Don't open the web browser, but echo the signin URL to stdout

  iam-user-credentials [<flags>] <sub-command>
    IAM User credential helper.

  iam-user-credentials get [<flags>] [<args>]
    Retrieve IAM user credentials for AWS CLI profiles or application authentication.

        --access-key ACCESS_KEY AWS access key
        --account-id ACCOUNT_ID AWS Account ID for the name
        --username USERNAME     Username of a AWS user associated with the access key for the name
        --credential-process    Output the credential in AWS credential process syntax

  iam-user-credentials store [<flags>] [<args>]
    Store IAM user access key and secret key securely for streamlined authentication.

        --access-key ACCESS_KEY AWS access key
        --account-id ACCOUNT_ID AWS Account ID for the name
        --username USERNAME     Username of a AWS user associated with the access key for the name
        --secret-key SECRET_KEY AWS secret key

  okta [<flags>] <sub-command>
    Generate AWS session credentials from Okta.

  okta device-auth [<flags>] [<args>]
    Generate AWS session credentials using SAML assertion from Okta device authentication.

        --org-domain ORG_DOMAIN                   Full domain hostname of the Okta org e.g. example.okta.com
        --oidc-client-id OIDC_CLIENT_ID           The ID is the identifier of the client is Okta app acting as the IdP for AWS
        --aws-acct-fed-app-id AWS_ACCT_FED_APP_ID The ID for the AWS Account Federation integration app
        --aws-iam-role AWS_IAM_ROLE               The AWS IAM Role ARN to assume
        --credential-process                      Output the credential in AWS credential process syntax

  config-switch [<flags>] <sub-command>
    Switching between AWS config.

  config-switch profile [<flags>]
    Switch between available aws profile.

  config-switch region [<flags>]
    Switch between available aws region.
Use case of open-browser
This only works with assume-role and federated-login, doesn't work with IAM user or user session.
IAM assume role
Profiles that use IAM roles pull credentials from another profile, and then apply IAM role permissions.
In the following examples, iam-user is the source profile for credentials and iam-assume-role borrows the same credentials then assumes a new role.
Credentials file
[profile iam-user]
aws_access_key_id=AKIAIOSFODNN7EXAMPLE
aws_secret_access_key=wJalrXUtnFEMI/K7MDENG/bPxRfiCYEXAMPLEKEY
Config file
[profile iam-user]
region = us-east-1
output = json

[profile iam-assume-role]
source_profile = iam-user
role_arn = arn:aws:iam::777788889999:role/user-role
role_session_name = my-session
region = ap-south-1
output = json
Federated login
Using IAM Identity Center, you can log in to Active Directory, a built-in IAM Identity Center directory, or another IdP connected to IAM Identity Center. You can map these credentials to an AWS Identity and Access Management (IAM) role for you to run AWS CLI commands.
In the following examples, using aws-sso profile assumes sso-read-only-role on 111122223333 account.
Config file
[profile aws-sso]
sso_session = my-sso-session
sso_account_id = 111122223333
sso_role_name = sso-read-only-role
role_session_name = my-session
region = us-east-1
output = json

[sso-session my-sso-session]
sso_region = us-east-2
sso_start_url = https://my-sso-portal.awsapps.com/start
sso_registration_scopes = sso:account:access
Refer
The docs
- https://docs.aws.amazon.com/IAM/latest/UserGuide/id_roles_providers_enable-console-custom-url.html
- https://docs.aws.amazon.com/cli/latest/userguide/cli-configure-files.html
Usa case of iam-user-credentials store
To store IAM user credential in the system credential store for best security rather than plain text ~/.aws/credentials file.
Manually the save the credential in the store using
aws-fusion iam-user-credentials store \
    --access-key 'AKIAIOSFODNN7EXAMPLE' \
    --secret-key 'wJalrXUtnFEMI/K7MDENG/bPxRfiCYEXAMPLEKEY' \
    --account-id '123456789012' \
    --username 'my-iam-user'
Use case of iam-user-credentials get
Configure aws config file to use credential process
Config file
[profile iam-user]
region = us-east-1
output = json
credential_process = aws-fusion iam-user-credentials get --account-id 123456789012 --username 'my-iam-user' --access-key 'AKIAIOSFODNN7EXAMPLE' --credential-process
Refer
The docs
Use case of okta device-auth
Configure aws config file to use credential process
Config file
[profile iam-user]
region = us-east-1
output = json
credential_process = aws-fusion okta device-auth --org-domain my.okta.com --oidc-client-id 0pbs4fq1q2vbGoFkC1m7 --aws-acct-fed-app-id 0oa8z9xa8BS9b2AFb1t7 --aws-iam-role arn:aws:iam::123456789012:role/PowerUsers --credential-process
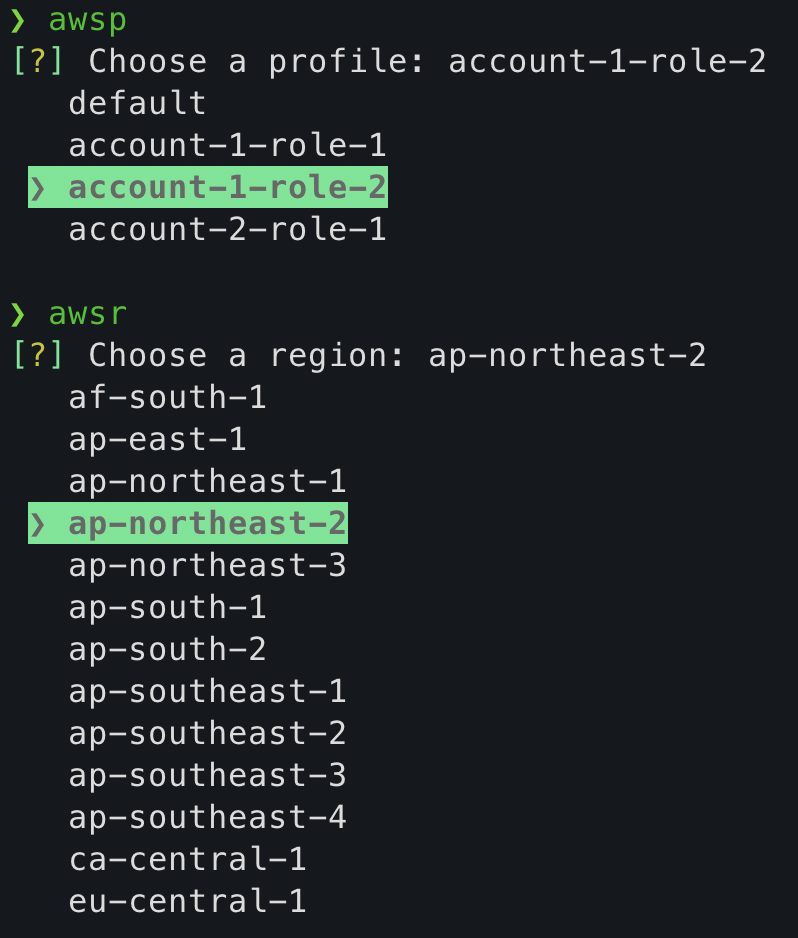
Use case of config-switch
A special of utility script to help easily switch profile and region
For Linux & Darwin (MacOS)
This works with 2 bash script, namely _awsp and _awsr
Post installing the app, create 2 aliases in .bashrc or .zshrc file.
## aws fusion setup
alias awsp="source _awsp"
alias awsr="source _awsr"
Using the command without the aliases will have no effect
For Windows
This works with 2 powershell script, namely _awsp.ps1 and _awsr.ps1
Post installing the app, create 2 aliases in $PROFILE (i.e. $HOME\Documents\PowerShell\Microsoft.PowerShell_profile.ps1) file.
## aws fusion setup
Set-Alias awsp "_awsp.ps1"
Set-Alias awsr "_awsr.ps1"
License
This project is licensed under the Mozilla Public License 2.0 - see the LICENSE file for details.
1 maintainer

Metadata
1 maintainer
Release files for aws-fusion 1.9.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| aws_fusion-1.9.0.tar.gz | 18.5 kB | With provenance | Details for aws_fusion-1.9.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| aws_fusion-1.9.0-py3-none-any.whl | Python 3 | none | any | Details for aws_fusion-1.9.0-py3-none-any.whl |
Total release size: 41.6 kB
Release files / aws_fusion-1.9.0.tar.gz
| Download URL | aws_fusion-1.9.0.tar.gz |
|---|---|
| Size | 18.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
5d6ebdc5acf39d53d5f2a34e22a3de859ee856d22da1089fae6328a8c361b046
|
|
BLAKE2b-256 checksum How to use checksums |
af8326fc13166fe32bb79f0e6884668062007e4b5b51c437bba42814cb3019cf
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 13, 2026.
Transparency logRelease files / aws_fusion-1.9.0-py3-none-any.whl
| Download URL | aws_fusion-1.9.0-py3-none-any.whl |
|---|---|
| Size | 23.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
17b785be969e878ace31f2c173794fae3bf38c1a14df86bbd0beb8c5f42383fd
|
|
BLAKE2b-256 checksum How to use checksums |
b1912e6d46723d092f986f9c1abc951b536b1f6c0aafc614a3d474648c3fb513
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 13, 2026.
Transparency logSecurity for aws-fusion 1.9.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for aws_fusion-1.9.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 13, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














