


A security linter from PyCQA
Free software: Apache license
Documentation: https://bandit.readthedocs.io/en/latest/
Source: https://github.com/PyCQA/bandit
Contributing: https://github.com/PyCQA/bandit/blob/main/CONTRIBUTING.md
Overview
Bandit is a tool designed to find common security issues in Python code. To do this Bandit processes each file, builds an AST from it, and runs appropriate plugins against the AST nodes. Once Bandit has finished scanning all the files it generates a report.
Bandit was originally developed within the OpenStack Security Project and later rehomed to PyCQA.
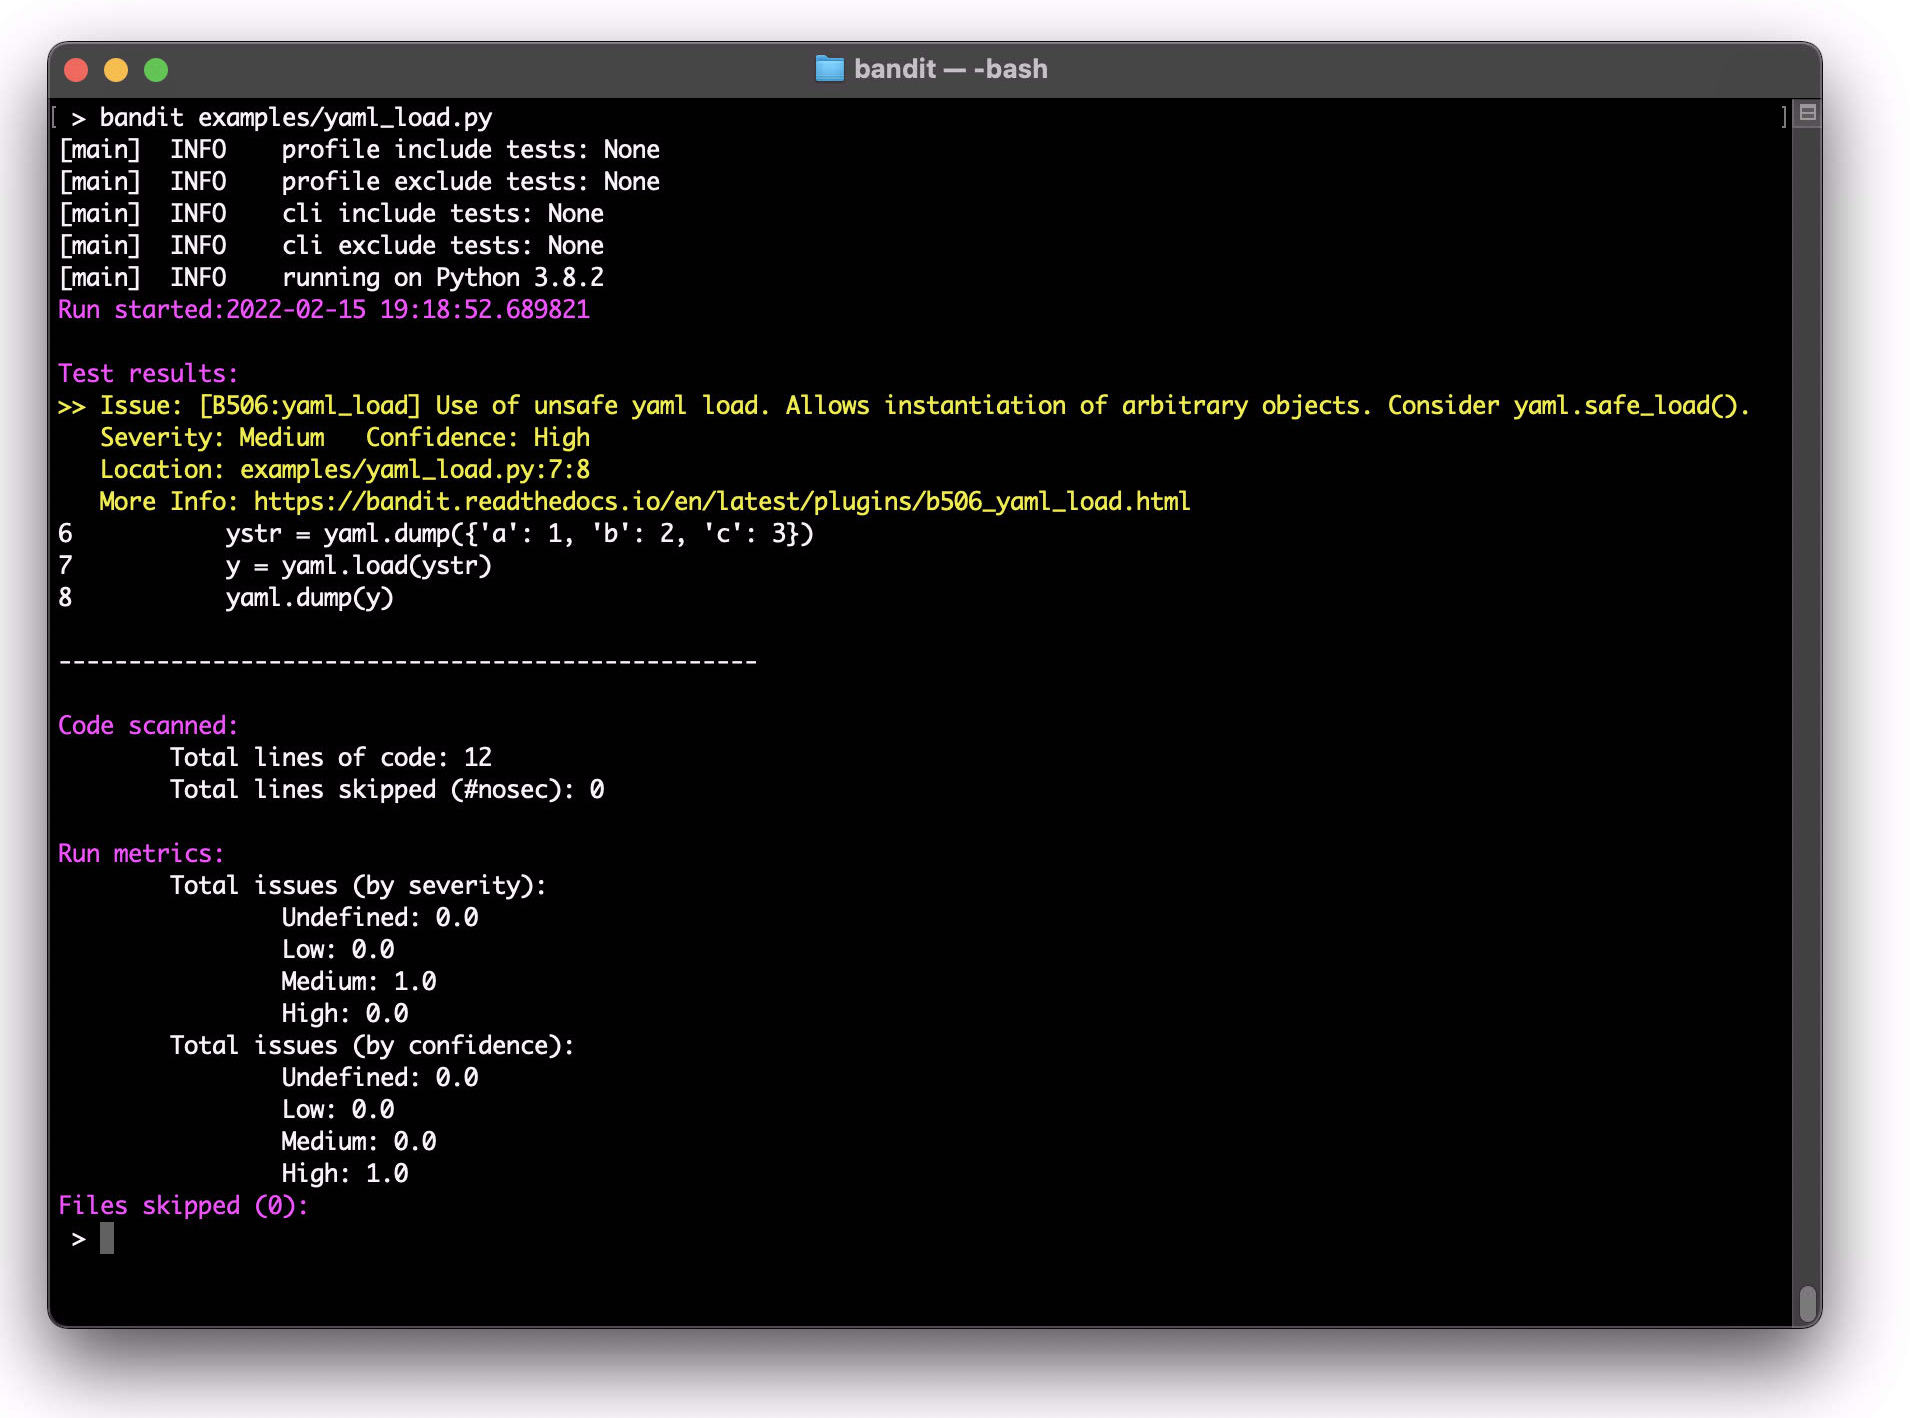
Show Your Style

Use our badge in your project’s README!
using Markdown:
[](https://github.com/PyCQA/bandit)
using RST:
.. image:: https://img.shields.io/badge/security-bandit-yellow.svg
    :target: https://github.com/PyCQA/bandit
    :alt: Security Status
References
Python AST module documentation: https://docs.python.org/3/library/ast.html
Green Tree Snakes - the missing Python AST docs: https://greentreesnakes.readthedocs.org/en/latest/
Documentation of the various types of AST nodes that Bandit currently covers or could be extended to cover: https://greentreesnakes.readthedocs.org/en/latest/nodes.html
Container Images
Bandit is available as a container image, built within the bandit repository using GitHub Actions. The image is available on ghcr.io:
docker pull ghcr.io/pycqa/bandit/banditThe image is built for the following architectures:
amd64
arm64
armv7
armv8
To pull a specific architecture, use the following format:
docker pull --platform=<architecture> ghcr.io/pycqa/bandit/bandit:latestEvery image is signed with sigstore cosign and it is possible to verify the source of origin using the following cosign command:
cosign verify ghcr.io/pycqa/bandit/bandit:latest \
  --certificate-identity https://github.com/pycqa/bandit/.github/workflows/build-publish-image.yml@refs/tags/<version> \
  --certificate-oidc-issuer https://token.actions.githubusercontent.com
Where <version> is the release version of Bandit.
Sponsors
The development of Bandit is made possible by the following sponsors:
|

|
|
If you also ❤️ Bandit, please consider sponsoring.


Release files for bandit 1.9.4
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| bandit-1.9.4.tar.gz | 4.2 MB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| bandit-1.9.4-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 4.4 MB
Release files / bandit-1.9.4.tar.gz
| Download URL | bandit-1.9.4.tar.gz |
|---|---|
| Size | 4.2 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
b589e5de2afe70bd4d53fa0c1da6199f4085af666fde00e8a034f152a52cd628
|
|
BLAKE2b-256 checksum How to use checksums |
aac30cb80dfe0f3076e5da7e4c5ad8e57bac6ac357ff4a6406205501cade4965
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 25, 2026.
Transparency logRelease files / bandit-1.9.4-py3-none-any.whl
| Download URL | bandit-1.9.4-py3-none-any.whl |
|---|---|
| Size | 134.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
f89ffa663767f5a0585ea075f01020207e966a9c0f2b9ef56a57c7963a3f6f8e
|
|
BLAKE2b-256 checksum How to use checksums |
05a4a26d5b25671d27e03afb5401a0be5899d94ff8fab6a698b1ac5be3ec29ef
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 25, 2026.
Transparency log













