
Read and verify Bitcoin from your terminal. Zero dependencies, no Bitcoin Core required.
Reads the chain through the Mempool.space public API, or your own Mempool instance, and checks what it can by computation: address checksums offline, and a transaction against its block's Merkle proof and proof of work.


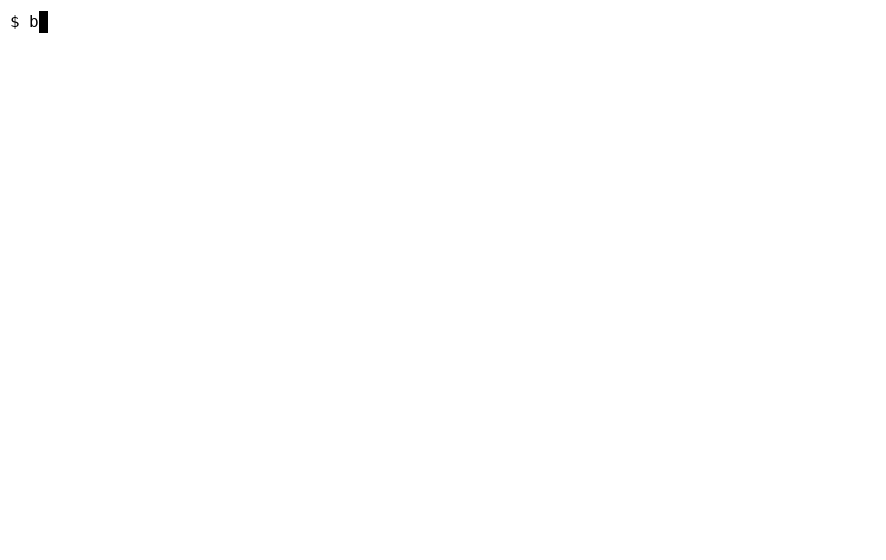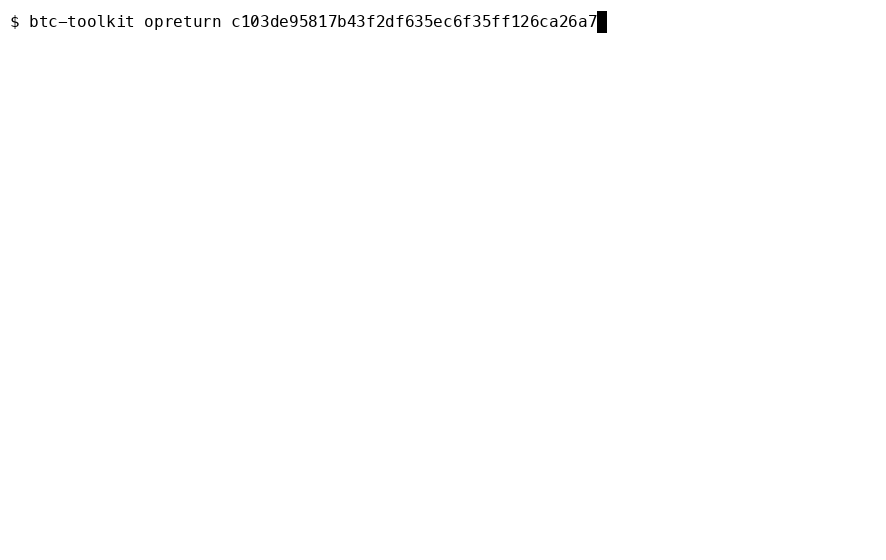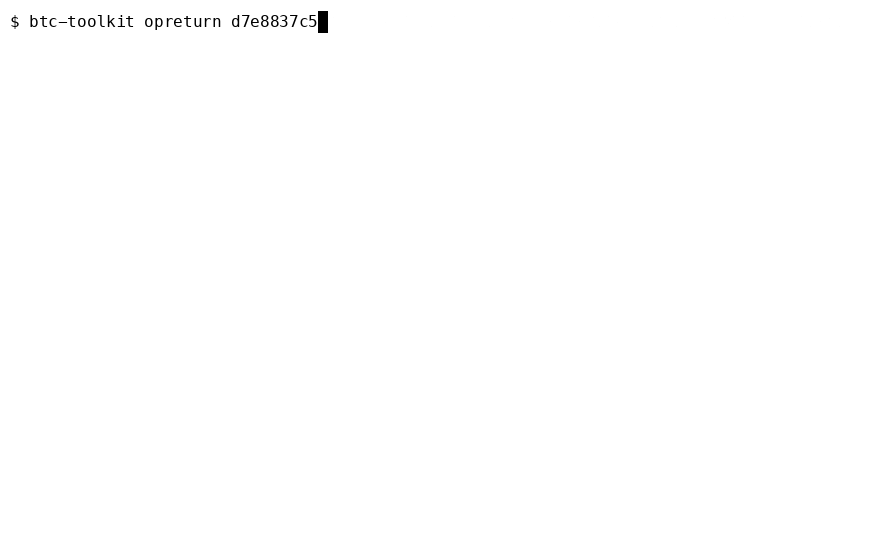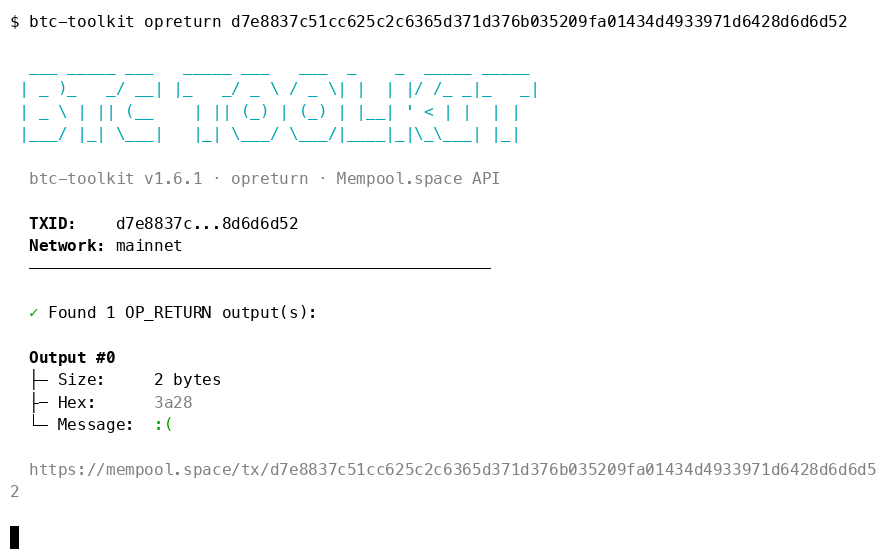
The $320M Liquid Network drain was negotiated on-chain. Two of its messages, decoded live — read the whole story.
Quick start
pipx install btc-toolkit        # or: pip install btc-toolkit · brew install devdavidejesus/tap/btc-toolkit
btc-toolkit fees                # current fee rates
btc-toolkit opreturn f4ac7abcb689df30ec5e8d829733622f389ca91367c47b319bc582e653cd8cab
btc-toolkit verify c103de95817b43f2df635ec6f35ff126ca26a7c6d20570c4b01866b2b3e69a19   # check it is in a block
btc-toolkit validate bc1qar0srrr7xfkvy5l643lydnw9re59gtzzwf5mdq                         # offline: nothing sent
Try it without installing anything: uvx btc-toolkit block 0.
Options go after the command: btc-toolkit fees --network signet, not
btc-toolkit --network signet fees. -n is short for --network, and
btc-toolkit <command> --help lists every option of a command.
Commands
| Command | Description |
|---|---|
btc-toolkit opreturn <txid> |
Decode OP_RETURN messages from a transaction |
btc-toolkit tx <txid> |
Transaction details: status, fees, size, input/output totals, RBF |
btc-toolkit address <address> |
Aggregated overview: type, balance, lifetime totals |
btc-toolkit balance <address> |
Confirmed + unconfirmed balance of any address |
btc-toolkit fees |
Recommended fee rates + mempool backlog |
btc-toolkit block <height|hash|latest> |
Block metadata by height, hash, or latest |
btc-toolkit utxo <address> |
Unspent outputs of any address |
btc-toolkit verify <txid> |
Check a transaction is in a block by computation: its Merkle proof and the header's proof of work |
btc-toolkit decode <rawtx> |
Decode a raw transaction offline (or --txid: fetch it and check its hash) |
btc-toolkit validate <address> |
Check an address offline: checksum, network, type — nothing is sent |
btc-toolkit inscription <txid> |
Ordinals inscription envelopes in a transaction: content type, size, SHA-256, text |
Every command, option and example: command reference.
What it verifies, and what it doesn't
Inspect Bitcoin data. Verify what you can. Know what you trust.
btc-toolkit is an explorer client for the terminal: a fast, scriptable way to inspect the Bitcoin blockchain without running infrastructure, for scripting, quick lookups, and learning how Bitcoin data is structured. It reads a Mempool API — mempool.space by default, or your own instance. Most commands report what that API says; some check it, or need no API at all:
| Command | Computed by btc-toolkit | Taken from the API |
|---|---|---|
validate |
Checksum, network and type — offline | Nothing |
decode |
Everything, from the raw bytes — offline | With --txid, the raw transaction, checked against the txid (which does not cover the witness) |
verify |
The txid, the Merkle root, the header hash and its proof of work | The raw transaction, the Merkle proof and the header (each checked), and the block height |
tx |
The addresses in --inputs / --outputs, from each output script, on a named network |
Status, fee, values and what spent each output |
address |
The address type, from the checksum-verified address | Balances, lifetime totals and counts |
opreturn, inscription |
The decoding of the scripts and envelopes | The transaction, unchecked (decode --txid checks one); inscriptions could not be checked even then, as a txid does not commit to the witness |
balance, utxo |
The address check, before any request | Balances and UTXOs |
block, fees |
Nothing | Everything shown |
What no command does: validate blocks, follow the most-work chain, or check consensus rules. For sovereign,
trustless verification, run Bitcoin Core and query it directly. The full threat model is
in SECURITY.md; how releases are built and how to verify one yourself, in
docs/releases.md.
verify — check a transaction is in a block
btc-toolkit verify c103de95817b43f2df635ec6f35ff126ca26a7c6d20570c4b01866b2b3e69a19
Instead of taking the API's "confirmed" on faith, verify recomputes the txid from the raw transaction, folds it up
the Merkle proof to the root (refusing 64-byte transactions posing as nodes, CVE-2017-12842), hashes the 80-byte
header that must contain that root, and checks its proof of work against the target its bits encode. The verdict
depends only on the work proven:
✓ VERIFIED("work": "strong"): a mainnet header at difficulty 50 T or more (btc-toolkit's own threshold, not a consensus rule) — about 2^77.5 hashes to forge.⚠ CONSISTENT, WEAK WORK("work": "weak"): everything checks out, but the header carries less work. That is cheap to fake: treat it as consistency, not proof. With--json,verifiedistruein both cases, so a script that must reject forged proofs should also require"work": "strong".
It does not prove the block height (the API reports it) or that the block is in the chain everyone follows. Details: command reference.
Installation
Python 3.11+ (supported versions), no dependencies:
pipx install btc-toolkit                       # isolated, via pipx
pip install btc-toolkit                        # or with pip
uv tool install btc-toolkit                    # or with uv (uvx btc-toolkit ... runs it without installing)
brew install devdavidejesus/tap/btc-toolkit    # or Homebrew, on macOS and Linux
git clone https://github.com/devdavidejesus/btc-toolkit.git && pip install -e btc-toolkit   # or from source
Shell completion (optional): static scripts in completions/ for bash, zsh and fish —
tab-complete commands, networks and flags. The Homebrew formula installs them for you.
Scripting
Every command takes --json, and the commands that take a txid, address or block read one item per line from
stdin (-) or a file (--file), emitting JSON Lines:
cat txids.txt | btc-toolkit tx - --json | jq -r '.fee_rate_sat_vb'
Exit codes are a contract: 0 ok · 1 network/API failure (or a failed verify) · 2 invalid input. Output
schemas and the stability policy: docs/json-schema.md; environment variables
(BTC_TOOLKIT_API_URL, BTC_TOOLKIT_NETWORK, BTC_TOOLKIT_TIMEOUT, NO_COLOR), retries and timeouts:
scripting and configuration.
Every command is also a plain, typed Python function (the package ships py.typed):
from btc_toolkit.opreturn import decode_op_return

for out in decode_op_return("c103de95817b43f2df635ec6f35ff126ca26a7c6d20570c4b01866b2b3e69a19"):
    print(out.decoded_text)   # we are whitehats. contact us on chain
Functions, result types and errors: docs/python-api.md.
Use your own Mempool instance
Every command accepts --api-url pointing to a self-hosted Mempool instance,
which runs on top of your own Bitcoin node (Umbrel, Start9, RaspiBlitz and similar node stacks offer it as an app):
btc-toolkit balance <address> --api-url http://umbrel.local:3006/api -n mainnet
-n tells btc-toolkit which chain your instance serves. Without it the chain is custom (unknown): addresses of
any Bitcoin network (mainnet, testnet/signet, regtest) are accepted, tx shows the API's addresses, and verify
reports the work as weak. Results never link to mempool.space when you use your own instance. With your own
instance, no third party sees your queries — the public mempool.space API is the zero-setup default, not a
requirement.
Seen in the wild
- The $320M Liquid Network drain (Sept 2026) was negotiated on-chain via OP_RETURN — every message of it decoded
with
opreturn, transaction IDs included: I Read a $320M Ransom Negotiation From My Terminal. - The wallet holding 562 BTC from the Coldcard hack (July 2026) became a message board: 49 OP_RETURN messages, read
with
opreturn --file: 49 Messages to a Thief.
btc-toolkit is listed on bitcoin.org's Development page and among the developer tools in Jameson Lopp's Bitcoin resources.
Roadmap
The original five-phase roadmap (OP_RETURN reader, balance, fees, blocks, UTXOs) shipped in v1.0.0; every release
since is in the CHANGELOG. What's next lives in the issues — testnet4
(#64), plain Esplora backends (#65) and a --json cookbook (#63);
good first issue marks the easy ones. Out of scope,
for good: keys, signing, broadcasting and runtime dependencies.
Don't Trust, Verify
Every txid, address, hex value, and technical claim in this README can be independently verified:
- Transaction data:
https://mempool.space/api/tx/<txid> - Address data:
https://mempool.space/api/address/<address> - Fee data:
https://mempool.space/api/v1/fees/recommended - Block data:
https://mempool.space/api/block/<hash> - UTXO data:
https://mempool.space/api/address/<address>/utxo - OP_RETURN spec: learnmeabitcoin.com/technical/script/return
- Esplora API model: github.com/Blockstream/esplora/blob/master/API.md
Support
btc-toolkit is free, MIT-licensed and has no sponsor. If it's useful to you, you can support its development on-chain:
Bitcoin: bc1qulq8xfcmgxxumjx3yndkfktqgw2exh0rym45sn
(Public address — donations are visible on-chain, as everything here is.)
Contributing
Found a bug or want to propose or build a new command? Open an issue or a PR. Every contribution keeps the
core rules — stdlib only, tests with every change, claims verifiable on-chain. The process, the project layout and
how to run the tests are in CONTRIBUTING.md.
Licensed under MIT · Built by @devdavidejesus
"Don't Trust, Verify."
1 maintainer

Metadata
1 maintainer
Release files for btc-toolkit 1.8.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| btc_toolkit-1.8.2.tar.gz | 90.8 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| btc_toolkit-1.8.2-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 145.4 kB
Release files / btc_toolkit-1.8.2.tar.gz
| Download URL | btc_toolkit-1.8.2.tar.gz |
|---|---|
| Size | 90.8 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
8ebdf7b026bc2a3b0ec31ce9073656b5b66021a7d2391dbbc4b4b88780ec1111
|
|
BLAKE2b-256 checksum How to use checksums |
3435e62298100d2b98a3680aefef86a783772566d5b45dac04056140d99023b4
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 22, 2026.
Transparency logRelease files / btc_toolkit-1.8.2-py3-none-any.whl
| Download URL | btc_toolkit-1.8.2-py3-none-any.whl |
|---|---|
| Size | 54.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
ba55a4f04f844509bf80d0c96661630f8a42a9b79e13f6323e6c8ac0346b4c35
|
|
BLAKE2b-256 checksum How to use checksums |
b09f717b2047b25ece6402617de528c6809898922064dae624894f7cb2b423b8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 22, 2026.
Transparency logSecurity for btc-toolkit 1.8.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for btc_toolkit-1.8.2.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 22, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














