
CAGE-lite
Prebind assurance for AI-agent actions at the business consequence boundary.
Try the live CAGE-lite demo →
Install from PyPI
·
View release v0.1.2
Agent platforms govern how agents run. CAGE governs whether agent actions are allowed to become business consequences.
CAGE-lite is my open-source reference implementation of CAGE: Control, Assurance, and Governance Evaluation.
The broader framework is introduced in CAGE-1. CAGE-lite focuses on making its Prebind Assurance model visible, testable, and easier to evaluate in practice.
The project started with a simple question:
An AI agent can propose an action, but what should happen before that action becomes real?
Before an agent releases a payment, grants access, approves a transaction, updates a system of record, or discloses protected information, an organization should be able to verify that the action is authorized and supported by the required evidence.
CAGE adds that final assurance step before the action becomes a binding business consequence.
CAGE-lite is currently a v1 product preview. The Python package version is 0.1.2, and the current CAGE Warrant schema is version 0.4.
CAGE-1 defines a broader evaluation framework across twelve areas. This release focuses on the Prebind Assurance path: evaluating an action before it crosses the business consequence boundary, recording the decision, and proving whether the resulting effect was blocked or allowed to bind.
Product preview
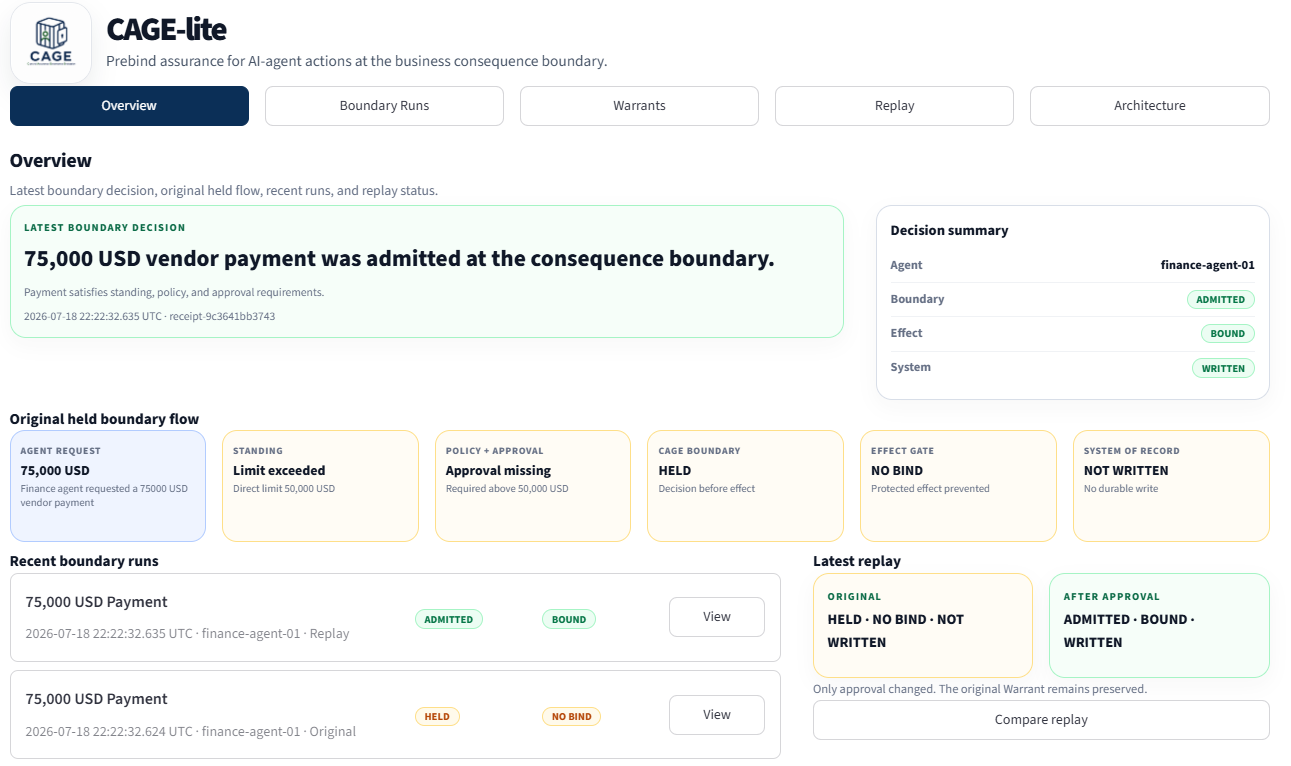
The CAGE-lite dashboard shows the latest boundary decision, the original held action, recent boundary runs, and the result of replaying the action after the missing evidence is supplied.
The hosted demo automatically loads the standard USD 75,000 held-to-admitted replay, allowing visitors to inspect the boundary decision, CAGE Warrants, replay linkage, and effect proof without installing anything locally.
Quick start
CAGE-lite requires Python 3.10 or later.
Install from PyPI
In an active Python 3.10 or later environment:
python -m pip install cage-lite
python -m cage_lite.demo.payment_replay
This runs the packaged payment replay and writes the generated artifacts under playground/v04-replay-demo/ in the current working directory.
To run the Streamlit dashboard, inspect the examples, or contribute changes, install CAGE-lite from source.
Windows PowerShell
git clone https://github.com/roopamwsure/cage-lite.git
cd .\cage-lite

python -m venv .venv
.\.venv\Scripts\Activate.ps1

python -m pip install --upgrade pip
python -m pip install -e .

python -m cage_lite.demo.payment_replay
python -m streamlit run cage_lite/ui/app.py
macOS and Linux
git clone https://github.com/roopamwsure/cage-lite.git
cd cage-lite

python3 -m venv .venv
source .venv/bin/activate

python -m pip install --upgrade pip
python -m pip install -e .

python -m cage_lite.demo.payment_replay
python -m streamlit run cage_lite/ui/app.py
The replay demo creates one original HELD Warrant and one linked ADMITTED replay Warrant under:
playground/v04-replay-demo/
The Streamlit application loads those artifacts by default. Developer controls remain hidden unless they are explicitly enabled.
Examples
The examples/ directory contains smaller demonstrations of individual CAGE behaviors:
payment_policy_demo.pyevaluates the payment policy and produces a held boundary decision without attempting an effect.payment_no_bind_demo.pyshows that a held action does not execute and records durableNO_BINDeffect proof.payment_approval_demo.pyadds the required approval, admits the action, executes the protected effect, and recordsBOUNDproof.payment_narrowed_demo.pynarrows the requested payment to the agent's permitted scope and records the scoped effect result.
Run an example from the repository root:
python examples/payment_no_bind_demo.py
python examples/payment_approval_demo.py
python examples/payment_narrowed_demo.py
The examples write local CAGE Warrants, evidence records, and effect records under playground/. The generated output is excluded from Git.
Where CAGE fits
CAGE does not replace agent runtimes, IAM, policy engines, guardrails, gateways, approval systems, observability platforms, or agent evaluation frameworks.
Those systems produce important signals. CAGE consumes those signals and evaluates whether a proposed action should be allowed to cross the business consequence boundary.
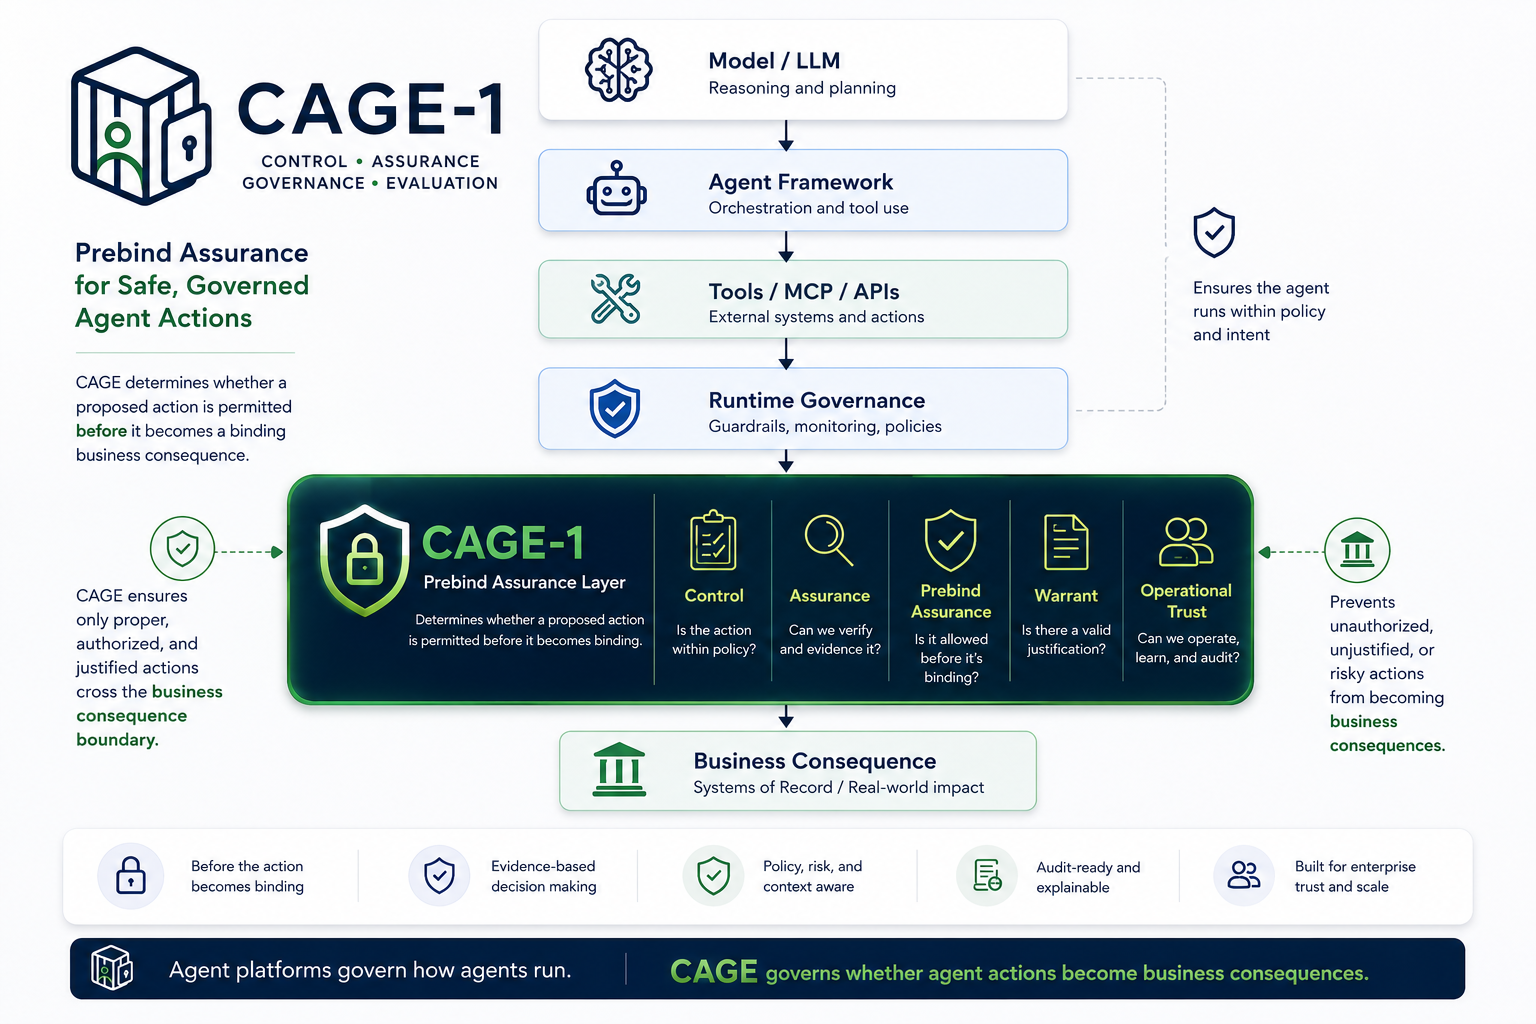
The diagram above shows the broader CAGE framework. CAGE-lite is the open-source implementation used to make this assurance model visible, testable, and easier to evaluate.
The basic idea
A simplified CAGE flow looks like this:
Agent proposes an action
        |
        v
Identity, standing, policy, and approval signals
        |
        v
CAGE prebind boundary
        |
        +---- HELD ----> NO_BIND ----> Business effect blocked
        |
        +---- ADMITTED -> BOUND ------> Business effect executed
        |
        v
CAGE Warrant and effect proof
CAGE Warrant
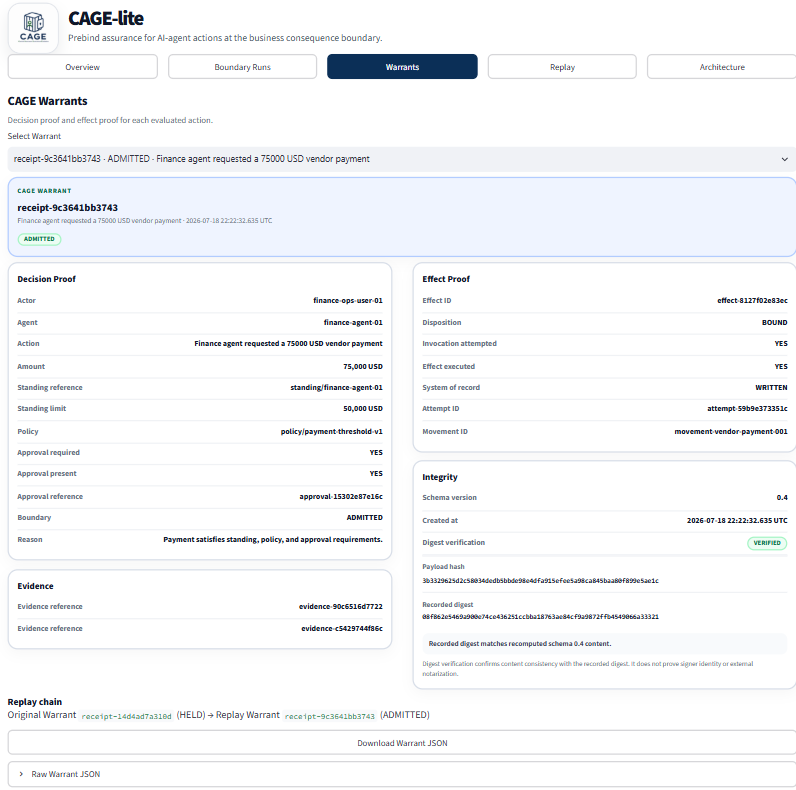
Each evaluated action produces a CAGE Warrant containing decision proof, effect proof, evidence references, replay linkage, and integrity information.
The Warrant distinguishes between deciding that an action may proceed and proving what happened after that decision.
Held-to-admitted replay
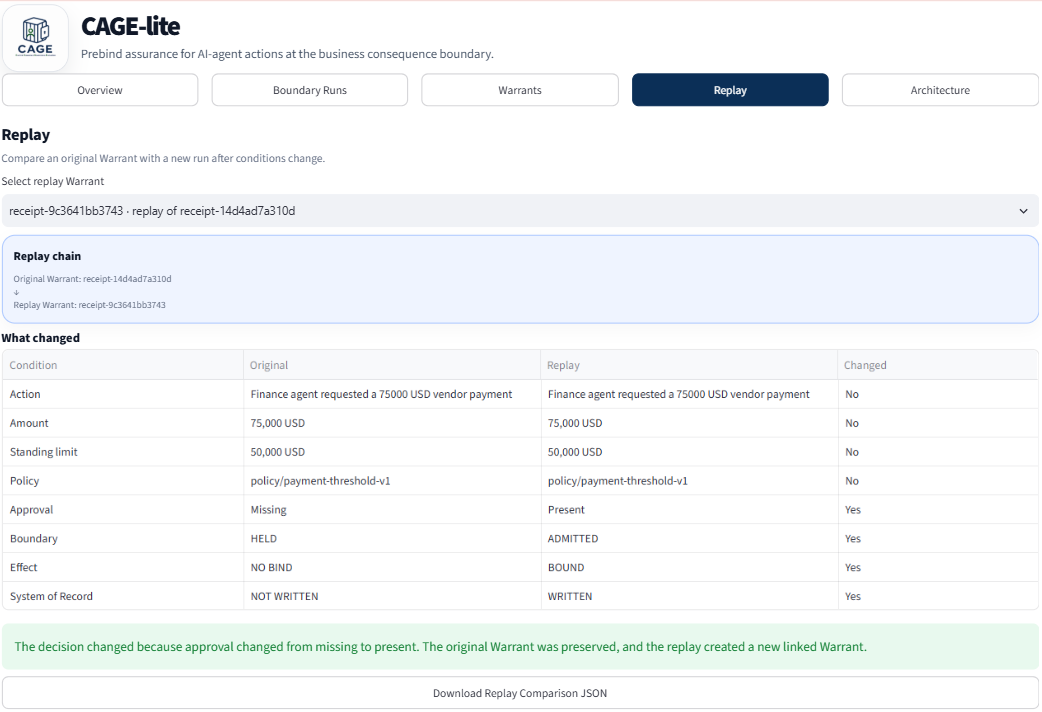
The included demo begins with a USD 75,000 vendor payment that exceeds the agent's USD 50,000 direct standing limit.
Without the required human approval, CAGE holds the action before effect execution:
- boundary:
HELD; - effect:
NO_BIND; - system of record:
NOT_WRITTEN.
The action is then replayed after approval evidence is added. The action, amount, standing limit, and policy remain unchanged. Only the approval state changes.
The replay is admitted, the effect is allowed to bind, and the original held Warrant remains preserved and linked to the replay Warrant.
Project links
- Live CAGE-lite demo
- CAGE-lite on PyPI
- CAGE-lite v0.1.2 release
- CAGE-1 on arXiv
- CAGE-1 author-hosted PDF
- Changelog
- Contributing guide
- Security policy
- Report an issue or request a feature
License
CAGE-lite is licensed under the Apache License 2.0.
1 maintainer

Metadata
1 maintainer
Release files for cage-lite 0.1.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| cage_lite-0.1.2.tar.gz | 927.0 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| cage_lite-0.1.2-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 1.8 MB
Release files / cage_lite-0.1.2.tar.gz
| Download URL | cage_lite-0.1.2.tar.gz |
|---|---|
| Size | 927.0 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
2b2c0d566ed0eabd19d7221ee2308f9a098a5093df56a6b465df9a7de0dfb70d
|
|
BLAKE2b-256 checksum How to use checksums |
77dbfd56291e40f8d4f48e53310634853cdf628c5c17f5cdfba6917fad78e009
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 21, 2026.
Transparency logRelease files / cage_lite-0.1.2-py3-none-any.whl
| Download URL | cage_lite-0.1.2-py3-none-any.whl |
|---|---|
| Size | 921.8 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
ef0bdaebfc9e2822ae44fa6f8e47bbfa953ac8e96b1c23a999a8f93b29fa0617
|
|
BLAKE2b-256 checksum How to use checksums |
ea109ee61fc0c063ef9fb1e89783505a749f80f119ba776c7ddde560148610e5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 21, 2026.
Transparency logSecurity for cage-lite 0.1.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for cage_lite-0.1.2.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 21, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














