
🧭 Canopus: Canonical-Optimized Placement Utility Suite for Quantum Compilation



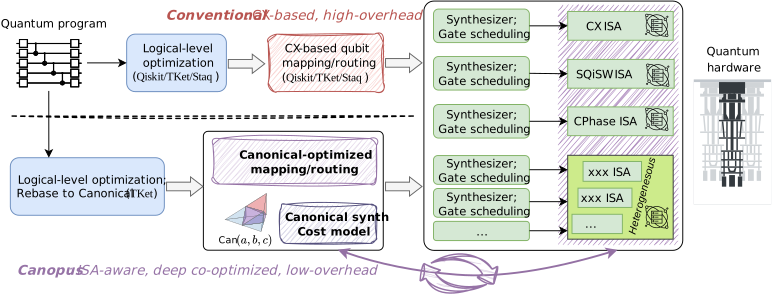
Canopus (Canonical-Optimized Placement Utility Suite) is a unified qubit mapping/routing framework tailored to diverse quantum ISAs, i.e., the implementation of the paper "Unifying Qubit Routing Across Diverse Quantum ISAs via Canonical Representation". Its main function is to optimize the layout and routing of qubits on quantum hardware, handling optimal synthesis with diverse ISAs in a unified approach through two-qubit canonical gate representation, providing guidance for hardware-software co-design.
Canopus evokes the name of the second-brightest star in the sky, symbolizing its role as a "navigational" guide for routing qubits through the complex constraints of quantum hardware.
Installation
Prerequisite: monodromy (+ lrslib)
Canopus depends on the monodromy library for Weyl-chamber coverage computation. monodromy is not on PyPI and must be installed manually before pip install canopus-quantum:
pip install git+https://github.com/Youngcius/monodromy
monodromy itself needs the lrs binary from lrslib. Platform-specific setup:
macOS
brew install gmp
cd lrslib-073 && make
sudo make install
Ubuntu / Debian
sudo apt update && sudo apt install -y build-essential libgmp-dev
cd lrslib-073 && make
sudo make install
Conda (any OS)
conda install -c conda-forge gmp
cd lrslib-073
make INCLUDEDIR="$CONDA_PREFIX/include" LIBDIR="$CONDA_PREFIX/lib"
make prefix=$HOME/.local install
echo 'export PATH="$HOME/.local/bin:$PATH"' >> ~/.bashrc && source ~/.bashrc
From PyPI (recommended)
pip install canopus-quantum
Pre-compiled wheels are published for Linux and macOS on Python 3.10 – 3.13. No Rust toolchain is required for this path.
The distribution name on PyPI is
canopus-quantum; the import name remainscanopus:import canopus
From source
git clone https://github.com/Youngcius/canopus.git
cd canopus
pip install .
pip install . runs the maturin build backend in an isolated environment, which:
- Compiles the Rust extension (
canopus.utils._accel) for the active Python version, - Packages the Python sources, and
- Installs the resulting wheel into the current environment.
Prerequisite for source builds: a working Rust toolchain. Install via rustup:
curl --proto '=https' --tlsv1.2 -sSf https://sh.rustup.rs | sh
Usage
More end-to-end examples live under ./examples/:
routing.ipynb— Canopus routing in detailrebasing.ipynb— Optimal ISA rebase (Bgate,√iSWAP, arbitrary)python route_demo.pyto test the routing effect by Sabre and Canopus on a demo circuitpython route_qft.py <n>— Compare Canopus vs Sabre routing on ann-qubit QFTpython rebase_xxx.pyto test the rebase passes for arbitrary ISAs
Package layout
canopus/                            # Python package
├── __init__.py
├── backends.py                     # Backend / ISA / cost-estimator definitions
├── basics.py                       # CanonicalGate, BGate, SQiSWGate
├── mapping.py                      # CanopusMapping & SabreMapping transpiler passes
├── synthesis.py                    # rebase_to_{canonical, sqisw, zzphase, custom, ...}
├── decomposition/                  # Two-qubit decomposition kernels
├── extensions/                     # Optional integrations (bqskit, ...)
└── utils/
    ├── _core.py                    # Pure-Python utilities
    ├── _accel.cpython-*.so         # Rust-compiled accelerator (built by maturin)
    └── _accel.pyi                  # Type stubs for the Rust extension

src/                                # Rust source for the accelerator
└── lib.rs                          # PyO3 bindings
Development
Install the dev extras and build the Rust extension in editable mode:
pip install -e ".[dev]"
poe dev          # equivalent to: maturin develop --release
Common tasks (defined in pyproject.toml):
| Command | Description |
|---|---|
poe dev |
Build & install the Rust extension in editable mode |
poe rebuild |
Clean and rebuild from scratch |
poe build |
Build a redistributable wheel into ./target/wheels/ |
poe clean |
Remove every compiled artifact and cache |
poe lint |
ruff check canopus |
poe fmt |
ruff format canopus |
poe fmt-check |
ruff format --check canopus |
poe typecheck |
mypy canopus |
poe test |
pytest |
poe check |
Aggregate gate that CI runs: lint + fmt-check + test |
See CONTRIBUTING.md for the full contribution workflow.
Evaluation artifact
./experiments/ contains the full evaluation suite that accompanies the paper.
Case studies
./experiments/eval_qft/— QFT kernel./experiments/eval_qldpc/— QLDPC stabilizer circuits
Benchmark suite
Evaluation commands are managed via ./experiments/Makefile. First prepare prerequisite files (coupling files, coverage sets, logical-level optimized circuits):
cd experiments && make
Then:
make canopus— evaluate Canopusmake baselines— evaluate baseline compilers (Sabre, TOQM, BQSKit)make sum_result— summarize results once routing evaluation completesmake disp_result— display summarized routing overheads across compilers, topologies, and ISAs
For fine-grained evaluation, you may also run bench_all.py, bench_all_toqm.py, etc. directly.
Citation
If you use Canopus in your work, please cite:
@article{yang2025unifying,
  title   = {Unifying Qubit Routing Across Diverse Quantum ISAs via Canonical Representation},
  author  = {Yang, Zhaohui and Zhang, Kai and Tian, Xinyang and Ren, Xiangyu and
             Liu, Yingjian and Li, Yunfeng and Ding, Dawei and Chen, Jianxin and Xie, Yuan},
  journal = {arXiv preprint arXiv:2511.04608},
  year    = {2025}
}
License
This project is licensed under the Apache License 2.0 — see the LICENSE file for details.
1 maintainer

Metadata
1 maintainer
Release files for canopus-quantum 0.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| canopus_quantum-0.2.0.tar.gz | 12.9 MB | With provenance | Details |
Built distributions (wheels)
Total release size: 15.0 MB
Release files / canopus_quantum-0.2.0.tar.gz
| Download URL | canopus_quantum-0.2.0.tar.gz |
|---|---|
| Size | 12.9 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
56b5e75e531f473cfe854a88c94bec767ae0dbc8f6d98100d1acd81194ea8fd3
|
|
BLAKE2b-256 checksum How to use checksums |
ef2bb80d8342abbd3b5f1ffe092cc34a3cfc04321577eddb42f22a4623686eeb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 14, 2026.
Transparency logRelease files / canopus_quantum-0.2.0-cp313-cp313-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | canopus_quantum-0.2.0-cp313-cp313-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 280.9 kB |
| Tags | CPython 3.13 Linux glibc 2.17+ x86-64 |
|
SHA-256 checksum How to use checksums |
c096c5c37096c47ce7a5fecc238a0a736cd02bd0789a0cfe5043070c68b9066b
|
|
BLAKE2b-256 checksum How to use checksums |
94b860dd22b5c44dae82bb93bea60954ff1f8d4e734508b155d5e601747badda
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 14, 2026.
Transparency logRelease files / canopus_quantum-0.2.0-cp313-cp313-macosx_11_0_arm64.whl
| Download URL | canopus_quantum-0.2.0-cp313-cp313-macosx_11_0_arm64.whl |
|---|---|
| Size | 250.8 kB |
| Tags | CPython 3.13 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
b7a51e9d14cca80e0f503edaf5ccb9d083edc400f3ed25416de45850d6407320
|
|
BLAKE2b-256 checksum How to use checksums |
a6c8774b882ce9808620370123eefa32073ed35909c092a05a30a2917b0a505a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 14, 2026.
Transparency logRelease files / canopus_quantum-0.2.0-cp312-cp312-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | canopus_quantum-0.2.0-cp312-cp312-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 280.9 kB |
| Tags | CPython 3.12 Linux glibc 2.17+ x86-64 |
|
SHA-256 checksum How to use checksums |
148e64c07a0572b63c59002dc3b305fda7043852563e9314c5915f243f656f1c
|
|
BLAKE2b-256 checksum How to use checksums |
975120b377919fec480aec5dfa2fc53bce01be3bb81052fc3af3d00ab427dbf7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 14, 2026.
Transparency logRelease files / canopus_quantum-0.2.0-cp312-cp312-macosx_11_0_arm64.whl
| Download URL | canopus_quantum-0.2.0-cp312-cp312-macosx_11_0_arm64.whl |
|---|---|
| Size | 250.8 kB |
| Tags | CPython 3.12 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
90958ee51b148141852e13f2da25954afbd3e98937c316af507877f0668f8665
|
|
BLAKE2b-256 checksum How to use checksums |
96bf1193f320871e5ed6e40f805a51f2001f977ff2c8c5556a6a0f60a6168827
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 14, 2026.
Transparency logRelease files / canopus_quantum-0.2.0-cp311-cp311-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | canopus_quantum-0.2.0-cp311-cp311-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 281.0 kB |
| Tags | CPython 3.11 Linux glibc 2.17+ x86-64 |
|
SHA-256 checksum How to use checksums |
67118bbe720dfa79516ffbe7534853f58e11fc820610b7f062f97598aad8bdfb
|
|
BLAKE2b-256 checksum How to use checksums |
65f69cc34e59e1990ffbe27ce4764584a6119a90b2b7b1570fd4f377298ea9f1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 14, 2026.
Transparency logRelease files / canopus_quantum-0.2.0-cp311-cp311-macosx_11_0_arm64.whl
| Download URL | canopus_quantum-0.2.0-cp311-cp311-macosx_11_0_arm64.whl |
|---|---|
| Size | 253.3 kB |
| Tags | CPython 3.11 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
0d8224ce9d1244c7e40ea7440dbcc9fe06c695fd8276d00dc069273728f761be
|
|
BLAKE2b-256 checksum How to use checksums |
559540915164ed44cd340f42b8a18349844aed34a8f9a806899fd928c7e35edb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 14, 2026.
Transparency logRelease files / canopus_quantum-0.2.0-cp310-cp310-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | canopus_quantum-0.2.0-cp310-cp310-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 281.1 kB |
| Tags | CPython 3.10 Linux glibc 2.17+ x86-64 |
|
SHA-256 checksum How to use checksums |
97efcb2cefc23e6a95a7637a6cce34a8a99b40fd747fa9fdd763a6369c1c0025
|
|
BLAKE2b-256 checksum How to use checksums |
048ae7ef2c8dfbfd13eae5f24138301b57ef67801db001f3380ac7c23061c73f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 14, 2026.
Transparency logRelease files / canopus_quantum-0.2.0-cp310-cp310-macosx_11_0_arm64.whl
| Download URL | canopus_quantum-0.2.0-cp310-cp310-macosx_11_0_arm64.whl |
|---|---|
| Size | 253.3 kB |
| Tags | CPython 3.10 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
dd4e2cde4030e4520e160cfadb289041ff41e53255a0bcc050c642c83cdb1fa4
|
|
BLAKE2b-256 checksum How to use checksums |
47ebd37d91cb85e0073980c809351139c0f2a70c0c1dd4bd267111fdc18974f7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 14, 2026.
Transparency logSecurity for canopus-quantum 0.2.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 9 files in this release have been uploaded with provenance metadata.
Attestation for canopus_quantum-0.2.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 14, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














