
cc-session-browser
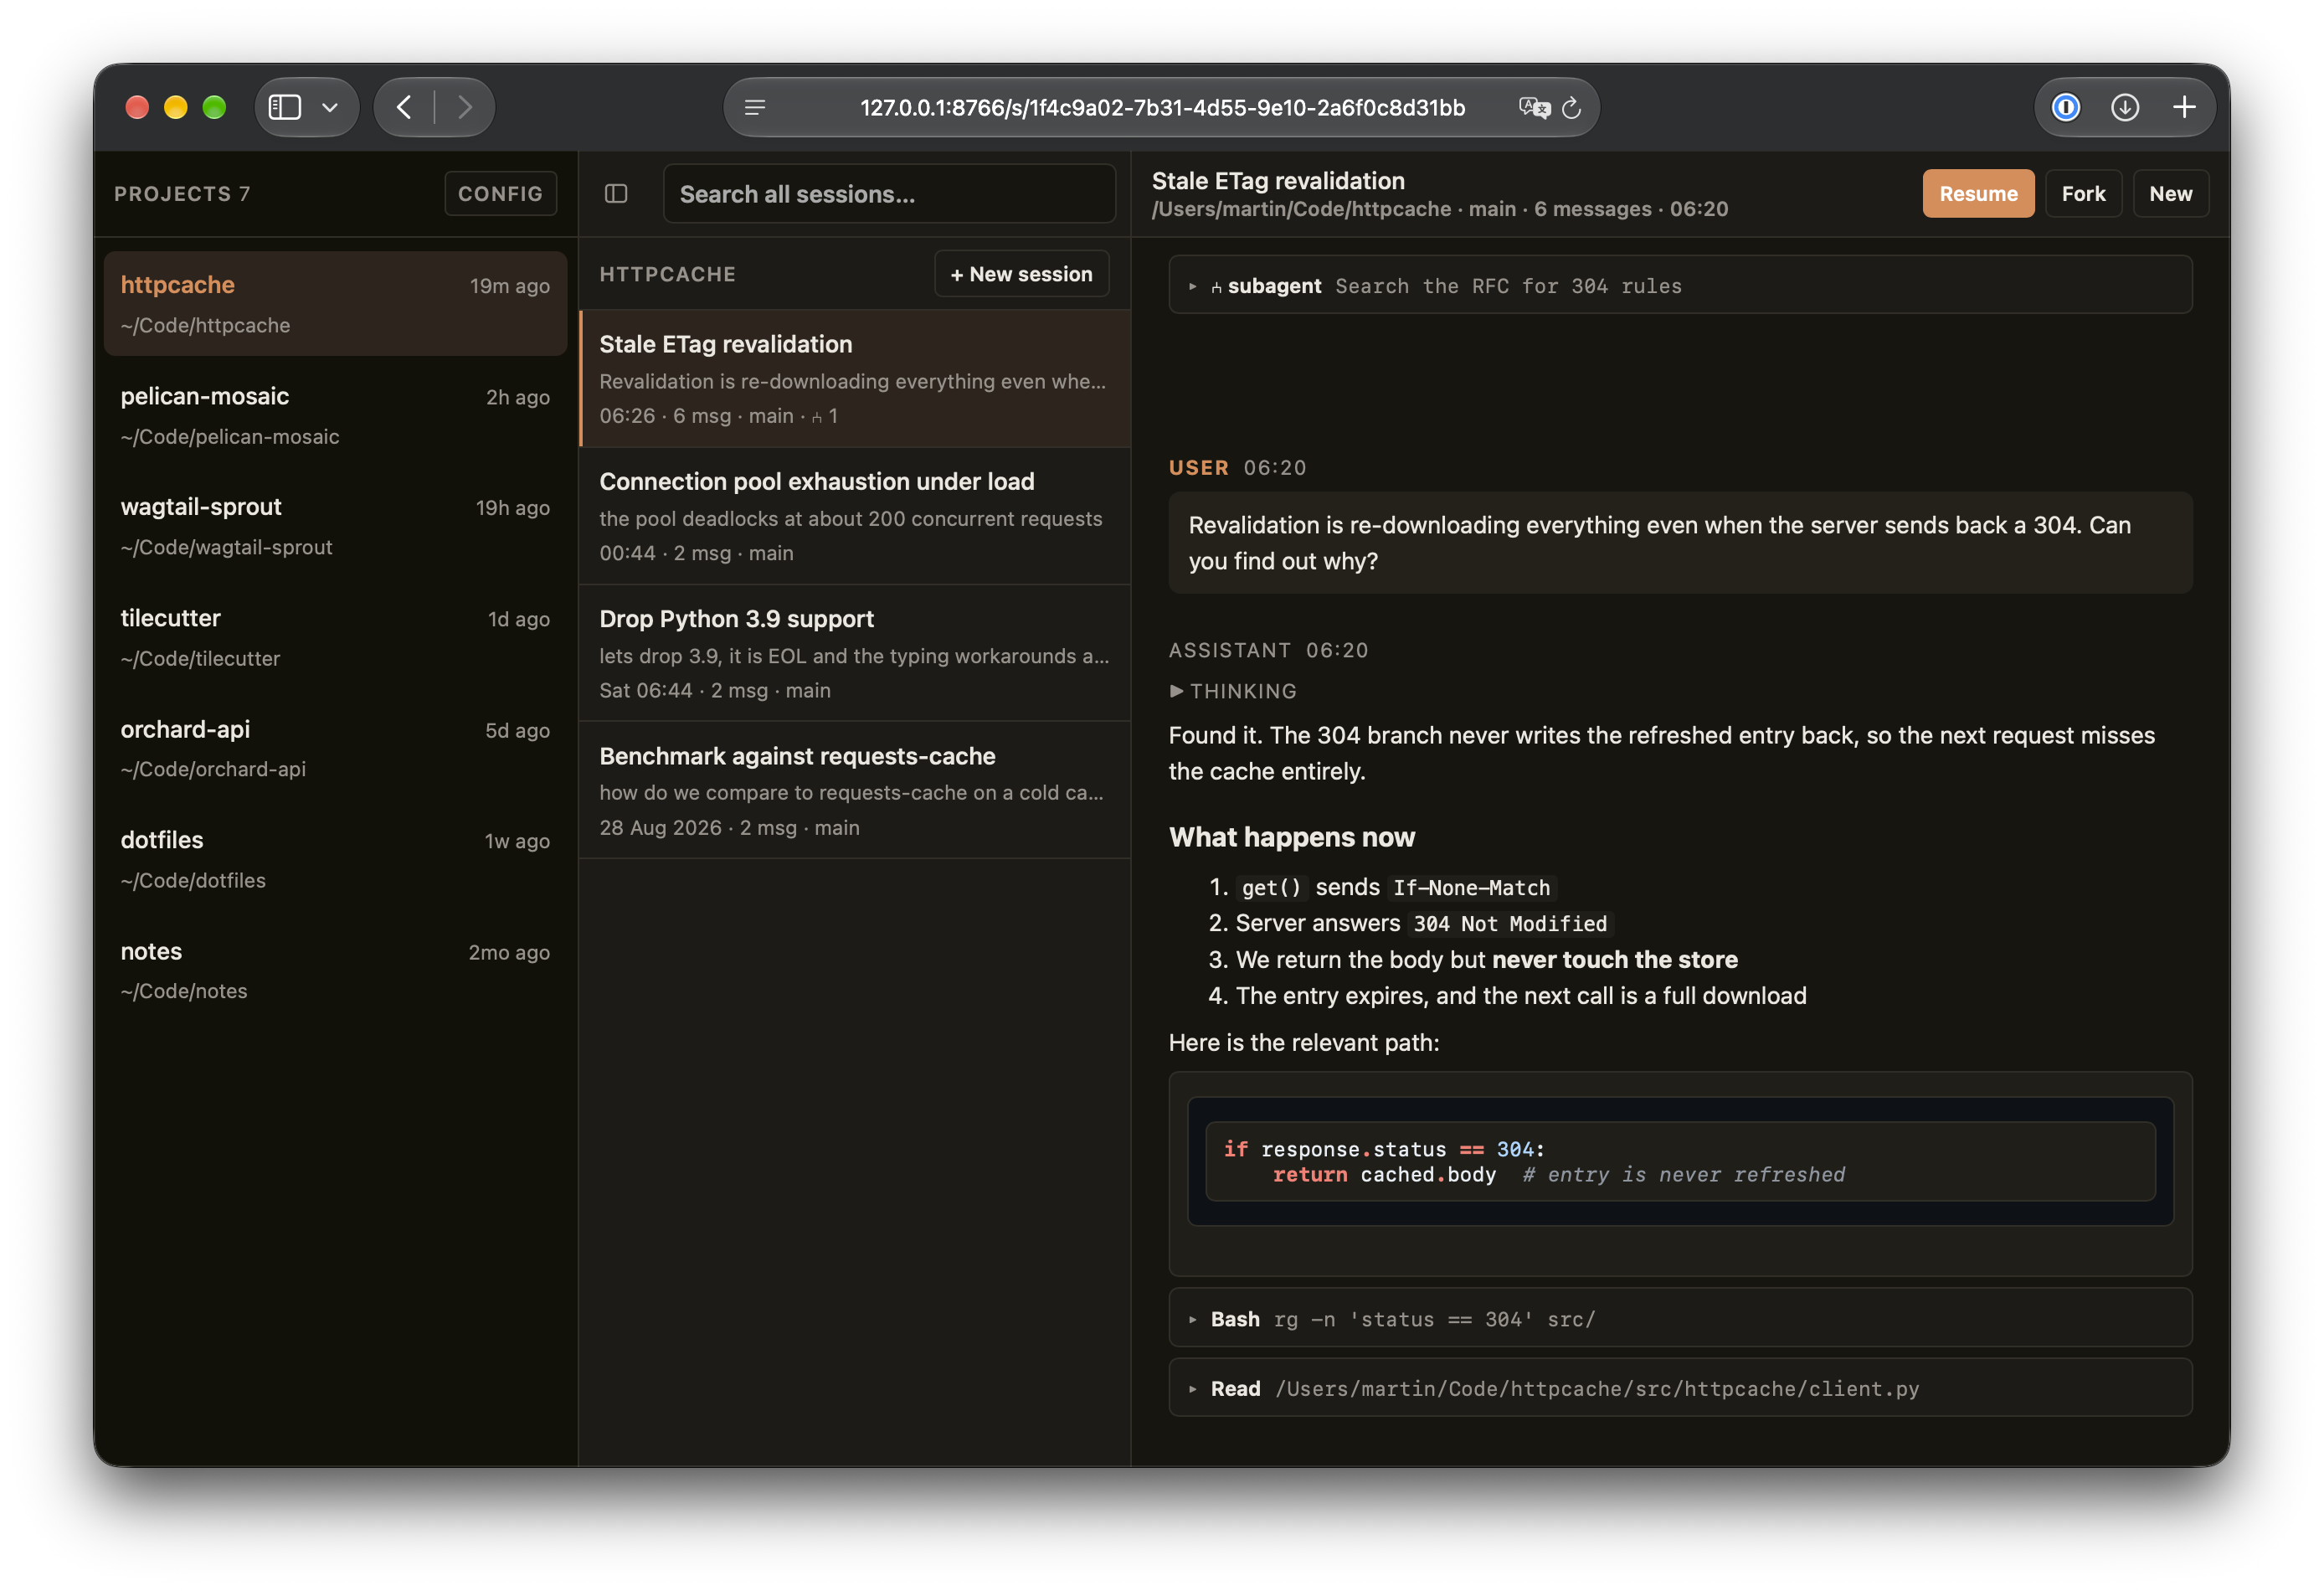
A browser for your Claude Code sessions.
uvx cc-session-browser
No install, no configuration. It indexes ~/.claude/projects and opens a
browser.
Features
- Browse every project and session Claude Code has recorded, with the real project path recovered from the transcripts rather than the dashed directory name.
- Read transcripts with rendered markdown, syntax-highlighted code, expandable tool calls and their output, inline screenshots, and subagent transcripts shown where they were spawned.
- Search across all sessions — titles, prompts, replies and tool invocations — or within a single project.
- Resume, fork, or start a session in your terminal. Forking uses
--fork-session, so the original transcript is never touched.
Nothing is sent anywhere: the tool reads local files and serves them on
127.0.0.1.
Configuration
Optional. Everything has a working default.
cc-session-browser --help-config    # every option, with your paths filled in
cc-session-browser --write-config   # write a commented starter file
The config file is read from the first of these that exists:
--config PATH$CC_SESSION_BROWSER_CONFIG./cc-session-browser.toml~/.config/cc-session-browser/config.toml(%APPDATA%on Windows)
$CLAUDE_CONFIG_DIR is honoured, so a non-standard Claude Code location needs
no configuration at all.
# cc-session-browser configuration


# Where Claude Code keeps its session transcripts. $CLAUDE_CONFIG_DIR is
# honoured automatically, so you rarely need to set this.
#
# projects_dir = "~/.claude/projects"


# Projects to leave out of the sidebar. Each entry is a glob, matched against
# the project name, its full path, and its Claude Code slug -- so you never
# have to know what a slug looks like.
#
# hide = [
#     "scratch",
#     "*/Workspace/throwaway-*",
# ]


[server]

# Bind address. Leave this on loopback: the endpoint that opens a terminal
# starts processes on your machine.
#
# host = "127.0.0.1"

# Port to serve on.
#
# port = 8765

# Open a browser window on startup.
#
# open_browser = true


[launch]

# Open a session in a new "window" or a new "tab".
# Tabs are supported for: gnome-terminal, iterm, kitty, konsole, wezterm, wt
# (kitty needs allow_remote_control). Every other terminal falls back to a
# window.
#
# mode = "window"

# Which terminal to use. Auto-detected from $TERM_PROGRAM when unset.
# Known terminals: ghostty, gnome-terminal, iterm, kitty, konsole, terminal, wezterm, wt
#
# terminal = "iterm"

# Full override, for a terminal that is not in that list. {script} is a
# generated shell script that cds into the project and runs claude; {cwd} is
# the project directory.
#
# terminal_argv = ["alacritty", "--working-directory", "{cwd}", "-e", "{script}"]

# Path to the claude CLI. Found on PATH when unset.
#
# claude_bin = "/usr/local/bin/claude"
Requirements
Python 3.11+. Terminal integration supports iTerm, Terminal.app, Ghostty,
kitty, WezTerm, GNOME Terminal, Konsole and Windows Terminal; anything else can
be driven with a terminal_argv template.
1 maintainer

Metadata
1 maintainer
Release files for cc-session-browser 0.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| cc_session_browser-0.1.0.tar.gz | 47.2 kB | With provenance | Details for cc_session_browser-0.1.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| cc_session_browser-0.1.0-py3-none-any.whl | Python 3 | none | any | Details for cc_session_browser-0.1.0-py3-none-any.whl |
Total release size: 101.1 kB
Release files / cc_session_browser-0.1.0.tar.gz
| Download URL | cc_session_browser-0.1.0.tar.gz |
|---|---|
| Size | 47.2 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
86b6563add83a8ece7bbb0a5bda67b8a1a85ecfb18e62854bc4fd9525c7c9772
|
|
BLAKE2b-256 checksum How to use checksums |
cbc49234cbaba316552170843ac04246ad1d9f21491149913492fbdfbc833833
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logRelease files / cc_session_browser-0.1.0-py3-none-any.whl
| Download URL | cc_session_browser-0.1.0-py3-none-any.whl |
|---|---|
| Size | 53.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
48e9c473c9adeab493d1785c87d828e4a83768b7c0250518fc740d70d11ee0a3
|
|
BLAKE2b-256 checksum How to use checksums |
acf6638a3f07dd0813f7bcac736fc65a6bedfee982bd1d51d80b8b4e12777d5f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logSecurity for cc-session-browser 0.1.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for cc_session_browser-0.1.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













