
CDK Docker Image Deployment
This module allows you to copy docker image assets to a repository you control. This can be necessary if you want to build a Docker image in one CDK app and consume it in a different app or outside the CDK, or if you want to apply a lifecycle policy to all images of a part of your application.
Getting Started
Below is a basic example for how to use the DockerImageDeployment API:
import * as ecr from 'aws-cdk-lib/aws-ecr';
import * as imagedeploy from 'cdk-docker-image-deployment';

const repo = ecr.Repository.fromRepositoryName(this, 'MyRepository', 'myrepository');

new imagedeploy.DockerImageDeployment(this, 'ExampleImageDeploymentWithTag', {
  source: imagedeploy.Source.directory('path/to/directory'),
  destination: imagedeploy.Destination.ecr(repo, {
    tag: 'myspecialtag',
  }),
});
Currently Supported Sources
Source.directory(): Supply a path to a local docker image as source.
Don't see a source listed? See if there is an open issue or PR already. If not, please open an issue asking for it or better yet, submit a contribution!
Currently Supported Destinations
Destination.ecr(repo, options): Send your docker image to an ECR repository in your stack's account.
Don't see a destination listed? See if there is an open issue or PR already. If not, please open an issue asking for it or better yet, submit a contribution!
Under the Hood
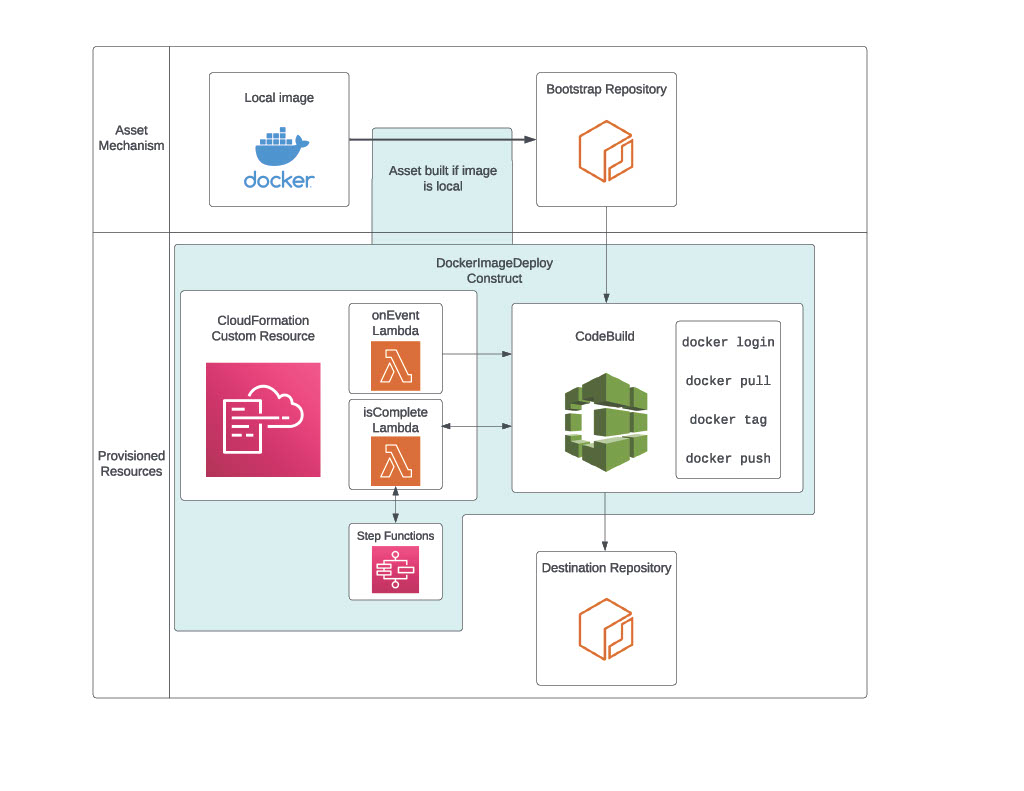
- When this stack is deployed (either via cdk deploy or via CI/CD), the contents of the local Docker image will be archived and uploaded to an intermediary assets ECR Repository using the cdk-assets mechanism.
- The
DockerImageDeploymentconstruct synthesizes a CodeBuild Project which uses docker to pull the image from the intermediary repository, tag the image if a tag is provided, and push the image to the destination repository. - The deployment will wait until the CodeBuild Project completes successfully before finishing.
The architecture of this construct can be seen here:
Security
See CONTRIBUTING for more information.
License
This project is licensed under the Apache-2.0 License.
1 maintainer

Metadata
1 maintainer
Release files for cdk-docker-image-deployment 0.0.1032
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| cdk_docker_image_deployment-0.0.1032.tar.gz | 13.1 MB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| cdk_docker_image_deployment-0.0.1032-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 26.2 MB
Release files / cdk_docker_image_deployment-0.0.1032.tar.gz
| Download URL | cdk_docker_image_deployment-0.0.1032.tar.gz |
|---|---|
| Size | 13.1 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
53a71e4c2d458bc7c0138702eed5ba5aba68435dff99d76cc8b7eb7ddbac6004
|
|
BLAKE2b-256 checksum How to use checksums |
2feafec687411662186c1a81fb7e311c142828911fe25ec6707cf279ca1d94a0
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.14.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 7, 2026.
Transparency logRelease files / cdk_docker_image_deployment-0.0.1032-py3-none-any.whl
| Download URL | cdk_docker_image_deployment-0.0.1032-py3-none-any.whl |
|---|---|
| Size | 13.1 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
41c4fa3fd5c3661f91ba8fbd0a1a1a78e8dd939b303e3ade0caf9f9dd32667b2
|
|
BLAKE2b-256 checksum How to use checksums |
f13cd6ba3bf95ec755d163b94e3d58544a14f82a7b4c9b518076796afb8a1576
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.14.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 7, 2026.
Transparency log













