
CertLord
TLS certificate lifecycle automation.
Version: 1.3.0. See the release notes.
The optional AWS/CloudFront renewal job is experimental and disabled by default. It requires separate SDK installation and job configuration. Verification so far covers a controlled provider. Live AWS permissions and edge propagation still require qualification.
CertLord automates TLS certificate issuance, renewal and deployment. It supports ACME through Certbot and importing existing PEM certificates, stores certificates in Vault and deploys them through Auton. Optional destination TLS verification checks the certificate actually served before acknowledgement. StatusCake/Updown adapters are optional; expiry observations are exposed for an external supervision system. Independent TLS checks also observe configured endpoints without issuing or deploying certificates. They expose the actual served fingerprint, failures and freshness through the API, CLI/TUI and metrics. It uses DWho, HTTPdis and Sonicprobe.
Redis stores temporary ACME HTTP-01 challenge responses and tracks pending work, retries and deployment leases. Vault stores certificate material. Use the Docker Compose installation to run the services together, or provision them separately for the Debian installation.
Docker installation
Use the Compose guide for initialization, persistent
Vault storage, API access and deployment configuration. The application image is
decryptus/certlord:1.3.0.
Command line and terminal interface
Use ordinary commands in scripts, or explicitly open the read-only terminal browser
with certlord tui. View the illustrated guide.
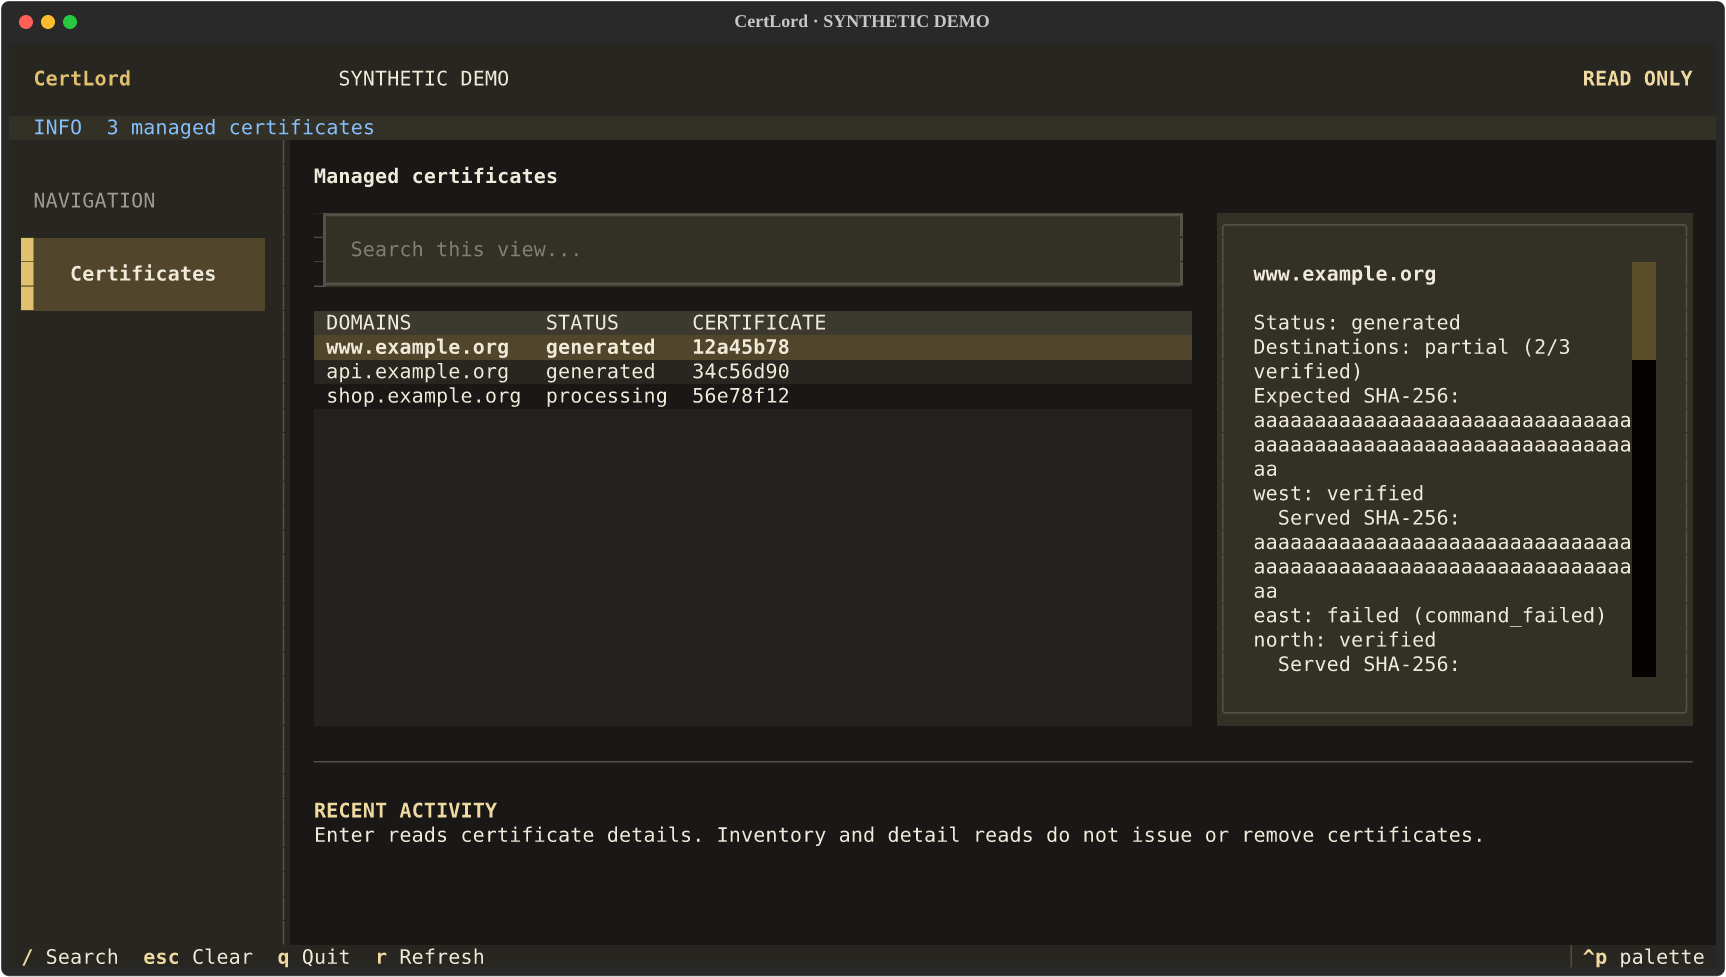
Real client capture with synthetic demonstration data; this is not deployment evidence.
Names and installation
- Python distribution and package:
certlord - Command and system service:
certlord - Default configuration:
/etc/certlord/certlord.yml - Service user and group:
certlord
Requires Python 3.11+ on POSIX; CI validates Python 3.11 and 3.12.
Newer interpreters are not yet validated. Install the Python package with python -m pip install ..
System configuration and external services must also be provisioned. The
Debian 12 package includes an isolated Python environment and the service account;
follow the installation guide before enabling the service.
Repository: https://github.com/decryptus/certlord.
Validate configuration, recovery and credentials in an isolated environment before deploying your service.
See MIGRATION.md before updating an existing installation.
Project documentation
- CLI and TUI screenshots
- Evaluate your installation
- Certificate UUIDs, HTTP API, CLI and TUI
- ACME HTTP Connector integration
- Debian 12 installation and isolated dependencies
- External certificate import and replacement
- Independent TLS endpoints: web, proxy, load balancer and CDN
- Operations and recovery
- Operation correlation and optional Auton receipts
- Coding conventions and contributions
Guide: Certificate observations and supervision.
Post-deployment TLS verification checks configured destinations before acknowledgement.
Named deployment destinations track each server's certificate fingerprint and result, retain partial success through restart, and support explicit retries of one failed destination.
Operations and recovery: health, queues, retries and first-version limits.
See configuration validation for YAML schema coverage and compatibility.
Documentation
- Users: installation, configuration, operation and API usage in this README and the user guide.
- Contributors: architecture, tests and development.
Textual terminal interface
See the Textual guide for installation, navigation and operation confirmations.
1 maintainer

Metadata
1 maintainer
Release files for certlord 1.3.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| certlord-1.3.0.tar.gz | 1.7 MB | With provenance | Details for certlord-1.3.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| certlord-1.3.0-py3-none-any.whl | Python 3 | none | any | Details for certlord-1.3.0-py3-none-any.whl |
Total release size: 1.8 MB
Release files / certlord-1.3.0.tar.gz
| Download URL | certlord-1.3.0.tar.gz |
|---|---|
| Size | 1.7 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
3a28a0b8d4f2af767eeb025da2ea8bd3f49d475df1faedde05ab28ace4661413
|
|
BLAKE2b-256 checksum How to use checksums |
0ab5763cae5552e246e79b2e859dc54c86e77a76785914e1bf79f952e969cf49
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 4, 2026.
Transparency logRelease files / certlord-1.3.0-py3-none-any.whl
| Download URL | certlord-1.3.0-py3-none-any.whl |
|---|---|
| Size | 108.6 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
15e1b6e3e93ca9f7ea29069a9311edbe964d209e3ec5a3189bfadee709f1e08d
|
|
BLAKE2b-256 checksum How to use checksums |
5b2bd45ba072f17094035163a64dc4ced19c2b426e3067b45438829a8ddbdd3b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 4, 2026.
Transparency logSecurity for certlord 1.3.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for certlord-1.3.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 4, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














