
CodePact
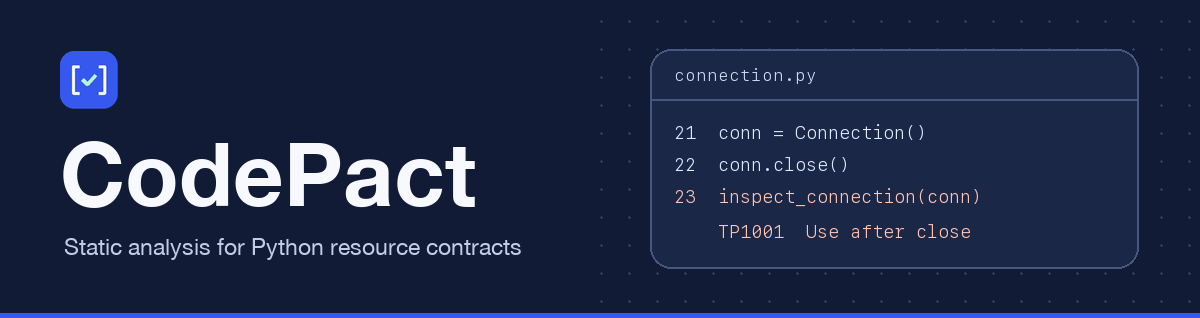
CodePact finds Python resource bugs before runtime. Declare how an object closes and which functions own or borrow it. CodePact reads source and can flag a connection used after close, cleanup skipped on a supported exit, or a discarded must-use result. Run it alongside your type checker and tests.


Documentation · Install options · Rule catalog · Roadmap
New in 0.9.0. Track persistent outcome duties with MustHandle, require
declarations on selected APIs, and compare code changes or two published
wheels. Reviewed HTTP and SQL profiles add bounded client and session checks,
and work models track when a task or future result remains unobserved.
Release notes ·
Review a change ·
Reviewed provider profiles
Quick start
In an empty directory with uv and Python 3.11 or later, start a project.
uv init --bare --name codepact-demo
uv add 'codepact[cli]==0.9.0'
uv run --locked codepact --version
mkdir src
Expect codepact 0.9.0.
Save the complete connection example
as src/connection.py and run the check.
uv run --locked codepact check --root src
Expect exit 1 with a related location pointing to the close.
connection.py:23:1: error TP1001: Borrowed call requires an open resource
  related: connection.py:22:1
Delete the final line and rerun with --mode strict to confirm exit 0.
Full walkthrough ·
Install with pip or run the standalone command
What you can check
| Declare | CodePact checks |
|---|---|
@resource(closed_by="close") |
Supported use after close and conflicting lifecycle metadata |
Owned[T] |
Cleanup duties across modeled exits and open resources at ownership handoff |
Borrowed[T] |
Closing a resource through a shared view |
@must_use or MustUse[T] |
Bare discarded calls to marked synchronous functions |
MustHandle[Result[T, E]] or MustHandle[Option[T]] |
Unacknowledged outcomes across supported assignments, aliases, and returns |
The helpers use typing.Annotated, so ordinary types remain available to mypy
and Pyright. The checker follows supported branches, aliases, calls, exceptions,
and cleanup paths. Check reports include primary and related source locations,
certainty, and coverage. Contract syntax ·
Supported syntax
Try experimental ownership
Add the following to pyproject.toml to enable move and lexical borrow checks.
[tool.codepact]
config-version = 1
experimental-ownership = true
Use move(value) to transfer a tracked handle and its cleanup duty. The
checker reports later use of the old handle. The TaskGroup model requires a
separate default-task-factory assumption.
Ownership examples and scope
The new runtime models require an explicit profile for CPython 3.13.16 on Linux x86-64. The profile describes the program you analyze. You can run the checker on any supported CLI platform. Configure a runtime profile
Run in CI
Start with a narrow source root. Use strict mode when incomplete coverage should fail the job, and retain the JSON report alongside the exit status.
uv run --locked codepact check --root src --mode strict --json > codepact-report.json
| Exit | Meaning |
|---|---|
0 |
The completed report passed the selected policy |
1 |
The completed report failed policy |
2 |
The invocation or check failed |
Advisory mode can pass with incomplete coverage. The coverage field describes which parts of the program the checker could analyze. Teams can configure rule severity, review a baseline, and record line-level exceptions with a reason. Checks with installed dependency roots or a runtime profile emit report schema 4 with provider selection and model applicability details. Adoption guide · CI workflow
Compatibility
The helper package runs on Python 3.11 and later, with CI on CPython 3.11–3.14. The analyzer supports Python 3.11–3.13 source targets. Native CLI wheels are available for Linux, macOS, and Windows on x86-64 and ARM64. Building from source requires Rust 1.96 or later and a linker. Platform matrix · Standalone CLI and Rust library
Contribute
Run uv sync --locked --extra cli and uv run --locked make check after installing the
repository's pinned Cargo audit tools. The contributor guide lists the setup
and focused check targets.
Contributing ·
Build the docs ·
MIT license
1 maintainer

Metadata
1 maintainer
Release files for codepact 0.9.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| codepact-0.9.0.tar.gz | 7.4 kB | Without provenance | Details for codepact-0.9.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| codepact-0.9.0-py3-none-any.whl | Python 3 | none | any | Details for codepact-0.9.0-py3-none-any.whl |
Total release size: 16.1 kB
Release files / codepact-0.9.0.tar.gz
| Download URL | codepact-0.9.0.tar.gz |
|---|---|
| Size | 7.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
adbfc72bcc3268e49bd9b0e4cd01b591957fd46cf5b48c86def3ffbb946cf554
|
|
BLAKE2b-256 checksum How to use checksums |
567cedf4bc3b5c7d38257df90e6c655024629a90c62ebbcabeb9fa92d2b4ebcb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Release files / codepact-0.9.0-py3-none-any.whl
| Download URL | codepact-0.9.0-py3-none-any.whl |
|---|---|
| Size | 8.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
2715ef8c521bbd46c8fcaf872fe1edf837b03ffa9981eb073dedb06a04725457
|
|
BLAKE2b-256 checksum How to use checksums |
2529464b2abb2658f2c5f6402d99ff48d12950b0e803448fcc17dac9dd8c51c2
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Security for codepact 0.9.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














