
This is an helper package that setup a RedTurtle’s Plone site ready to work with Volto.




Introduction
This product allows you to set a max siza validation for file and image fields in content-types.
How to use it
Just add the product to the buildout and install it in the site you want to use.
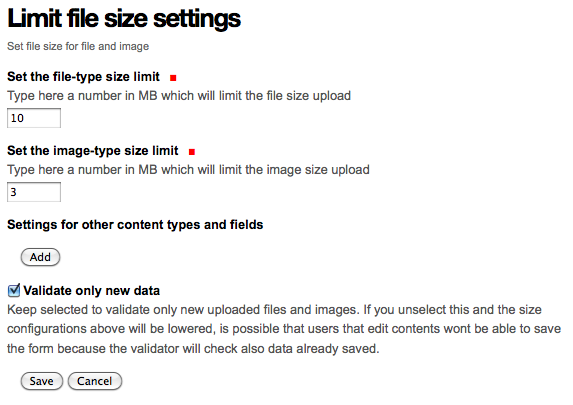
A new “Limit file size settings” option will be added in the control panel, where you can change the File and Image attachments.
No users will be able to upload files that exceed the limit. Also in TinyMCE text editor.
Validator bypass
If some users need to bypass the validation and upload some larger files, there is a new permission “collective.limitfilesizepanel: Bypass limit size” that allows to do this.
You only need to set this permission to some roles, and they’ll have no upload limits.
Compatibility
This products runs on Python 3.11+ and has been tested on:
Plone 6.0
Plone 6.1
Plone 6.2
For Plone 5.2, please refer to 3.0.x releases. For older versions, please refer to 2.x branch/tags
Credits
Developed with the support of:
All of them supports the PloneGov initiative.
Authors
This product was developed by RedTurtle Technology team.

Changelog
3.1.0 (2026-10-22)
Added @limit-sizes service and limit-sizes expander to expose file and image size limits (in MB), the new_data_only setting and the bypass permission of the current user. Run upgrade step to 1400 to set the new permission’s roles. [daniele]
Removed “Settings for other content types and fields” (types_settings) setting and collective.z3cform.jsonwidget dependency: limits are now only the global ones for files and images. Upgrade step to 1400 removes the old registry record and uninstalls collective.z3cform.jsonwidget (if installed and not required by other products). collective.z3cform.jsonwidget is still in install_requires only to allow its uninstall: it will be removed in the next release. [cekk]
Use native (PEP 420) namespace for collective. [cekk]
Expose the control panel on plone.restapi (@controlpanels/limitfilesize-settings), so it can be managed from Volto. [cekk]
“Validate only new data” is no more required, so it can be unchecked. [cekk]
Support Plone 6.0, 6.1 and 6.2 on Python 3.11+ and drop Plone 5.2 support. Configure the package with plone.meta (tox and GitHub Actions) and remove the old buildout-based test setup. [cekk]
3.0.3 (2023-09-27)
Fix check in validators if product is not installed. [cekk]
3.0.2 (2023-05-02)
Raise custom ValidationError to have a 400 on restapi calls. [cekk]
3.0.1 (2023-05-02)
Raise ValueError instead Invalid for restapi calls. [cekk]
3.0.0 (2023-04-27)
Python3 support. [cekk]
Drop usage of persistent fields in registry. Now we use collective.z3cform.jsonwidget. [cekk]
Change validator to work also with restapi calls. [cekk]
2.1.2 (2018-07-17)
Fix release [cekk]
2.1.1 (2018-07-17)
Fix permission for upload view [eikichi18]
2.1.0 (2018-05-09)
Fix validators for Dexterity fields. Now works well with Files and images [cekk]
Add support for Tinymce validation also for Plone 5 [cekk]
2.0.3 (2018-01-30)
Don’t break validation for view with no specific context. [bsuttor]
2.0.2 (2017-09-15)
Fix brown bag release [cekk]
2.0.1 (2017-09-14)
Don’t break validation if the product isn’t installed. If not installed, shouldn’t do nothing. [cekk]
Fix patched__call__ if the product isn’t installed. [arsenico13]
2.0.0 (2017-05-04)
Version 1.3 don’t uninstall cleanly [keul]
Now validates also files and images created in TinyMCE [cekk]
Dexterity support [cekk]
1.3 (2015-07-06)
Added type+field configuration [keul]
Pyflakes cleanup [keul]
1.2 (2013-08-19)
Add German translations. [jone]
Ensure consistency of megabyte symbols to be MB. [davidjb]
1.1.2 (2013-03-26)
run rolemap configurations when upgrading from older versions [keul]
1.1.1 (2013-03-26)
fixed pypi classifiers [keul]
1.1 (2013-03-26)
Added a proper uninstall step [keul]
Now based on collective.monkeypatcher [keul]
i18n refactoring [keul]
Do not try to automatically validate file size for already existings attachments.
This provent to get validation error when editing file after size limit has been changed [keul]
Added new permission “collective.limitfilesizepanel: Manage limit file size settings”. Users with this permission can bypass size validation [cekk]
1.0 (Unreleased)
Initial release


Release files for collective.limitfilesizepanel 3.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| collective_limitfilesizepanel-3.1.0.tar.gz | 87.1 kB | Without provenance | Details for collective_limitfilesizepanel-3.1.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| collective_limitfilesizepanel-3.1.0-py3-none-any.whl | Python 3 | none | any | Details for collective_limitfilesizepanel-3.1.0-py3-none-any.whl |
Total release size: 124.3 kB
Release files / collective_limitfilesizepanel-3.1.0.tar.gz
| Download URL | collective_limitfilesizepanel-3.1.0.tar.gz |
|---|---|
| Size | 87.1 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
c6cc50aa20d515866fc04ac462ad5ecacc4309e9e046f38d3da89ec87375b27e
|
|
BLAKE2b-256 checksum How to use checksums |
07a770270745c22cddc59f442bd16386940097e7eeb7b300f24659137c0c339c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/6.2.0 CPython/3.11.11
|
Release files / collective_limitfilesizepanel-3.1.0-py3-none-any.whl
| Download URL | collective_limitfilesizepanel-3.1.0-py3-none-any.whl |
|---|---|
| Size | 37.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
11f457d3d3bb59444baafb0b6d4a50101a5e3783c07475e2acc93294961e174c
|
|
BLAKE2b-256 checksum How to use checksums |
572c39118ebae478937ea8d09d44d9abd17dc096c86dd92ec6c0ecfd4499049d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/6.2.0 CPython/3.11.11
|
Security for collective.limitfilesizepanel 3.1.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














