
Comfy-Pack: Making ComfyUI Workflows Shareable
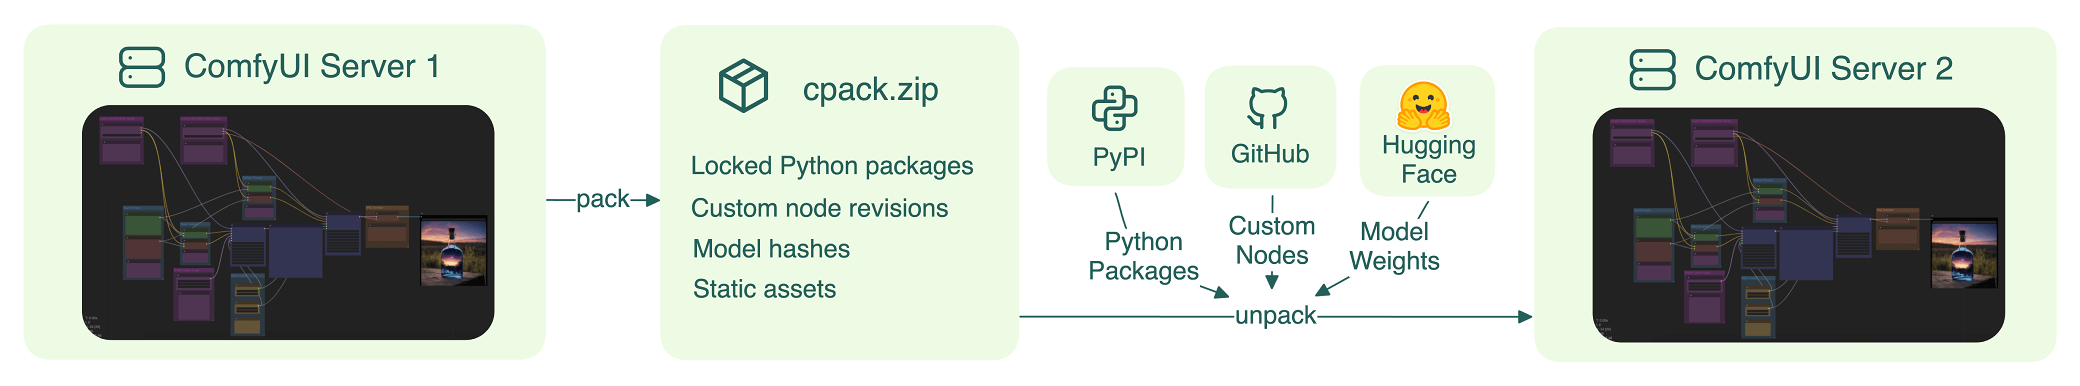
comfy-pack is a comprehensive toolkit for reliably packing and unpacking environments for ComfyUI workflows.
- 📦 Pack workflow environments as artifacts: Saves the workflow environment in a
.cpack.zipartifact with Python package versions, ComfyUI and custom node revisions, and model hashes. - ✨ Unpack artifacts to recreate workflow environments: Unpacks the
.cpack.zipartifact to recreate the same environment with the exact Python package versions, ComfyUI and custom node revisions, and model weights. - 🚀 Deploy workflows as APIs: Deploys the workflow as a RESTful API with customizable input and output parameters.
Motivations
ComfyUI Manager is great for find missing custom nodes. But when sharing ComfyUI workflows to others(your audience or team members), you've still likely heard these responses:
- "Custom Node not found"
- "Cannot find the correct model file"
- "Missing Python dependencies"
These are fundamental challenges in workflow sharing – every component should match exactly: custom nodes, model files, and Python dependencies. Modern pacakge managers like npm and poetry introduced "lock" feature, which means record the exact version for every requirement. ComfyUI Manager isn't designed for that.
We learned it from our community and developed comfy-pack to address these problems. With a single click, it captures and locks your entire workflow environment into a .cpack.zip file, including Python packages, custom nodes, model hashes, and required assets.
Users can recreate the exact environment with one command:
comfy-pack unpack workflow.cpack.zip
This means you can focus on your creative work while comfy-pack handles the rest.
Usages
Installation
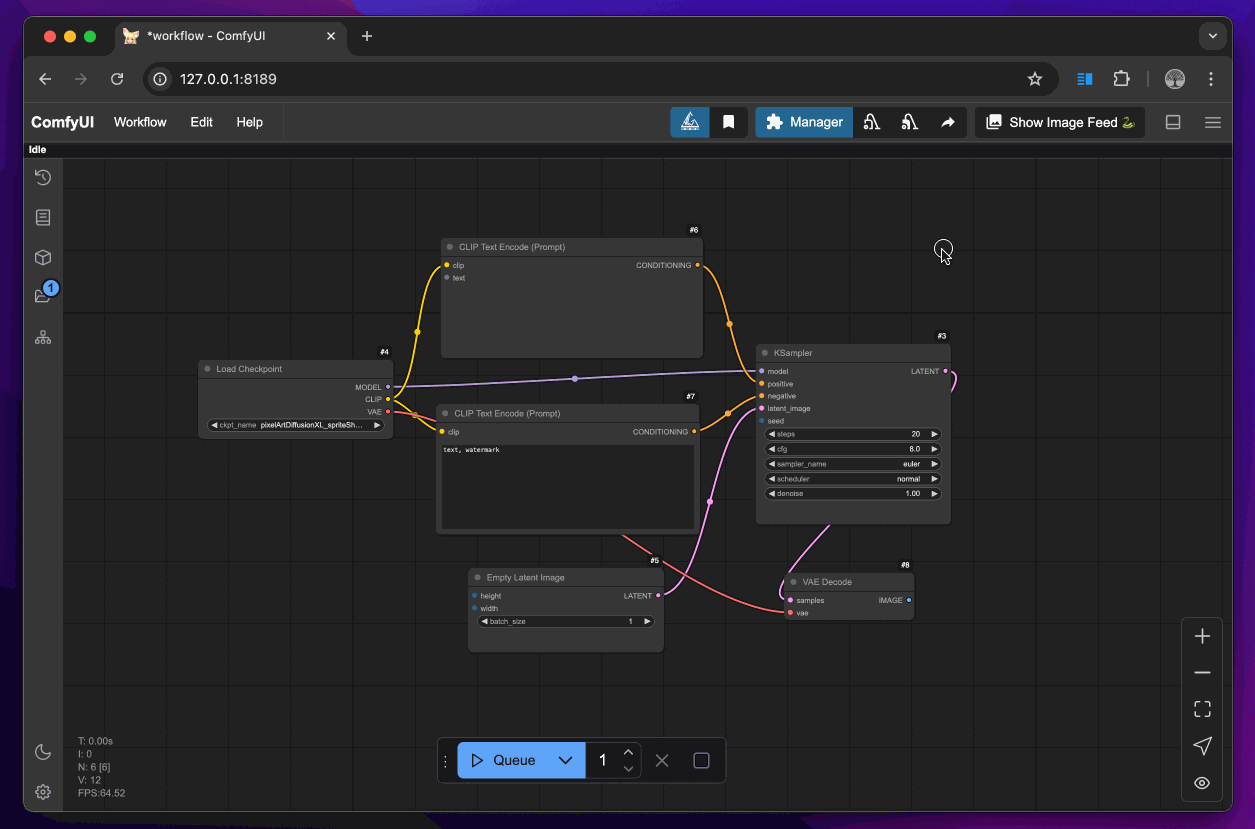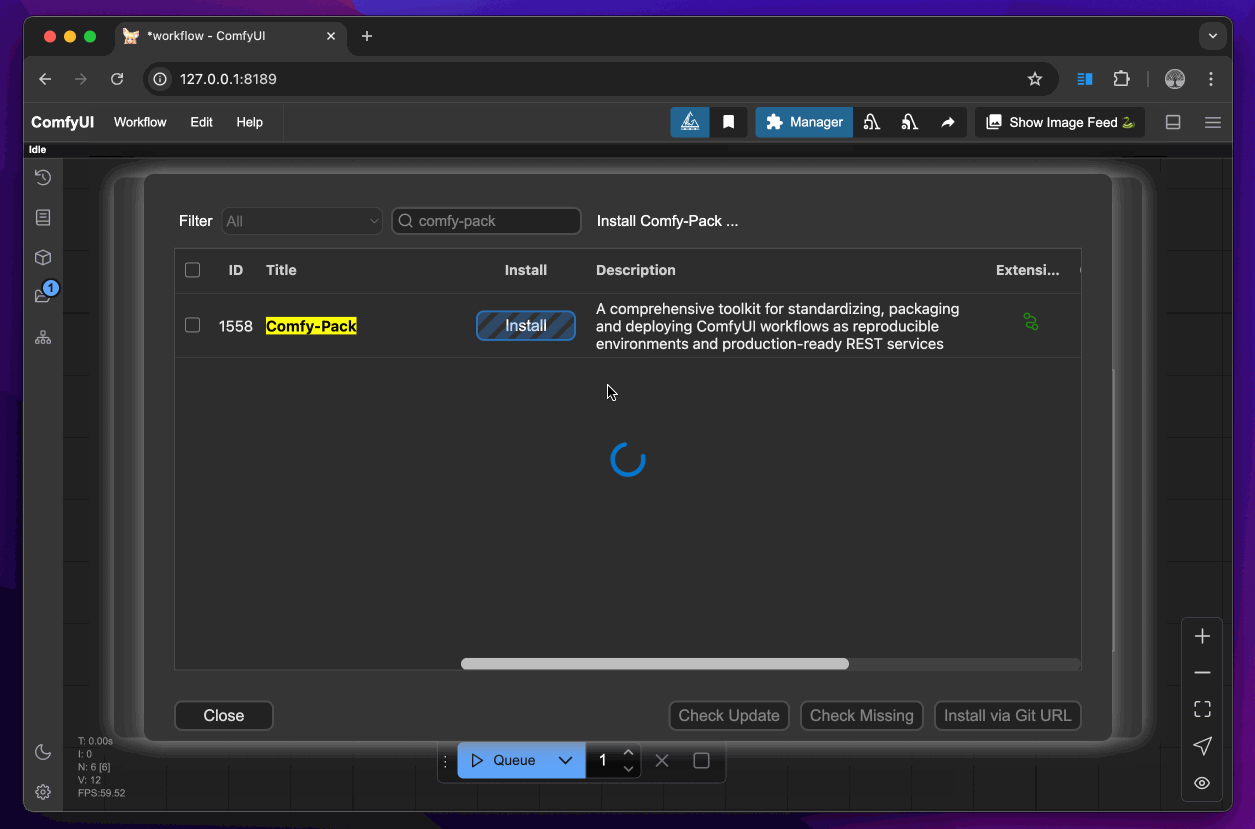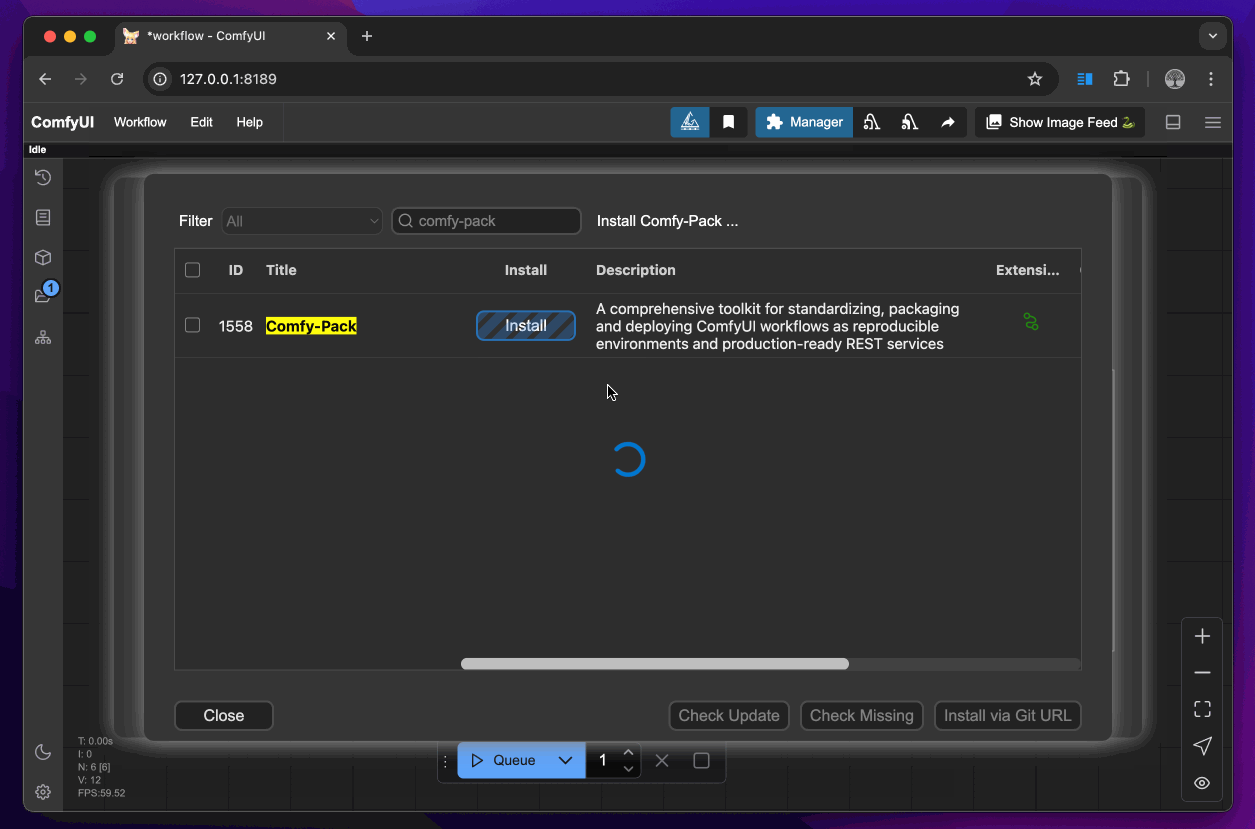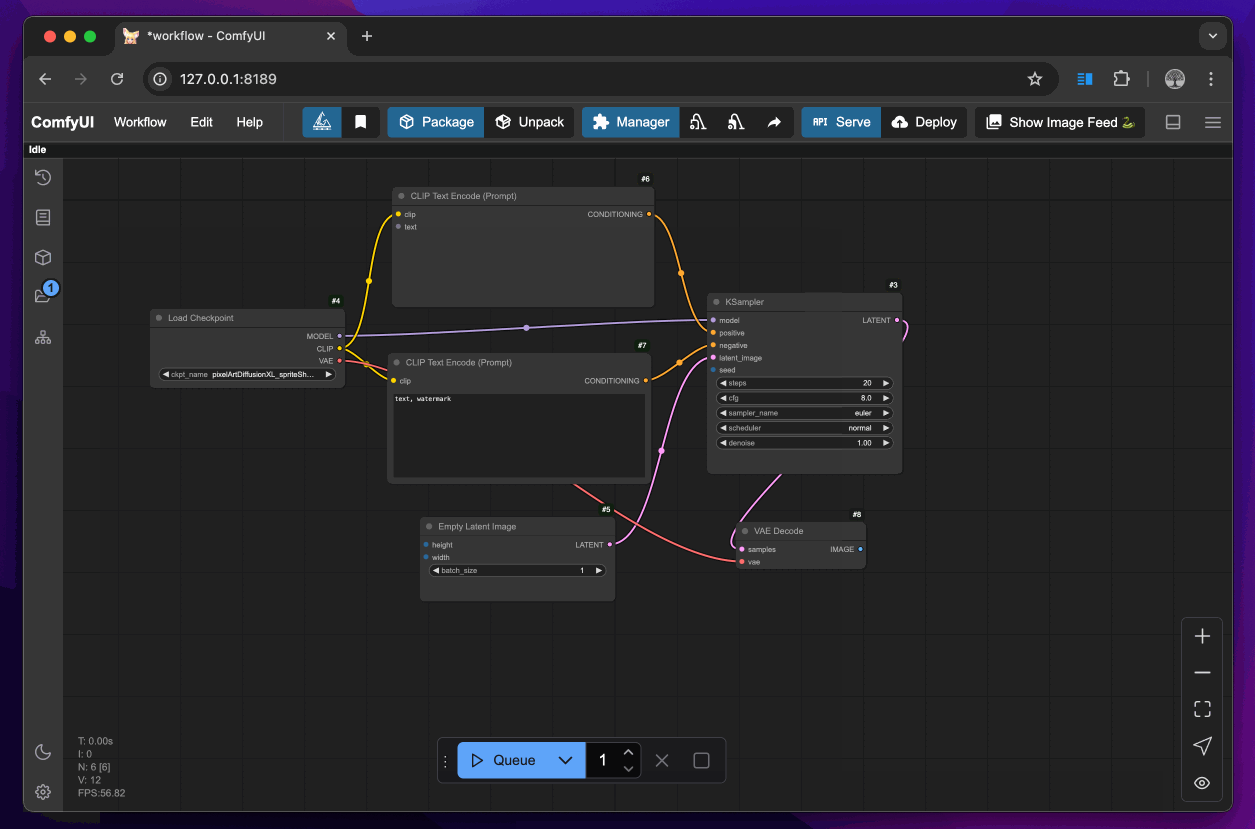
We recommend you use ComfyUI Manager to install comfy-pack. Simply search for comfy-pack and click Install. Restart the server and refresh your ComfyUI interface to apply changes.
Alternatively, clone the project repository through git.
cd ComfyUI/custom_nodes
git clone https://github.com/bentoml/comfy-pack.git
To install the comfy-pack CLI, run:
pip install comfy-pack
Pack a ComfyUI workflow and its environment
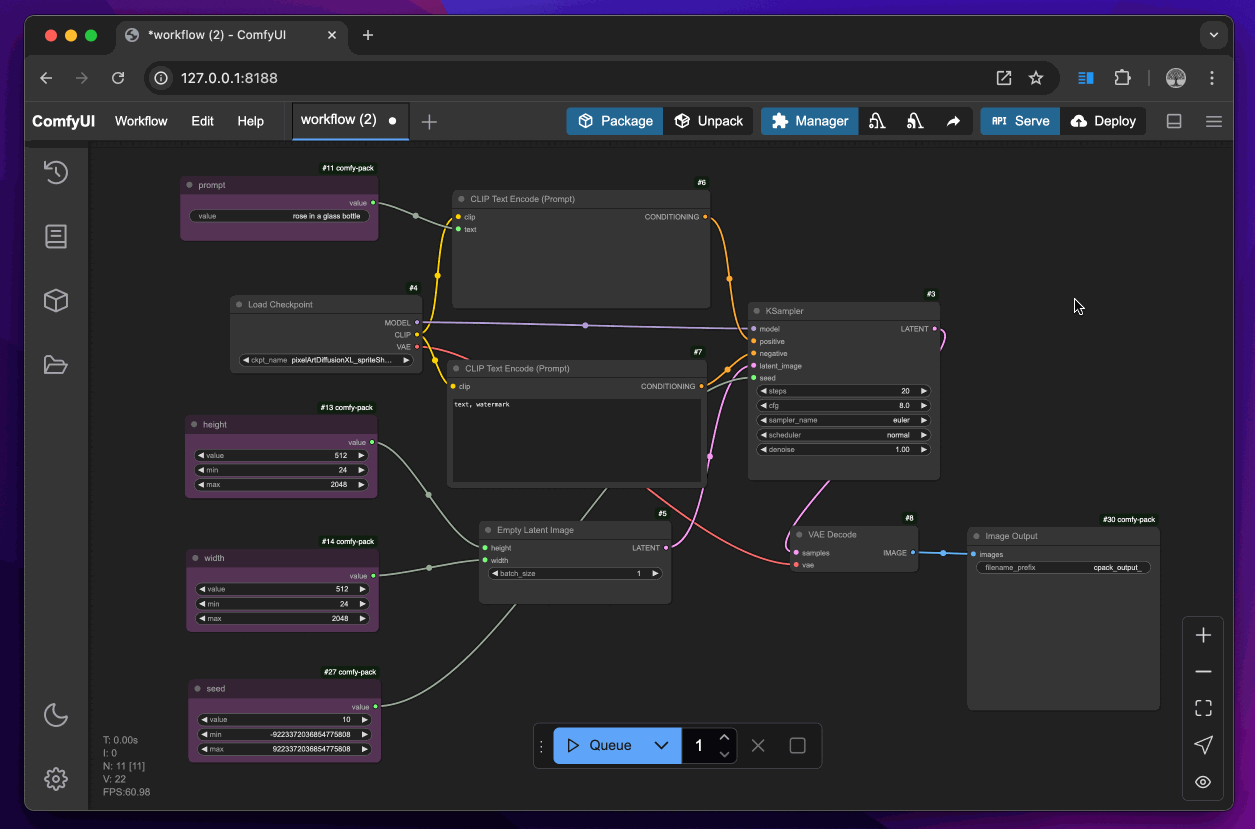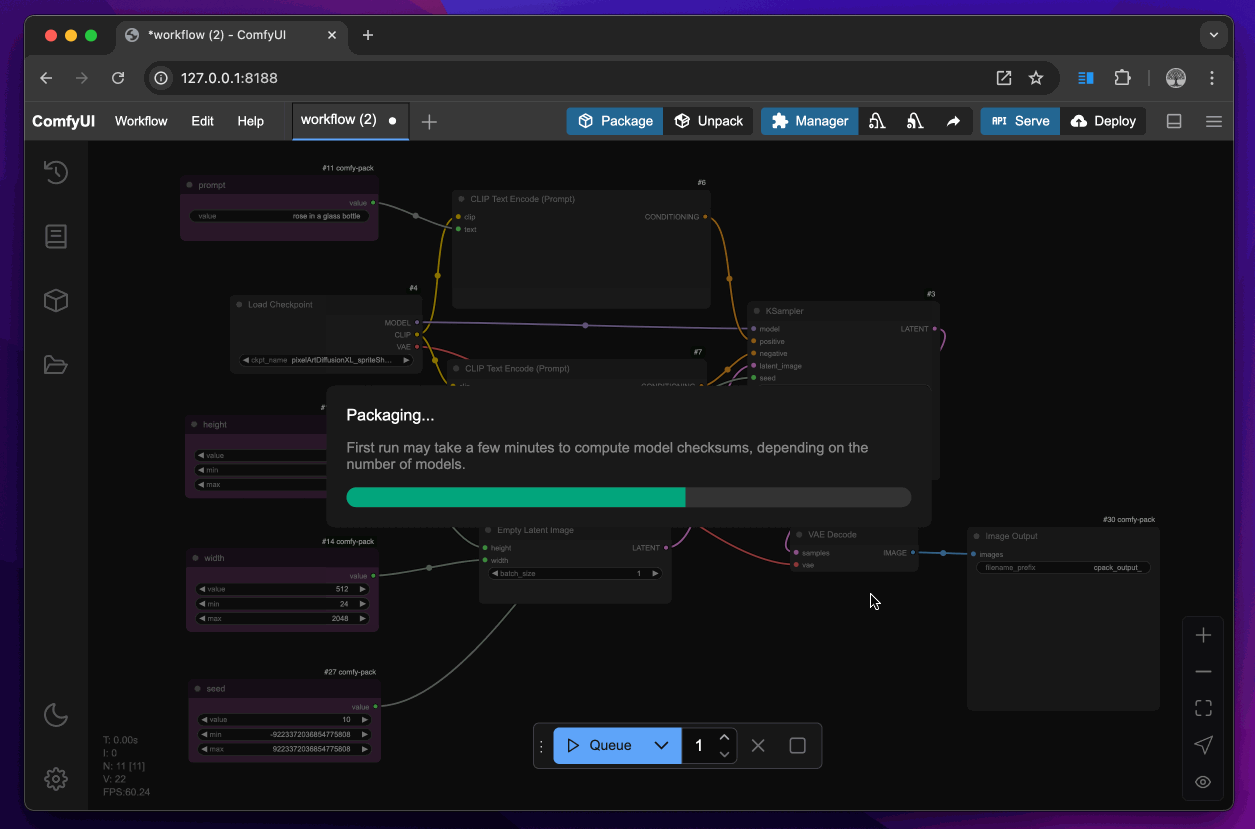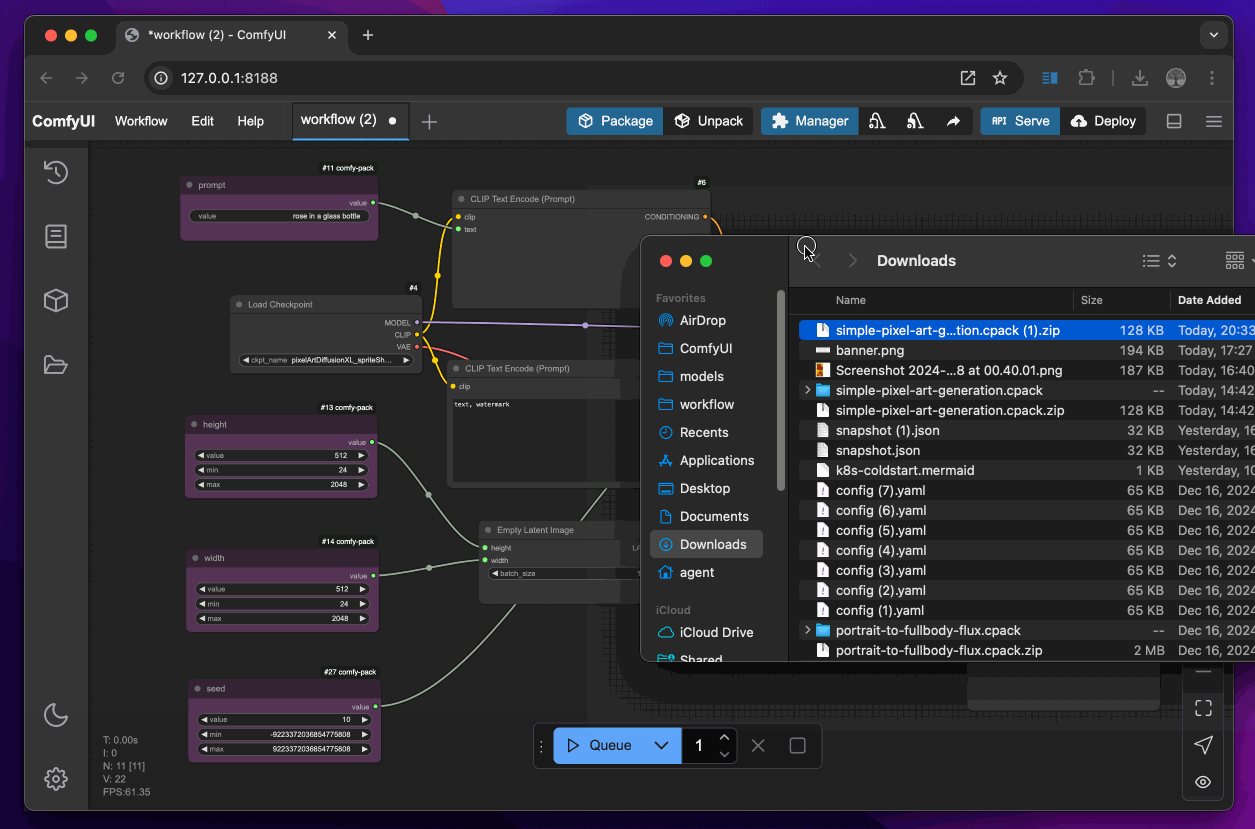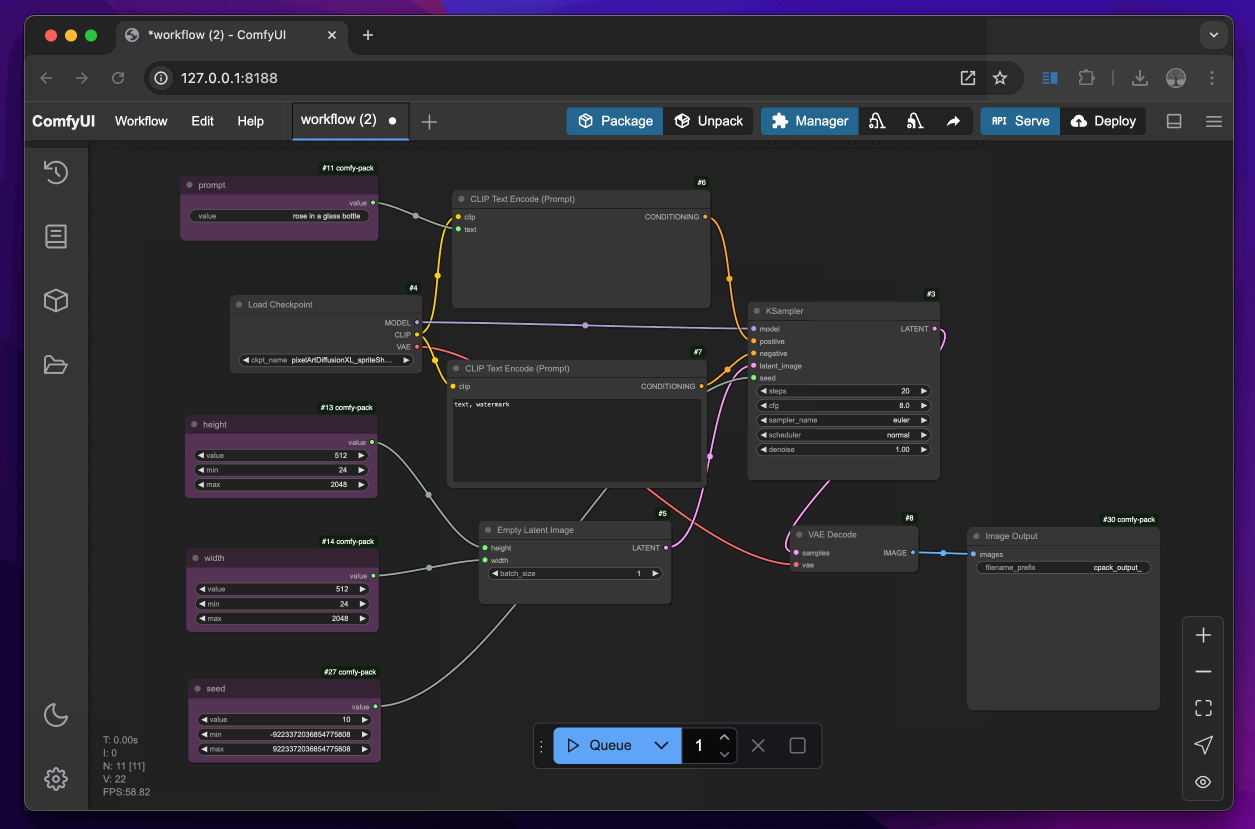
You can package a workflow and the environment required to run the workflow into an artifact that can be unpacked elsewhere.
- Click the Package button to create a
.cpack.zipartifact. - (Optional) Select the models that you want to include (only model hash will be recorded, so you won't get a 100GB zip file).
Unpack the ComfyUI environments
Unpacking a .cpack.zip artifact will restore the ComfyUI environment for the workflow. During unpacking, comfy-pack will perform the following steps.
- Prepare a Python virtual environment with the exact packages used to run the workflow.
- Clone ComfyUI and custom nodes from the exact revisions required by the workflow.
- Search for and download models from common registries like Hugging Face and Civitai. Unpacking workflows using the same model will not cause the model to be downloaded multiple times. Instead, model weights will be symbolically linked.
To unpack:
comfy-pack unpack workflow.cpack.zip
Huggingface gated models can be accessed by setting your HF_TOKEN as an environment variable before unpacking:
export HF_TOKEN=hf_XXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXx
comfy-pack unpack workflow.cpack.zip
For example cpack files, check our examples folder.
Deploy a workflow as an API
You can turn a ComfyUI workflow into an API endpoint callable using any clients through HTTP.
1. Annotate input & output
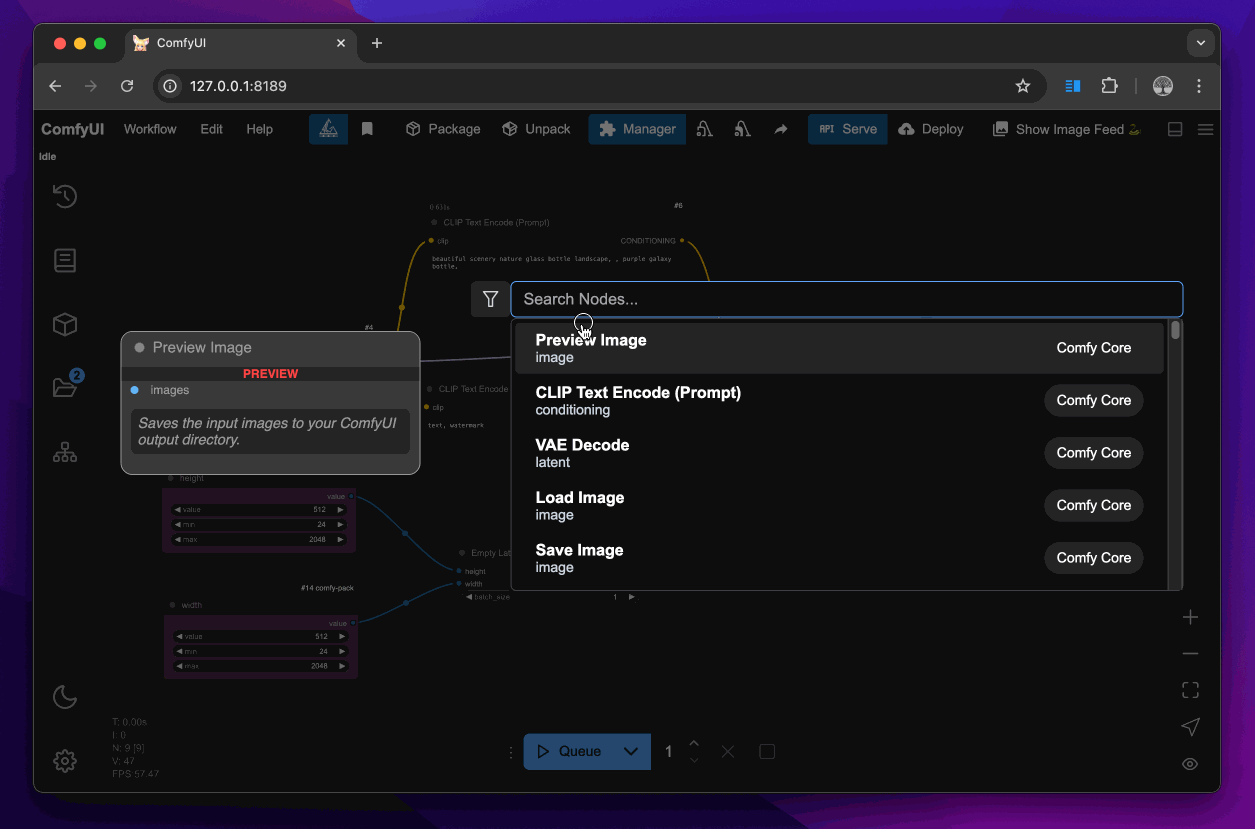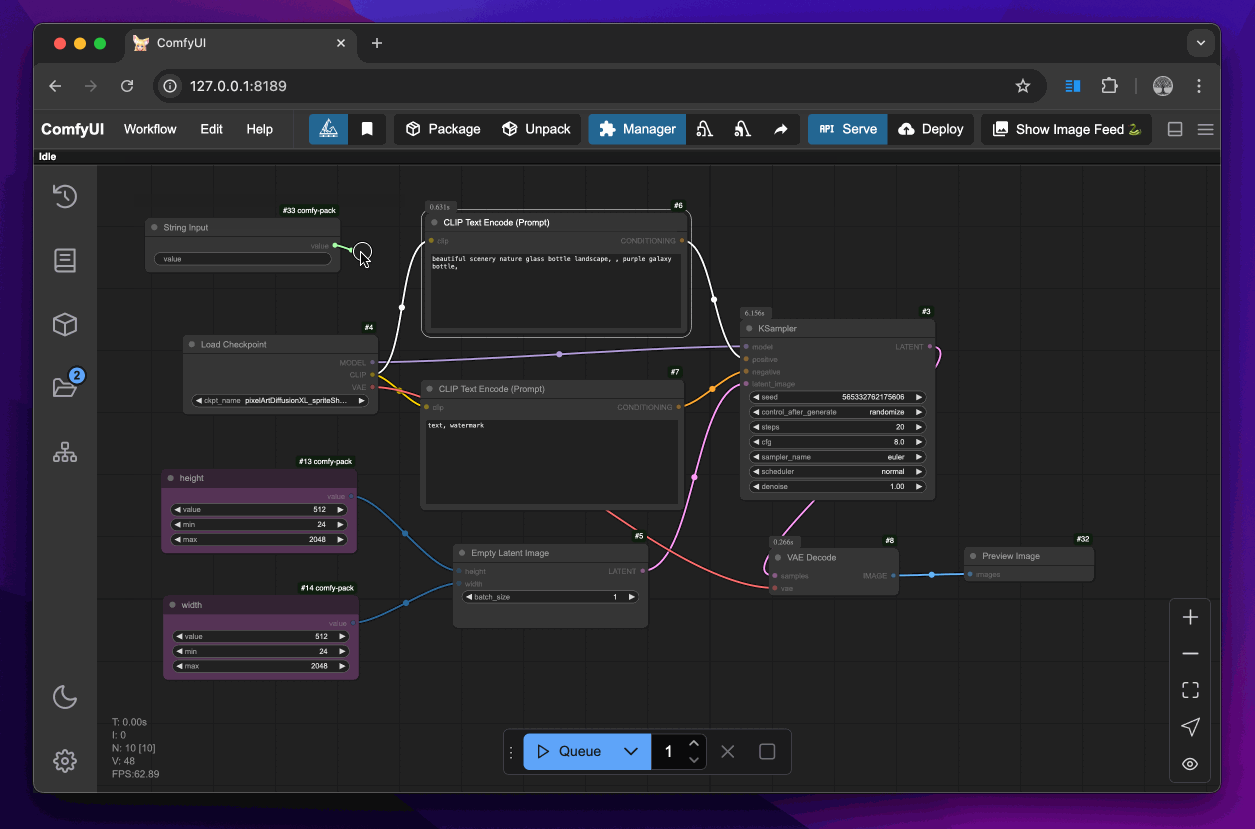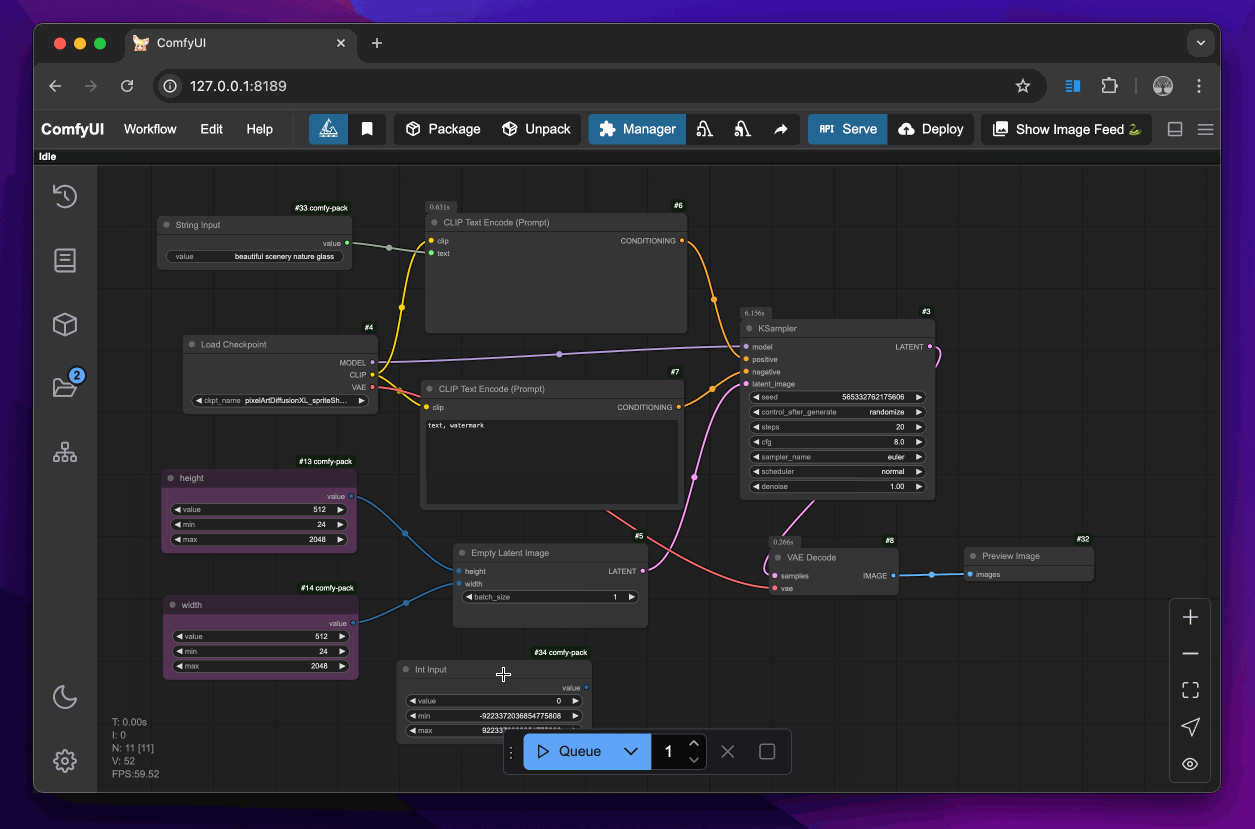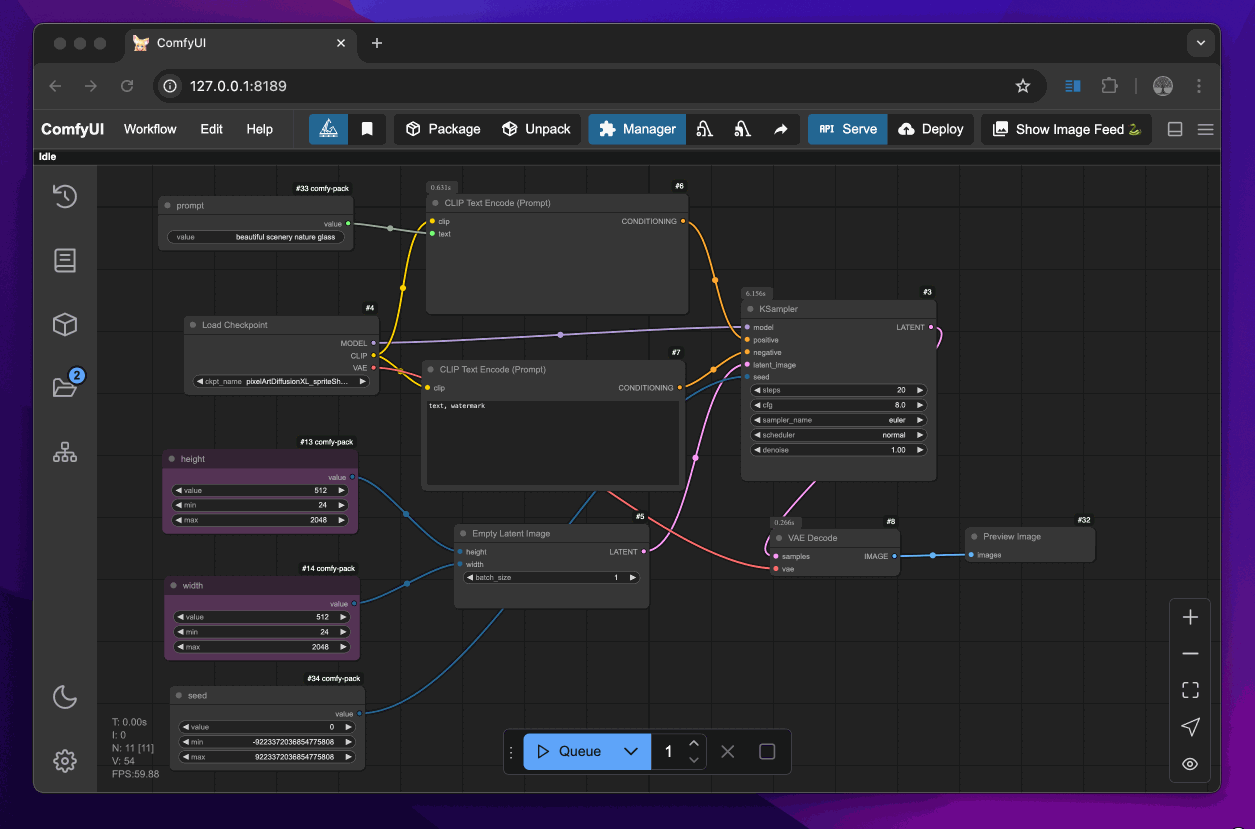
Use custom nodes provided by comfy-pack to annotate the fields to be used as input and output parameters. To add a comfy-pack node, right-click and select Add Node > ComfyPack > output/input > [Select a type]
Input nodes:
- ImageInput: Accepts
imagetype input, similar to the officialLoadImagenode - StringInput: Accepts
stringtype input (e.g., prompts) - IntInput: Accepts
inttype input (e.g., dimensions, seeds) - AnyInput: Accepts
combotype and more input (e.g., custom nodes)
Output nodes:
- ImageOutput: Outputs
imagetype, similar to the officialSaveImagenode - FileOutput: Outputs file path as
stringtype and saves the file under that path
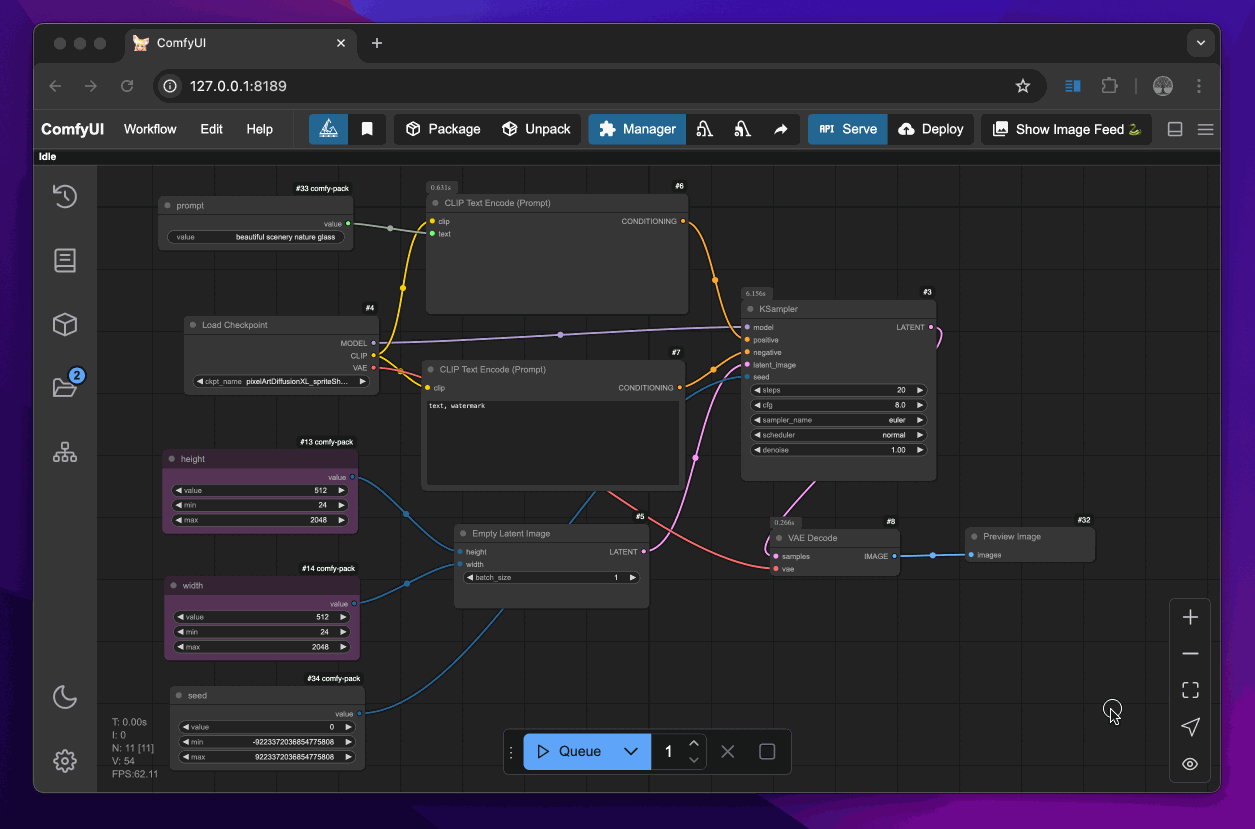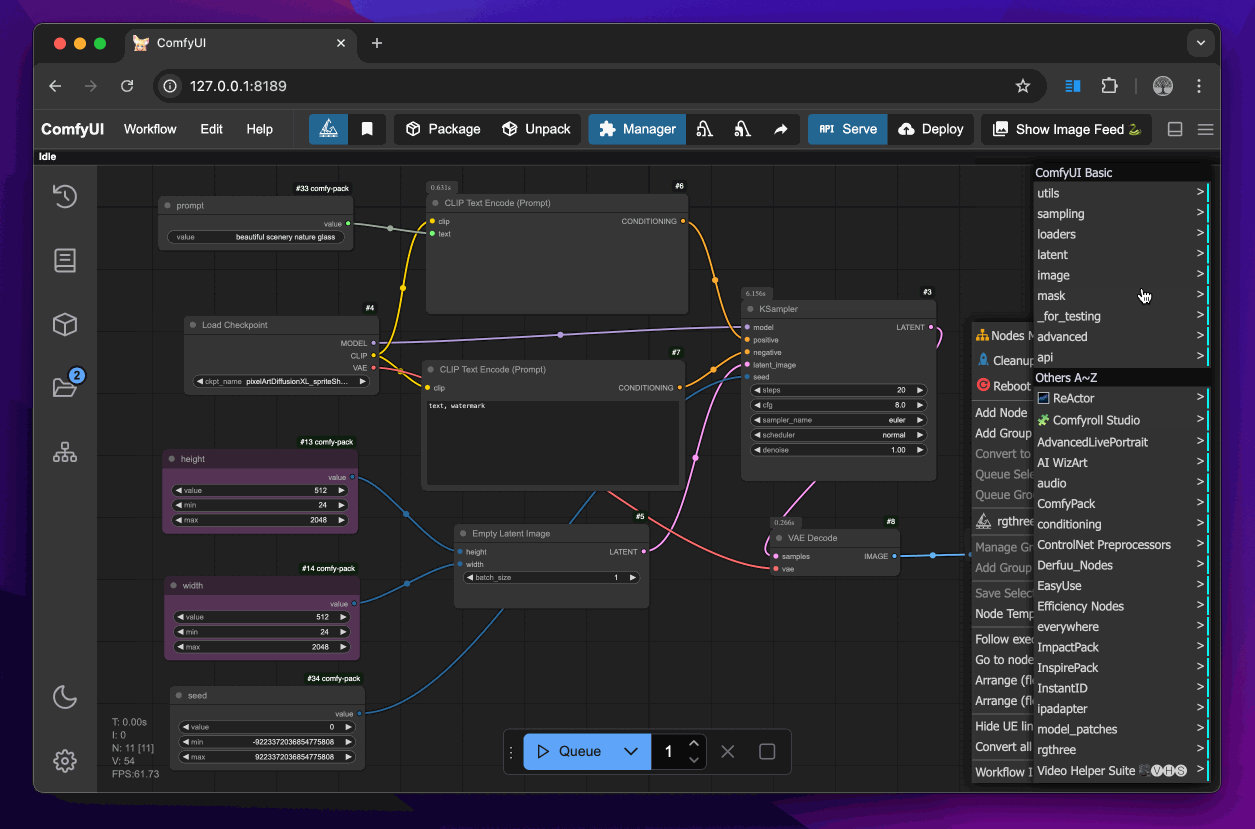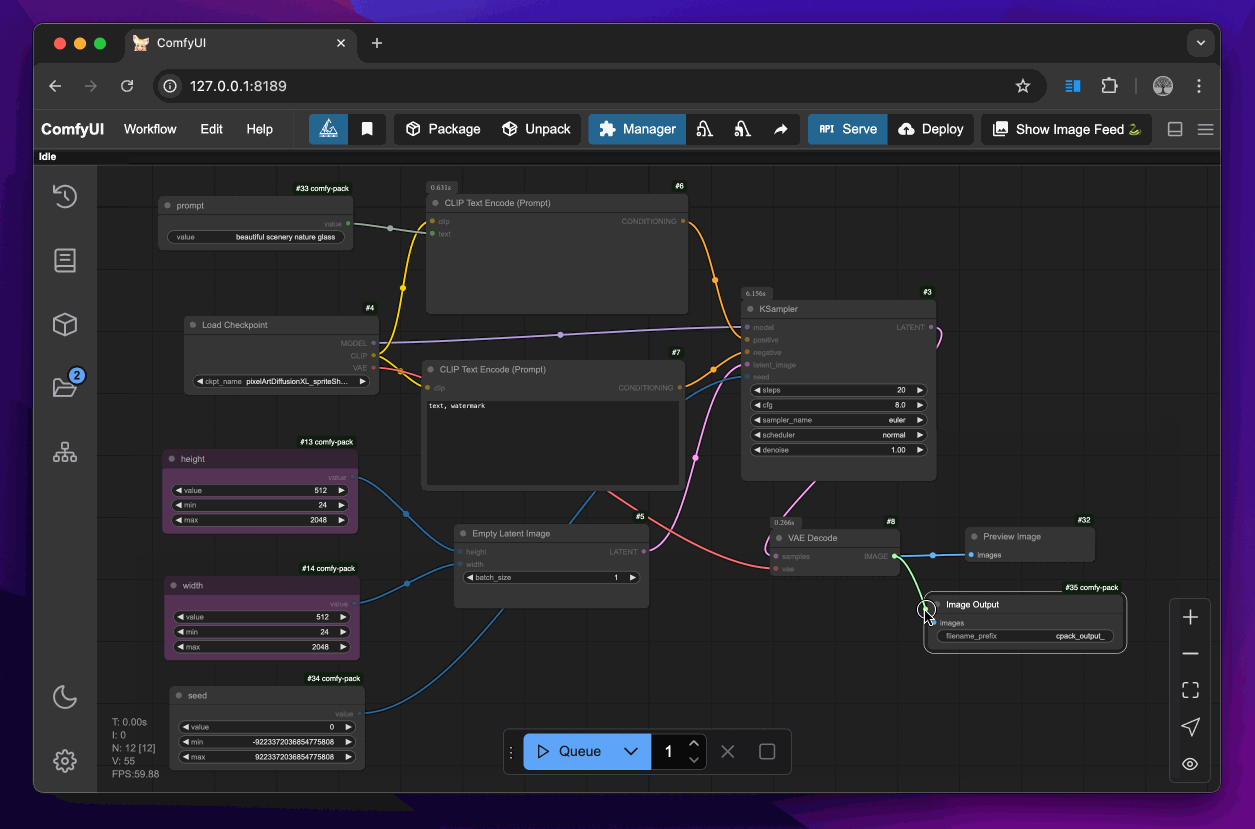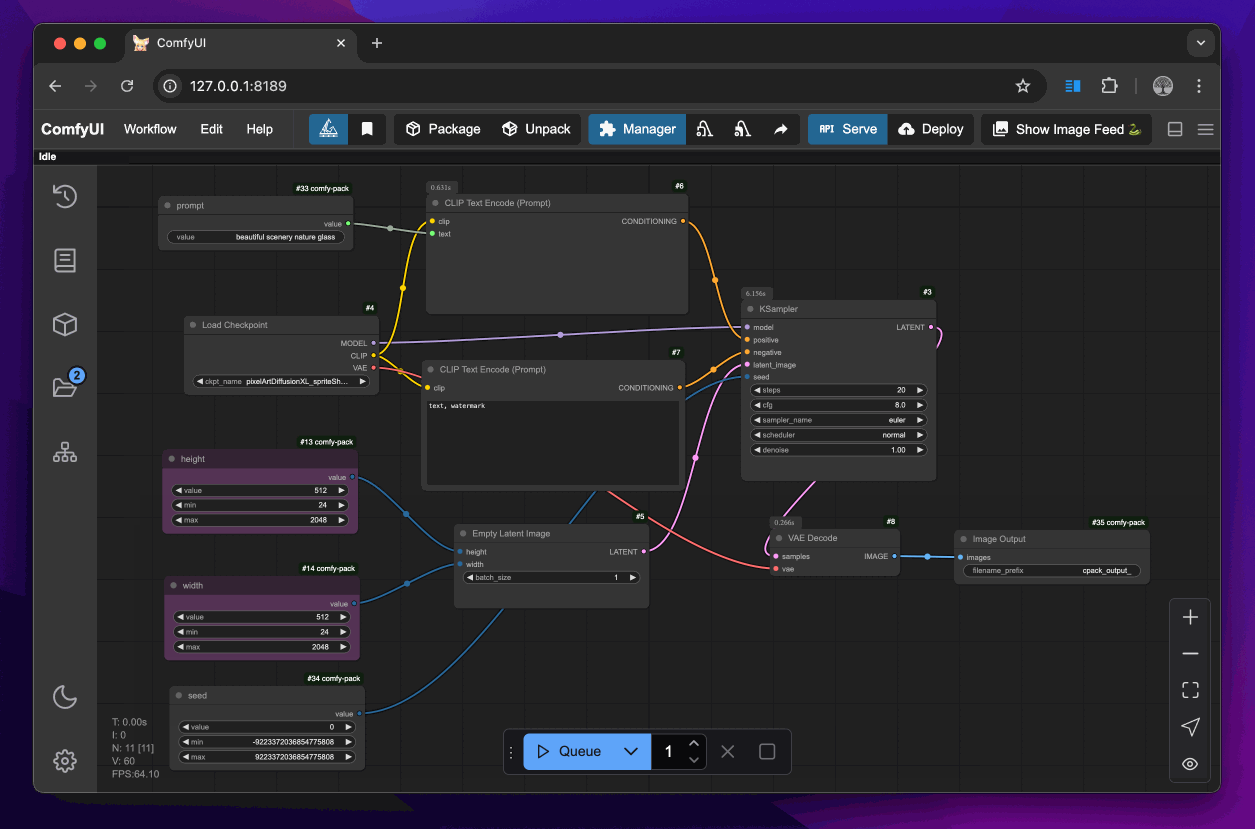
More field types are under way.
2. Serve the workflow
Start an HTTP server at http://127.0.0.1:3000 (default) to serve the workflow under the /generate path.
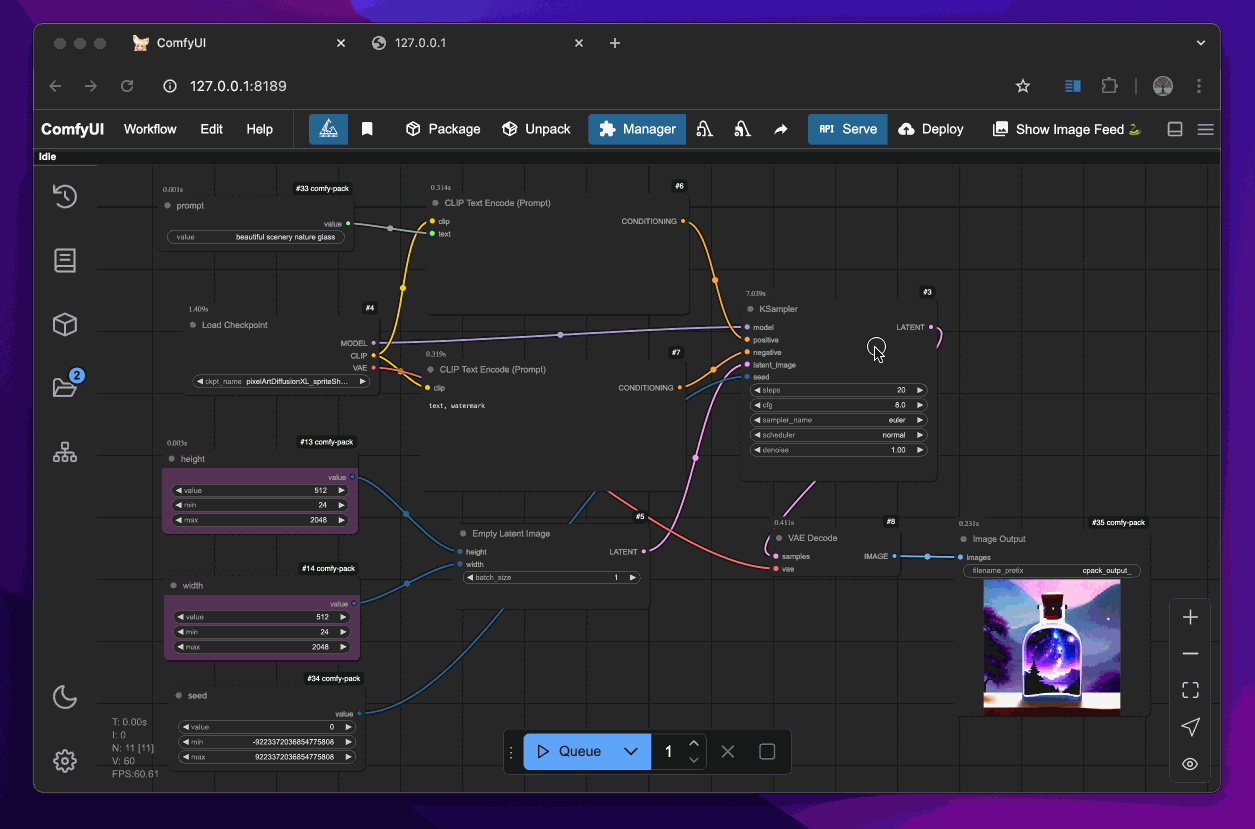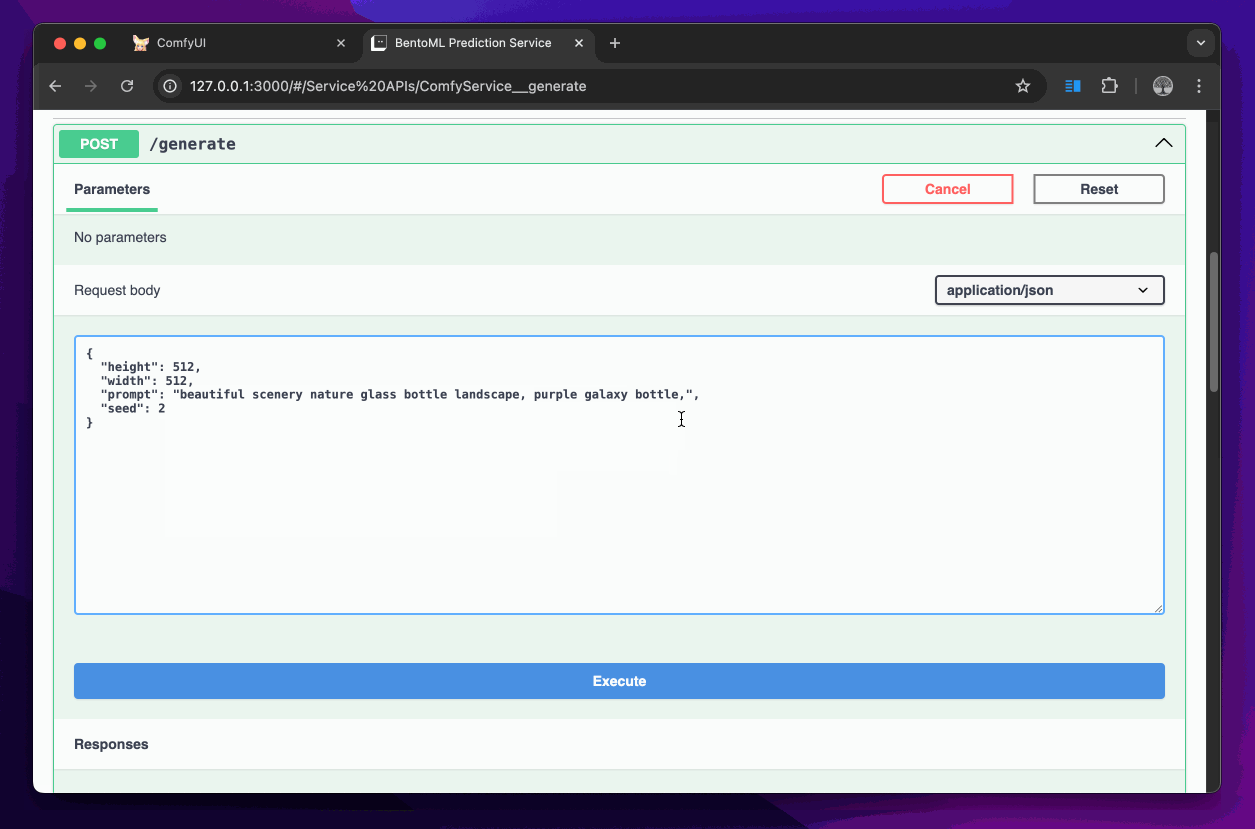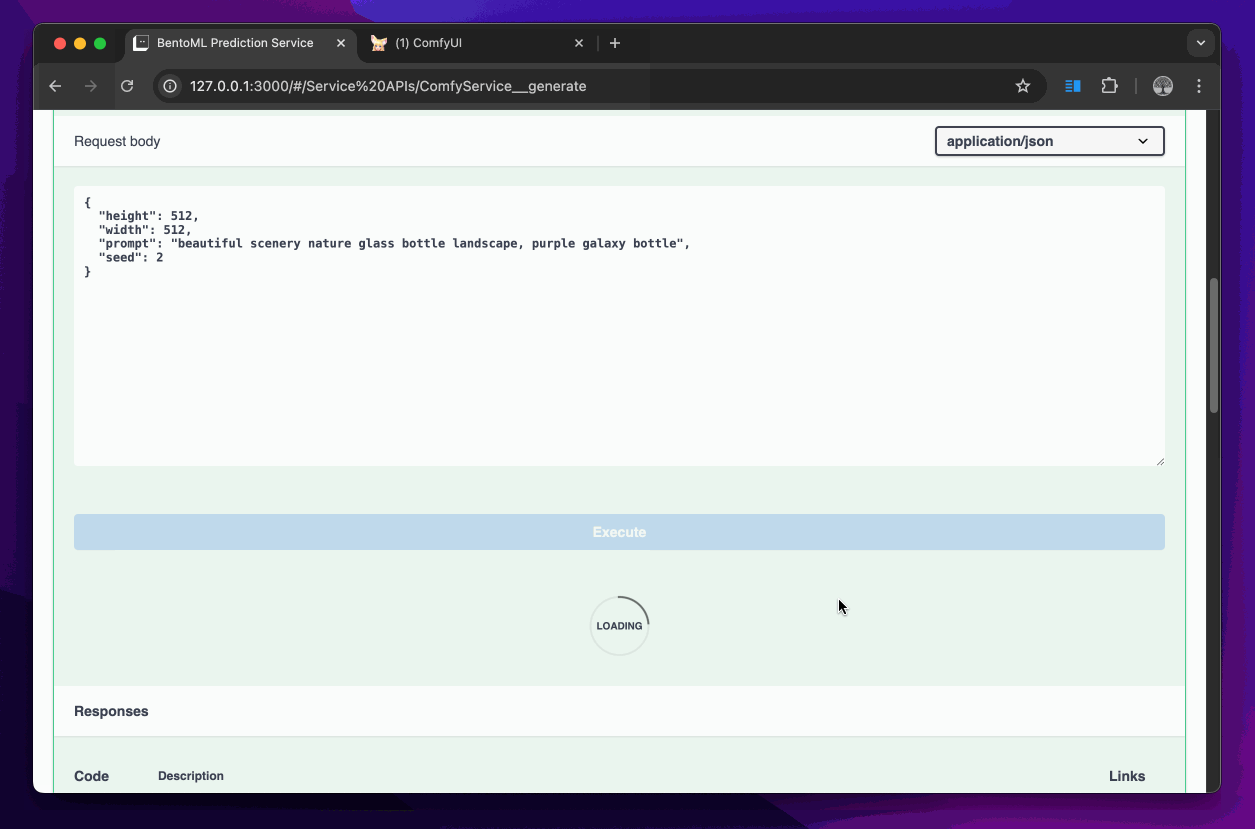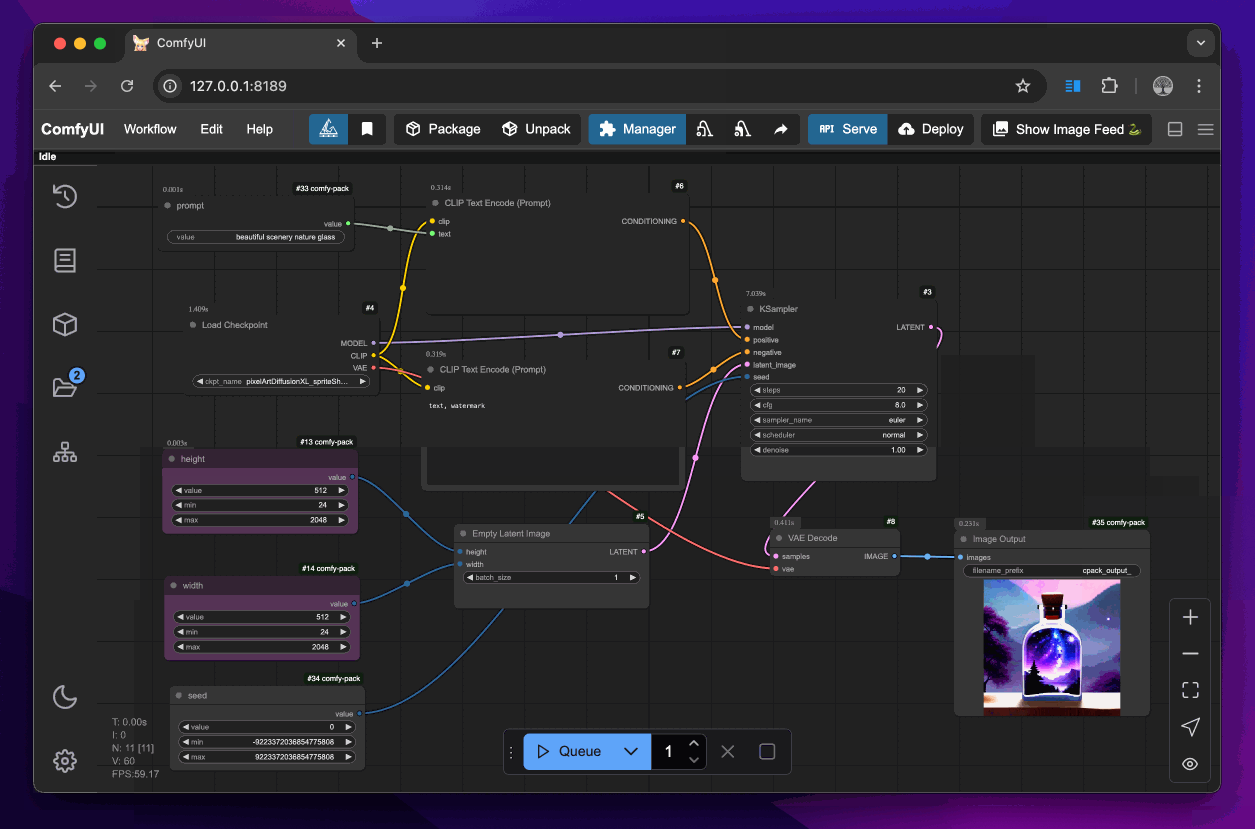
You can call the /generate endpoint by specifying parameters configured through your comfy-pack nodes, such as prompt, width, height, and seed.
Examples to call the endpoint:
CURL
curl -X 'POST' \
  'http://127.0.0.1:3000/generate' \
  -H 'accept: application/octet-stream' \
  -H 'Content-Type: application/json' \
  -d '{
  "prompt": "rocks in a bottle",
  "width": 512,
  "height": 512,
  "seed": 1
}'
BentoML client
Under the hood, comfy-pack leverages BentoML, the unified model serving framework. You can invoke the endpoint using the BentoML Python client:
import bentoml

with bentoml.SyncHTTPClient("http://127.0.0.1:3000") as client:
        result = client.generate(
            prompt="rocks in a bottle",
            width=512,
            height=512,
            seed=1
        )
3. (Optional) Pack the workflow and environment
Pack the workflow and environment into an artifact that can be unpacked elsewhere to recreate the workflow.
# Get the workflow input spec
comfy-pack run workflow.cpack.zip --help

# Run
comfy-pack run workflow.cpack.zip --src-image image.png --video video.mp4
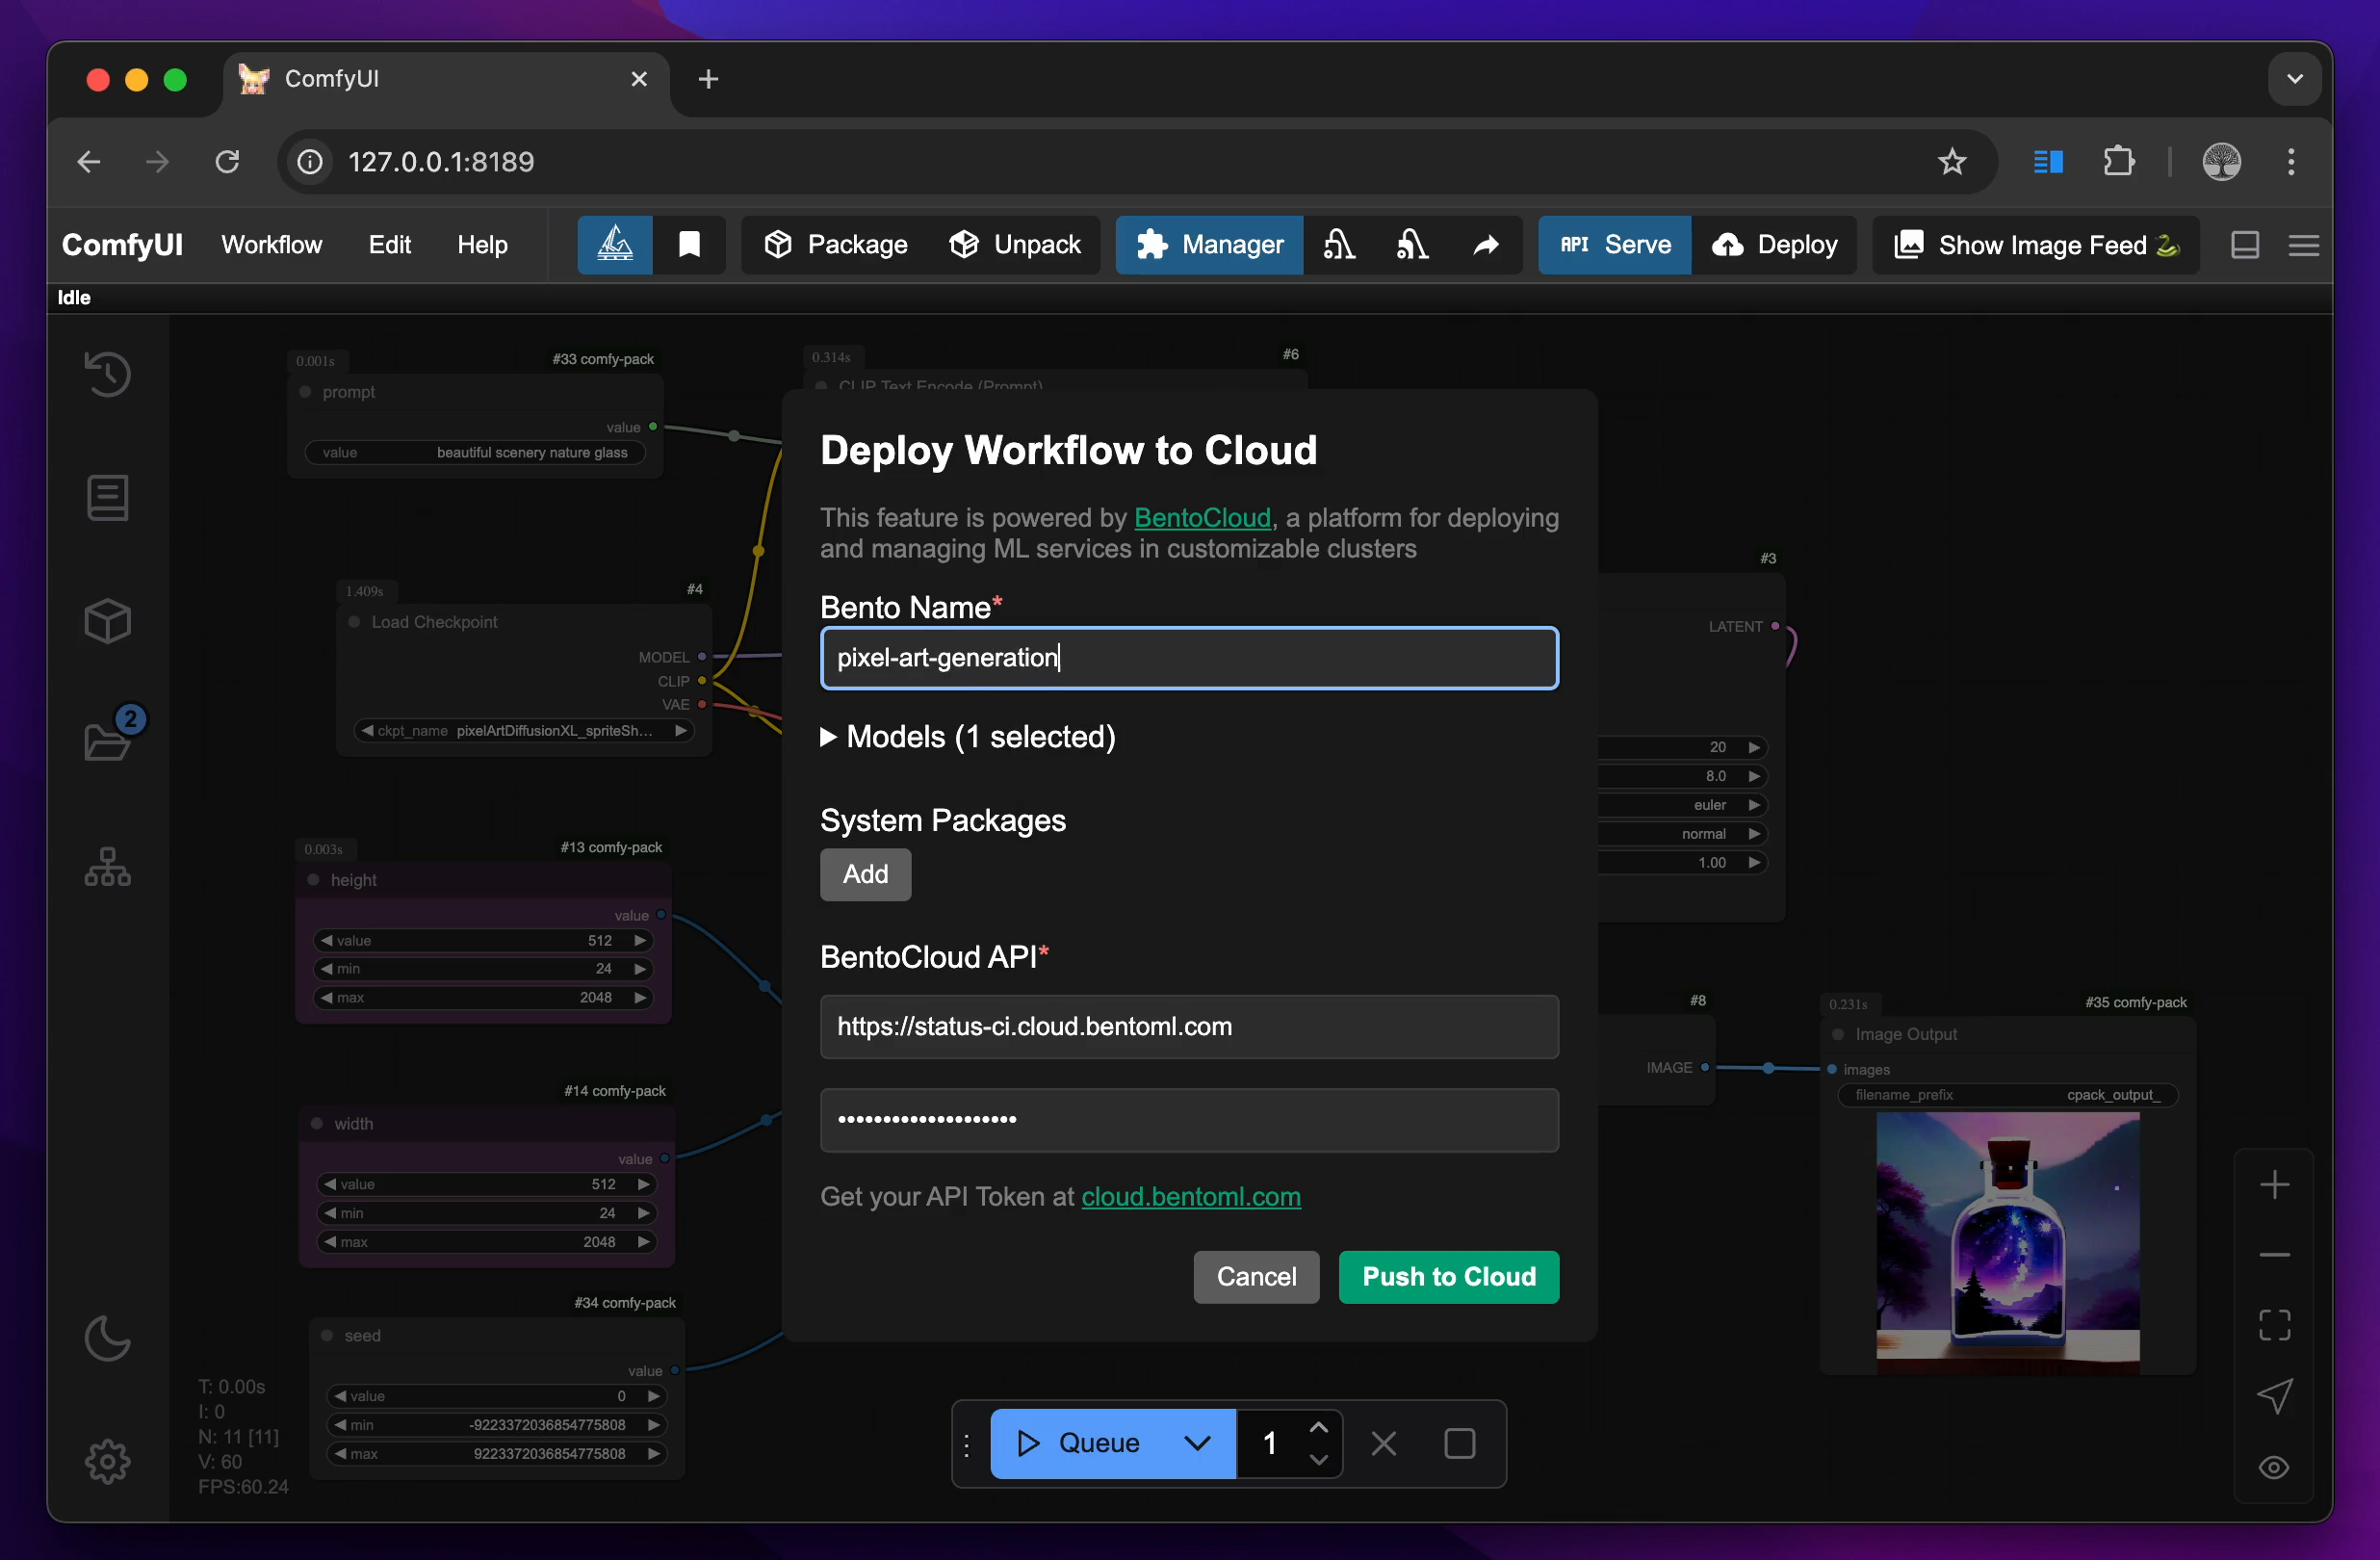
4. (Optional) Deploy to the cloud
Deploy to BentoCloud with access to a variety of GPUs and blazing fast scaling.
Follow the instructions here to get your BentoCloud access token. If you don’t have a BentoCloud account, you can sign up for free.
Security Guidelines
A cpack file only contains the metadata of the workflow environment, such as Python package versions, ComfyUI and custom node revisions, and model hashes. It does not contain any sensitive information like API keys, passwords, or user data. However, unpacking a cpack file will install custom nodes and Python dependencies. It is recommended to unpack cpack files from trusted sources.
comfy-pack has a strict mode for unpacking. You can enable it by setting the CPACK_STRICT_MODE environment variable to true. It will sacrifice some flexibility and compatibility for security. For now, comfy-pack will:
- Use more strict index strategy in Python package installation
More security features are under way.
Roadmap
This project is under active development. Currently we are working on:
- Enhanced user experience
- Docker support
- Local
.cpackfile management with version control - Enhanced service capabilities
Community
comfy-pack is actively maintained by the BentoML team. Feel free to reach out 👉 Join our Slack community!
Contributing
As an open-source project, we welcome contributions of all kinds, such as new features, bug fixes, and documentation. Here are some of the ways to contribute:
- Repost a bug by creating a GitHub issue.
- Submit a pull request or help review other developers’ pull requests.


Release files for comfy-pack 0.4.4
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| comfy_pack-0.4.4.tar.gz | 29.9 kB | With provenance | Details for comfy_pack-0.4.4.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| comfy_pack-0.4.4-py3-none-any.whl | Python 3 | none | any | Details for comfy_pack-0.4.4-py3-none-any.whl |
Total release size: 61.5 kB
Release files / comfy_pack-0.4.4.tar.gz
| Download URL | comfy_pack-0.4.4.tar.gz |
|---|---|
| Size | 29.9 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
b778319a174bb65332ff67aadad5f42e4b9b63e776c74d1a80ac5ecfd55132f7
|
|
BLAKE2b-256 checksum How to use checksums |
7bf3a4c183bb6e175f1cbc3f016d4999b479dad4ba8b61b640bd96a458d4fea9
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 10, 2025.
Transparency logRelease files / comfy_pack-0.4.4-py3-none-any.whl
| Download URL | comfy_pack-0.4.4-py3-none-any.whl |
|---|---|
| Size | 31.6 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
f3c59301bfe2c1816747d0396d4271a341ffa2fd18f09360e0a1350fcd72fcf9
|
|
BLAKE2b-256 checksum How to use checksums |
e571a6cc47d130618fc3272741c7791392a176d5a4909a351817a252515e3a55
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 10, 2025.
Transparency logSecurity for comfy-pack 0.4.4
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for comfy_pack-0.4.4.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 10, 2025.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














