
Confantic
Confantic is a lightweight, text-based user interface to edit YAML and JSON configuration files with real-time validation and feedback.
YAML and JSON configuration files are all over the place. For less polished workflows, they can become a sort of "user interface" into the configuration of system. Expecting users to fill out text files to modify configuration is an extremely easy thing to develop, but has obvious UX limitations; the most notable of which is user's often don't know which fields are expected and their constraints. Confantic seeks to address this and take configuration files as UI a little more seriously.
Installation
pip install confantic
Usage
Confantic is built on top of Pydantic to define the configuration model. To use it, you first need a pydantic model to validate against. Lets use this one as an example:
model.py
from pydantic import BaseModel


class ProgramConfig(BaseModel):
    name: str
    version: str
    debug: bool = False
To specify which model to use when editing, you use a Model URI that tells python how to import the model. It supports two different specifications:
- <file path>:<model class> (ex. ./my_folder/my_file.py:MyModel)
- <module path>:<model class> (ex. my_module.my_submodule:MyModel)
Now, we can run the following command to start creating a config:
confantic model.py:ProgramConfig config.json
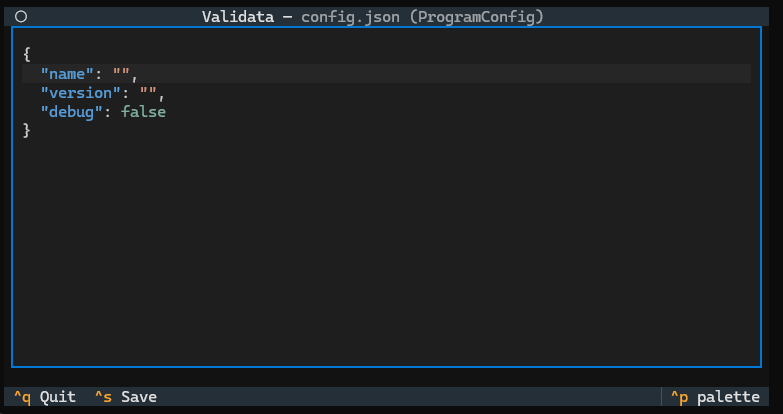
If the target file (config.json in this case) does not exist, it will populate the editor with some attempted defaults for the field - to at least give you the structure of the model.
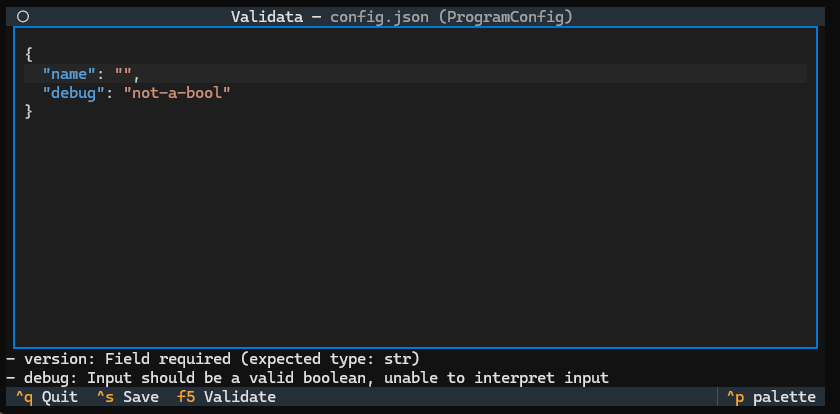
If we change some of the fields to create an error, we see the error show up at the bottom:
1 maintainer

Metadata
1 maintainer
Release files for confantic 1.0.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| confantic-1.0.0.tar.gz | 6.7 kB | With provenance | Details for confantic-1.0.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| confantic-1.0.0-py3-none-any.whl | Python 3 | none | any | Details for confantic-1.0.0-py3-none-any.whl |
Total release size: 13.8 kB
Release files / confantic-1.0.0.tar.gz
| Download URL | confantic-1.0.0.tar.gz |
|---|---|
| Size | 6.7 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
c267212e49eeed140e79f3a36445d9d08d71114169a03f47e758032e9f636f6f
|
|
BLAKE2b-256 checksum How to use checksums |
d9768640ee60b9ffea3a4efbff815a06a612349c6db1b53ff85f383a279a0768
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 30, 2026.
Transparency logRelease files / confantic-1.0.0-py3-none-any.whl
| Download URL | confantic-1.0.0-py3-none-any.whl |
|---|---|
| Size | 7.0 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
77bdf46276c6d03cfa5310c74ebcb1715ef7855e9eae5b945a73aaa2d5586e42
|
|
BLAKE2b-256 checksum How to use checksums |
1aeb481e5aedbc08d40fa708194395497ad35f25ef45093871e7c0aba2827fe8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 30, 2026.
Transparency logSecurity for confantic 1.0.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for confantic-1.0.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 30, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













