
coxstream
Exact out-of-core Cox proportional hazards regression via streaming Newton-Raphson.

Standard CoxPH solvers (lifelines, scikit-survival, R survival) load the
full cohort into memory before fitting, so on registry-scale data they exhaust
RAM long before the computation is hard. coxstream computes the exact Efron
partial-likelihood estimate by streaming a single time-sorted pass over the data
per Newton-Raphson iteration, holding only O(p^2) state for p covariates.
Working memory is therefore independent of the number of observations n:
the model fits on a workstation even when the cohort is far larger than RAM.
The streamed estimate is the in-memory maximum-likelihood estimate, and the Efron tie correction is carried across chunk boundaries, so heavily tied data are handled exactly.
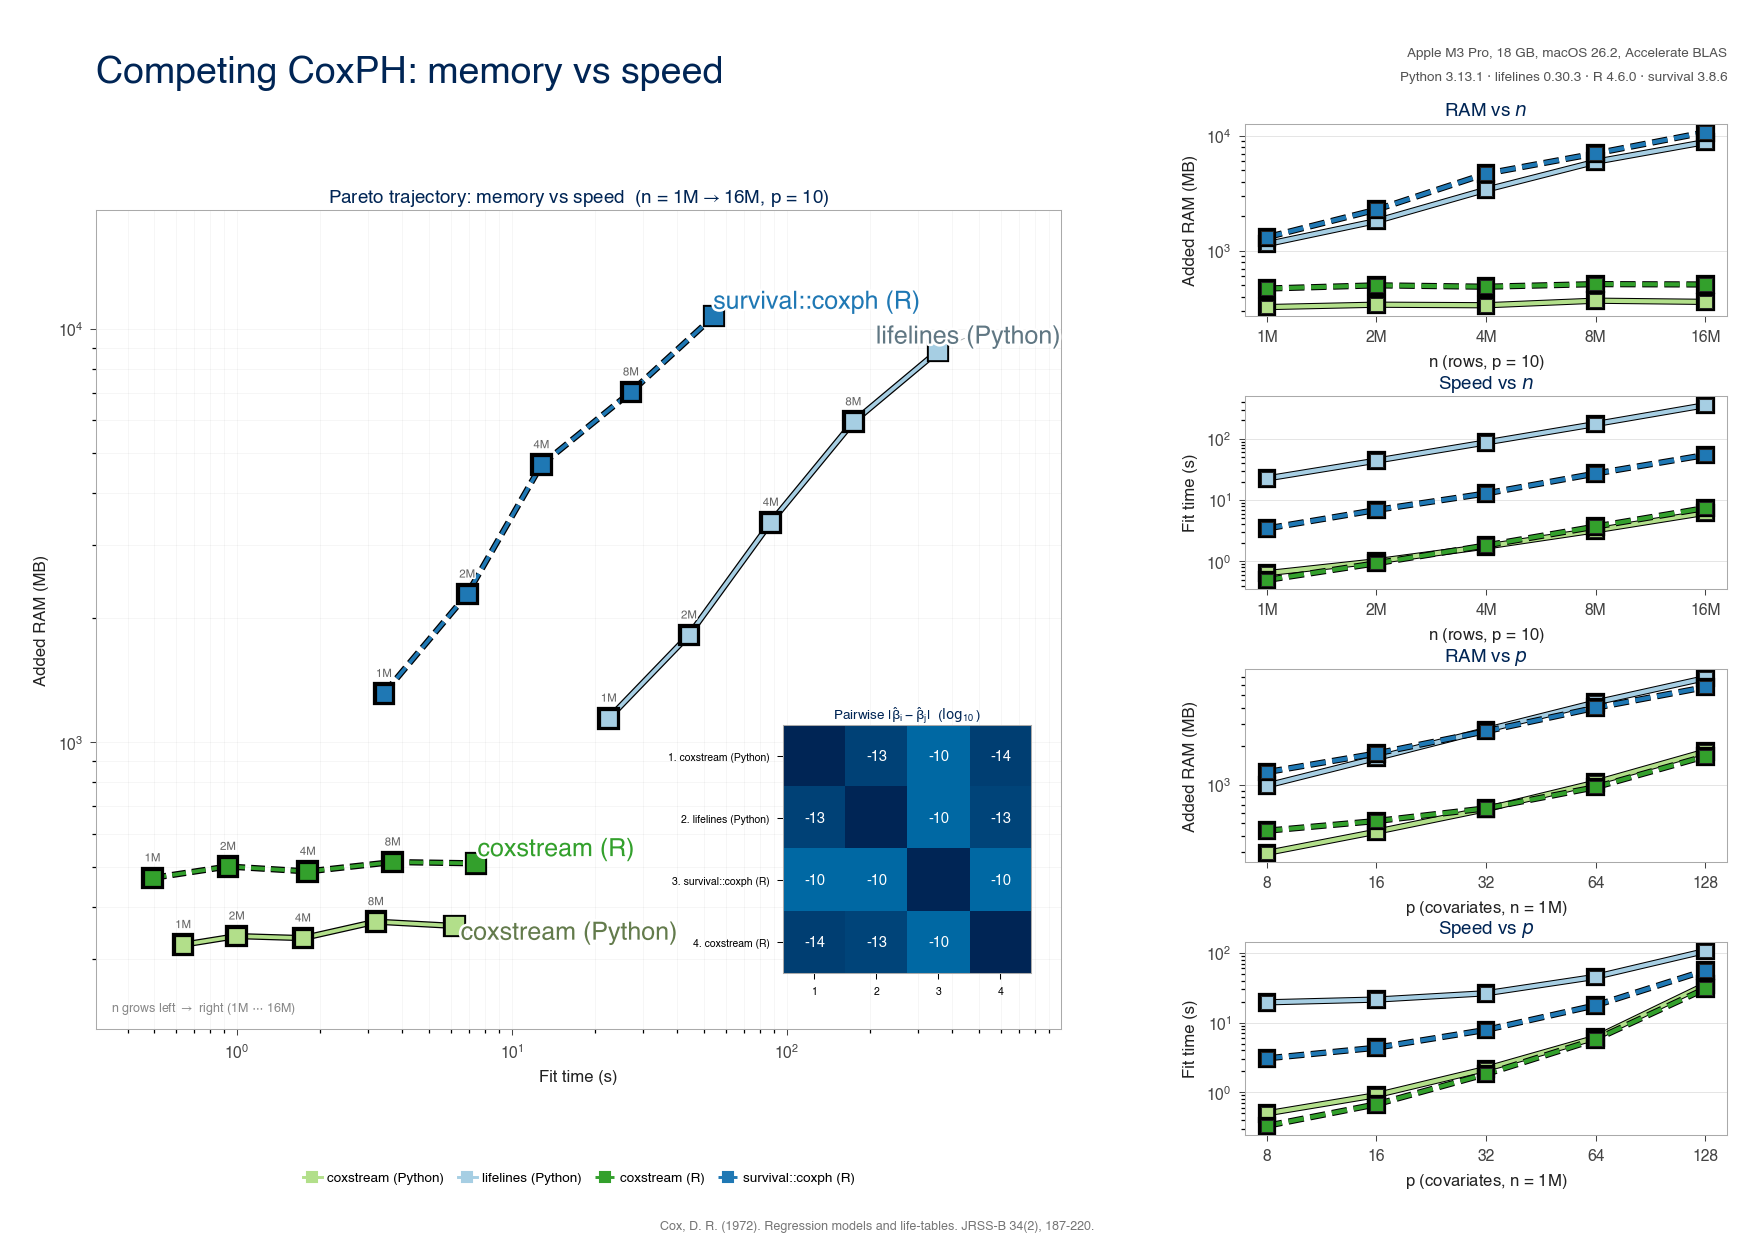
Memory vs. speed against lifelines and R survival::coxph: coxstream's peak
RAM stays flat in the number of rows while in-memory solvers grow with the
cohort, at matching coefficients. See the accompanying paper for the full
methodology.
Install
pip install coxstream             # core (numpy only)
pip install coxstream[parquet]    # + out-of-core fit_parquet (pyarrow)
Prebuilt wheels are published for current CPython versions on Linux (x86_64, aarch64), macOS (universal2), and Windows, so most installs need no toolchain. A C compiler is only needed when building from the sdist (e.g. on a platform without a wheel), since the package compiles a small Cython kernel.
Usage
In memory:
import numpy as np
from coxstream import CoxStream

model = CoxStream().fit(durations, events, X, feature_names=names)
print(model.coef_, model.standard_errors_, model.n_iter_)
standard_errors_ and variance_matrix_ come from the observed information accumulated in the final pass, so they cost no extra pass over the data; n_passes_ reports how many full passes the fit made (one per iteration plus one).
If your cohort records interval endpoints rather than a precomputed follow-up
time, pass start/stop and the duration is stop - start (right-censored
follow-up; entry times are not modelled):
model = CoxStream().fit(start=entry, stop=exit, events=events, X=X)
Out of core, from a Parquet file pre-sorted by descending event time (never materialises the cohort):
from coxstream import CoxStream

# The file must already be sorted by duration DESC. `fit_parquet` verifies this
# from the Parquet footer statistics alone (no full pass) and rejects a file
# that is out of order; pass assume_sorted=True to skip the check.
#
# Sort it once with an out-of-core sorter -- both spill to disk, so they handle
# a cohort larger than RAM (a sort-engine benchmark found these the fastest):
#   duckdb:  COPY (SELECT * FROM 'cohort.parquet' ORDER BY duration DESC)
#            TO 'cohort_desc.parquet' (FORMAT PARQUET);
#   polars:  (pl.scan_parquet("cohort.parquet")
#              .sort("duration", descending=True)
#              .sink_parquet("cohort_desc.parquet"))
#   R:       duckdb via its R client runs the same COPY ... ORDER BY DESC.
# If the cohort fits in RAM, skip the file and call .fit, which sorts for you.

model = CoxStream().fit_parquet(
    "cohort_desc.parquet",
    duration_col="duration",
    event_col="event",
    covariate_cols=["age_std", "sex", "treatment"],
)
print(model.coef_)
To validate a file's order ahead of time -- a dry run, e.g. a CI or pipeline
gate right after you sort and before a long fit -- call check_sorted, which
runs the same footer-only check without fitting and raises on a file that is
provably out of order:
from coxstream import check_sorted

check_sorted("cohort_desc.parquet", duration_col="duration")  # raises if unsorted
It doubles as a shell gate -- it exits non-zero on an out-of-order file, so a pipeline step can fail fast without a bespoke CLI:
python -c "import coxstream; coxstream.check_sorted('cohort_desc.parquet', 'duration')"
Validation
coxstream is verified against lifelines and R survival::coxph:
- It reproduces the in-memory maximum-likelihood estimate to machine precision on synthetic data.
- On heavily tied synthetic data (monthly-discretised event times) the exact
Efron pass matches
lifelineswhere the Breslow approximation would diverge. - Peak resident memory is flat in
nwhile in-memory solvers grow with the cohort and eventually exhaust RAM.
The package's own test suite is dependency-free: it checks exactness against a
self-contained plain-numpy Cox Newton-Raphson reference. The cross-checks
against lifelines and R survival::coxph above live in the accompanying
benchmark and paper.
The methodology and full results are in the accompanying paper (see Citation).
Scope
coxstream implements the exact Efron partial likelihood for large-n,
modest-p tabular survival data. It is a focused estimator, not a full survival
suite: it does not provide baseline-hazard estimation, time-varying covariates,
or proportional-hazards diagnostics.
Testing
pip install -e '.[test]'           # core suite (numpy only)
pip install -e '.[test,parquet]'   # + the out-of-core fit_parquet test
pytest
Citation
If you use coxstream, please cite it via the metadata in
CITATION.cff.
License
MIT. See LICENSE.
1 maintainer

Metadata
1 maintainer
Release files for coxstream 0.3.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| coxstream-0.3.0.tar.gz | 194.5 kB | With provenance | Details |
Built distributions (wheels)
Total release size: 10.8 MB
Release files / coxstream-0.3.0.tar.gz
| Download URL | coxstream-0.3.0.tar.gz |
|---|---|
| Size | 194.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
c76bddc5cbc2245bb246e2bc46f7cf2784ab3f71b01c5d52d76ebc74ae5f7603
|
|
BLAKE2b-256 checksum How to use checksums |
f7c217652d617fb71733d7bf8e20ec778c9873ebaaba183a264adbdb26d506b8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logRelease files / coxstream-0.3.0-cp314-cp314-win_amd64.whl
| Download URL | coxstream-0.3.0-cp314-cp314-win_amd64.whl |
|---|---|
| Size | 273.1 kB |
| Tags | CPython 3.14 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
5dbacab8c11dbc7d1c2795e32cfd1290f0194b095506a5fe2c717019804c3ed0
|
|
BLAKE2b-256 checksum How to use checksums |
a329f61133ee9c32b5ac198d7b1378b314b27eb44c2759a1d2f88b8bcb5ee5fa
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logRelease files / coxstream-0.3.0-cp314-cp314-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl
| Download URL | coxstream-0.3.0-cp314-cp314-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 735.7 kB |
| Tags | CPython 3.14 Linux glibc 2.17+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
e6f2973d0f16cdabcea478ce3363f5d1446189646e7aad61b90f413496c565e2
|
|
BLAKE2b-256 checksum How to use checksums |
441e24b93d5a2b30116ef7f03c26c112697686d346b72aa7e09293659a5c64fd
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logRelease files / coxstream-0.3.0-cp314-cp314-manylinux2014_aarch64.manylinux_2_17_aarch64.manylinux_2_28_aarch64.whl
| Download URL | coxstream-0.3.0-cp314-cp314-manylinux2014_aarch64.manylinux_2_17_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 727.6 kB |
| Tags | CPython 3.14 Linux glibc 2.17+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
99f9558f75aadb0c15491815f28b20464effcea8d3375ff2d5fb3c6a25bbc699
|
|
BLAKE2b-256 checksum How to use checksums |
5ddbbab4a04b0ff717594b4b22ee0650f2785390345cc90169d4d9acd54f3cbf
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logRelease files / coxstream-0.3.0-cp314-cp314-macosx_10_15_universal2.whl
| Download URL | coxstream-0.3.0-cp314-cp314-macosx_10_15_universal2.whl |
|---|---|
| Size | 373.1 kB |
| Tags | CPython 3.14 macOS 10.15+ universal2 (ARM64, x86-64) |
|
SHA-256 checksum How to use checksums |
b873dab780884e2c0bdaaf3f6ce025ff43f28415243aa5592274c3087502a795
|
|
BLAKE2b-256 checksum How to use checksums |
074394790c0111b9da6865811d0bb9737a8d31c91eabfc37dc9ed137575a7dfd
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logRelease files / coxstream-0.3.0-cp313-cp313-win_amd64.whl
| Download URL | coxstream-0.3.0-cp313-cp313-win_amd64.whl |
|---|---|
| Size | 271.9 kB |
| Tags | CPython 3.13 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
c5a151b43b7eb3774ef57555d73b96571bc0cb0ff7dd5e4a558f33e094c83c71
|
|
BLAKE2b-256 checksum How to use checksums |
c4a532c1d7a425ebb8ff13c2667ac82045b40c88dc7fa52da35c63d494b60473
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logRelease files / coxstream-0.3.0-cp313-cp313-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl
| Download URL | coxstream-0.3.0-cp313-cp313-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 747.5 kB |
| Tags | CPython 3.13 Linux glibc 2.17+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
4eb4395c5862836212c7e944bb045bb22101d128e4e125ccf3c6d931c16a4b8c
|
|
BLAKE2b-256 checksum How to use checksums |
50ff2615d2095ca0737f94730d1d9eb230367d37e6e6b9da9e3db3695a08af08
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logRelease files / coxstream-0.3.0-cp313-cp313-manylinux2014_aarch64.manylinux_2_17_aarch64.manylinux_2_28_aarch64.whl
| Download URL | coxstream-0.3.0-cp313-cp313-manylinux2014_aarch64.manylinux_2_17_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 727.2 kB |
| Tags | CPython 3.13 Linux glibc 2.17+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
2e660e8c4f18d7efc9b8b0775415ff854bb9b4cf585b47daee639379e91e899b
|
|
BLAKE2b-256 checksum How to use checksums |
dfe38d30a69c14e927e6a7bf58cd3817cd763bca6ea3f3892669da33918266e8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logRelease files / coxstream-0.3.0-cp313-cp313-macosx_10_13_universal2.whl
| Download URL | coxstream-0.3.0-cp313-cp313-macosx_10_13_universal2.whl |
|---|---|
| Size | 372.4 kB |
| Tags | CPython 3.13 macOS 10.13+ universal2 (ARM64, x86-64) |
|
SHA-256 checksum How to use checksums |
22c3f5ab768eaa85901039dbb6ede676c4da1107996f1ee7840f5358ec500ef1
|
|
BLAKE2b-256 checksum How to use checksums |
05d5670915bf39222bc1d5b6e66d9630304d2a0d14b7bdeccbce21abef0d547c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logRelease files / coxstream-0.3.0-cp312-cp312-win_amd64.whl
| Download URL | coxstream-0.3.0-cp312-cp312-win_amd64.whl |
|---|---|
| Size | 272.1 kB |
| Tags | CPython 3.12 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
808f86bbbd94c19a3cc184d8c92977deeafb05330a7c65300201df3494ed60c7
|
|
BLAKE2b-256 checksum How to use checksums |
3db43b8162fadc93667be413e55c911976bf03be7218f1a3a7c33d9c2397abeb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logRelease files / coxstream-0.3.0-cp312-cp312-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl
| Download URL | coxstream-0.3.0-cp312-cp312-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 744.9 kB |
| Tags | CPython 3.12 Linux glibc 2.17+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
39204782a5494ebe32d065df6a166fb648f64b183c8981f85acf1afbbc9a2c73
|
|
BLAKE2b-256 checksum How to use checksums |
81c765571f1263d4791f8c6daaa3506089ada18821047b994884e5f02a0894f7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logRelease files / coxstream-0.3.0-cp312-cp312-manylinux2014_aarch64.manylinux_2_17_aarch64.manylinux_2_28_aarch64.whl
| Download URL | coxstream-0.3.0-cp312-cp312-manylinux2014_aarch64.manylinux_2_17_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 731.7 kB |
| Tags | CPython 3.12 Linux glibc 2.17+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
e422fb40cb0ec222d963cc2e9e4378a5e60b17a81d83e83cc773288dec67a18c
|
|
BLAKE2b-256 checksum How to use checksums |
0ca2c21012be23bd761d153cd31bc11fec6ca8be5a58f8054004114167a4dae3
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logRelease files / coxstream-0.3.0-cp312-cp312-macosx_10_13_universal2.whl
| Download URL | coxstream-0.3.0-cp312-cp312-macosx_10_13_universal2.whl |
|---|---|
| Size | 373.0 kB |
| Tags | CPython 3.12 macOS 10.13+ universal2 (ARM64, x86-64) |
|
SHA-256 checksum How to use checksums |
7d84afd4198e98dd1e70531e6e4ee60bb9901ed81f4506920be9761e92e66d45
|
|
BLAKE2b-256 checksum How to use checksums |
497cff2947f581aaccef490f8b08abc989b3da6487c1f2a3c1be6439bc832189
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logRelease files / coxstream-0.3.0-cp311-cp311-win_amd64.whl
| Download URL | coxstream-0.3.0-cp311-cp311-win_amd64.whl |
|---|---|
| Size | 269.5 kB |
| Tags | CPython 3.11 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
9ccc81c39a28f3283d429f338ceb7836c9928c7f15079fbd33420ba940348858
|
|
BLAKE2b-256 checksum How to use checksums |
f3e3eb7211f83cdd375bfd627c1b8d40fb72e4fd3034537b71bf0180c8137bea
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logRelease files / coxstream-0.3.0-cp311-cp311-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl
| Download URL | coxstream-0.3.0-cp311-cp311-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 747.5 kB |
| Tags | CPython 3.11 Linux glibc 2.17+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
f1bbdb1beee305a238ddd128bf7e059a60ef679b2368c3dfe656f2e18ecd537a
|
|
BLAKE2b-256 checksum How to use checksums |
0b60d34a8a4bae30c2effb0eba0e71e3b29f71a46efac0536d04d676da3955e4
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logRelease files / coxstream-0.3.0-cp311-cp311-manylinux2014_aarch64.manylinux_2_17_aarch64.manylinux_2_28_aarch64.whl
| Download URL | coxstream-0.3.0-cp311-cp311-manylinux2014_aarch64.manylinux_2_17_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 739.5 kB |
| Tags | CPython 3.11 Linux glibc 2.17+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
5f6e5fb792dceae98a06f3c78227881fb5bd170ebe813c9ed9bf03e9fdf6e82d
|
|
BLAKE2b-256 checksum How to use checksums |
66a7f61c0e39c7846066a6486f95bf2e9fb65a63830cf17e8259619461edf4e1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logRelease files / coxstream-0.3.0-cp311-cp311-macosx_10_9_universal2.whl
| Download URL | coxstream-0.3.0-cp311-cp311-macosx_10_9_universal2.whl |
|---|---|
| Size | 371.0 kB |
| Tags | CPython 3.11 macOS 10.9+ universal2 (ARM64, x86-64) |
|
SHA-256 checksum How to use checksums |
9b9ee5f3a96aed821be28f6d1487aaac72522daf6a4011da327789d22757236e
|
|
BLAKE2b-256 checksum How to use checksums |
073855846368d8bb58965c4d3d5445aa0e718814c27d5b21f96c3a46d7745214
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logRelease files / coxstream-0.3.0-cp310-cp310-win_amd64.whl
| Download URL | coxstream-0.3.0-cp310-cp310-win_amd64.whl |
|---|---|
| Size | 269.7 kB |
| Tags | CPython 3.10 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
1db3d09aef0b200909970a546ec2579b28ae95435a82499ed46e548845f10488
|
|
BLAKE2b-256 checksum How to use checksums |
08de65933eaf438b445dbd3c881e7fcf8697b34cf7cdee3a28c5a168d372ca4a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logRelease files / coxstream-0.3.0-cp310-cp310-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl
| Download URL | coxstream-0.3.0-cp310-cp310-manylinux2014_x86_64.manylinux_2_17_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 724.2 kB |
| Tags | CPython 3.10 Linux glibc 2.17+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
28ffd77d2870afb1f39858e45a9ee29b3698da5ae5ddc9fc0bf4fb0731c992ed
|
|
BLAKE2b-256 checksum How to use checksums |
cd735869218490f1c648b4c11efa0157abf47f10b0901140579973257cc8e2b3
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logRelease files / coxstream-0.3.0-cp310-cp310-manylinux2014_aarch64.manylinux_2_17_aarch64.manylinux_2_28_aarch64.whl
| Download URL | coxstream-0.3.0-cp310-cp310-manylinux2014_aarch64.manylinux_2_17_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 717.6 kB |
| Tags | CPython 3.10 Linux glibc 2.17+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
c98f9e04f7e046381860d4c3ea333f7c72b18152b1ae82e3f10ca254e9caba48
|
|
BLAKE2b-256 checksum How to use checksums |
f581b5bd71df34c4790642f4278a0684c71fcab099ff75d93d2b1826849ffdbc
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logRelease files / coxstream-0.3.0-cp310-cp310-macosx_10_9_universal2.whl
| Download URL | coxstream-0.3.0-cp310-cp310-macosx_10_9_universal2.whl |
|---|---|
| Size | 372.2 kB |
| Tags | CPython 3.10 macOS 10.9+ universal2 (ARM64, x86-64) |
|
SHA-256 checksum How to use checksums |
0fae8d00f78050ed294afe35478e39e778190248c78254758816d9f7dda38628
|
|
BLAKE2b-256 checksum How to use checksums |
7fbf259097d97c81c7e39ad607d3be5b11d2ddb5bc736ba30dc16545c2be88ca
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logSecurity for coxstream 0.3.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 21 files in this release have been uploaded with provenance metadata.
Attestation for coxstream-0.3.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 6, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














