
🛡️ Desktop-2FA
A secure, offline two-factor authentication (2FA) manager for desktop environments. Built with Python, featuring strong encryption and no cloud dependencies.
🌐 Landing Page: desktop-2fa.org


✨ Features
| Feature | Description |
|---|---|
| 🔐 Vault Security | AES-256-GCM encryption with Argon2id key derivation |
| ⏱️ TOTP Generation | RFC 6238 compliant code generation |
| 💻 Full CLI | Complete command-line interface for managing tokens |
| 📋 Clipboard Support | Automatic copying of TOTP codes to clipboard |
| 🔓 Stateless Design | Every command requires explicit password authentication |
| 🛡️ Password Policy | Configurable password strength enforcement with zxcvbn |
| 🧪 Well Tested | 302 tests passing with comprehensive coverage |
| 📖 Security Model | Detailed threat analysis and cryptographic design documentation |
📸 Screenshots
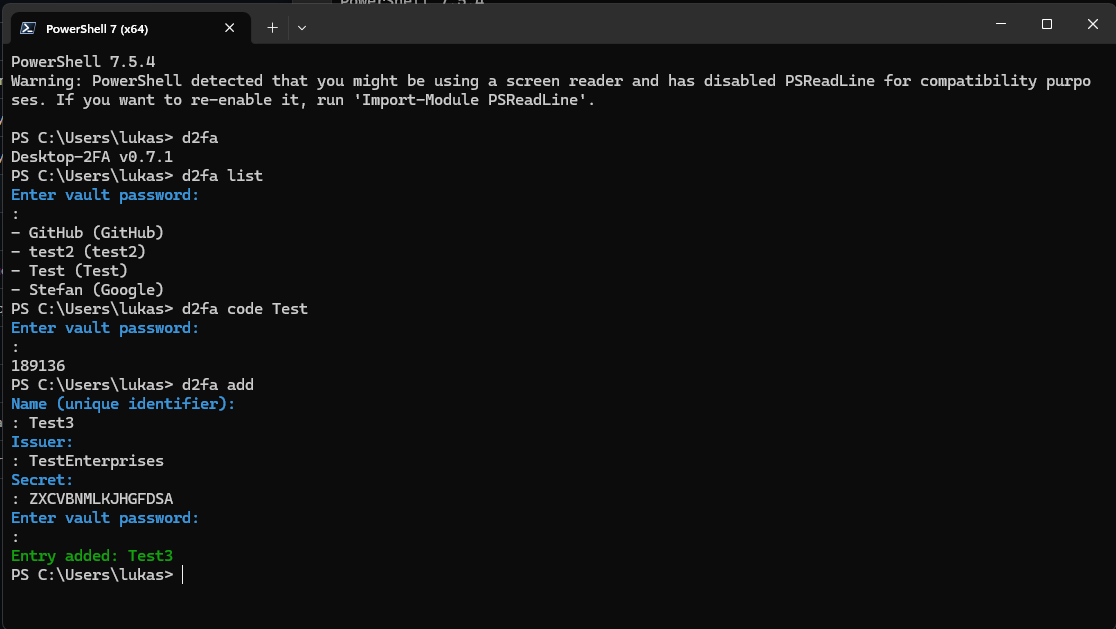
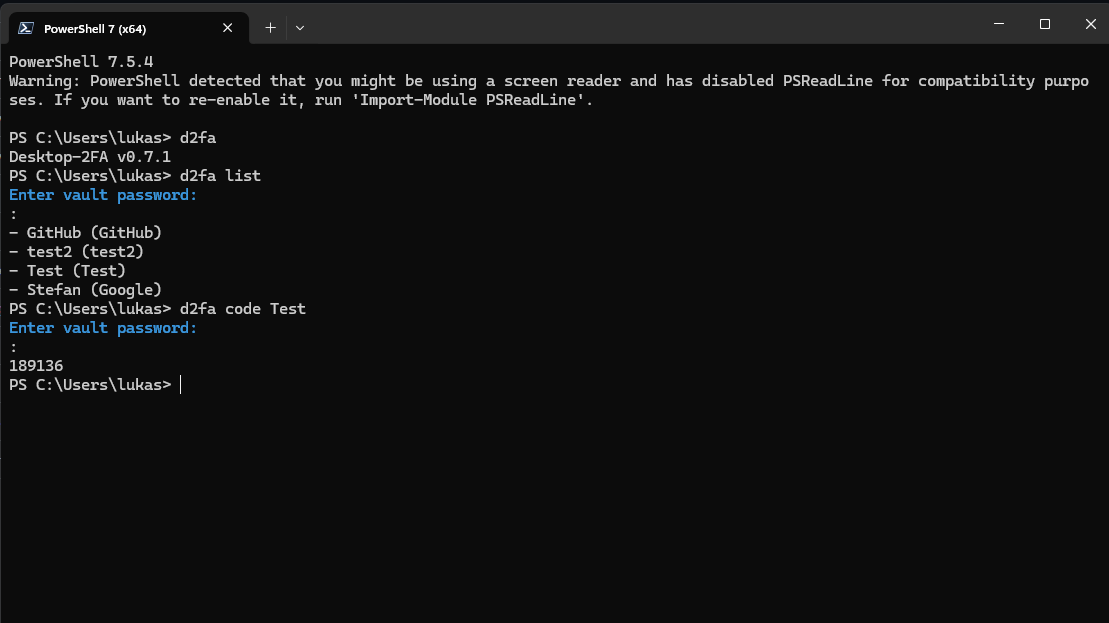
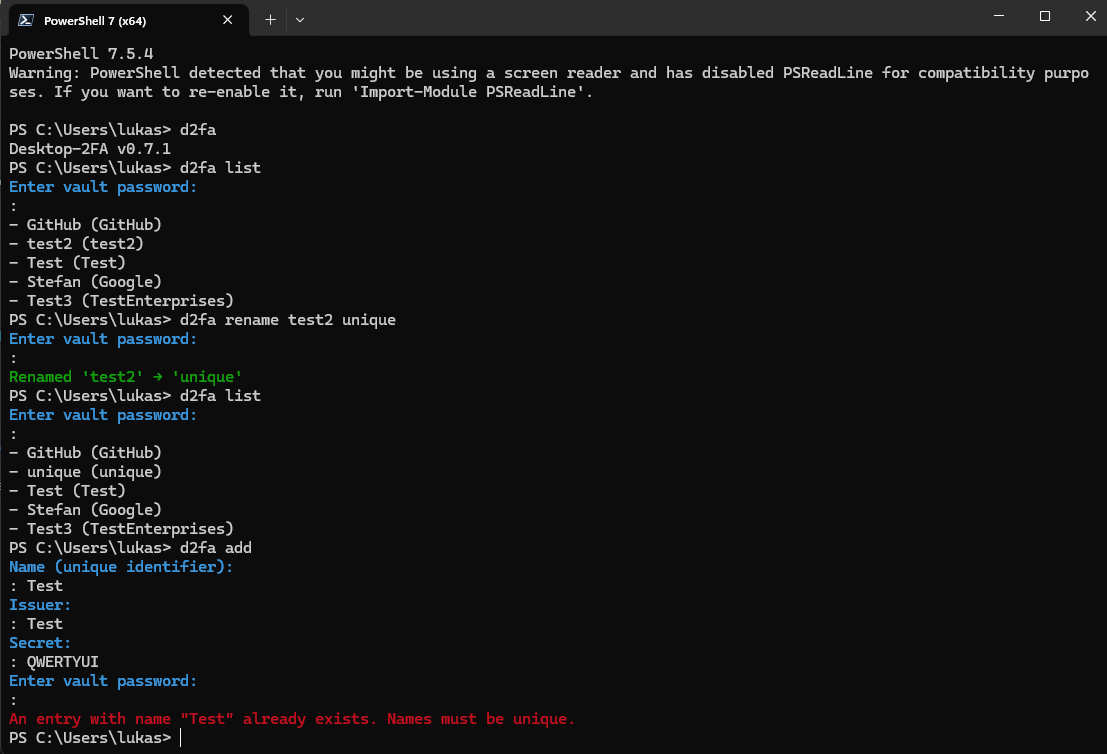
🚀 Quick Start
Installation
pip install desktop-2fa
Verify installation:
python -c "import desktop_2fa; print(desktop_2fa.__version__)"
# Output: 0.8.2
Basic Usage
# Initialize a new vault
d2fa vault init

# Add a new TOTP token
d2fa add GitHub GitHub JBSWY3DPEHPK3PXP

# List all entries
d2fa list

# Generate a code
d2fa code GitHub
Choose a vault file for any command with --vault, or set
DESKTOP_2FA_VAULT to select one by default. An explicit --vault takes
precedence over the environment variable; without either, the default remains
~/.desktop-2fa/vault.
# Use a separate vault for this command
d2fa --vault ./development-vault list

# Show the currently selected vault path
d2fa vault path
Non-Interactive Usage
# Provide password via command line
d2fa --password mypassphrase add GitHub GitHub JBSWY3DPEHPK3PXP

# Provide password via file
d2fa --password-file /path/to/passphrase.txt add GitHub GitHub JBSWY3DPEHPK3PXP
📁 Vault Lifecycle
The vault is an encrypted storage file located by default at
~/.desktop-2fa/vault. A custom path can be selected with --vault or
DESKTOP_2FA_VAULT.
Vault Creation
When a command requires a vault and none exists:
- The CLI prompts for a new password (interactive mode) or requires
--password/--password-file(non-interactive mode) - An empty encrypted vault is created
- A confirmation message is always printed:
Vault created at <path>
Vault Loading
When a command requires a vault and it exists:
- The CLI prompts for the existing password (interactive mode) or requires credentials (non-interactive mode)
- The vault is decrypted and loaded
- If the password is invalid, the CLI exits with
typer.Exit(1)
Duplicate Entry Handling
The rename command enforces deterministic behavior when multiple entries match the target name:
- If multiple entries match the provided name (issuer or account_name), the rename is aborted
- Error message:
Error: Multiple entries named '<name>' exist. Operation aborted. Resolve duplicates first. - No entry is renamed in this case
- This check occurs before any mutation
📖 CLI Commands
Core Commands
| Command | Description |
|---|---|
d2fa add <name> <issuer> <secret> |
Add a new TOTP entry |
d2fa list |
List all stored TOTP entries |
d2fa rename <old> <new> |
Rename an entry |
d2fa remove <name> |
Remove an entry |
d2fa code <name> [--copy|--copy-only] |
Generate TOTP code with clipboard copy options |
Vault Management
| Command | Description |
|---|---|
d2fa vault init [--force] |
Initialize a new vault (d2fa init-vault is an alias) |
d2fa vault unlock |
Open vault with weak password warning (if configured) |
d2fa vault change-password |
Change the vault password |
d2fa vault path |
Show the selected vault path |
d2fa backup |
Create an encrypted backup of the vault |
d2fa export <path> |
Export vault to file |
d2fa import <path> [--force] |
Import vault from file |
Global Options
| Option | Description |
|---|---|
--version |
Show the installed version |
--password <pwd> |
Provide vault password directly |
--password-file <path> |
Read vault password from file |
--vault <path> |
Select the vault file; place before the command |
--allow-weak-passwords |
Allow weak passwords |
--help |
Show command help |
The --vault option takes precedence over DESKTOP_2FA_VAULT. When neither
is provided, Desktop-2FA uses ~/.desktop-2fa/vault. The --json, --raw,
--quiet, --copy, and --copy-only options belong to d2fa code; --force
is available on vault initialization and import commands.
🔒 Security
The vault uses:
- AES-256-GCM for authenticated encryption
- Argon2id for key derivation (time_cost=4, memory_cost=128MiB, parallelism=2)
- zxcvbn for password strength evaluation
- Versioned header for forward compatibility
Every command requires explicit password authentication. No session-based access.
Password Strength Evaluation
Desktop-2FA uses zxcvbn to evaluate password strength when creating or changing vault passwords:
- Score 0-2 (Weak): Easily guessable passwords (e.g., "password123")
- Score 3-4 (Strong): Resistant to common attacks (recommended)
Examples:
- ❌ Weak:
password,123456,qwerty,admin2024 - ✅ Strong:
Battery-Horse-Staple-Correct,Mountain@River*2024,MySecureVault#42
Configuration (~/.config/d2fa/config.toml):
[security]
# Require strong passwords (score >= 3)
reject_weak_passwords = false  # warn but allow | true: reject weak passwords
When reject_weak_passwords = false:
- Weak passwords trigger a yellow warning
- User is prompted to confirm continuation
- Password acceptance is non-blocking
When reject_weak_passwords = true:
- Weak passwords are rejected immediately
- Command exits with error
- User must choose a stronger password
Backward Compatibility:
If you have min_password_entropy set in your config (legacy option), it is recognized and treated as equivalent to requiring zxcvbn score >= 3.
Security Hardening (v0.8.0)
Version 0.8.0 maintains all previous security hardening from v0.7.3 and introduces modular architecture for better code isolation:
- Empty passwords are immediately rejected with a clear error message
- Permission errors are distinguished from missing vault files
- No Python stack traces are shown to users
- User-friendly error messages for filesystem permission issues
- Modular design separates CLI and core cryptographic components for enhanced security boundaries
- zxcvbn-based password strength evaluation (new in v0.8.0)
📚 Documentation
| Document | Description |
|---|---|
| User Manual | Complete usage guide |
| Security Model | Detailed threat analysis and cryptographic design |
| CLI UX Specification | UX contract and behavior |
| Cryptography | Security implementation details |
🧪 Testing
pytest tests/              # Run all tests
pytest --cov=src/desktop_2fa  # Run with coverage
🏗️ Project Structure
src/desktop_2fa/
├── app/           # Application components
├── cli/           # Command-line interface
├── crypto/        # Encryption utilities
├── totp/          # TOTP generation
├── ui/            # User interface components
├── vault/         # Vault management
└── utils/         # Utilities
📄 License
Apache License 2.0. See LICENSE file.
👤 Author
Łukasz Perek
🏆 Sponsorship
desktop‑2fa is supported through the Kilo OSS Sponsorship Program.
📧 Contact
For questions or support, contact us at contact@desktop-2fa.org
💖 Support the Project
Desktop‑2FA is an independent open‑source tool built with a focus on autonomy, transparency, and offline security. If you find it useful and want to support ongoing development, you can do so through the platforms below:
- Ko‑fi: https://ko-fi.com/lukaszperek
- Buy Me a Coffee: https://buymeacoffee.com/lukaszperek
- AirTM: https://airtm.me/lukper
1 maintainer

Metadata
1 maintainer
Release files for desktop-2fa 0.8.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| desktop_2fa-0.8.2.tar.gz | 337.2 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| desktop_2fa-0.8.2-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 376.4 kB
Release files / desktop_2fa-0.8.2.tar.gz
| Download URL | desktop_2fa-0.8.2.tar.gz |
|---|---|
| Size | 337.2 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
bb453216b3881016541a555ce6a0c36b810db051f767ee150ee7d4a604c7e3a7
|
|
BLAKE2b-256 checksum How to use checksums |
b0604710a09265a7f24c6ddf6fd8fe37e713508aab990023f903c7e616103d58
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.15
|
Release files / desktop_2fa-0.8.2-py3-none-any.whl
| Download URL | desktop_2fa-0.8.2-py3-none-any.whl |
|---|---|
| Size | 39.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
54e17d3d550be07f4ca0a5134d8097bbce220433a0ae8a1cd63311fc67b9bb6d
|
|
BLAKE2b-256 checksum How to use checksums |
3fc6d6fdc6d1e2fdb73907e4bb97c75c30e046c5a108e9e09021f9f934322cf2
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.15
|
Security for desktop-2fa 0.8.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














