
deviant-scan
Find the one thing in your code that breaks the pattern.
Deviant learns your project's own conventions, flags the exceptions, and shows the git history you need to judge them. You write no rules, and finding the exceptions needs no AI, no API key and no network.
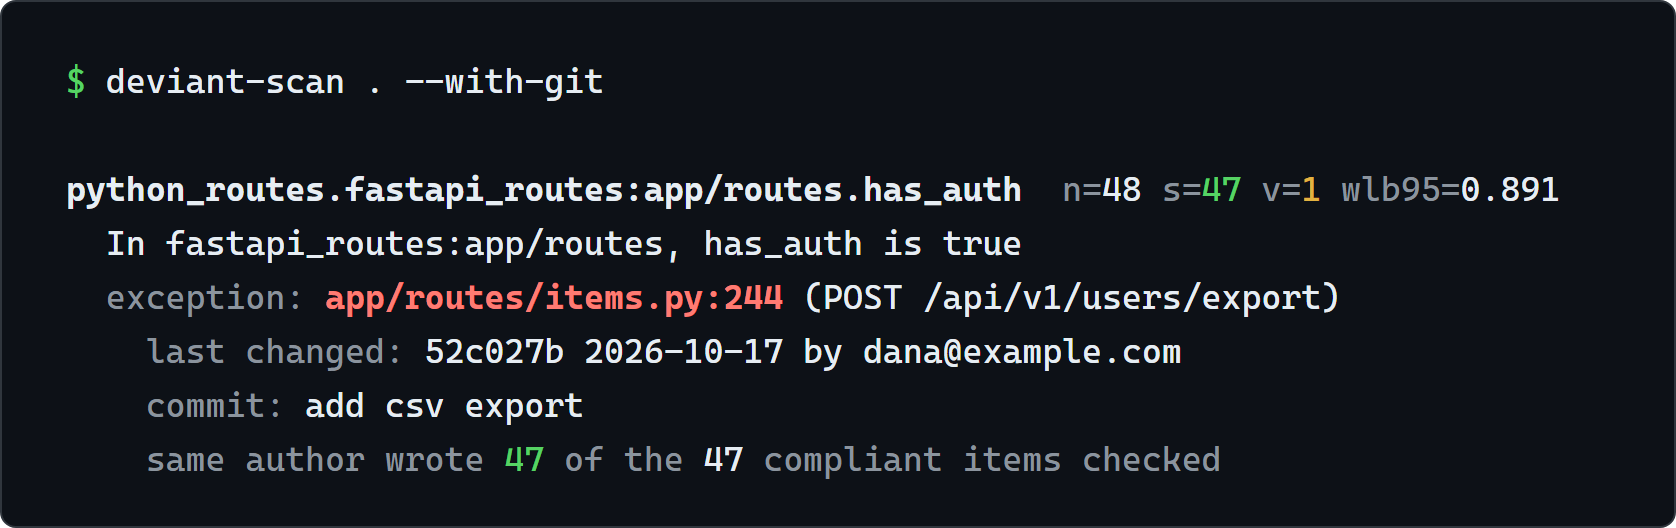
47 of your 48 API routes check who is calling. The 48th doesn't, and it exports every user's data. Nobody noticed. Deviant counts what your code already does, picks out the rare item that breaks the pattern, and shows the git history behind it.
Use it
pip install deviant-scan
deviant-scan path/to/your/project --with-git
Or without installing it: uvx deviant-scan path/to/your/project --with-git.
It checks FastAPI routes and GitHub Actions workflows today. Add --json for machine-readable
output. Everything runs on your machine. It reads your files and never runs your code.
In Claude Code
A plugin judges each exception as a bug, intentional or unsure, with proof:
/plugin install deviant --marketplace ImalkaPerera/deviant
Learn more
MIT licence.
1 maintainer

Metadata
1 maintainer
Release files for deviant-scan 0.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| deviant_scan-0.1.0.tar.gz | 43.5 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| deviant_scan-0.1.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 70.0 kB
Release files / deviant_scan-0.1.0.tar.gz
| Download URL | deviant_scan-0.1.0.tar.gz |
|---|---|
| Size | 43.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
fb1ae189f2fb6c2b273bde9ab7a97af0219324018e86e85692ca7c99a114bab6
|
|
BLAKE2b-256 checksum How to use checksums |
596b46a783426ea8c382a35e35f82b7d190e351a3c0224fd2a3bf659a9b59b27
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 17, 2026.
Transparency logRelease files / deviant_scan-0.1.0-py3-none-any.whl
| Download URL | deviant_scan-0.1.0-py3-none-any.whl |
|---|---|
| Size | 26.5 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
09b7e4b62083eeb69baa8b24b957f06ae7d783aa8e45c4758c4fd5a94291b532
|
|
BLAKE2b-256 checksum How to use checksums |
ab7a60cace79af53a7f43831963ec33e172338a12caec7529f0cb2569d8c28ac
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 17, 2026.
Transparency log












