
Duckle
Local-first ETL/ELT pipelines that run on DuckDB. Python builds the plan, DuckDB moves the rows. Your data never leaves the machine.



Build your first pipeline
Paste this into Claude Code, Cursor, or Codex. The agent does the rest.
Run
uvx duckle quickstartto build my first pipeline and run it
Nothing to install first. The agent fetches Duckle and the DuckDB engine on demand, runs a real pipeline, and shows you the rows.
Prefer to drive it yourself:
uvx duckle quickstart      # no install
pip install duckle         # or install it
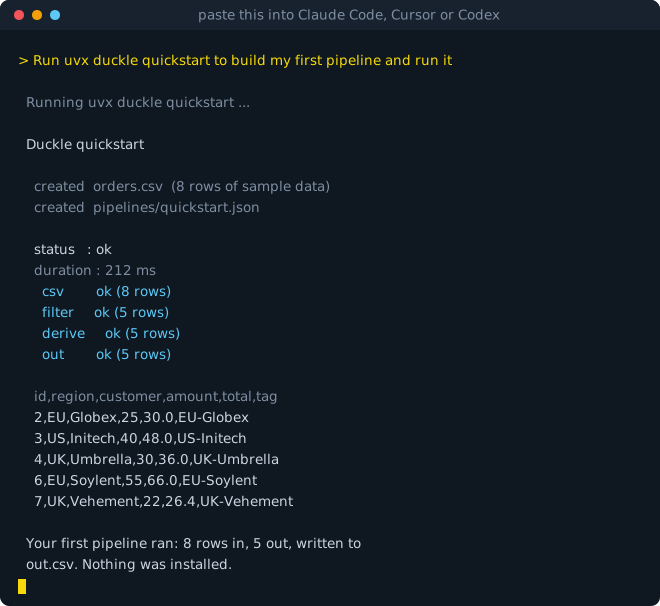
quickstart scaffolds sample data and a pipeline, runs it, and shows you the rows. One command from nothing to a result, because the engine comes with it: a ~20 MB native binary plus the DuckDB CLI. No JVM, no Docker, no server, no account.
Or install it
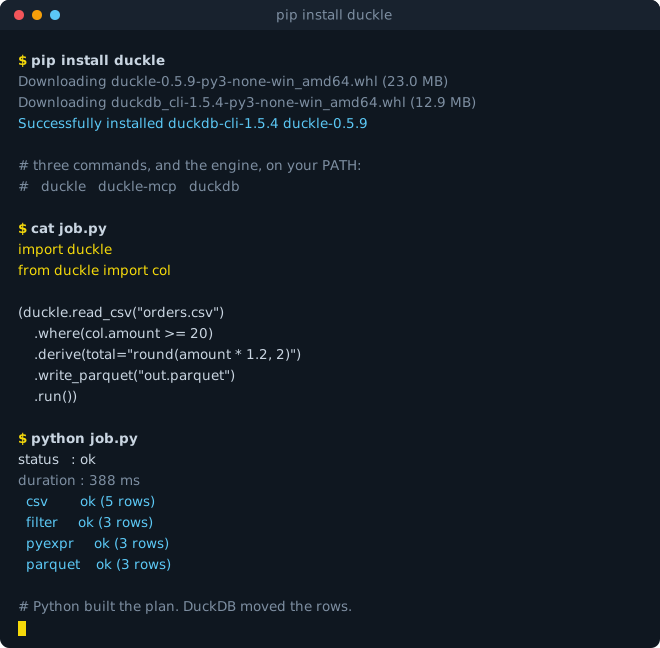
Where uvx is for trying it, pip is for keeping it: a persistent duckle command, duckle-mcp for agents, and import duckle in Python.
No data passes through Python
Every method appends a node to a pipeline graph. Nothing executes until .run(), and then the whole graph is handed to the engine, compiled to SQL, and executed inside DuckDB.
That is the difference from a dataframe library: a billion-row job costs what the SQL costs, because it is SQL. There is no interpreter in the data path, and no to_pandas() escape hatch quietly pulling rows into memory.
import duckle
from duckle import col

(duckle.read_csv("orders.csv")
    .where(col.amount >= 20)
    .derive(total="round(amount * 1.2, 2)", tag="f'{region}-{id}'")
    .write_parquet("out.parquet")
    .run())
Python expressions, compiled to SQL
amount * 1.2, f'{a}-{b}', x if c else y, name.strip().upper() and email is None are translated to vectorized DuckDB SQL at plan time:
.derive(band="'high' if amount > 50 else 'low'")
# CASE WHEN ("amount" > 50) THEN 'high' ELSE 'low' END
An expression with no exact SQL equivalent is rejected with the construct named, never quietly executed somewhere slower. Comprehensions, lambda, indexing and eval are refused by name.
Prefer editor completion over strings? col builds the same tree with real operators, and fragments are reusable:
eu_only = col.region.isin(["EU", "UK"])
p.where(eu_only & (col.amount >= 20))
See exactly what will run, before it runs:
p.explain() # prints the compiled SQL, one block per stage
360+ components, not 10 file formats
Component ids map onto attribute paths, so anything in the catalog is reachable:
duckle.src.salesforce(object="Account", authMode="clientCredentials")
duckle.xf.geo.reproject(geomColumn="geom", targetCrs="EPSG:3857")
duckle.snk.salesforce.bulk(operation="upsert", externalIdField="Ext__c")
104 sources, 66 sinks and 138 transforms: Postgres, MySQL, Oracle, SQL Server, Snowflake, Databricks, Teradata, SAP OData, Salesforce (including Bulk API 2.0), Kafka, WebSocket, S3, SFTP, IMAP, LanceDB and more.
duckle.component_ids(contains="salesforce")
duckle.describe("snk.salesforce.bulk")   # settings, and which ones the engine ignores
A CI gate that needs no engine
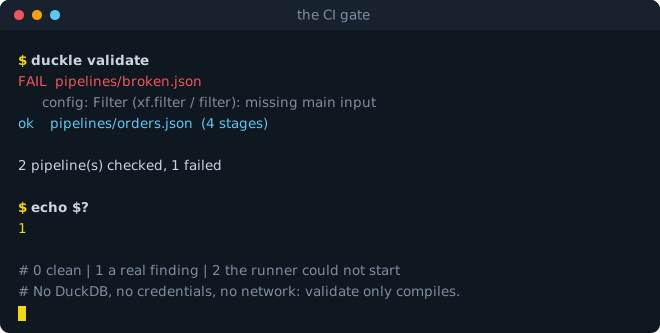
duckle validate compiles every pipeline without opening a source or writing a sink, so it needs no DuckDB, no credentials and no network. Exit codes are stable and safe to gate on:
| code | meaning |
|---|---|
0 |
clean |
1 |
a real finding: a pipeline failed, or did not compile |
2 |
the runner could not start: bad usage, missing engine |
duckle validate --json          # machine-readable, for a build step
duckle --pipeline my.json       # run one
Note: validate does not yet catch every missing required property, so a clean validate is not proof that a run will succeed.
Agent-ready, with nothing installed
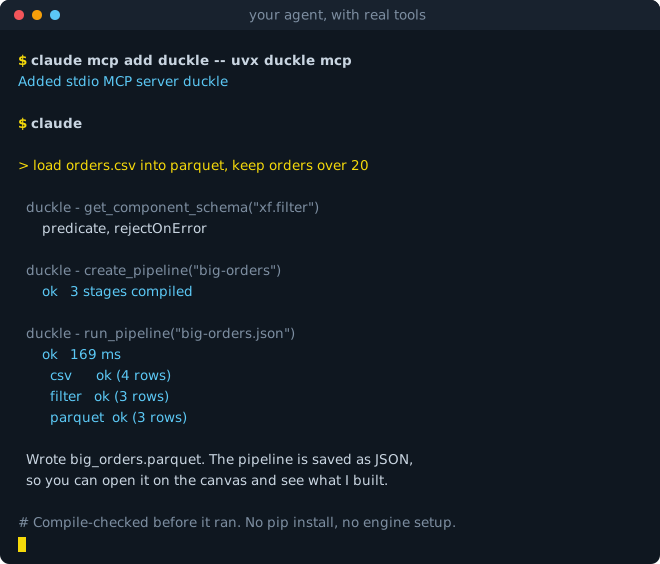
The same package is an MCP server, so an AI agent gets a governed way to work with data instead of a shell. Point Claude Code, Claude Desktop or Cursor at it:
{ "mcpServers": { "duckle": { "command": "uvx", "args": ["duckle", "mcp"] } } }
Or in Claude Code:
claude mcp add duckle -- uvx duckle mcp
That is the whole setup. No pip install, no PATH, no engine to configure: uv fetches the package and the DuckDB engine into a throwaway environment and the server finds it there. If you did pip install duckle, "command": "duckle", "args": ["mcp"] works the same way.
19 tools, including list_components, get_component_schema, create_pipeline, validate_pipeline, run_pipeline, pipeline_lineage, trust_report and schema_drift.
What that buys over letting an agent write a script: it can discover a real connector rather than guess one, compile-check a pipeline before anything executes, run it, and get column-level lineage back. validate_pipeline opens no source and writes no sink, so an agent can check its work without touching your data. The pipeline it produces is the same JSON your desktop canvas opens, so you can inspect what it built.
Code and canvas are the same file
Pipelines are the same JSON the Duckle desktop studio reads. A pipeline written in Python opens on the canvas, and one drawn on the canvas runs from Python:
p.save("pipelines/orders.json")          # opens in the studio
duckle.from_json("pipelines/orders.json").run()
Install notes
duckle depends on duckdb-cli, published by the DuckDB Foundation, so the engine arrives with the install and works offline. To pin your own build instead, set DUCKLE_DUCKDB_BIN.
Wheels ship for Linux, macOS and Windows on x86-64 and arm64. The wheel carries a compiled Rust binary and is Python-version independent (py3-none-<platform>).
Apache-2.0 · GitHub · duckle.org · Issues
1 maintainer

Metadata
1 maintainer
Release files for duckle 0.7.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Built distributions (wheels)
| File | Reset | |||
|---|---|---|---|---|
| duckle-0.7.1-py3-none-win_arm64.whl | Python 3 | none | Windows ARM64 | Details |
| duckle-0.7.1-py3-none-win_amd64.whl | Python 3 | none | Windows x86-64 | Details |
| duckle-0.7.1-py3-none-manylinux2014_x86_64.manylinux_2_17_x86_64.whl | Python 3 | none | Linux glibc 2.17+ x86-64 | Details |
| duckle-0.7.1-py3-none-manylinux2014_aarch64.manylinux_2_17_aarch64.whl | Python 3 | none | Linux glibc 2.17+ ARM64 | Details |
| duckle-0.7.1-py3-none-macosx_11_0_x86_64.whl | Python 3 | none | macOS 11.0+ x86-64 | Details |
| duckle-0.7.1-py3-none-macosx_11_0_arm64.whl | Python 3 | none | macOS 11.0+ ARM64 | Details |
Total release size: 158.2 MB
Release files / duckle-0.7.1-py3-none-win_arm64.whl
| Download URL | duckle-0.7.1-py3-none-win_arm64.whl |
|---|---|
| Size | 26.3 MB |
| Tags | Python 3 Windows ARM64 |
|
SHA-256 checksum How to use checksums |
b1922603509b8235825d91ea3e9f0653586955a10ae03c9a1b1c8d99097ca237
|
|
BLAKE2b-256 checksum How to use checksums |
c49e8ff2745eed64b89113629a9911d974ac9b7bf55681badabeab64fe679c4f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 30, 2026.
Transparency logRelease files / duckle-0.7.1-py3-none-win_amd64.whl
| Download URL | duckle-0.7.1-py3-none-win_amd64.whl |
|---|---|
| Size | 27.6 MB |
| Tags | Python 3 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
74d717f9f63717fd936b7fadae8a93d114f94dd76ec5f46f92f74d7e2b06a64d
|
|
BLAKE2b-256 checksum How to use checksums |
05a193a62eb62cf36dae6e7d75e0f3d9ee9532c2613d1f8191cc68eb087435ad
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 30, 2026.
Transparency logRelease files / duckle-0.7.1-py3-none-manylinux2014_x86_64.manylinux_2_17_x86_64.whl
| Download URL | duckle-0.7.1-py3-none-manylinux2014_x86_64.manylinux_2_17_x86_64.whl |
|---|---|
| Size | 27.7 MB |
| Tags | Linux glibc 2.17+ x86-64 Python 3 |
|
SHA-256 checksum How to use checksums |
e8e0a1f1f98a3e228ca140def9d2e0365f66fe43d4b132563a0a3a111d6c86a9
|
|
BLAKE2b-256 checksum How to use checksums |
8ea33a4f5a5dece5d7a3def0397d7fd1d18974503fc4a3bfe3fae9edb424082a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 30, 2026.
Transparency logRelease files / duckle-0.7.1-py3-none-manylinux2014_aarch64.manylinux_2_17_aarch64.whl
| Download URL | duckle-0.7.1-py3-none-manylinux2014_aarch64.manylinux_2_17_aarch64.whl |
|---|---|
| Size | 26.6 MB |
| Tags | Linux glibc 2.17+ ARM64 Python 3 |
|
SHA-256 checksum How to use checksums |
ba5a9b08bf21788597cd7f954dba7566f9c25fc0e49b6e3e1bec1845f3b88e58
|
|
BLAKE2b-256 checksum How to use checksums |
1b57c3b4dec3eb1af608b5d4f377da32a1df6eaec85420a711e898bd8f555959
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 30, 2026.
Transparency logRelease files / duckle-0.7.1-py3-none-macosx_11_0_x86_64.whl
| Download URL | duckle-0.7.1-py3-none-macosx_11_0_x86_64.whl |
|---|---|
| Size | 25.6 MB |
| Tags | Python 3 macOS 11.0+ x86-64 |
|
SHA-256 checksum How to use checksums |
f14913dfb93ca12e37392c39feada52dd022b5b3b2e36dcadd7ec5b374bf508e
|
|
BLAKE2b-256 checksum How to use checksums |
ec2f114feb8a9db1edd5c3da056ff8f38cb60ce63a078d7cd6f64e66b2fbb82b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 30, 2026.
Transparency logRelease files / duckle-0.7.1-py3-none-macosx_11_0_arm64.whl
| Download URL | duckle-0.7.1-py3-none-macosx_11_0_arm64.whl |
|---|---|
| Size | 24.5 MB |
| Tags | Python 3 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
5dd6da4beb7ee7c932129766e404a5294bbc8400eeb0a16c6469b1705b1f0657
|
|
BLAKE2b-256 checksum How to use checksums |
3ff9e1458bf424a431b41355b98e26d8efb1268d6cd43d3de1c9eb1470f18e80
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 30, 2026.
Transparency log













