
Dynamic Systems Testing Framework (DSTF)
DSTF is regression and unit testing for the behaviour of time-dependent systems: Modelica libraries, FMUs, Julia models, or anything Python can compute. It finds a library's tests, simulates them with a backend — Dymola, OpenModelica, FMPy, Julia or Python, or one a plug-in adds — and scores each result against a stored baseline by the criteria you write. It reports a verdict per test on the command line, as JUnit XML for CI, and as a dashboard and a page per test in the browser.
DSTF is in beta: the command line and the testing.json keys may still change between minor versions; the changelog says when.
Install
$ uv tool install dynamic-systems-testing-framework
or pipx install dynamic-systems-testing-framework. The command is dstf.
The author extra adds dstf author, a browser tool for writing criteria
beside the plots they score; fmpy and om add what the FMPy and
OpenModelica backends drive.
A first run
The Python example library needs no simulator. From a clone of this repository, in a Python environment with numpy and scipy:
$ git clone https://github.com/ORNL-Modelica/DynamicSystemsTestingFramework.git
$ cd DynamicSystemsTestingFramework
$ python3 -m pip install numpy scipy
$ dstf --config examples/python/PythonTestingLib/Resources/ReferenceResults/testing.json run
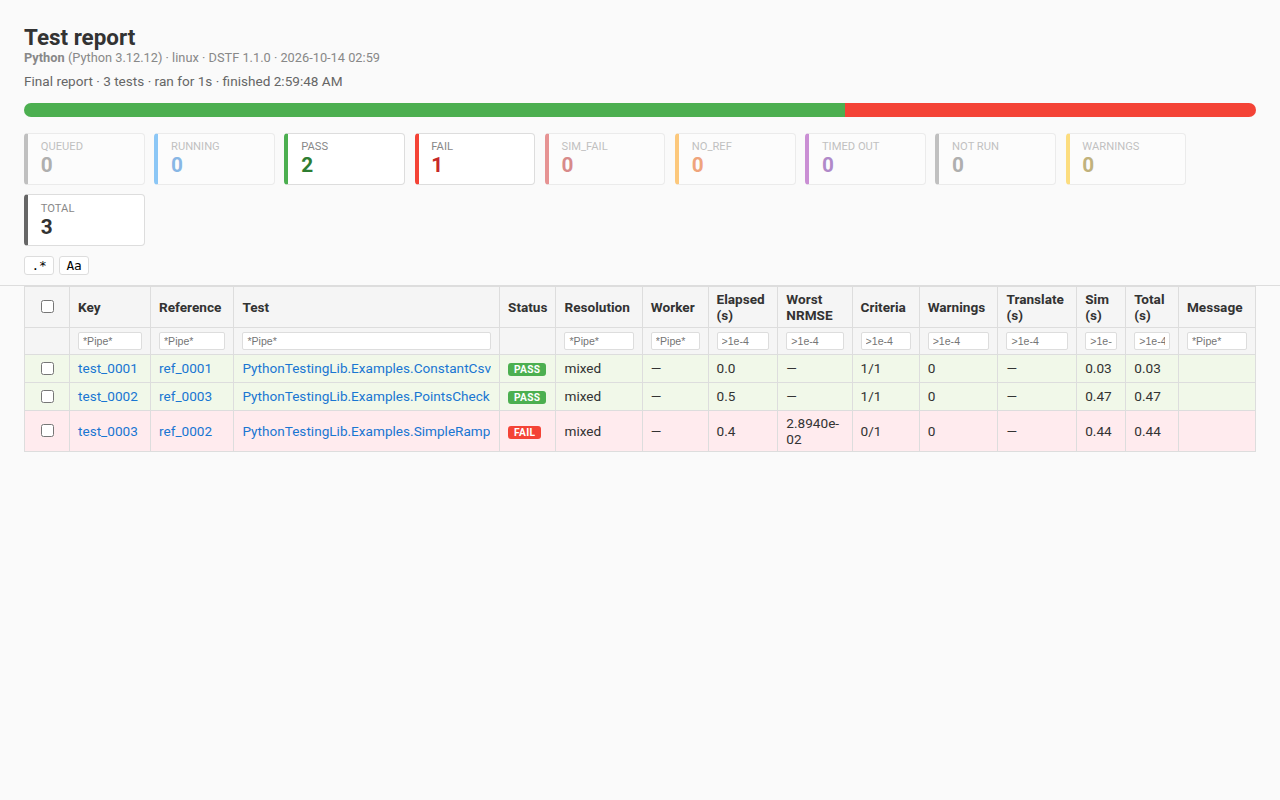
It runs three tests, compares each with its stored baseline, prints a verdict per test and opens the dashboard:
Documentation
https://dstf.readthedocs.io/ — a first run, setting up testing.json for
your library, adding tests, reading results, baselines, criteria, CI, a page
per simulator, writing a backend plug-in, and a reference of every command,
key and comparison mode.
Changelog and licence
What changed in each version is in CHANGELOG.md. DSTF is released under the MIT licence: LICENSE.
1 maintainer

Metadata
1 maintainer
Release files for dynamic-systems-testing-framework 1.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| dynamic_systems_testing_framework-1.1.0.tar.gz | 1.3 MB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| dynamic_systems_testing_framework-1.1.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 2.8 MB
Release files / dynamic_systems_testing_framework-1.1.0.tar.gz
| Download URL | dynamic_systems_testing_framework-1.1.0.tar.gz |
|---|---|
| Size | 1.3 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
737660e63a18e5e5c78e00c77a31a0ed354ae42f500a4ff71c33e7f456f766f3
|
|
BLAKE2b-256 checksum How to use checksums |
a4230a5b19c97f7bf8f4a9b3a43759a981b53ce79da38c5e838ea45056c939ae
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 15, 2026.
Transparency logRelease files / dynamic_systems_testing_framework-1.1.0-py3-none-any.whl
| Download URL | dynamic_systems_testing_framework-1.1.0-py3-none-any.whl |
|---|---|
| Size | 1.4 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
0ab18c53083c15ec74016222dfbd9622f8240267cfd538fa43227ba49f740152
|
|
BLAKE2b-256 checksum How to use checksums |
48302d6248f522fbb3121ff9ffc4bb6a6abc509bc5c9888599500079f882128b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 15, 2026.
Transparency log













