
A local Git dashboard for people juggling agents and too many repos.
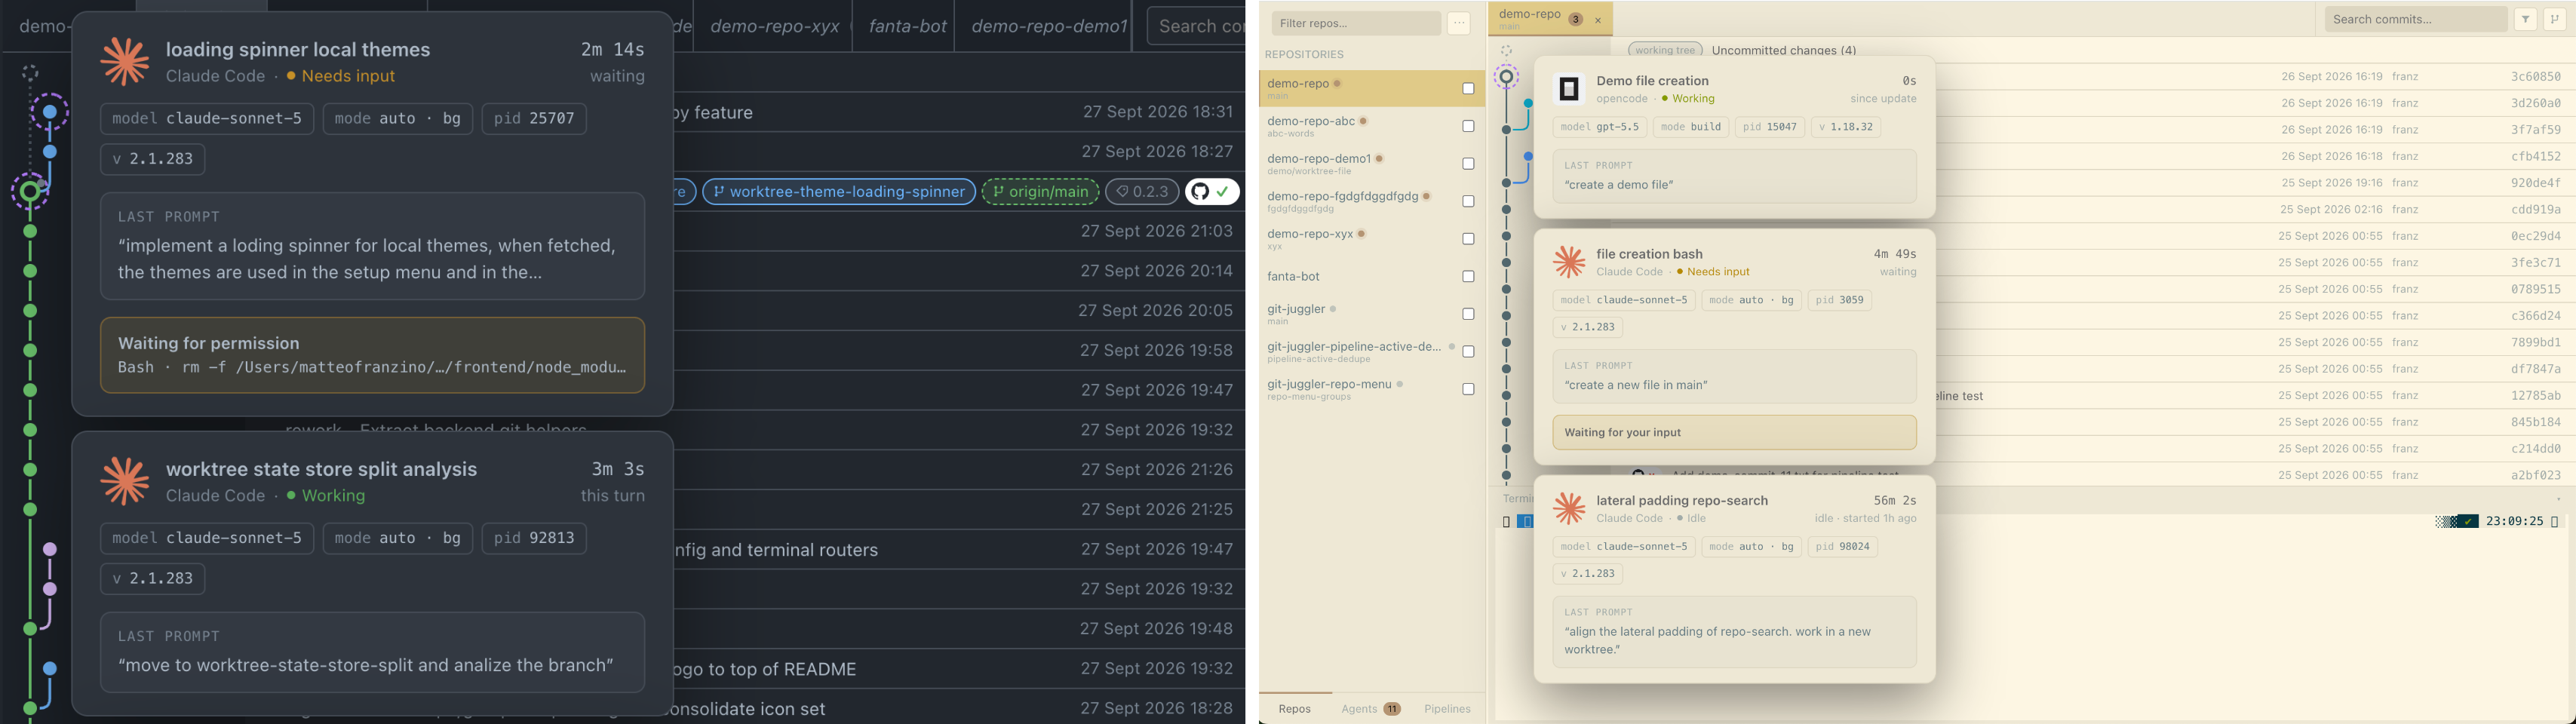
Watch agents work live, follow every repo’s git graph, and catch what changed across your workspace — all from one place, without opening a dozen editors.
What it does
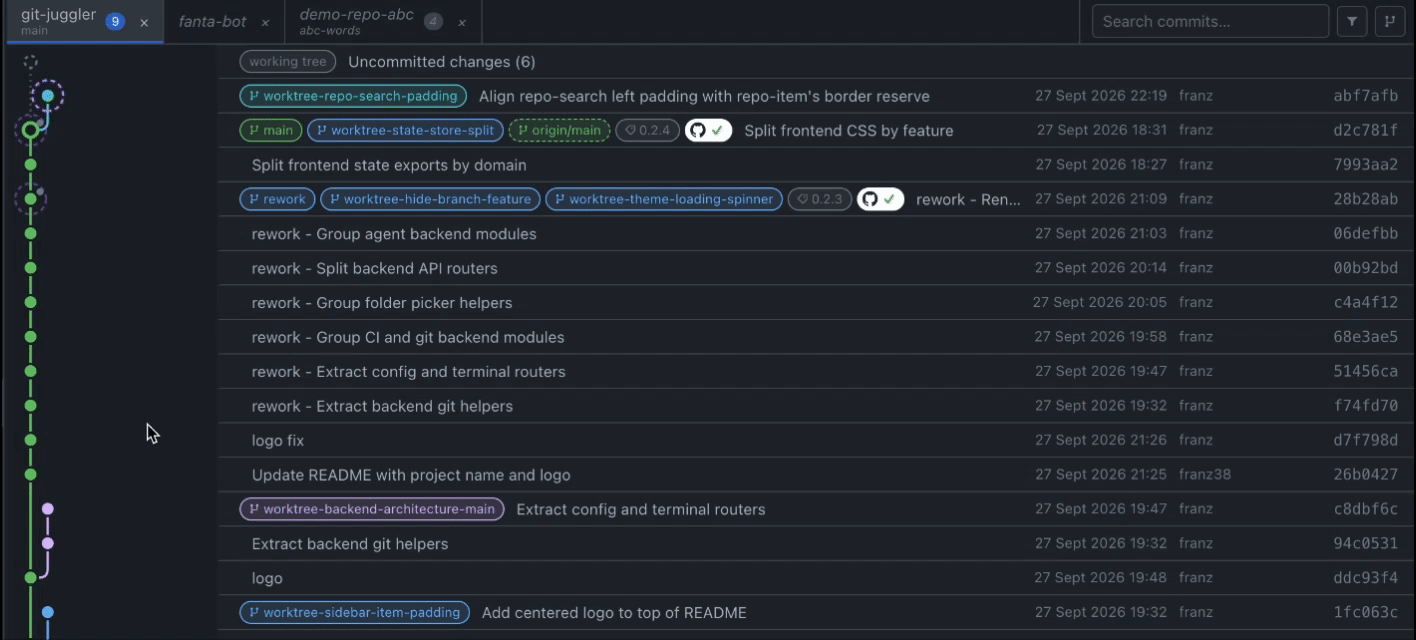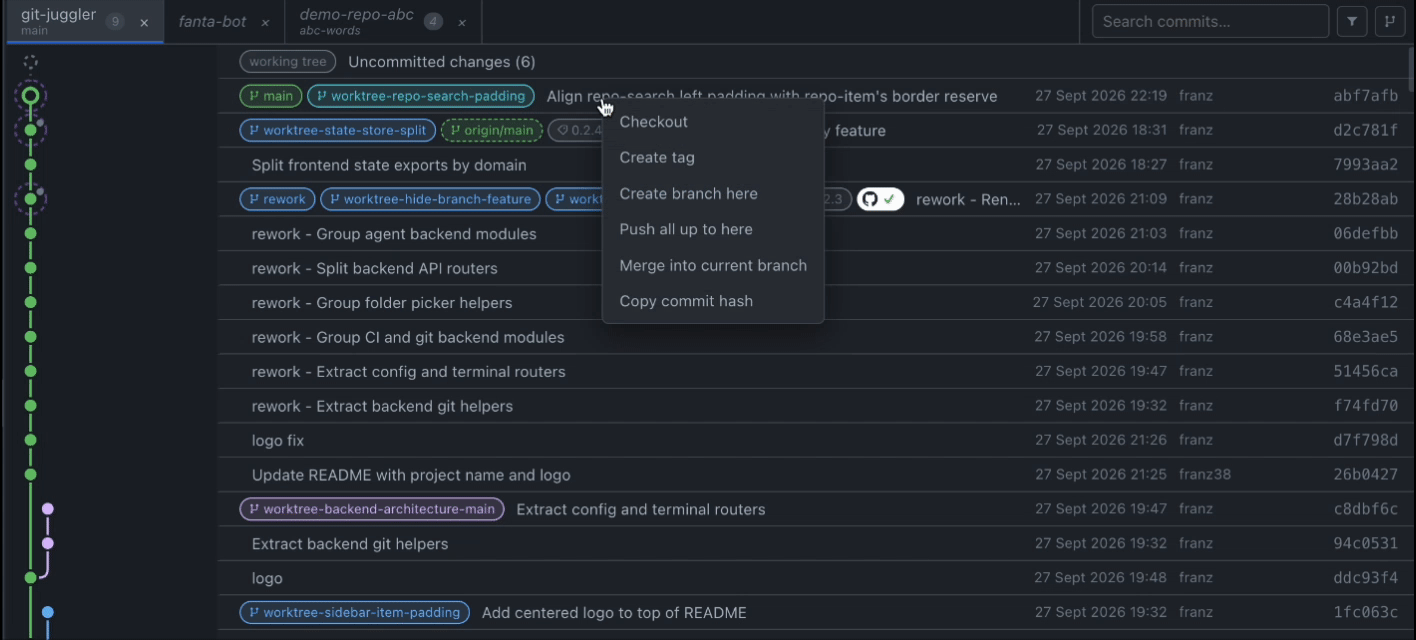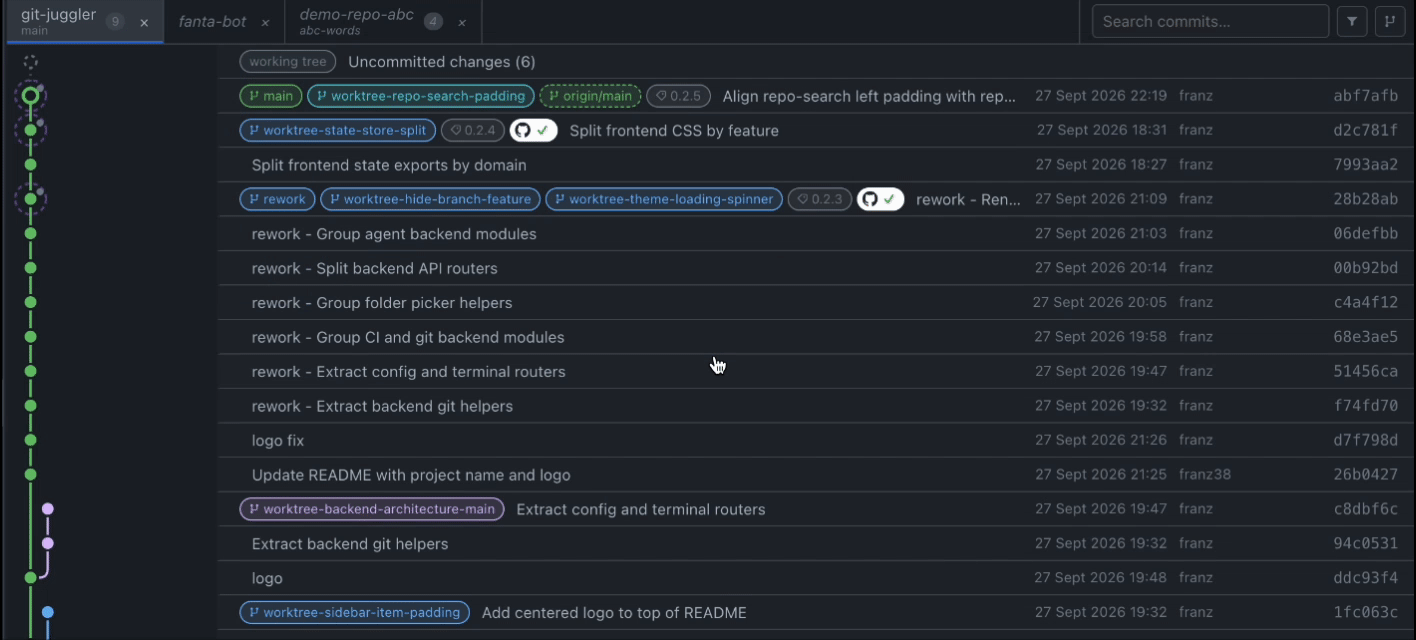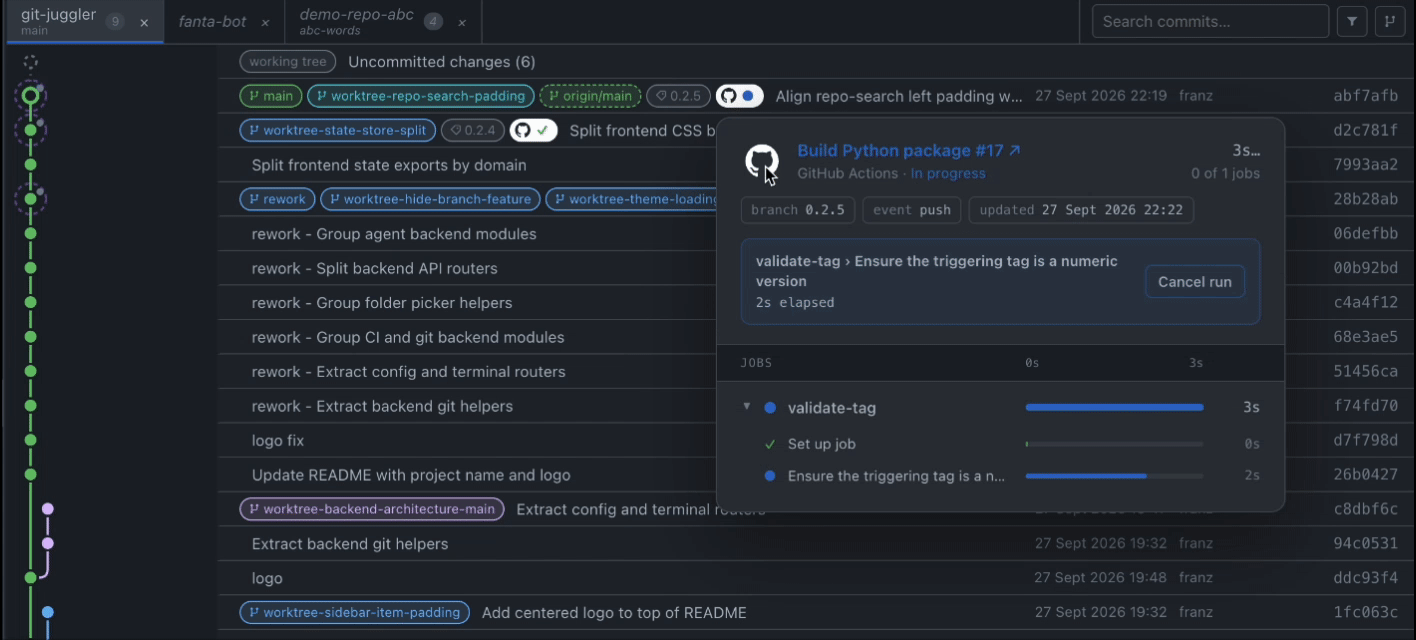
- Scans the immediate children of one or more configured folders for Git repos.
- Lets you inspect and manage each repo's graph, branches, tags, stashes, dirty files, and file diffs.
- Keeps a persistent terminal per open repo and runs Git actions there so you see the real commands and output.
- Tracks local Claude Code and OpenCode sessions.
- Connects GitHub Actions and Jenkins runs to commits and active pipelines.
- VS Code-compatible themes.
Privacy / local-first
- Runs locally and binds to
127.0.0.1by default. - No telemetry or analytics are built in, and none are planned.
- Repo scanning and Claude/OpenCode session tracking read local files on your machine.
- Git mutations run through visible terminal commands, so you can see the exact command and output.
- Network requests are only used for features you configure, such as CI integrations.
How to install
git-juggler is published on PyPI. The recommended way to install it is with
pipx, which puts the git-juggler command on your
PATH in its own isolated environment, without touching your system Python:
pipx install git-juggler
git-juggler [path-to-scan] [--host HOST] [--port PORT] [--no-open]
<path-to-scan> is optional and defaults to the current directory. It is used
to seed the initial search path; after that, search paths are managed in the app
from the welcome wizard or Settings.
--host HOSTchanges the bind host from the default127.0.0.1.--port PORTchanges the backend port from the default8788.--no-opendisables opening the app in your browser automatically.
If you don't have pipx yet:
macOS
brew install pipx
pipx ensurepath
Linux
sudo apt install pipx   # Debian/Ubuntu
sudo dnf install pipx   # Fedora
pipx ensurepath
Many recent distros (like macOS with Homebrew) block a plain global
pip install outside a virtual environment (PEP 668); pipx is the
supported way around that.
Windows
py -m pip install --user pipx
py -m pipx ensurepath
Restart your terminal after ensurepath so the updated PATH takes effect.
To upgrade later: pipx upgrade git-juggler.
Dev mode
Use the dev script to start both the backend and frontend dev servers:
./scripts/dev.sh [path-to-scan] [--port PORT] [--no-open]
- The frontend toolchain requires Node
^20.19.0or>=22.12.0. path-to-scanis optional. On first run, it seeds the folder whose immediate children are scanned for Git repos.--port PORTis optional. It changes the backend port from the default8788; the dev script passes the selected port to Vite automatically.--no-opendisables opening the app in your browser automatically.
Or run them manually in two terminals:
python3 -m venv .venv
.venv/bin/pip install -e .
.venv/bin/git-juggler <path-to-scan> --reload [--no-open]
cd src/frontend
npm install
npm run dev                                     # http://localhost:5173 (proxies /api and /ws to :8788)
Open http://localhost:5173.
By default, ./scripts/dev.sh opens http://localhost:5173 in your browser.
Production (single port)
cd src/frontend && npm install && npm run build
cd ../.. && .venv/bin/git-juggler <path-to-scan> [--no-open]
The backend serves the built frontend in this mode, so only port 8788 is needed. By default, it opens the app in your browser.
Build a Python package
The Python wheel includes the built frontend assets. The generated assets are
not committed; scripts/build-package.sh builds them and copies them into the
backend package before creating the distributions.
python3 -m venv .venv
.venv/bin/pip install build
./scripts/build-package.sh
The wheel and source distribution are written to dist/.
Install the wheel locally with:
pipx install dist/git_juggler-*.whl --force
git-juggler <path-to-scan> [--no-open]
Versions are derived from Git tags. GitHub Actions runs the same build, uploads the distributions as artifacts, and publishes tagged releases to PyPI.
1 maintainer

Metadata
1 maintainer
Release files for git-juggler 0.2.18
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| git_juggler-0.2.18.tar.gz | 5.6 MB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| git_juggler-0.2.18-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 6.0 MB
Release files / git_juggler-0.2.18.tar.gz
| Download URL | git_juggler-0.2.18.tar.gz |
|---|---|
| Size | 5.6 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
967eab03716541ecf6d97e727e84f6f68e34bc4fa7f5cb72a1412a74afbbf71c
|
|
BLAKE2b-256 checksum How to use checksums |
3b4cd80858551a65b8ff3ac53170ca83881dfbe8630ee45b5caeeb6c83389cb0
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logRelease files / git_juggler-0.2.18-py3-none-any.whl
| Download URL | git_juggler-0.2.18-py3-none-any.whl |
|---|---|
| Size | 434.4 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
3a4fdb20d5cd76430d9b8cfdbc76323b52edd7c9f2b97508516a068d7b474eaf
|
|
BLAKE2b-256 checksum How to use checksums |
7289cfa6068bcf222593ba1e5e301a526dfc8467e00dd14443d1733c83aaee02
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logSecurity for git-juggler 0.2.18
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for git_juggler-0.2.18.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














