
githubtakeout
Backup and archive Git Repos and Gists from GitHub
- Copyright (c) 2015-2026 Corey Goldberg
| Development | GitHub |
| License | MIT |
| Releases |

|
| Supported Python Versions |
|
About:
githubtakeout is a data export tool for backing up and archiving Git
repositories hosted on GitHub. It clones a user's repos and creates an archive
of each.
It supports public/private repos and public/secret gists. By default, it
doesn't save commit history or branches (.git directory), or Gist
repositories (both can be enabled with command line options).
When you run the program, archives of your repos will be saved in a directory
named backups inside your current working directory, unless a different
location is specified using the --dir option.
Archives are saved in compressed zip format (.zip) by default. You can also
save as tarballs (.tar.gz) using the --format=tar option, or skip archiving
using the --format=none option.
If a repo with history exists from a previous run, it will pull new changes.
Otherwise, it will clone the repo. Use the --keep if you don't want repos
deleted after an archive is created.
Requirements:
- Python 3.12+
- Git 1.7+
Installation:
Install from PyPI:
pip install githubtakeout
Authentication:
By default, githubtakeout will only retrieve an account's public repos. To
access private repos and secret gists, you need to authenticate.
First, you must create a
personal access token
on Github (either a fine-grained or classic personal access token). Once you
have a token, you can set the GITHUB_TOKEN environment variable:
$ export GITHUB_TOKEN=<access token>
You can also set this in an .env file in the current directory. It should
contain:
GITHUB_TOKEN=<access token>
If you prefer to be prompted for your token each time you run the program, use
the --token argument.
CLI Options:
$ githubtakeout --help
usage: githubtakeout [OPTIONS] [username]

Backup and archive Git Repos and Gists from GitHub.

positional arguments:
  username                 github username

options:
  -h, --help               show this help message and exit
  --dir DIR                output directory (default: .)
  --pattern PATTERN        regex matching repo names to include
  --skip_pattern PATTERN   regex matching repo names to skip
  --format {tar,zip,none}  archive format (default: zip)
  --gists                  include gists
  --history                include commit history and branches (.git directory)
  --skip_forks             skip repos that are forks
  --keep                   keep repos after archiving
  --list                   list repos only
  --token                  prompt for auth token
Screenshot:
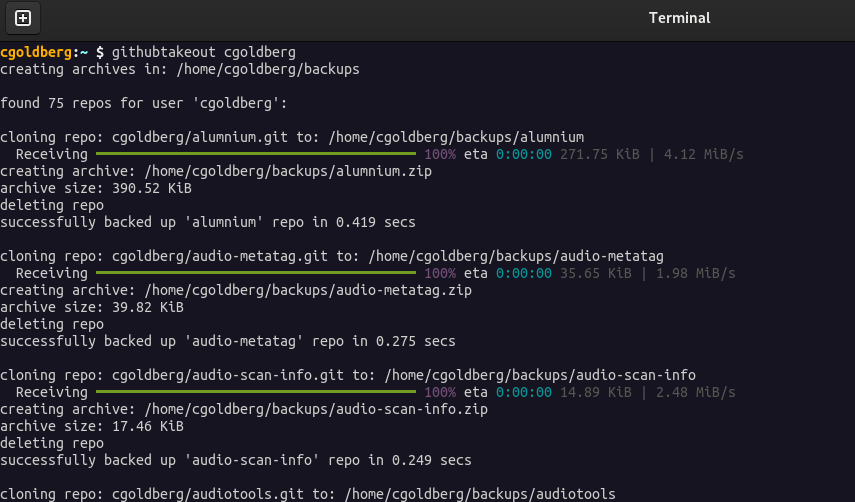
Usage Example:
Install from PyPI with pipx and run:
pipx install githubtakeout
githubtakeout <github username>
1 maintainer

Metadata
1 maintainer
Release files for githubtakeout 0.1.32
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| githubtakeout-0.1.32.tar.gz | 9.1 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| githubtakeout-0.1.32-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 17.7 kB
Release files / githubtakeout-0.1.32.tar.gz
| Download URL | githubtakeout-0.1.32.tar.gz |
|---|---|
| Size | 9.1 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
a65ae48030bf7d2c74a02a15a5c03456d746c56c93b32dda7af9dfff50523a09
|
|
BLAKE2b-256 checksum How to use checksums |
71aeade24f2ff3218dfa922eef62f6aabac75c732e97ed480cd8357804d344b6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 23, 2026.
Transparency logRelease files / githubtakeout-0.1.32-py3-none-any.whl
| Download URL | githubtakeout-0.1.32-py3-none-any.whl |
|---|---|
| Size | 8.6 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
d4a4d76d5146e5a0b431264d14fee7ba54f15cca9a67061fe2e6ad5c34a7d497
|
|
BLAKE2b-256 checksum How to use checksums |
ddf2153c979a360a1862799b87899090e05178a60fb2c7450c8b6465f0374980
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 23, 2026.
Transparency logSecurity for githubtakeout 0.1.32
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for githubtakeout-0.1.32.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 23, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














