
🗜 gitz - git commands for rapid development 🗜
This is a collection of seventeen git utilities aimed at people doing rapid development using Git.
Gitz is for two types of users - quality-obsessed individuals who relentlessly manicure their pull requests until every byte is in the right place; and ultra-rapid developers who want to generate large features quickly while taking advantage of continuous integration.
Most of these utilities only exist here, one came from a chat on Reddit and I don’t know where one of them came from.
Four of them are written in Bash, the rest use Python 3. They have been tested on Mac OS/X (Darwin) and on Ubuntu, and will likely work on any Unix-like operating system.
How to install
Use pip:
pip3 install gitzOr simply download this directory and make sure it’s in your shell’s PATH - gitz has no external dependencies.
Getting help
This page contains a summary and a link to a manual page for each command. From the terminal, use -h flag like this: git new -h or use man like this: man git-new.
When to use gitz
At the start of a session
git new safely creates fresh branches from upstream
git update for each branch, rebases from upstream and force-pushes
During development
git st is a more compact and prettier git status
git when shows you when documents were last changed
During rapid development
git infer commits files with an automatically generated message - great for committing tiny changes for later rebasing down
While cleaning up a branch for review
git permute permutes, squashes or removes commits in the current branch
git split split one or more commits, perhaps with the staging area, into many small individual commits, one per file
During repository maintenance
git rotate rotates through all branches
git copy, git delete, and git rename work on both local and upstream branches
Working with continuous integration
git stripe pushes a sequence of commits to individual remote branches where CI can find and test them
The movie
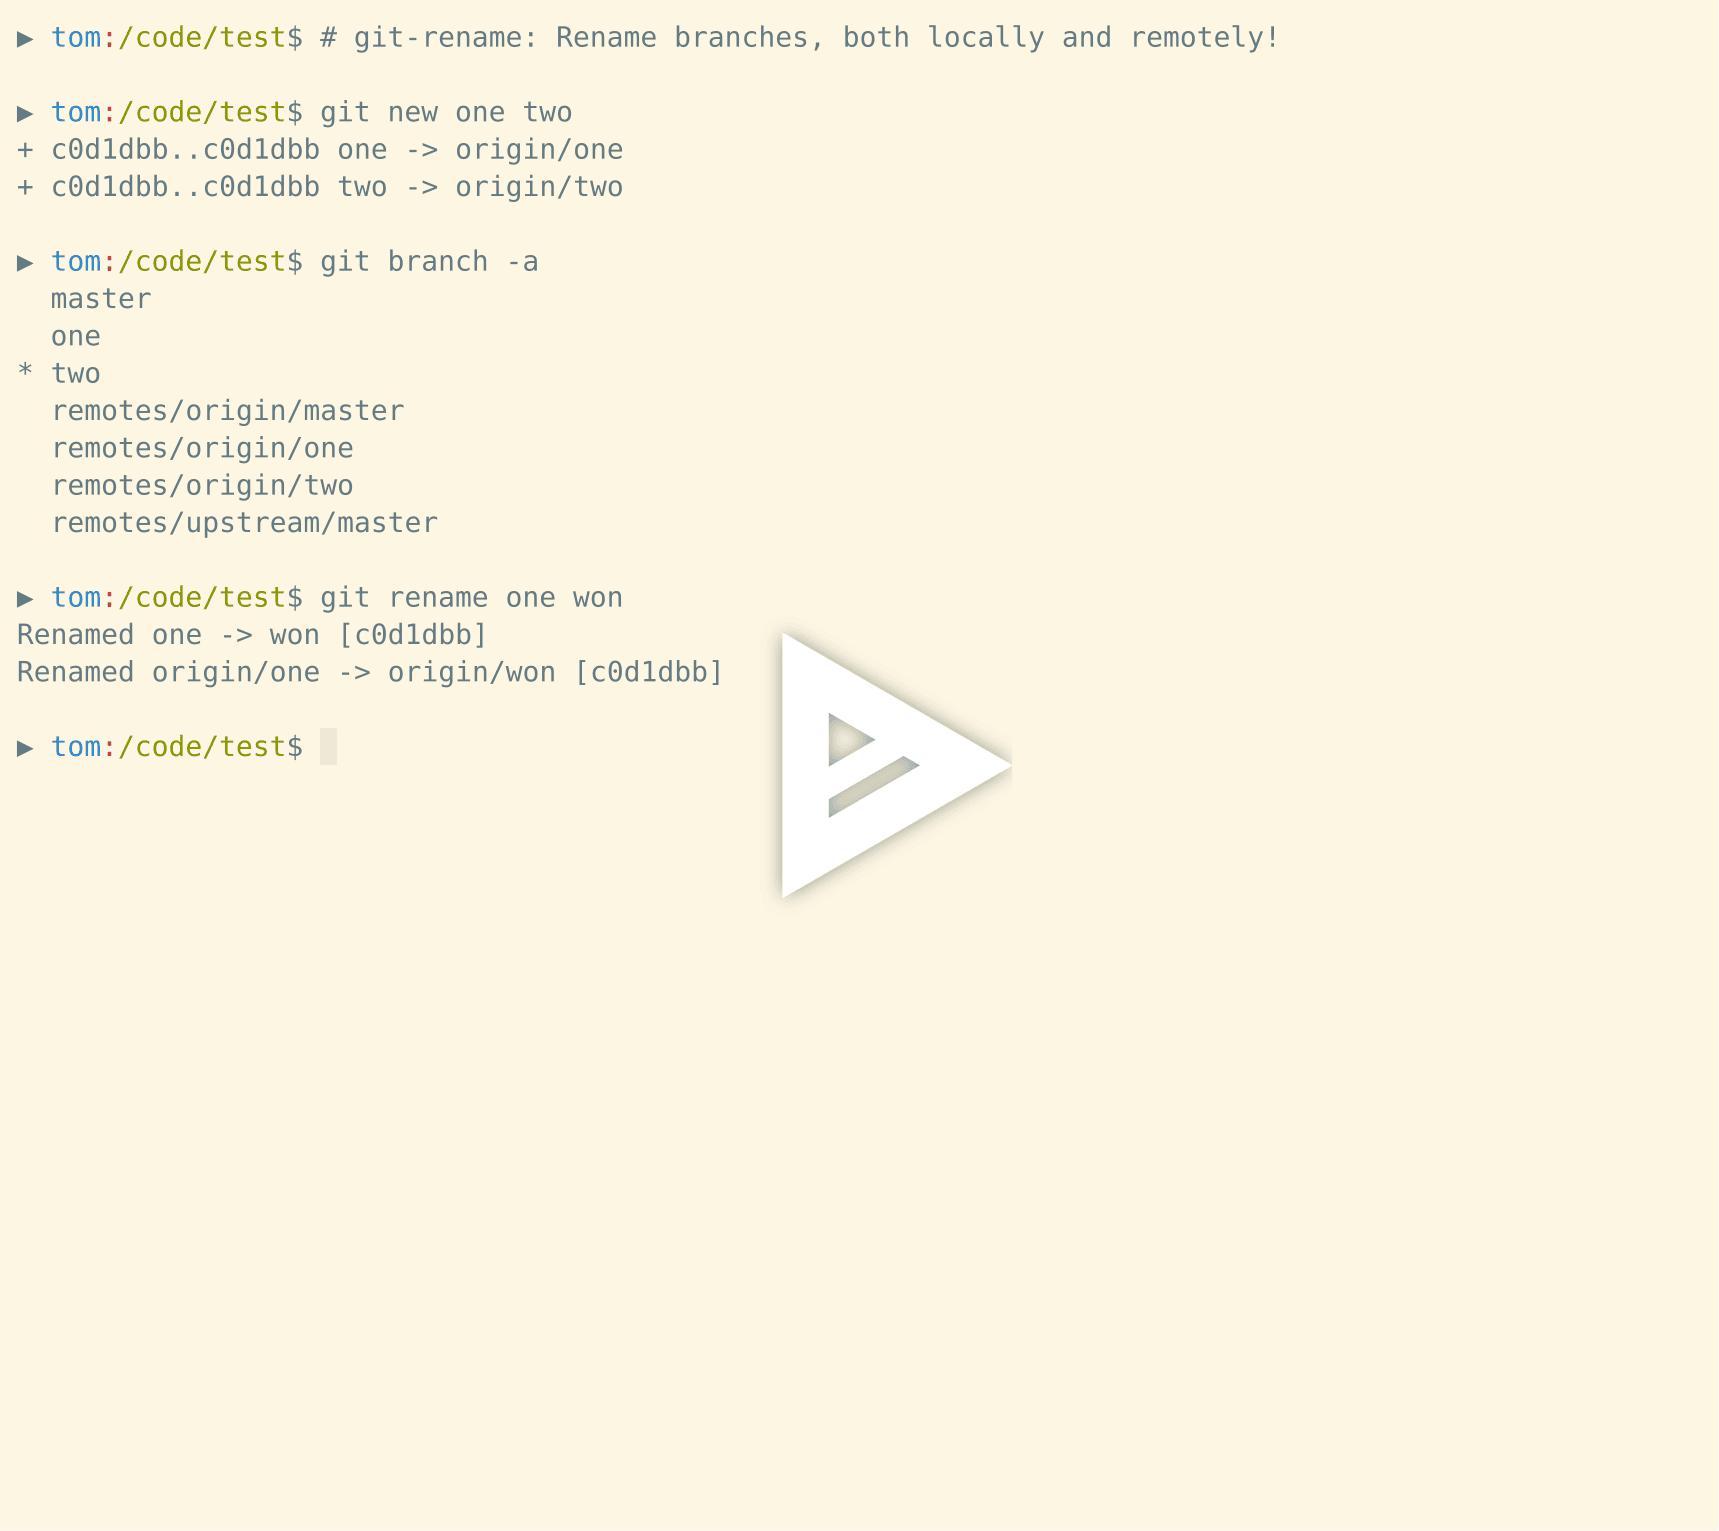
The gitz commands
Safe commands
Informational commands that don’t change your repository
- git gitz
Print information about the gitz git commands
- git go
Open a browser page for the current repo
- git infer
Commit changes with an automatically generated message
- git multi-pick
Cherry-pick multiple commits, with an optional squash
- git new
Create and push new branches
- git rot
Rotate through branches in a Git repository
- git st
Colorful, compact git status
- git stripe
Push a sequence of commit IDs to a remote repository
- git when
For each file, show the most recent commit that changed it.
Dotfiles are ignored by default.
Dangerous commands that delete, rename or overwrite branches
- git copy
Copy a git branch locally and remotely
- git delete
Delete one or more branches locally and remotely
- git rename
Rename a git branch locally and remotely
By default, the branches develop and master are protected - they are not allowed to be copied to, renamed, or deleted.
You can configure this in three ways:
setting the --all/-a flag ignore protected branches entirely
setting the environment variable GITZ_PROTECTED_BRANCHES overrides these defaults
setting a value for the keys PROTECTED_BRANCHES in the file .gitz.json in the top directory of your Git project has the same effect
Dangerous commands that rewrite history
Slice, dice, shuffle and split your commits.
These commands are not intended for use on a shared or production branch, but can significantly speed up rapid development on private branches.
- git adjust
Amend any commit, not just the last
- git permute
Reorder and delete commits in the current branch
- git split
Split a range of commits into many single-file commits
- git update
Update branches from a reference branch
1 maintainer

Metadata
1 maintainer
Release files for gitz 1.9.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| gitz-1.9.0.tar.gz | 894.1 kB | Without provenance | Details for gitz-1.9.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| gitz-1.9.0-py3-none-any.whl | Python 3 | none | any | Details for gitz-1.9.0-py3-none-any.whl |
Total release size: 914.4 kB
Release files / gitz-1.9.0.tar.gz
| Download URL | gitz-1.9.0.tar.gz |
|---|---|
| Size | 894.1 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
b6eddbca08e773900ea2fe0c55ca75b2cd46147ec9327ab4aedf36cd8d35f05b
|
|
BLAKE2b-256 checksum How to use checksums |
5e6ca75e6a2ee4a13e76e2d1c63f5769476d3d0890fa98358ccfc427fedfdecf
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
uv/0.10.12 {"installer":{"name":"uv","version":"0.10.12","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"macOS","version":null,"id":null,"libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":null}
|
Release files / gitz-1.9.0-py3-none-any.whl
| Download URL | gitz-1.9.0-py3-none-any.whl |
|---|---|
| Size | 20.3 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
dfafaadf645f43d023fc204823be6f2812b7c5aff9da4f4a1f439ac1c66bba7c
|
|
BLAKE2b-256 checksum How to use checksums |
11f7733a9a13b953c5e0ad2f8ecc6f7e9a55e4e69a34848236d29e816bccc1aa
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
uv/0.10.12 {"installer":{"name":"uv","version":"0.10.12","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"macOS","version":null,"id":null,"libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":null}
|
Security for gitz 1.9.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














