
This release is a pre-release and may not be stable for production use.
http-faker
介绍
灵活又简单的mock服务
gitee地址: https://gitee.com/guojongg/http-faker
httpfaker基于faker和flask库,提供强大的逻辑处理能力;通过对配置文件(yaml/json)的描述,可返回想要的任意数据。
httpfaker针对返回数据的规则编写灵活,简单。除了可以满足传统的接口mock外,还支持处理业务逻辑,可实现真正的业务功能。
适用于:
- 前端人员: 前后端分离开发,无需等到后台接口实现即可开始进行页面请求
- 测试人员: 提前进行接口测试代码编写;服务未至,用例先行
- 其他需要写一个简单api的人员: 通过yaml文件配置,可减少开发代码;无需关注请求处理部分,只需关注自己的业务逻辑即可。
简单使用
# 安装
pip install httpfaker

# 简单使用
httpfaker init
cd httpfaker-project
httpfaker
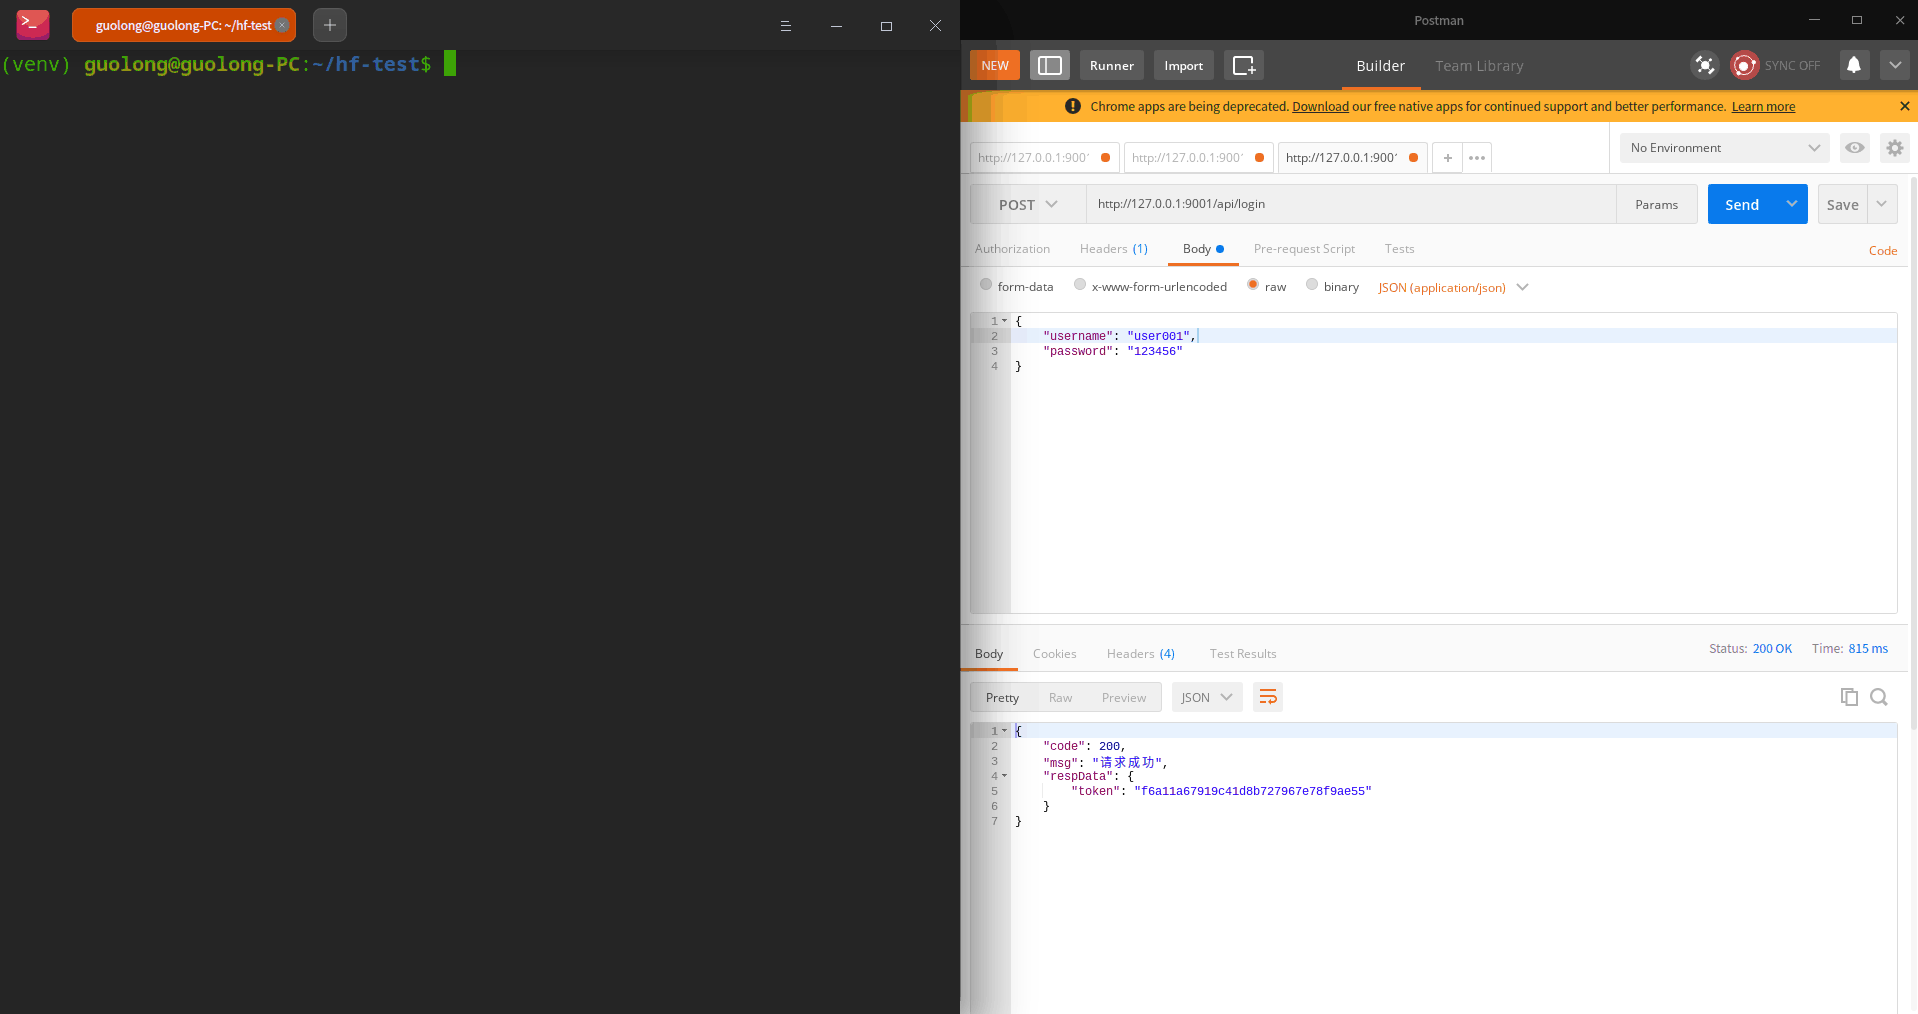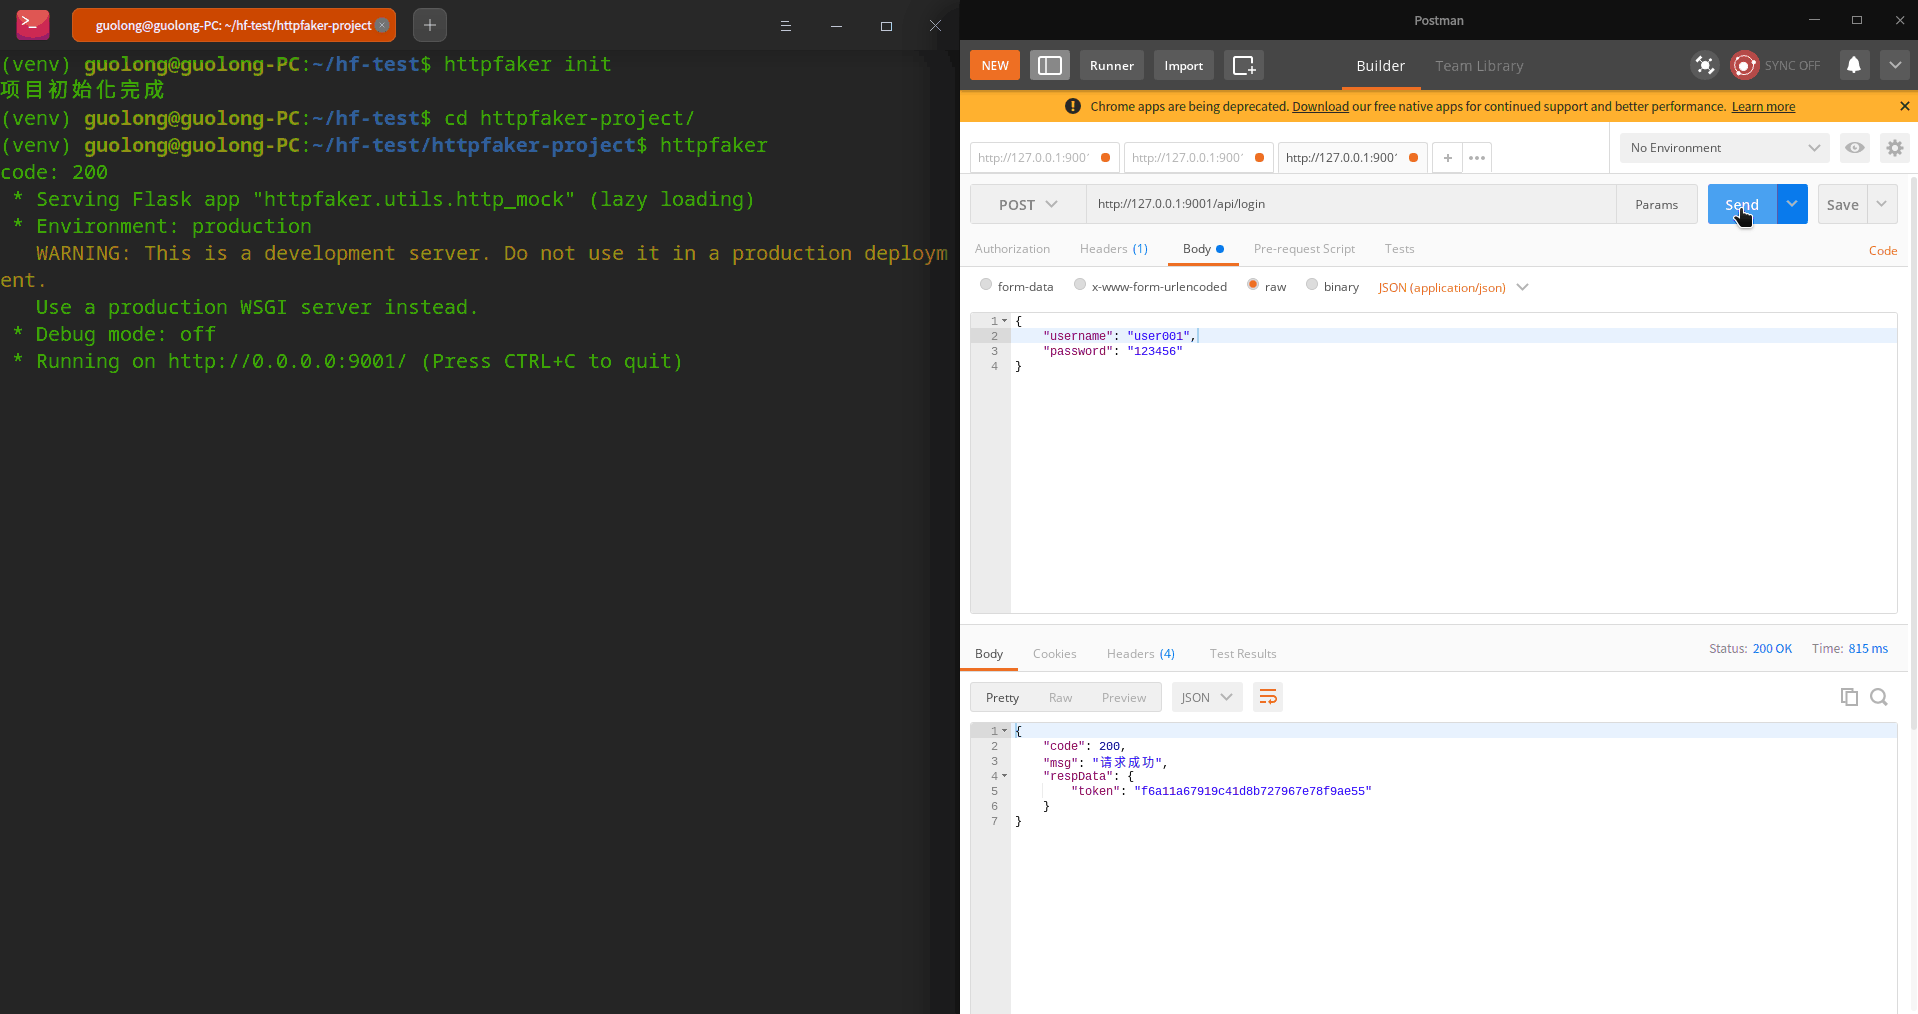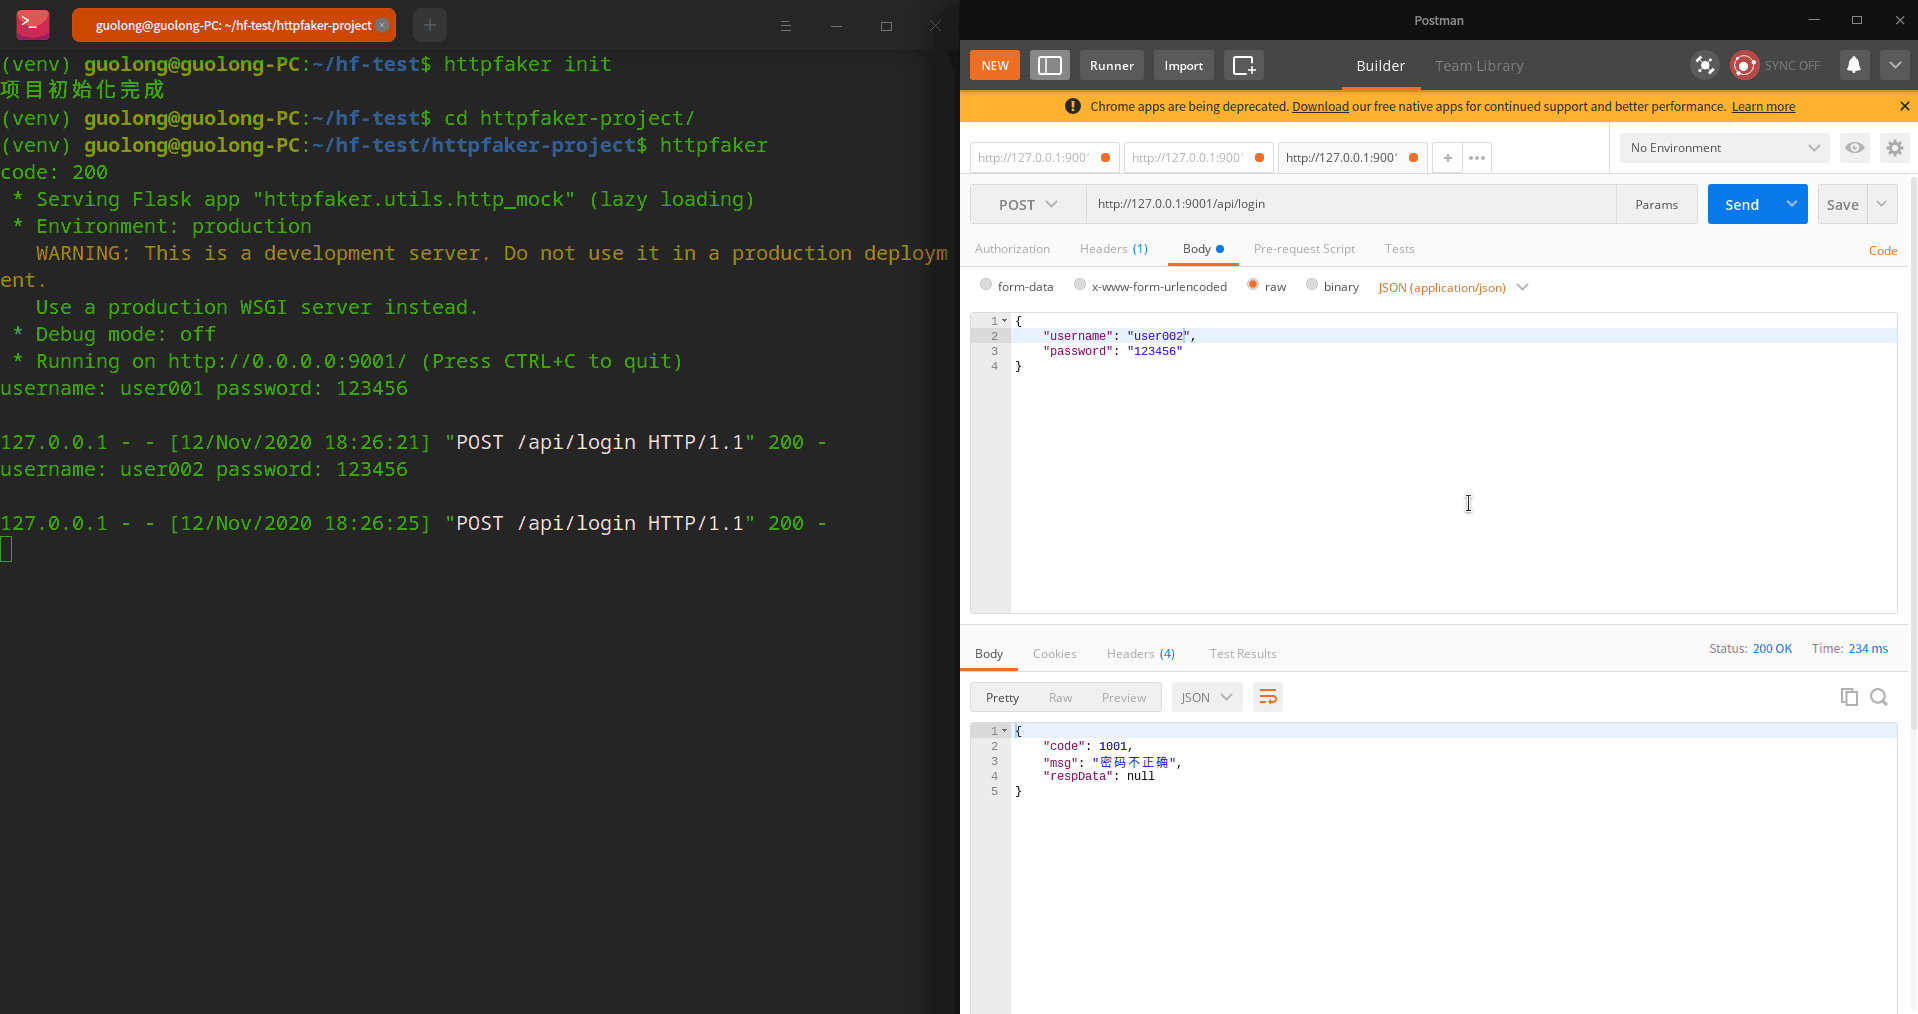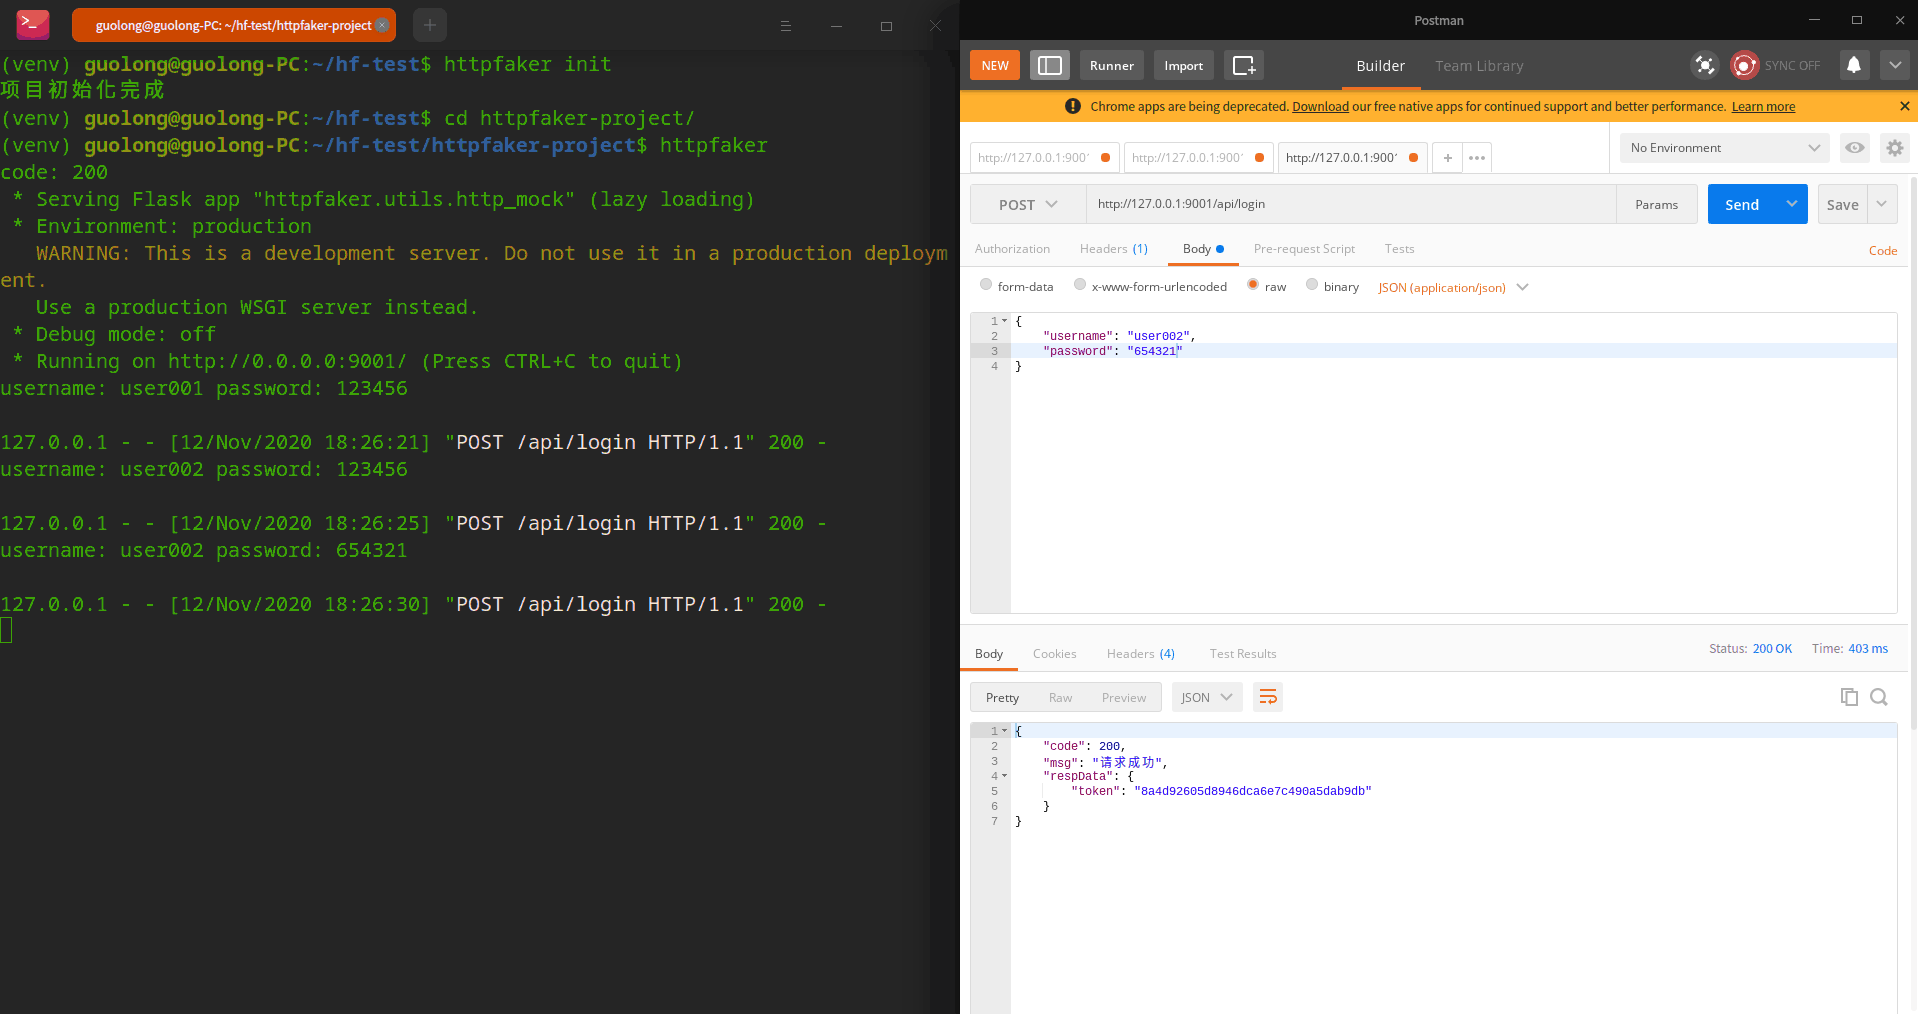
上面例子中使用httpfaker init预生成了一个example.yml文件,yaml文件中描述了一个登录的场景:
- 前端通过
post方法调用/api/login这个地址,并在请求body中传来了username和password两个参数。 httpfaker接收到请求后会按照logic中描述的逻辑进行业务处理:先打印了请求参数,再按照verify中描述的,调用verify_accont方法, 来验证用户名和密码是否匹配,然后按照token中描述的调用gen_token方法,生成token。 (verify_account和gen_token方法已经注册到httpfaker调用函数中了,注册方法见自定义方法的注册)- 在逻辑处理完成后,httpfaker按照
response中描述的内容进行字段返回,headers中引用了在env中定义的content_type;body中的code、msg、data等字段直接引用logic中已经生成的结果。
在上述流程中完成了用户登录到返回数据的一个完整流程,包含了业务处理部分,使mock服务不仅仅只是mock,还可以包括真实的业务逻辑。
其它
- http2api: httpfaker支持录入接口数据,使用http2api,只需要在前端进行请求,可以自动将请求内容转换为httpfaker可读的模板。
- swagger2api: 支持将swagger格式的接口数据直接转换为httpfaker可读的模板。
完整示例
1 maintainer

Metadata
1 maintainer
Release files for httpfaker 0.0.4b1112
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| httpfaker-0.0.4b1112.tar.gz | 20.1 kB | Without provenance | Details |
Release files / httpfaker-0.0.4b1112.tar.gz
| Download URL | httpfaker-0.0.4b1112.tar.gz |
|---|---|
| Size | 20.1 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
4344166eda910a07796e72ae49b03920ec8995ec086b1edbe706ae4a10dde0bd
|
|
BLAKE2b-256 checksum How to use checksums |
8ee8b8c6a4596cfe6acdc8a94c7e740c77813762df6d6adfd7228a5964b2cd0a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.2.0 pkginfo/1.6.1 requests/2.24.0 setuptools/50.3.2 requests-toolbelt/0.9.1 tqdm/4.51.0 CPython/3.7.3
|
Security for httpfaker 0.0.4b1112
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














