
hurl-orchestra
AI first API automation testing.
Test your API from login to checkout. Write each step as a small text file, and hurl-orchestra runs the steps in the right order and shows you which step broke.



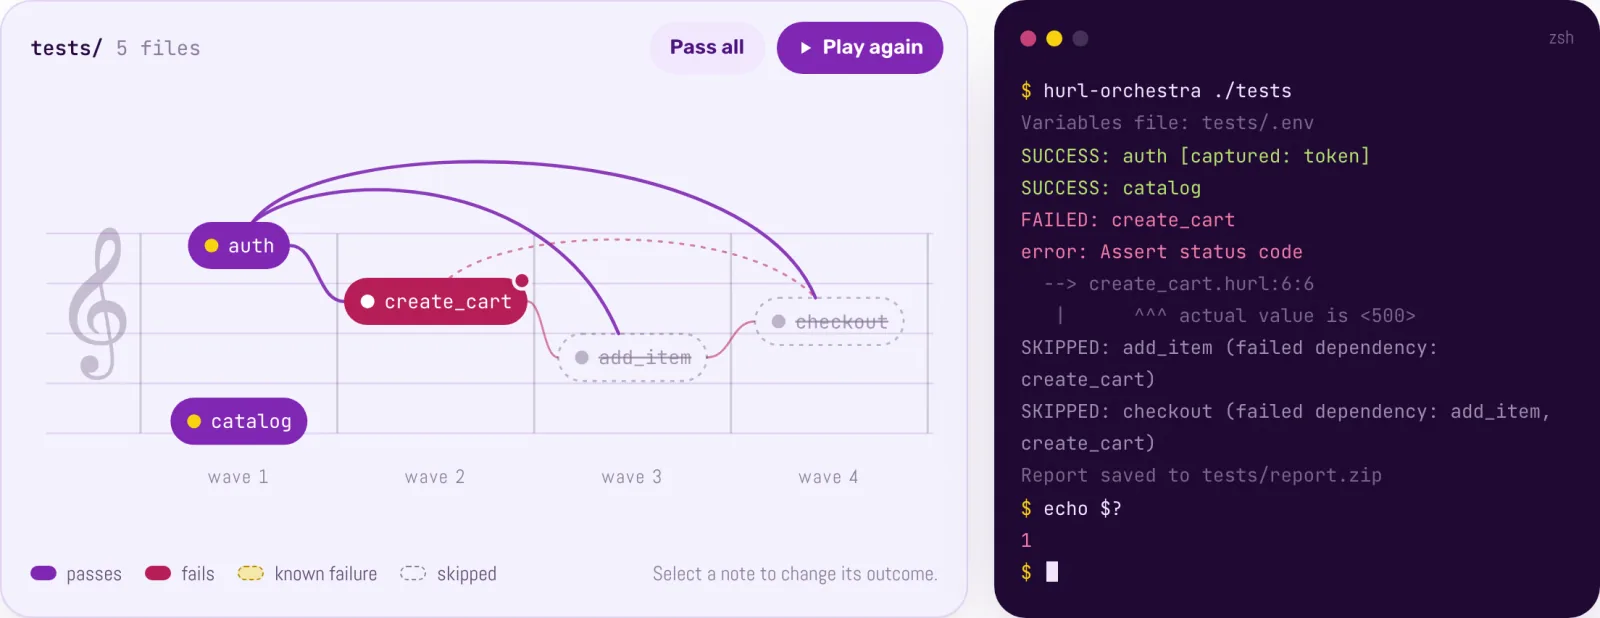
Play with it on the docs home page: select a note, make it fail, watch the run.
Say what each step needs, and the order follows
---
id: profile
deps: [auth]
---
GET {{base_url}}/profile
Authorization: Bearer {{auth_token}}
HTTP 200
pip install hurl-orchestra
hurl-orchestra ./tests
I built hurl-orchestra for the moment a Hurl test suite outgrows one file. Each file says which steps must pass first, and the tool works out the rest: it runs the steps in the right order, runs independent steps at the same time and passes values like a login token to the steps that need them. When one step fails, only the steps that depend on it stop, so one run shows every broken flow, not just the first one.
Why teams pick it
- AI first. Plain-text requests, a few frontmatter fields, a JSON plan (
--dry-run --json) and CTRF results. A coding agent can write a test, check the graph and read the failure without a human in the loop. There is no model inside and nothing to configure. Use it with your AI assistant → - Declared, not scripted.
depsreplace the shell script that calls Hurl in the right order. - Captures that do not collide.
authcapturestoken, and its dependents getauth_token. - Honest about flaky failures.
known_failurestolerates a failure you understand, with a reason and an expiry date, and the report still shows it. - Polite under load. A
retrypolicy backs off exponentially, with jitter, and honoursRetry-After. - Ready for CI. A zip of every Hurl report on every run, and a CTRF file for the GitHub job summary.
Under the hood
- Small. Python 3.11+, one dependency (
python-frontmatter), and the standard library'sgraphliband thread pool for the waves. - Safe with secrets. Captured values reach Hurl through a private variables file per call, never the process list.
- Fails early. The whole graph is validated before the first request: unknown deps, cycles, wrong types, malformed tolerances and bad regexes.
- Tested. 250+ tests, with ruff and fully typed mypy checks in CI.
- Docs written for people and agents. Short procedures in Simplified Technical English, checked by Vale, and published as
llms-full.txttoo.
Read the docs
Get started · Concepts · How-to · Reference · Troubleshooting
Say hi
If hurl-orchestra saved your suite from a pile of shell scripts, or you have a flow it cannot express yet, I would like to hear about it. Open an issue, or read CONTRIBUTING.md to send a change.
MIT License · Made at Esta couve flor
1 maintainer

Metadata
1 maintainer
Release files for hurl-orchestra 0.11.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| hurl_orchestra-0.11.0.tar.gz | 42.5 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| hurl_orchestra-0.11.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 68.5 kB
Release files / hurl_orchestra-0.11.0.tar.gz
| Download URL | hurl_orchestra-0.11.0.tar.gz |
|---|---|
| Size | 42.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
70056f5b27a17be338f88f5e2734b99c3a6cc29ae1d4314f05ffaca654924bf5
|
|
BLAKE2b-256 checksum How to use checksums |
9efadd7c530308cd76c90ac90d2aa59f3919ce7257895b6b009390f61793485e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 27, 2026.
Transparency logRelease files / hurl_orchestra-0.11.0-py3-none-any.whl
| Download URL | hurl_orchestra-0.11.0-py3-none-any.whl |
|---|---|
| Size | 26.0 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
48b1e1424ff1702df58980cbd39d9dcf729a9e2ab1ca7c0c0d116547213a127e
|
|
BLAKE2b-256 checksum How to use checksums |
786cd8d64c5c327757ad5df955b02144d1b0244448a017ad1ed14daaa158b256
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 27, 2026.
Transparency log













