
Hybrid Groups


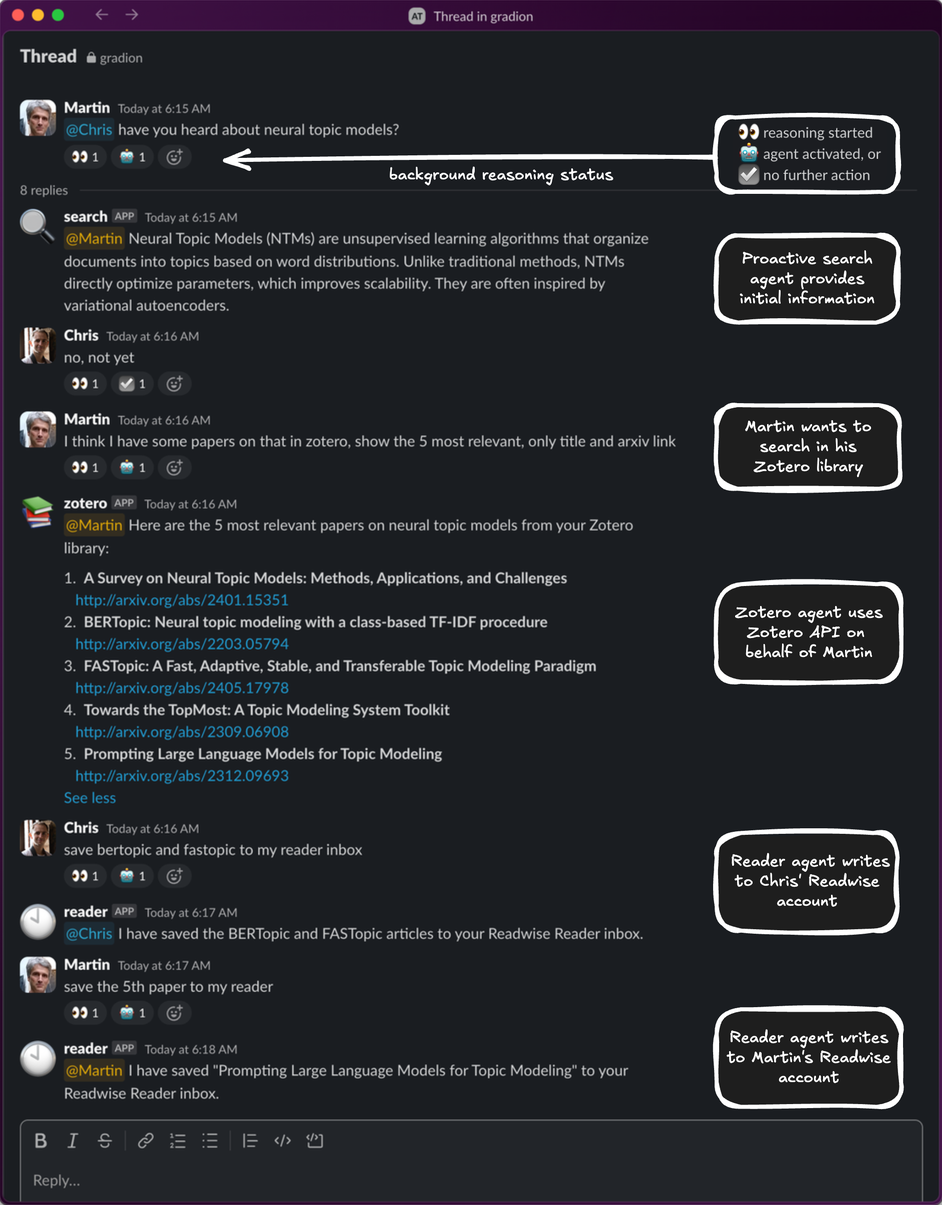
Hybrid Groups integrates Group Genie into Slack and GitHub. It enables existing single-user AI agents to participate in group chat conversations without requiring modification to the agents themselves. While many AI agents excel at responding to direct queries from individual users, they typically cannot handle multi-party conversations where relevant information emerges from complex exchanges between multiple participants. Hybrid Groups solves this by combining intelligent pattern detection with a flexible agent integration layer. It monitors group chats, detects conversation patterns, and reformulates multi-party exchanges into self-contained queries that AI agents can process.
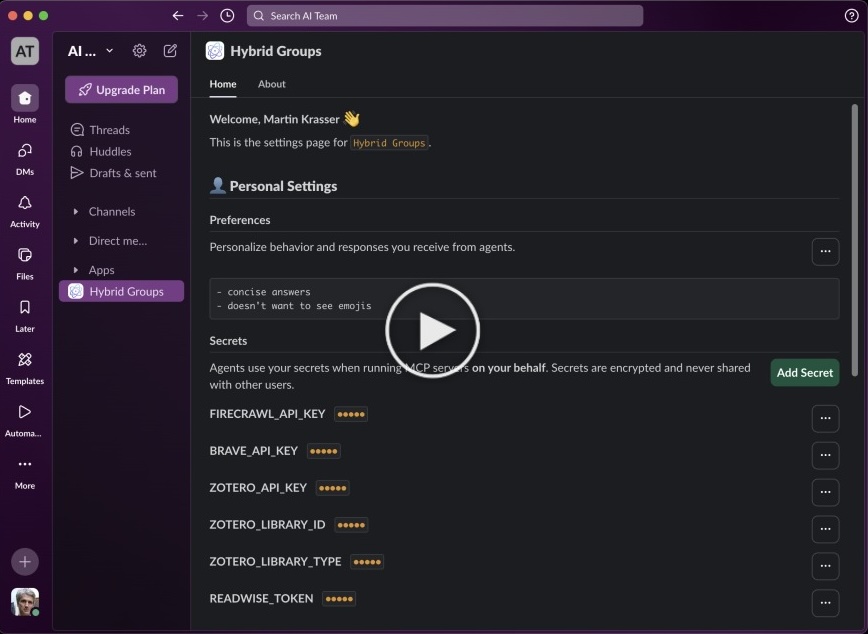
Hybrid Groups supports user-specific credentials and preferences, session persistence for resuming conversations after restarts, service connectors for accessing 250+ external services (Gmail, Notion, Figma, etc.), media attachment support, action approval workflows, and custom commands. Agents act on behalf of individual team members using their personal credentials and preferences, enabling users to securely access their private resources while maintaining proper access boundaries to other users.
 |
 |


Release files for hybrid-groups 0.2.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| hybrid_groups-0.2.2.tar.gz | 4.7 MB | With provenance | Details for hybrid_groups-0.2.2.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| hybrid_groups-0.2.2-py3-none-any.whl | Python 3 | none | any | Details for hybrid_groups-0.2.2-py3-none-any.whl |
Total release size: 9.4 MB
Release files / hybrid_groups-0.2.2.tar.gz
| Download URL | hybrid_groups-0.2.2.tar.gz |
|---|---|
| Size | 4.7 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
3ba8cd841f4d765a10a75386baba0a607a34596ec68c555f043ab1b9bcfb37c4
|
|
BLAKE2b-256 checksum How to use checksums |
e6aa378f4912df1b2cfbe98aebe928ec8777e07412606f499beeb78de4ee9477
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 22, 2026.
Transparency logRelease files / hybrid_groups-0.2.2-py3-none-any.whl
| Download URL | hybrid_groups-0.2.2-py3-none-any.whl |
|---|---|
| Size | 4.7 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
015931fd2a4aa194e1a40a1ae35cdbc7291c27c78db264c173dd37faaa7feed0
|
|
BLAKE2b-256 checksum How to use checksums |
ce9b9ea7040061b88385c717375389c8a329de7db0875aa3e0d4c973eaeabd30
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 22, 2026.
Transparency logSecurity for hybrid-groups 0.2.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for hybrid_groups-0.2.2.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 22, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














