
Iiwi
Iiwi · /ˈiː.wiː/ "ee-wee"
Turn your AI coding work into clear engineering reports.



English | 繁體中文
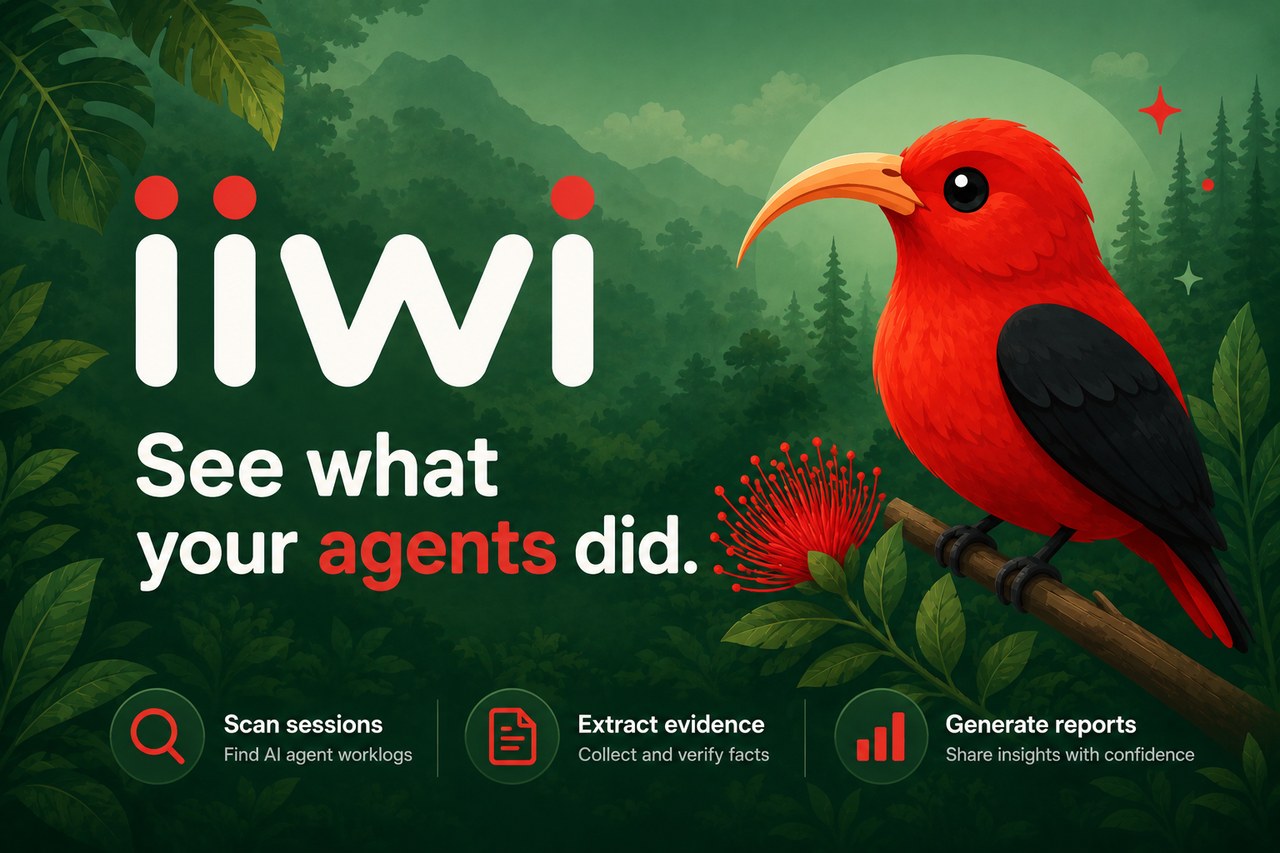
You already did the work. Iiwi turns the history left by your coding agents into an update you can review and share.
Iiwi works with OpenCode, Claude Code, and Codex. It finds what you worked on, keeps related work together, and turns it into a Markdown report without making you reread old agent conversations.
- Works across projects. Iiwi finds your coding-agent sessions wherever you worked.
- Keeps related work together. Sessions are grouped by repository.
- You stay in control. Choose and edit what belongs in the final report.
- Protects sensitive information. Common secret patterns are removed before reports are written.
How it works
- Read — Iiwi finds local AI coding history from OpenCode, Claude Code, or Codex.
- Review — Keep, edit, reorder, or remove the work that matters.
- Generate — Create a Markdown report you can share with your team.
What you get
A reviewed report can look like this:
# Weekly engineering update

## My Project
- Simplified the report workflow and made review easier to use.
- Added Claude Code and Codex session support.
- Fixed documentation checks in CI.

## Blockers
- None
Quick start
Requires Python 3.11+ and git.
pipx install iiwi                 # or: pip install iiwi

iiwi doctor                      # check that Iiwi can read your setup
iiwi                             # open the interactive menu
From the menu, choose what you want to do and Iiwi walks you through the rest.
Two useful shortcuts:
iiwi daily                       # prepare today's standup update
iiwi report --period last-week   # prepare last week's report
Reports are saved under reports/ by default.
Use the interactive menu
Run iiwi with no arguments when you do not want to remember commands or flags.
The menu lets you review recent work, prepare a standup, generate reports, check past reports, verify your setup, and change settings.
When generating a report, Iiwi shows the work it found first. Pick what belongs, edit anything you want to change, and Iiwi writes the Markdown report.
For the full review workflow and keyboard controls, see the Quick Review guide. For the daily flow, see the Daily Standup guide.
Use the CLI directly
The interactive menu is the easiest place to start. If you prefer commands, these cover the most common cases:
iiwi doctor                       # check your setup
iiwi daily                        # prepare a daily standup
iiwi report --period last-week    # generate last week's report
Run iiwi --help for the rest, or see the
CLI reference for every command, flag, example, and exit code.
Configuration
You can start using Iiwi without changing any settings.
If you want to change things such as the model, timezone, paths, or defaults, use:
iiwi config init                  # walk through the settings
iiwi config list                  # see the settings currently in use
See the configuration guide for all available settings and advanced setup.
Privacy
Iiwi reads and processes your session history on your machine. If you use AI drafting, Iiwi redacts common secret patterns before passing the text to the CLI you configured for drafting. What that CLI does next depends on its own configuration.
Reports can still contain private goals, filenames, commands, and working paths, so review a report before sharing it.
See Privacy and security for the full data flow, redaction behavior, and current limits.
Documentation
Most day-to-day details live in the guides below instead of this README:
- CLI reference — commands, flags, examples, and exit codes
- Quick Review guide — review controls and report flow
- Daily Standup — Yesterday / Today / Blockers workflow
- Configuration — settings, models, paths, and environment variables
- Privacy and security — what stays local and what reports can contain
- Support and limits — current harness-specific limits
For contributors and deeper technical details, see
Architecture, Security policy, and the rest of the
docs/ directory.
The name
The ʻiʻiwi is a scarlet Hawaiian honeycreeper whose long curved bill reaches nectar others cannot — which is what this tool does with the sessions your agent left behind. Pronounced the anglicised way, "ee-wee".
Development
git clone https://github.com/mike840609/iiwi.git
cd iiwi
uv sync --locked --extra dev                    # install the project and its dev tools

uv run iiwi                                     # run your working copy
uv run pytest --cov=iiwi --cov-fail-under=80    # tests, with the coverage gate CI enforces
uv run ruff check .                             # lint
uv run pyright                                  # type check
The last three are exactly what CI runs, so a green local run means a green PR.
Name forms
The name is cased by where it appears:
| Context | Form |
|---|---|
| Distribution, CLI, URLs, application directories | iiwi |
| Python package and imports | iiwi |
| Prose | Iiwi |
| Environment variables | IIWI_ prefix |
| Error base class | IiwiError |
License
MIT
1 maintainer

Metadata
1 maintainer
Release files for iiwi 0.16.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| iiwi-0.16.1.tar.gz | 1.2 MB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| iiwi-0.16.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 1.4 MB
Release files / iiwi-0.16.1.tar.gz
| Download URL | iiwi-0.16.1.tar.gz |
|---|---|
| Size | 1.2 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
898f88cbf3d00acf6a6166e0c172b4f7202a52a12a33f1bc3e14c848962afe06
|
|
BLAKE2b-256 checksum How to use checksums |
3ee99a2f2822bdf205078134901249ddb94566ba83c1fe48136e50df54e037f8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logRelease files / iiwi-0.16.1-py3-none-any.whl
| Download URL | iiwi-0.16.1-py3-none-any.whl |
|---|---|
| Size | 205.5 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
a9ce9acc84ff8bb779d5e3be74914c77e8cabe1b58337629e22b6fba398964fc
|
|
BLAKE2b-256 checksum How to use checksums |
59b9281d1cf92fabc1038c587ccfab8f31905f31ce8abd506a2be5bcb1ea8f0c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logSecurity for iiwi 0.16.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for iiwi-0.16.1.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 9, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














