


ipysensitivityprofiler
Jupyter Widgets for visualizing local sensitivities of vectorized functions with
signature y = f(x) where x, y are arrays.
Main Features
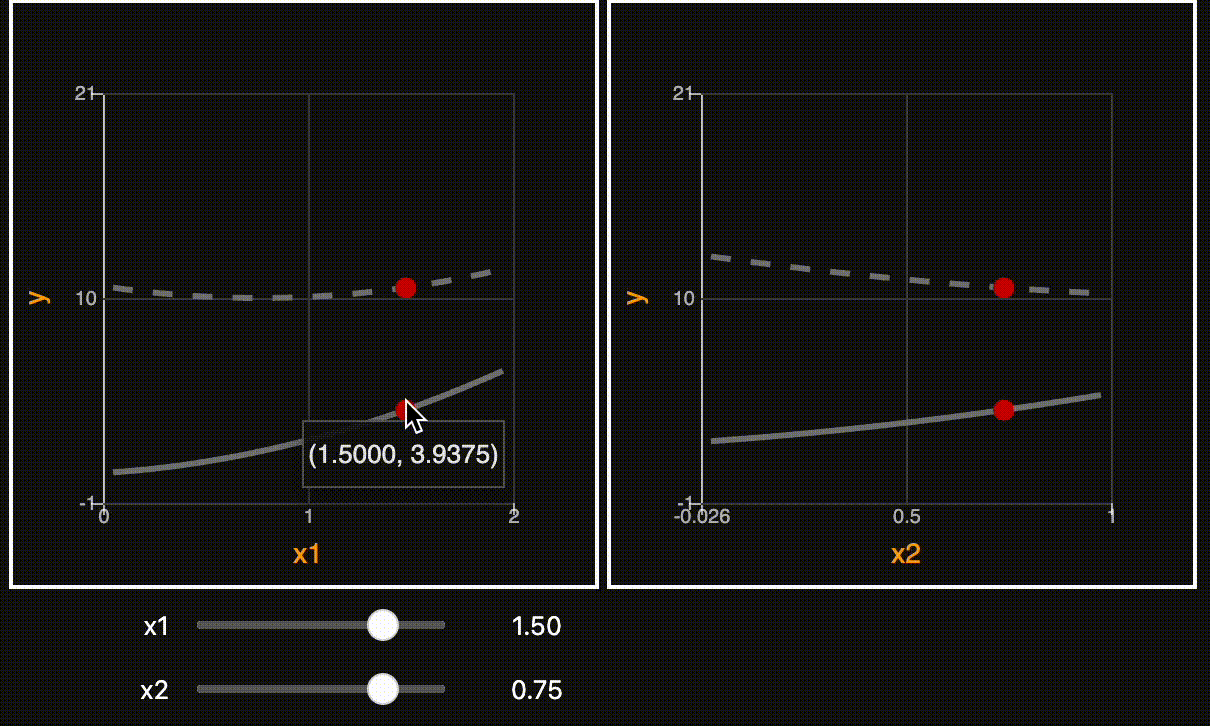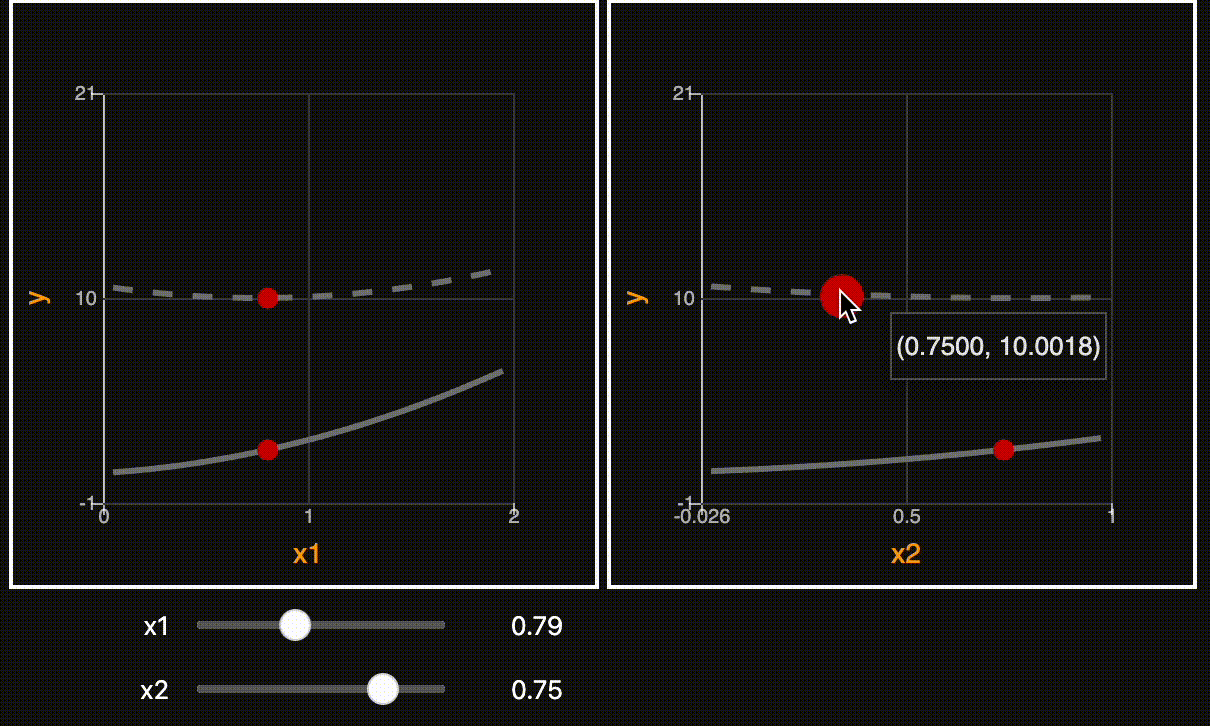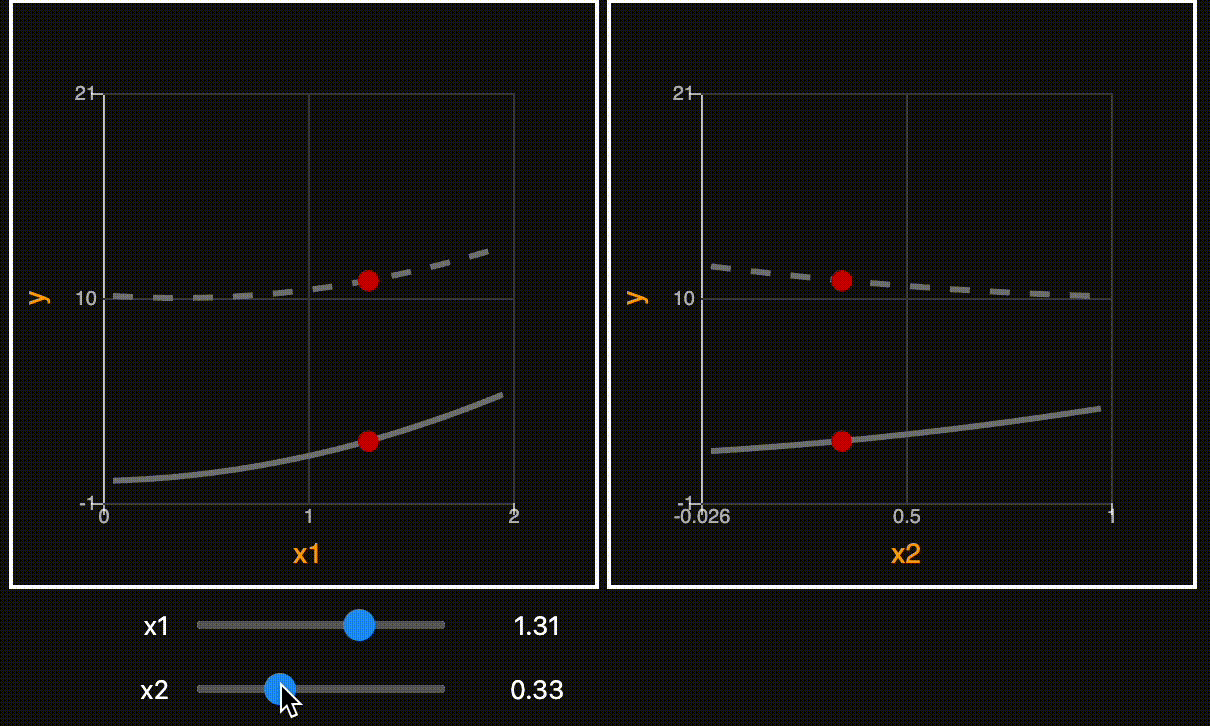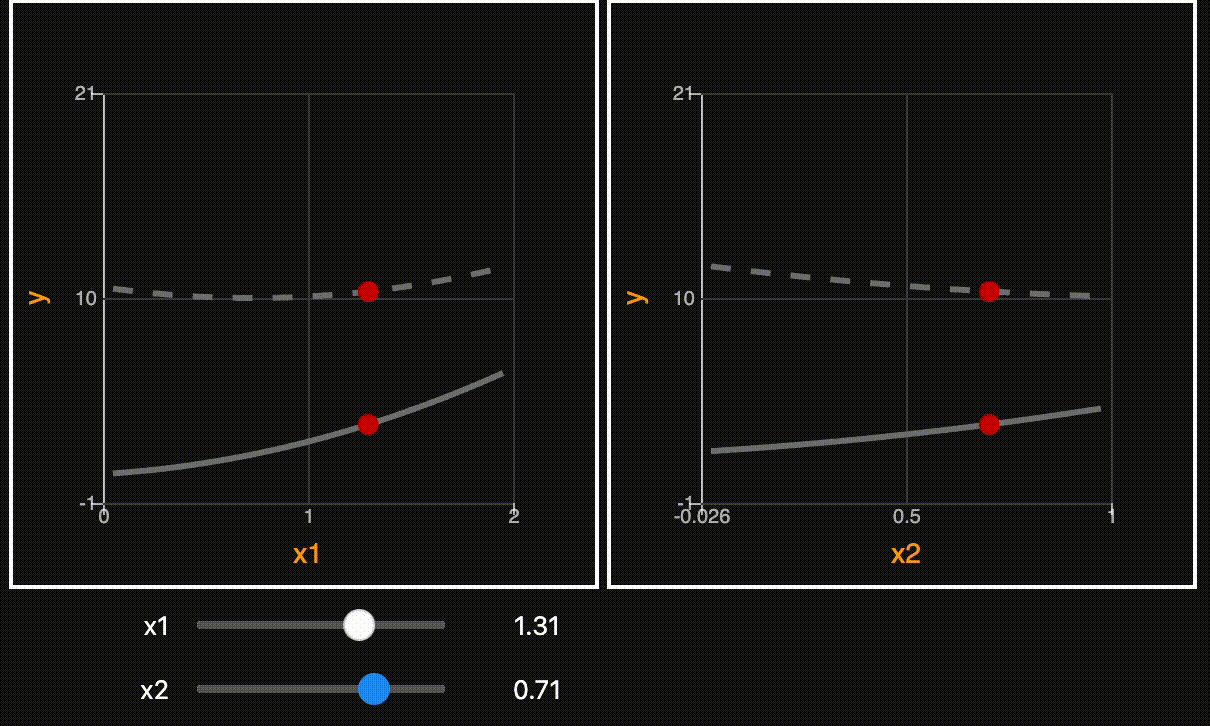
- Visualize multiple outputs against multiple inputs interactively
- Overlay more than one model at once
- Download pictures of individual plots (by clicking on the red dot)
Installation
pip install ipysensitivityprofiler
Example Usage
See the example notebooks, or run them without installing anything on binder.
Import the library and define one or more vectorized models:
import numpy as np
import ipysensitivityprofiler as isp

def quadratic1(x):
    """y = x1**2 + x2**2 + x1*x2"""
    return np.prod(x, axis=1) + np.power(x, 2).sum(axis=1)

def quadratic2(x):
    """y = 10 + x1**2 + x2**2 - 2 * x1*x2"""
    return 10 - 2 * np.prod(x, axis=1) + np.power(x, 2).sum(axis=1)
Then profile them:
isp.profiler(
    models=[quadratic1, quadratic2],
    xmin=[0, 0],
    xmax=[2, 1],
    ymin=[0],
    ymax=[20],
    x0=[1.5, 0.75],
    resolution=10_000,
    xlabels=["x1", "x2"],
    ylabels=["y"],
)
Use Case
A local sensitivity profile is the trace of a function obtained by holding all dimensions fixed but one. Profiling a model interactively is useful for debugging models (spotting obviously wrong trends early), for robust design (seeing how performance changes when the design is perturbed away from nominal), and for model comparison (overlaying a high-fidelity model, a low-fidelity one, and ground truth on the same plot to see where they disagree).
Limitations
Models must be fast for interactivity: they must be able to evaluate thousands of datapoints on the order of milliseconds. This is a non-issue for empirical regressions (e.g. neural nets) or first-order physics-based models.
The other limitation is screen real estate. Beyond a certain number of inputs and outputs, humans become overwhelmed and the screen runs out of room, so this library is best suited for targeted studies on a subspace of a larger problem.
Documentation
Documentation is available here
(generated using sphinx).
Contributing
Contributions are welcome — see CONTRIBUTING.md for how to set up
the development environment (pixi) and run the QA pipeline.
A Note on AI-Assisted Development
This library began in 2024 as hand-written code, and its foundation — the profiling idea itself, the widget architecture, and the vectorized numerics behind it — reflects deliberate design rather than generated output. We recognize how capable AI has since become, and we leverage it judiciously and under human oversight — applying it where it genuinely improves the project, such as performance audits and test coverage, not as a substitute for understanding it. Every change, whatever its source, is held to the same standard of review.
License
Distributed under the terms of the MIT License.
1 maintainer

Metadata
1 maintainer
Release files for ipysensitivityprofiler 0.0.3
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| ipysensitivityprofiler-0.0.3.tar.gz | 22.2 kB | With provenance | Details for ipysensitivityprofiler-0.0.3.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| ipysensitivityprofiler-0.0.3-py3-none-any.whl | Python 3 | none | any | Details for ipysensitivityprofiler-0.0.3-py3-none-any.whl |
Total release size: 40.3 kB
Release files / ipysensitivityprofiler-0.0.3.tar.gz
| Download URL | ipysensitivityprofiler-0.0.3.tar.gz |
|---|---|
| Size | 22.2 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
0c8868786a8528a42da53c14ca561aeb4bf2fe857df6eccf32ce57a7b54ab667
|
|
BLAKE2b-256 checksum How to use checksums |
bb14818f71a437791948786b20d0110932967a55e2866da8ecefa639418366de
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 30, 2026.
Transparency logRelease files / ipysensitivityprofiler-0.0.3-py3-none-any.whl
| Download URL | ipysensitivityprofiler-0.0.3-py3-none-any.whl |
|---|---|
| Size | 18.0 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
4b6343e3d32859e6ffe3d168e43fdf3ed9453d20cbc8b2b97aa8dfbfe1f1969c
|
|
BLAKE2b-256 checksum How to use checksums |
f0f307862cffe6e9fb37e87f5ada5696715f9e6edc1ac3935353c936049dfd20
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 30, 2026.
Transparency logSecurity for ipysensitivityprofiler 0.0.3
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for ipysensitivityprofiler-0.0.3.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 30, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














