


kx is a kubectl wrapper that adds index-based resource selection. Run
kx get <resource> once, then reference any result by number instead of typing
full resource names.
Install
Requires kubectl on your PATH. Every install path delivers the same prebuilt
binary — no Python runtime, no dependencies.
With uv (recommended), pipx, or pip:
uv tool install kx-cli
pipx install kx-cli
pip install kx-cli
As a kubectl plugin via krew, where kx is published as idx:
kubectl krew install idx
alias kx="kubectl idx"
Or run it without installing — the package is kx-cli, the command is kx:
uvx --from kx-cli kx get pods
pipx run --spec kx-cli kx get pods
Standalone binaries for linux, macOS and Windows are attached to every GitHub Release.
Usage
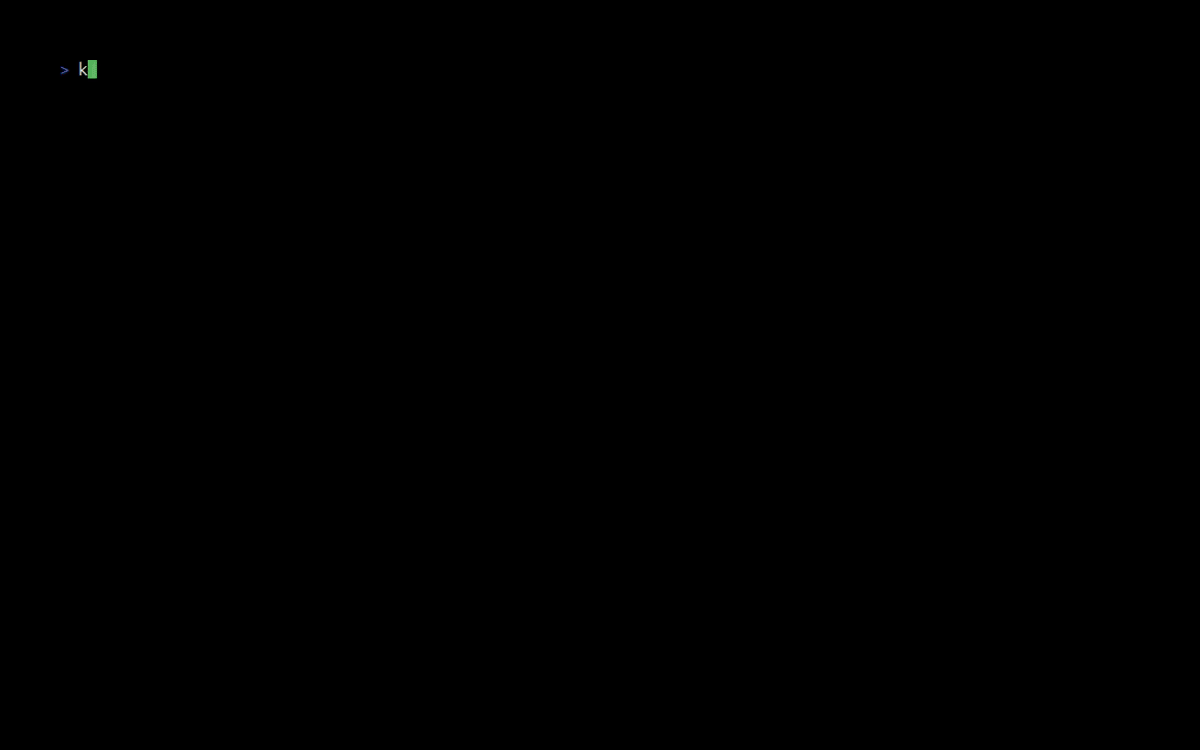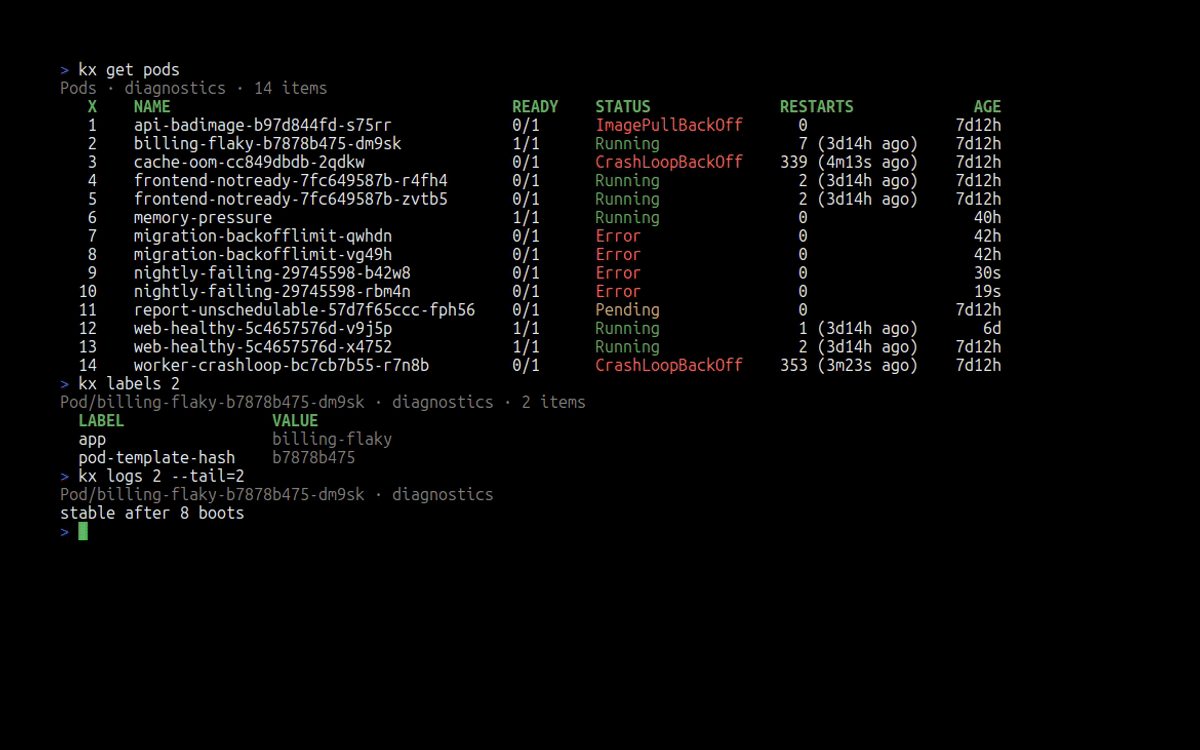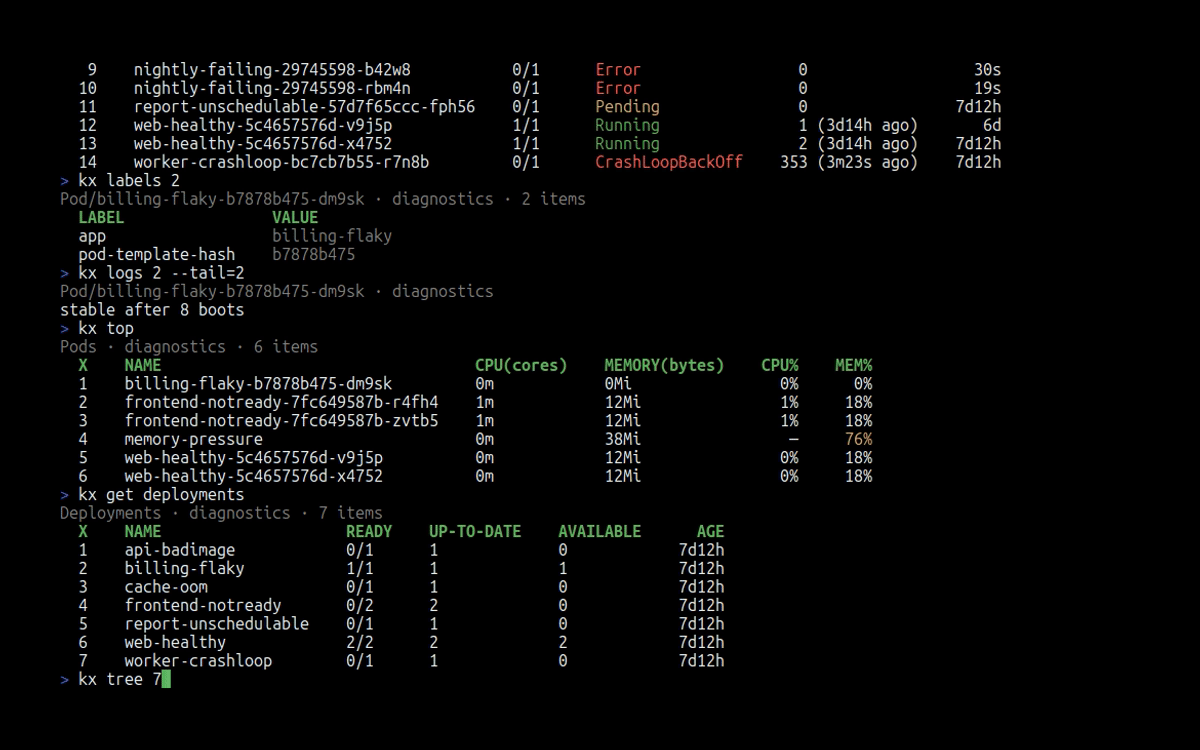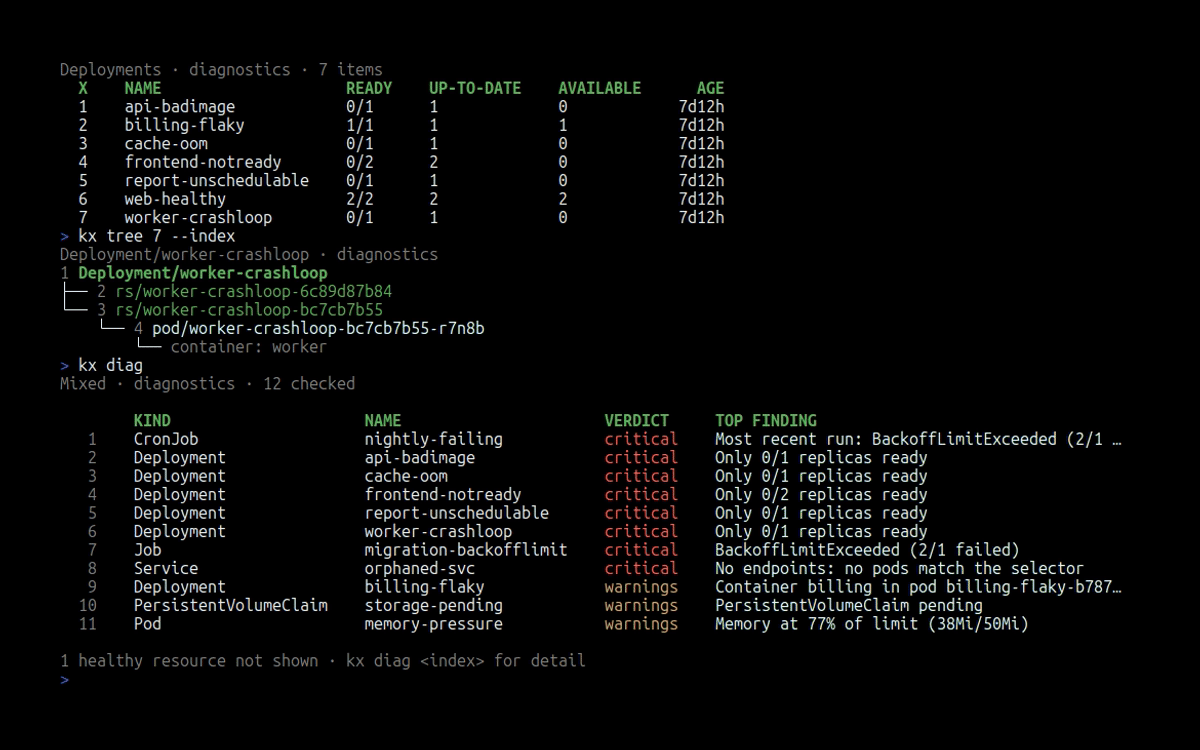
A kx session at a glance — one listing, then everything after it by number.
kx get pods    # lists pods, numbering each row
kx logs 3      # the third pod
kx diag 3      # why it's unhealthy
Indexes come several at a time, as ranges, or narrowed.
kx delete 3 5                   # several at once
kx delete 3..7                  # an inclusive range, walking either direction
kx delete ..5                   # open at the start
kx delete 5..                   # open to the end of the listing
kx get pods -m api              # --match/-m filters rows by name substring
kx get pods -n prod -l app=api  # anything else passes through to kubectl
-A listings are indexed too: each row records its own namespace, so
kx describe 7 reaches a resource in a namespace you aren't in, and two pods
sharing a name keep separate numbers.
Known kinds can drop the get — kx pods, kx deploy -n kube-system,
kx svc -m api — kubectl's shorthands and your CRDs included. A CRD resolves
from kubectl's on-disk discovery cache, with no API call.
--watch/-w redraws the table in place, rather than appending lines the way
kubectl -w does.
kx completion <bash|zsh|fish|powershell> completes indexes with the resource
behind them, so kx describe <TAB> offers 1 api-7d8f (Pod) rather than a
bare number.
Triage a namespace
Bare kx diag sweeps the current namespace — every workload kind, plus
Services, PVCs, Ingresses and pods nothing owns — and ranks what's unhealthy.
It reads live usage too, so a pod running hot against its memory limit is
flagged as an OOMKill risk before it dies.
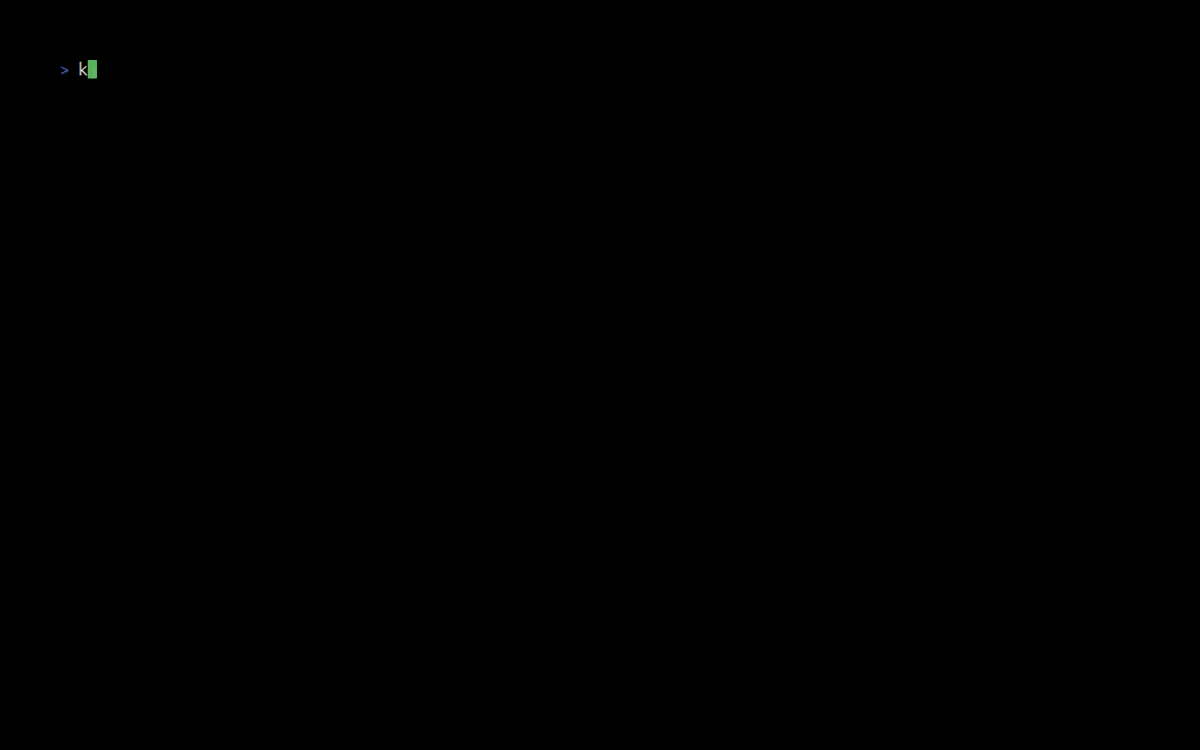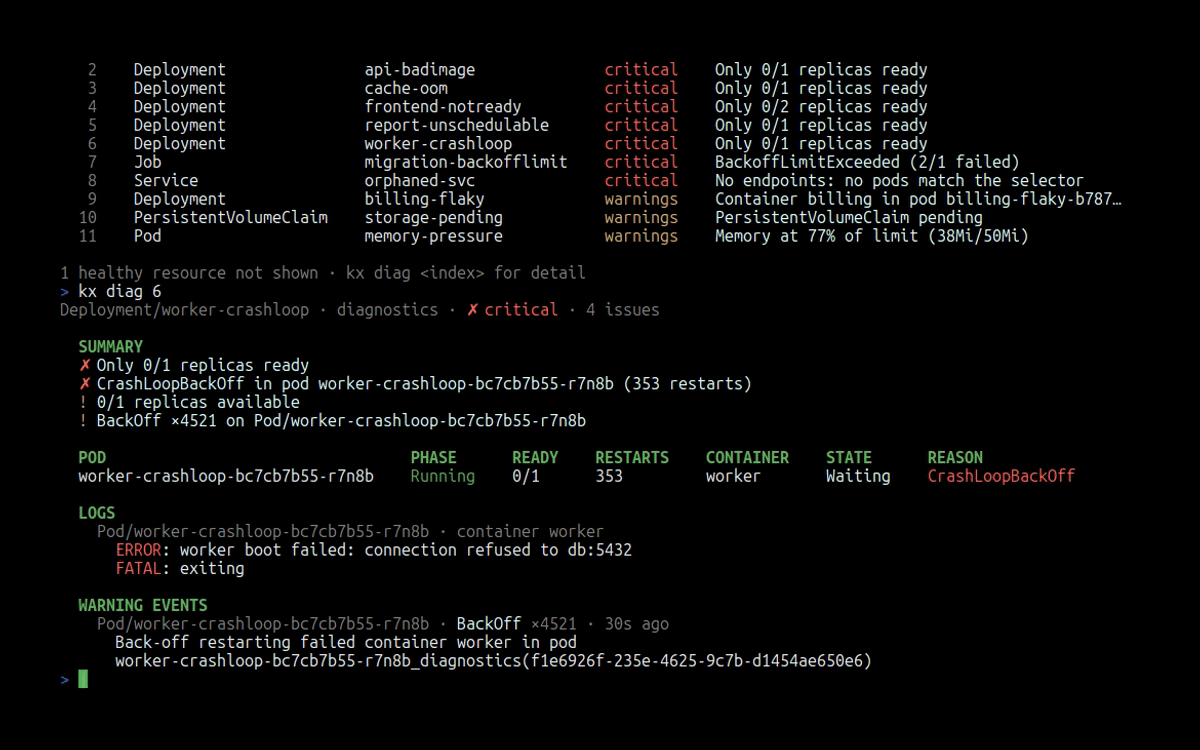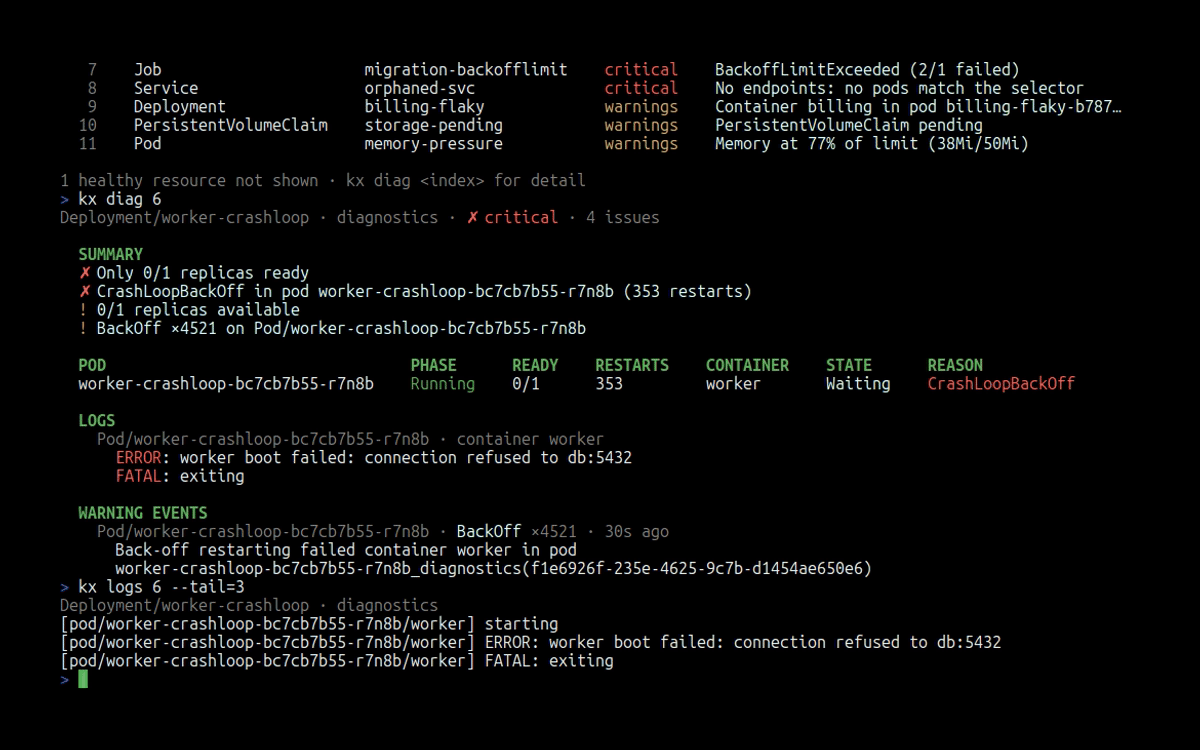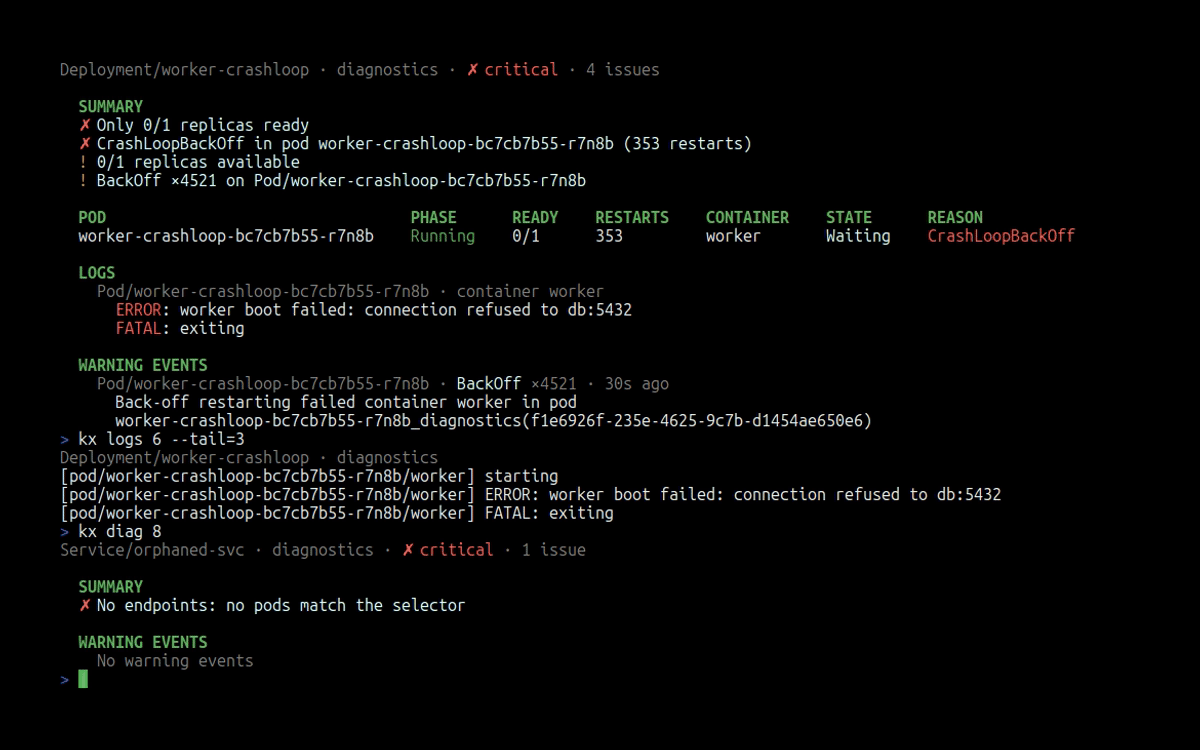
kx diag <index> diagnoses a single resource: a top level verdict, a findings
summary, a per-pod status table, log tails from broken containers and warning
events — one screen instead of four kubectl commands.
Read a Secret in plaintext
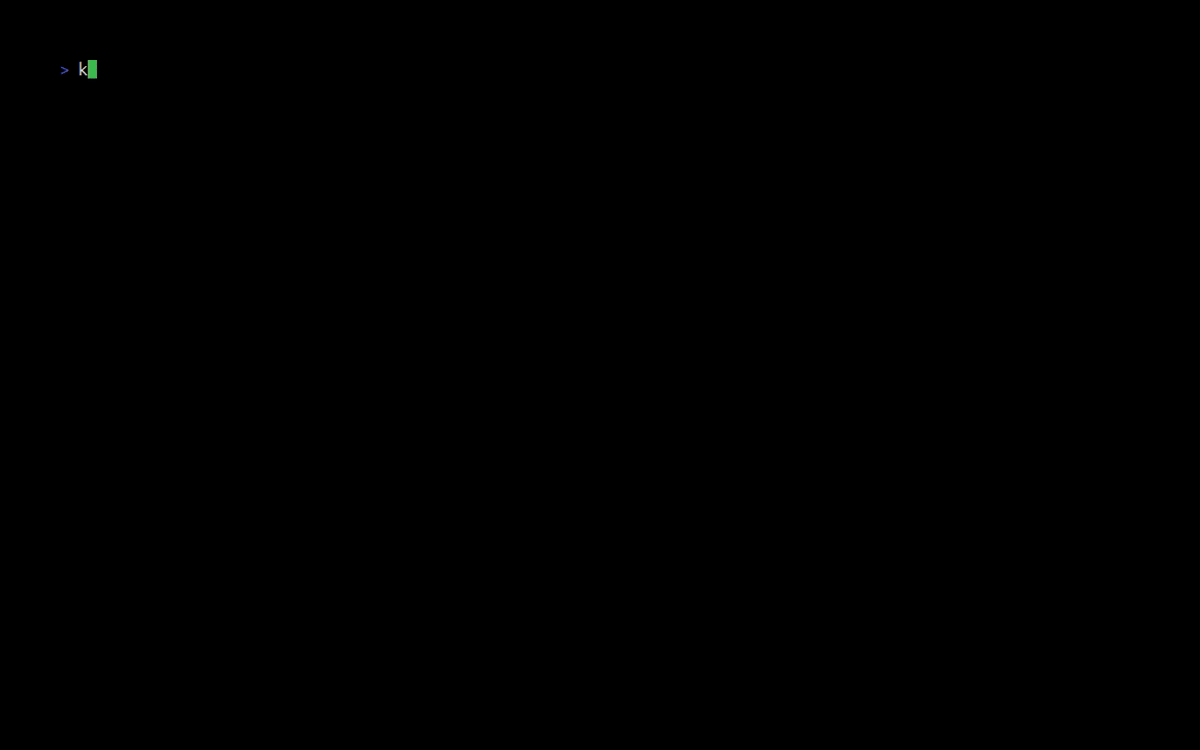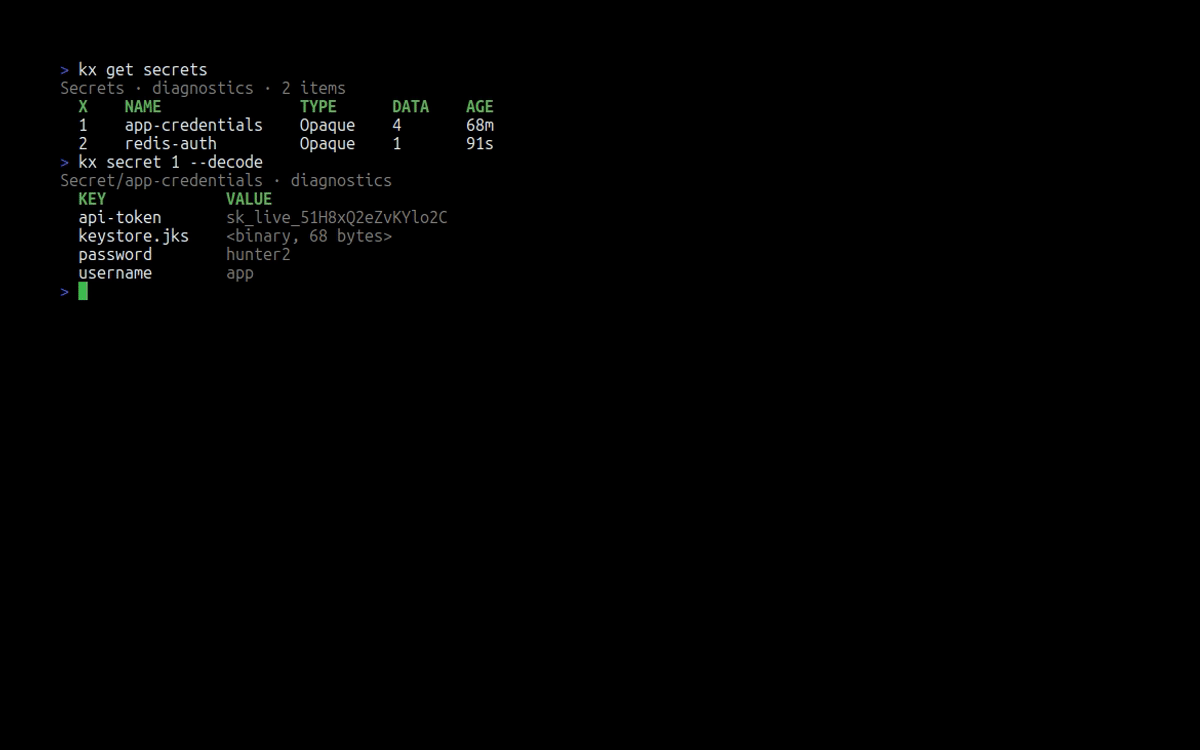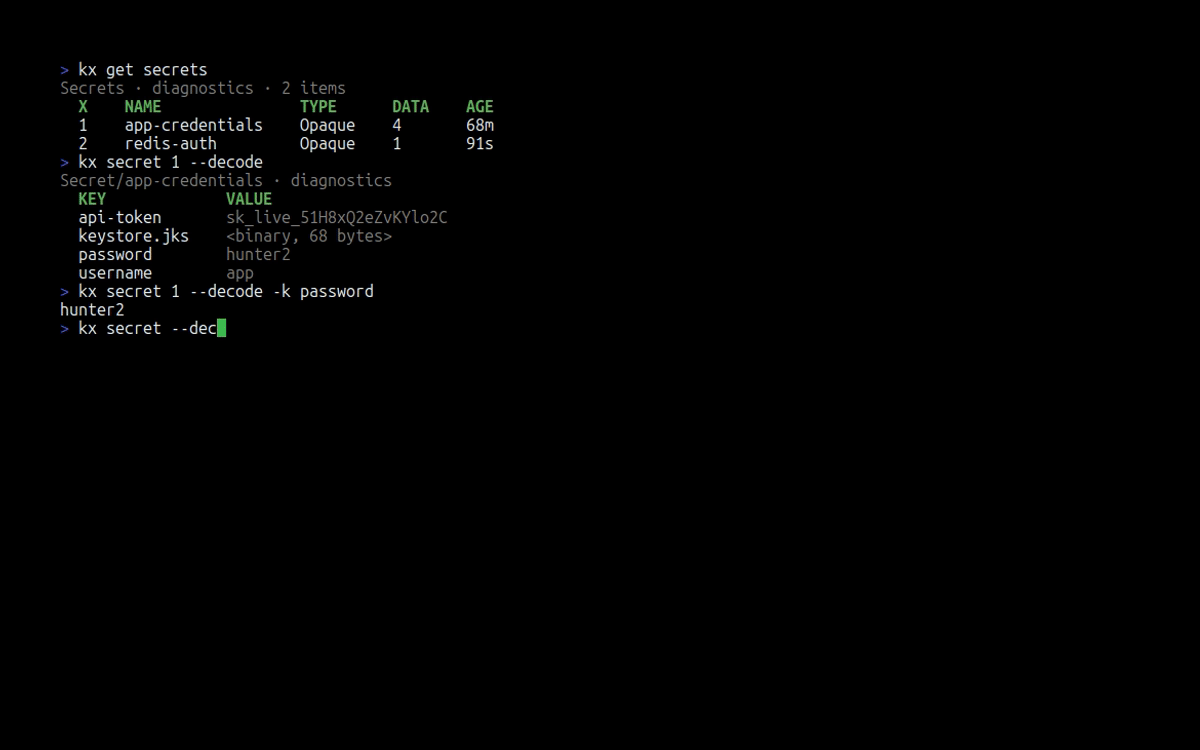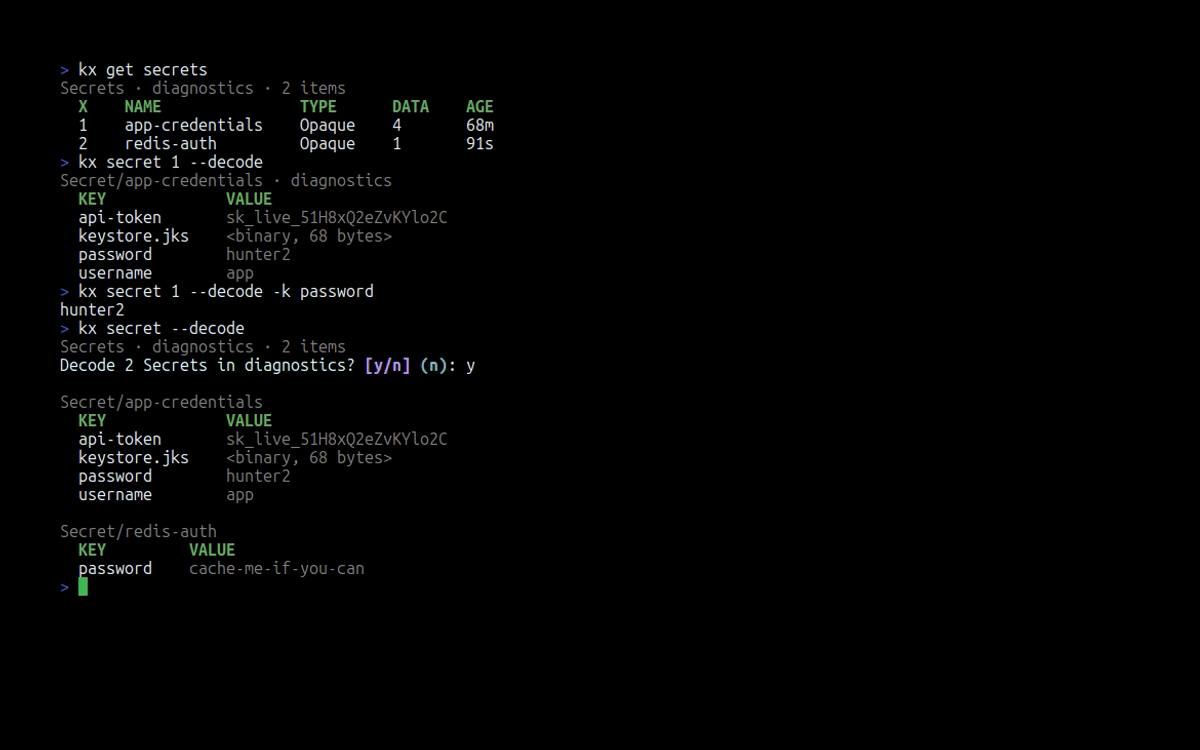
kx secret <index> --decode prints an indexed Secret's keys and values decoded.
--key/-k prints a single value raw — no banner, no wrapping — so it drops
straight into a shell.
export PGPASSWORD=$(kx secret 1 --decode -k password)
Bare kx secret --decode decodes every Secret in the namespace in one call,
confirming first — that prints every credential you have.
Scan images for CVEs
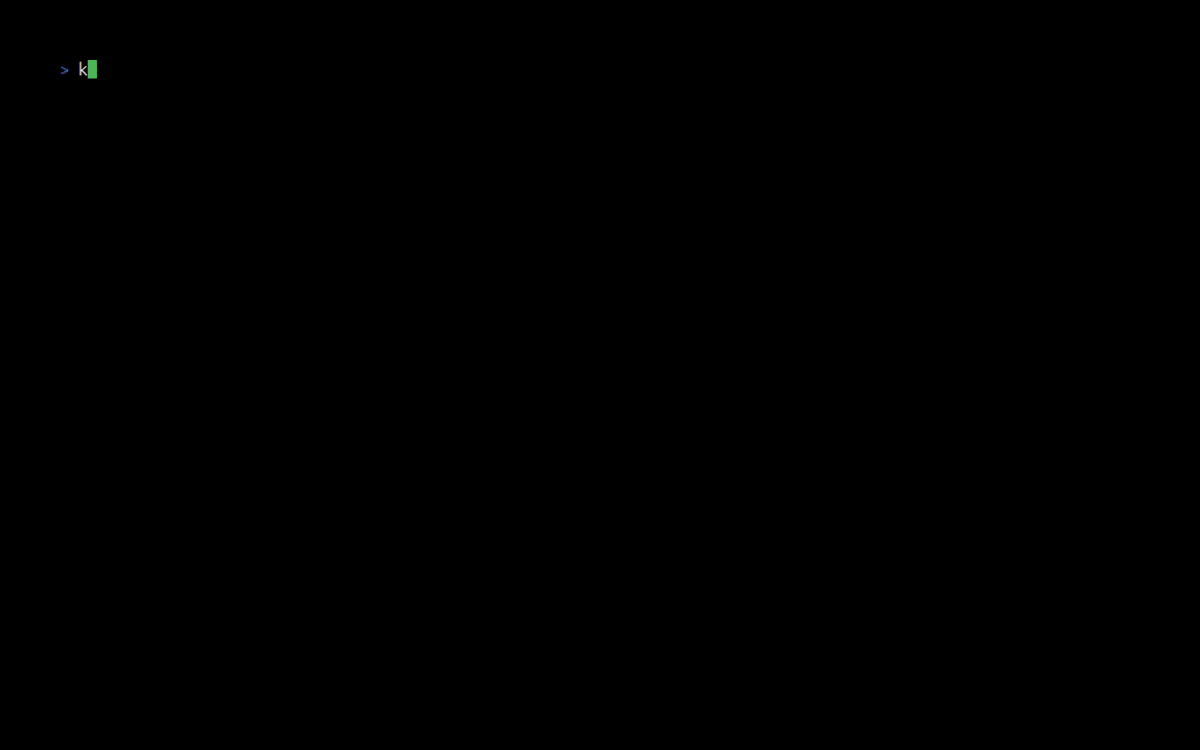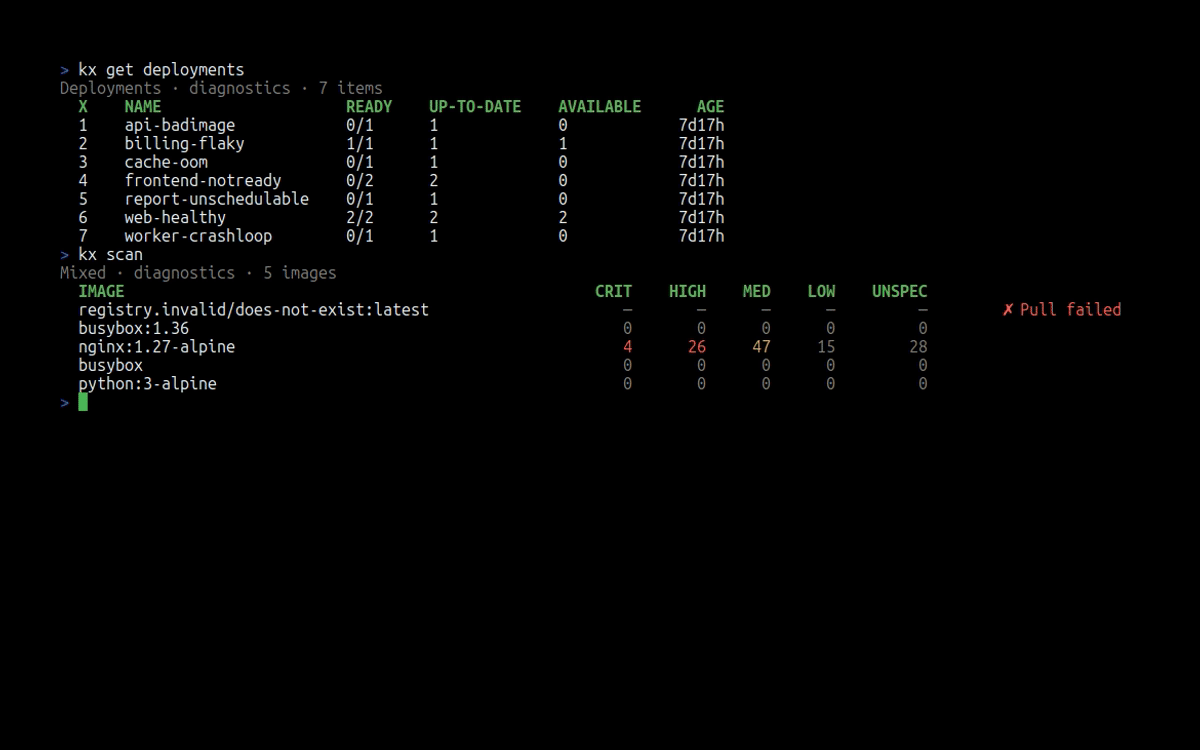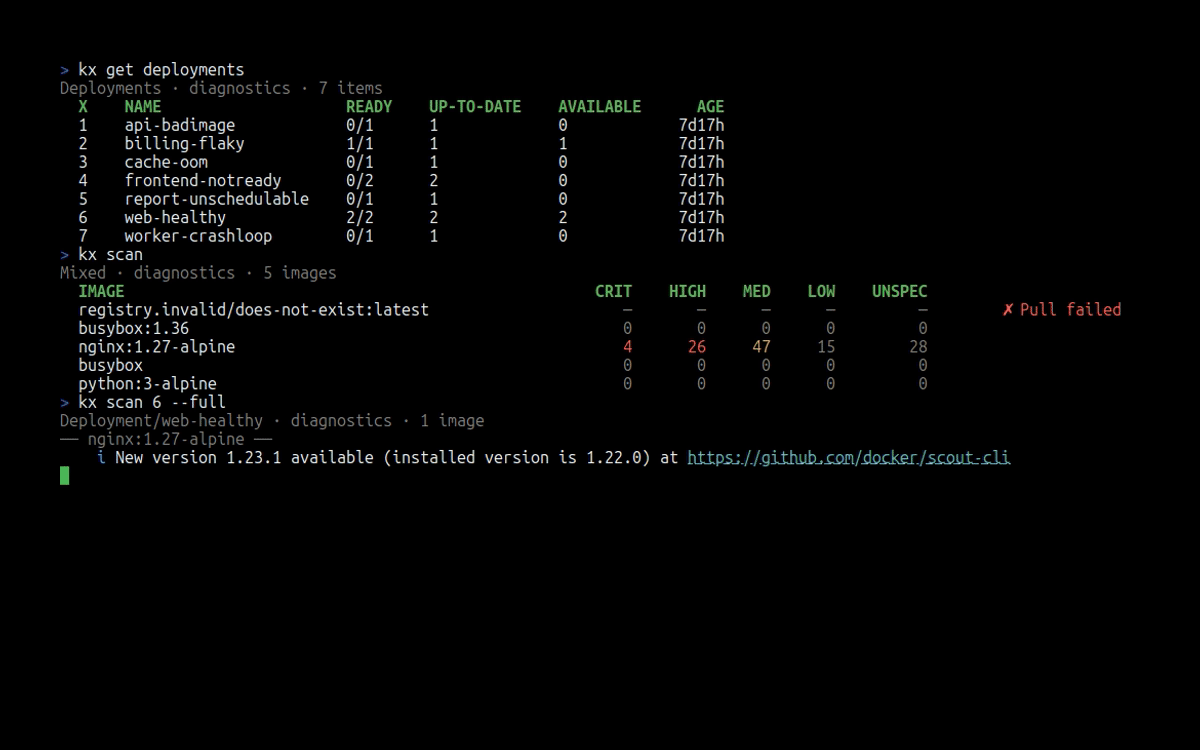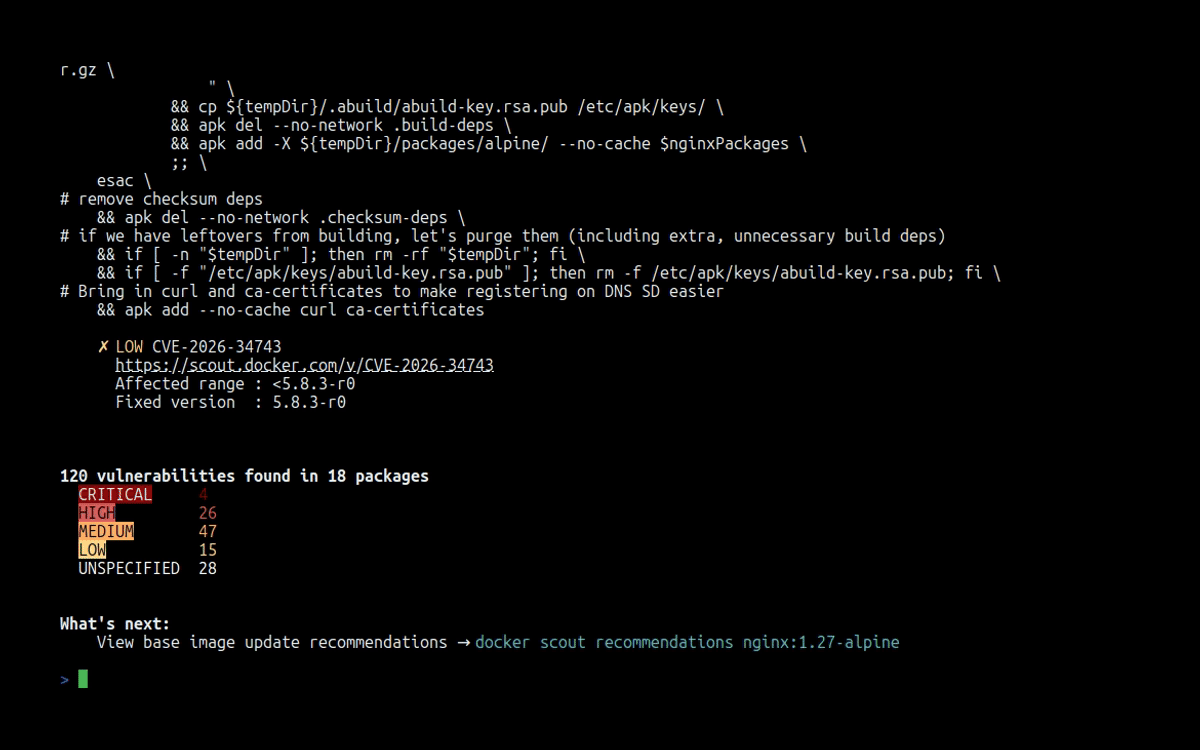
kx scan <index> scans the unique container images of an indexed workload.
Bare kx scan sweeps every workload in the namespace. Results come back as a
severity summary, or the full per-image CVE report with --full.
Requires the CLI for the selected engine — Docker Scout
by default, or Trivy and
Grype via kx engine.
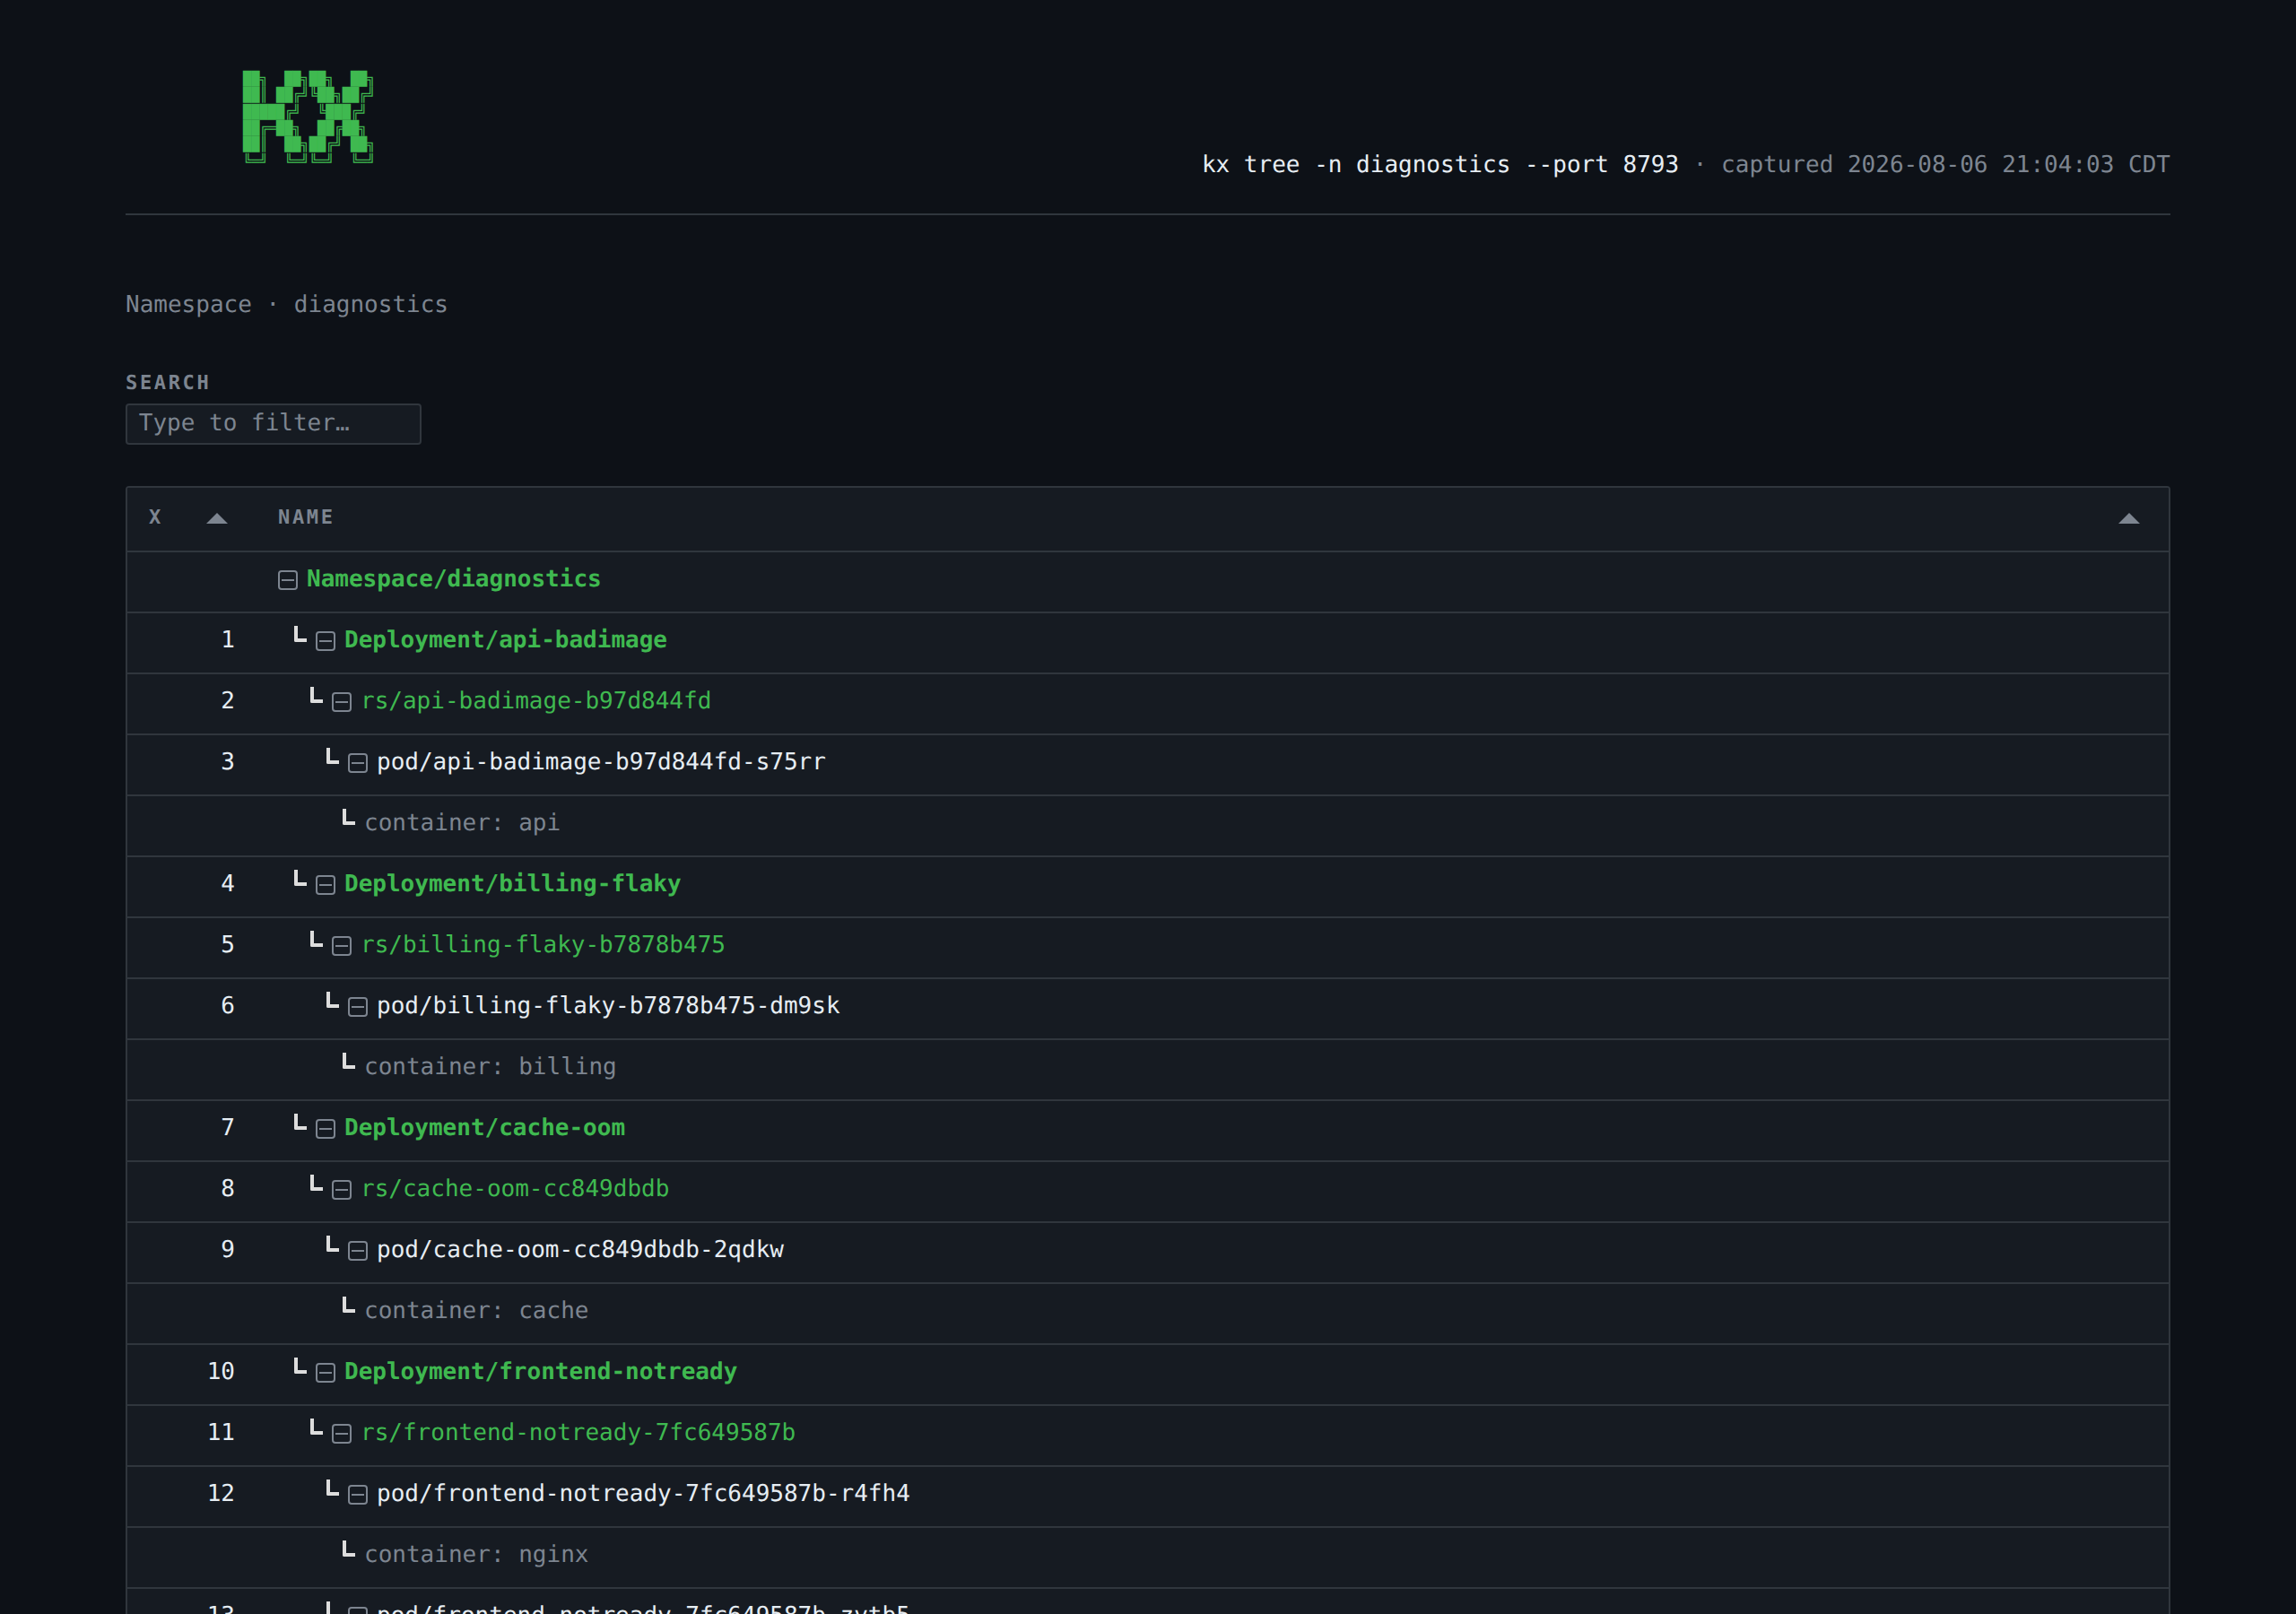
See what owns what
kx tree <index> walks the ownership graph — Deployment to ReplicaSet to Pods —
and indexes every node it draws, so anything in the tree is one number away.
Bare kx tree graphs the whole namespace.
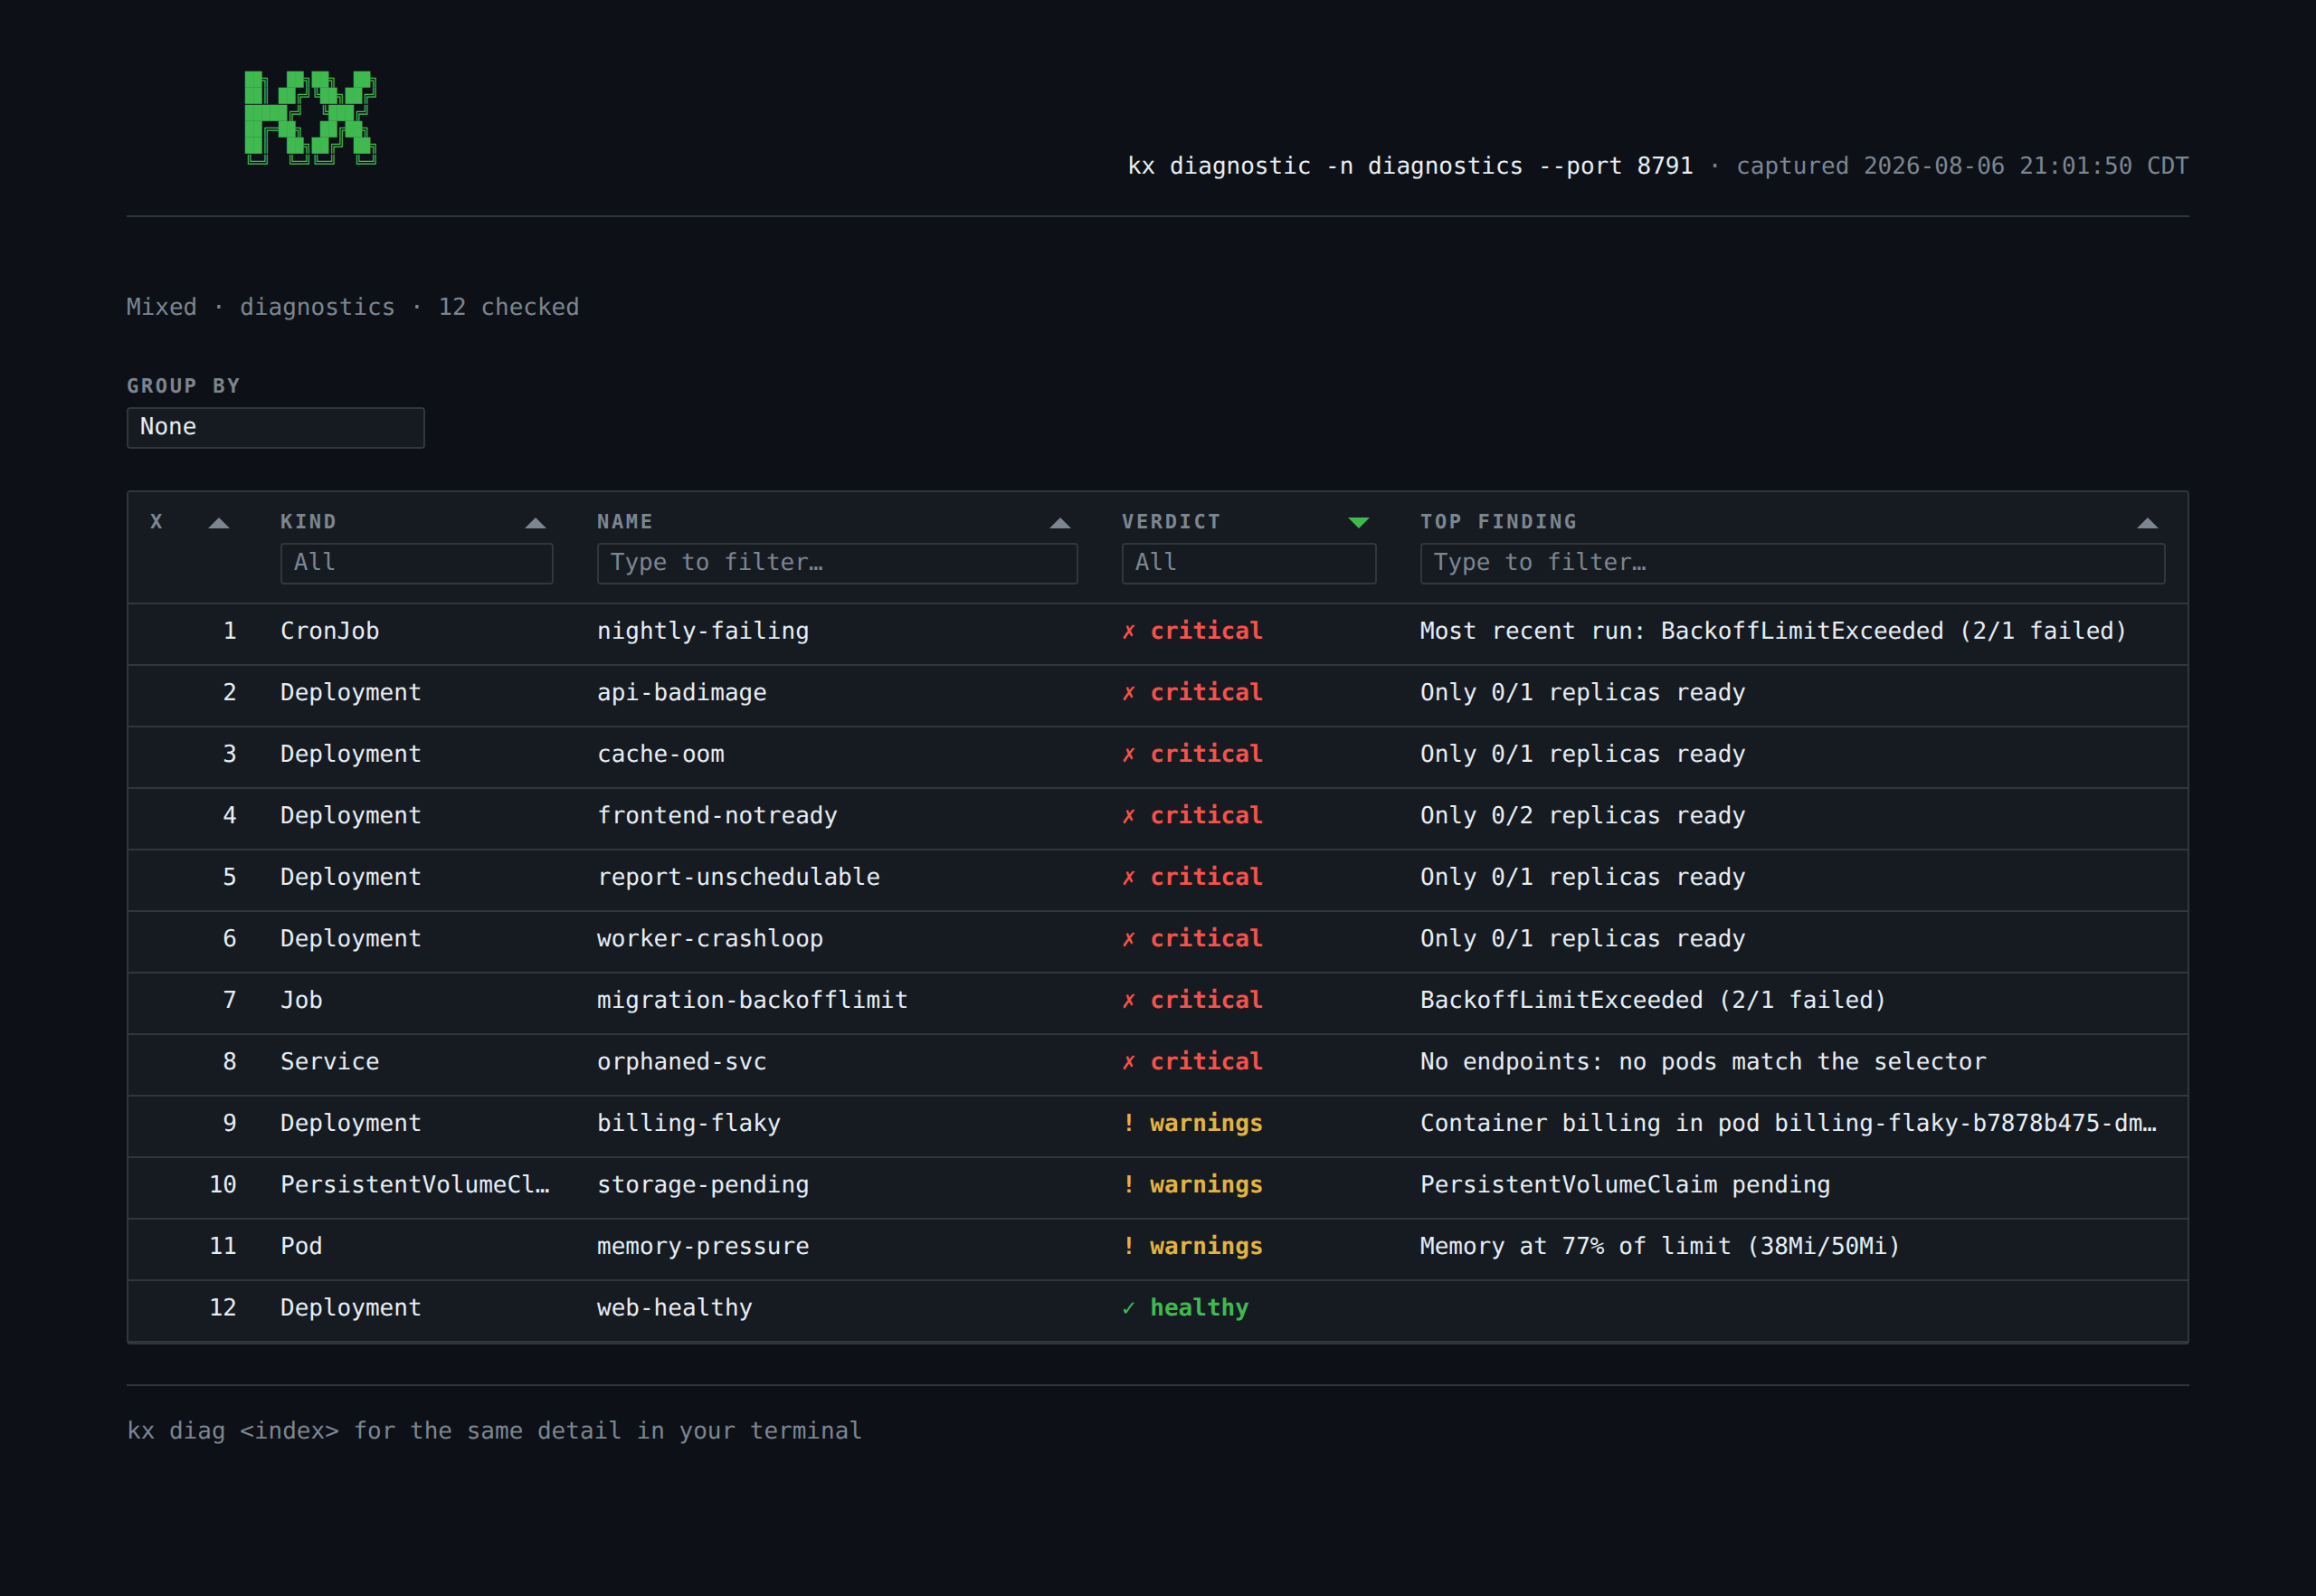
Reports in the browser
--html on kx diag, kx scan, kx tree, and kx top renders the same
analysis as a page and opens it in your browser. It binds 127.0.0.1 only and
writes nothing to disk.
The page is drawn in your active theme. Sweep rows expand into that resource's full report, image rows into the CVEs behind their counts — detail the terminal has no room for.
--out <path> writes the page to a file instead of serving it, which is what
you want in CI — kx diag --out report.html is the whole command.
Use kx in CI
--fail-on <severity> turns a sweep into a build gate, and --json prints the
same analysis as a document for anything downstream.
kx diag -A --fail-on critical                        # 0 if the cluster is healthy, 2 if not
kx scan -A --fail-on high                            # the same, for image vulnerabilities
kx scan -n prod --fail-on high --json | jq '.images[] | select(.counts.critical > 0)'
kx diag -A --fail-on critical --out report.html      # publishes the report *and* fails the build
kx diag -A --fail-on warning --since 24h             # ignore what failed before today
--since bounds how far back the report looks — a warning event, an OOMKill a
container recovered from, a pod or run that failed. Without it a failure from
last month holds the gate red forever. Whatever is still going wrong — a
CrashLoopBackOff, a Pending pod — is reported either way. diag_max_age sets
a window once, for every run.
Exit 2 means findings breached the threshold, 1 means kx itself failed — so a pipeline can tell "the cluster is sick" from "the check never ran".
State and history
kx keeps up to 10 kx get results in ~/.kx/state.json, with a cursor
marking the entry indexes resolve against.
kx state              # the listing indexes currently resolve against
kx state --all        # the whole history, with positions
kx state 2            # jump to position 2
kx state back         # step back one (forward steps the other way)
kx state drop 2       # remove position 2 (--all clears everything, slots included)
Each entry remembers the context it was listed in, so a staging index is never
resolved against production — kx refuses and relists instead. KX_STATE
points kx at a different state file, so a second terminal keeps its own history.
Configuration
kx reads ~/.kx/config.toml, and every setting takes a KX_* environment
override. The two worth changing have commands of their own — kx theme and
kx engine both persist your choice.
Styling is dropped when stdout isn't a terminal, so kx get pods | grep worker
stays clean. NO_COLOR is honored too.
Themes
kx theme lists the available themes with a preview of each. kx theme <name>
persists your choice, by name or index.
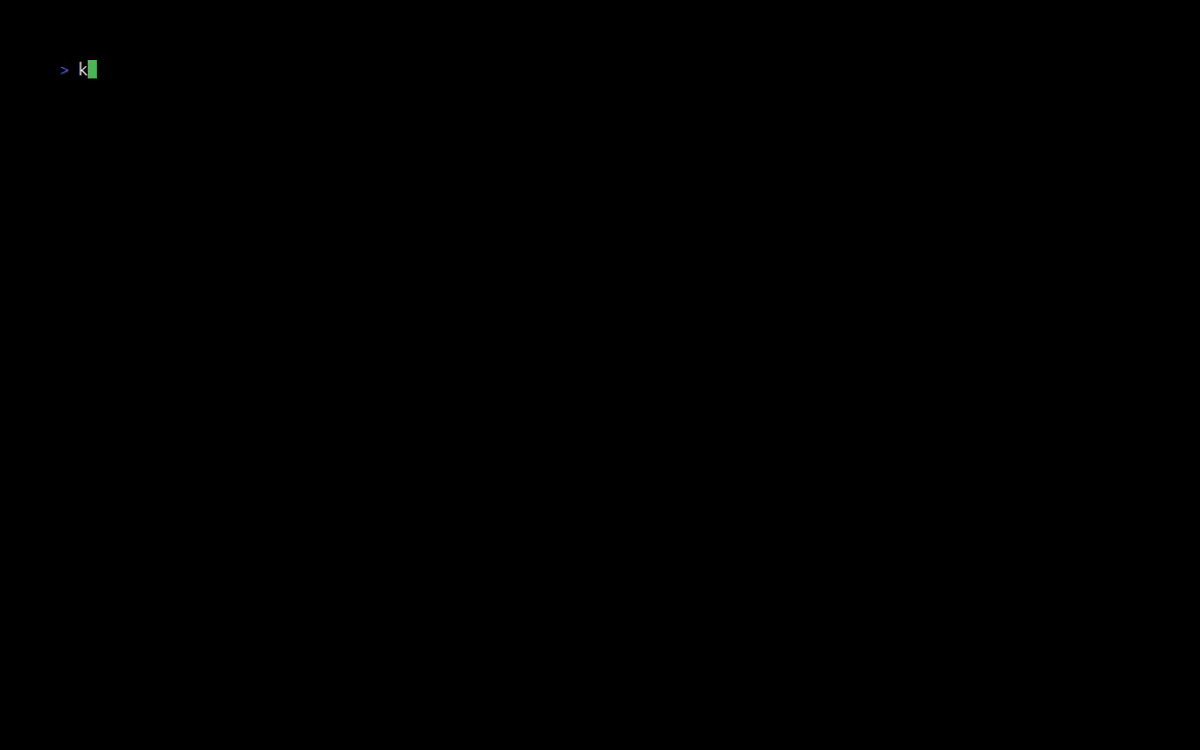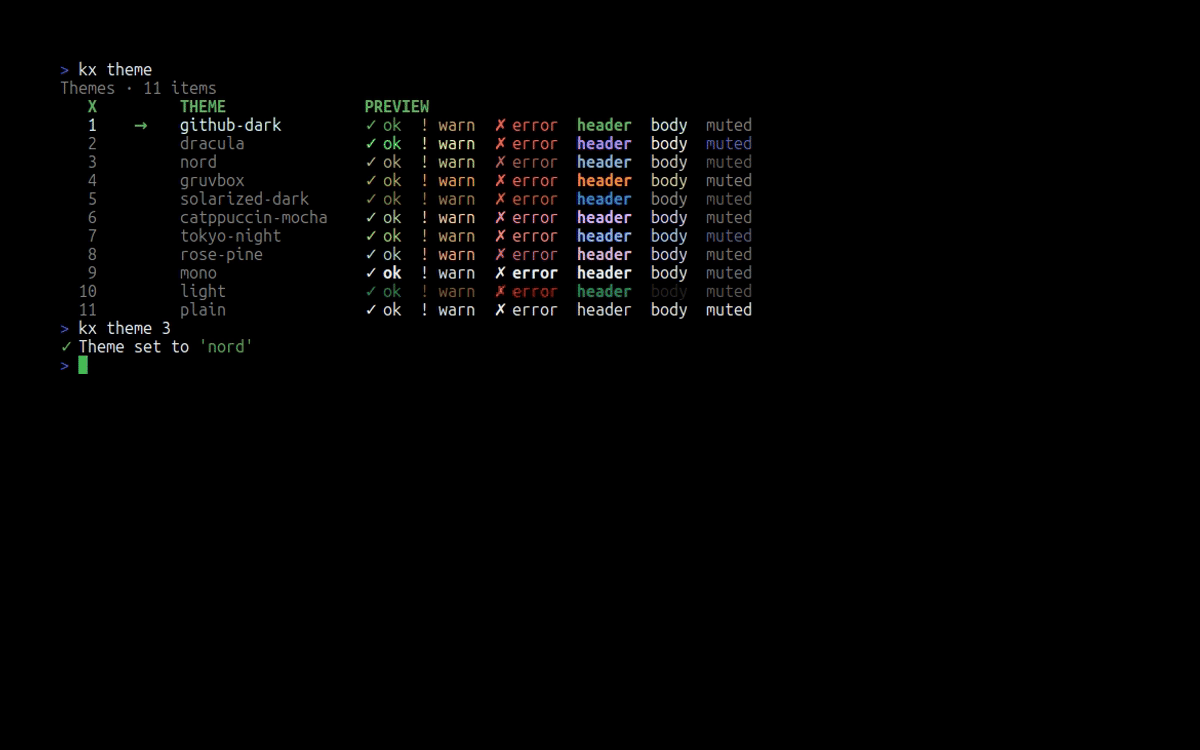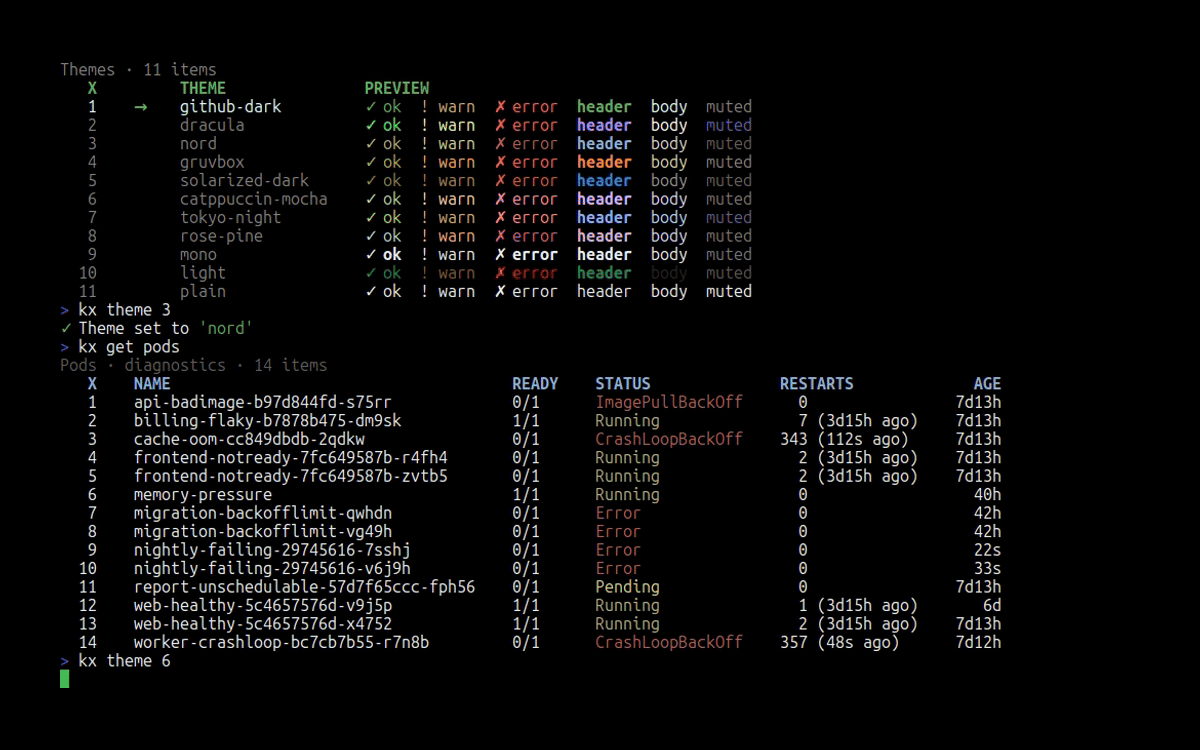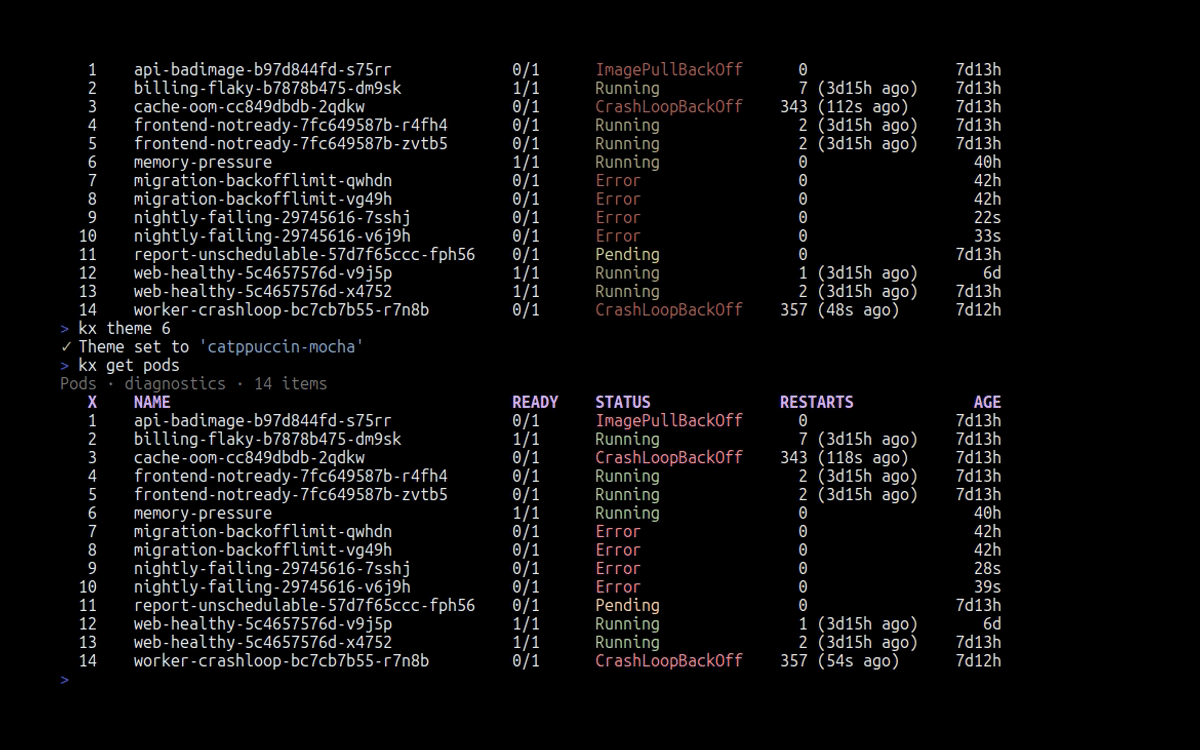
Eleven prefabs ship with it: github-dark (default), dracula, nord,
gruvbox, solarized-dark, catppuccin-mocha, tokyo-night, rose-pine,
mono, light and plain.
Commands
| Command | Description |
|---|---|
kx annotate <index> [<key=value>...] |
Set or remove annotations on an indexed resource. |
kx annotations <index>... |
Show annotations for one or more indexed resources. |
kx context [<index>] |
List kubeconfig contexts, or switch to an indexed one; alias: kx contexts. |
kx cordon <index>... |
Mark one or more indexed Nodes unschedulable. |
kx cp <src> <dest> |
Copy files to or from an indexed pod via kubectl cp. |
kx debug <index> [<command>...] |
Open a debug shell on an indexed Pod (an ephemeral container, for images with no shell) or Node (a privileged pod on the host). |
kx delete <index>... |
Delete one or more indexed resources (prompts for confirmation unless --yes). |
kx describe <index>... |
Show full kubectl describe output for one or more indexed resources. |
kx diagnostic [<index>] |
Diagnose an indexed Deployment, StatefulSet, DaemonSet, Job, CronJob, Service, PersistentVolumeClaim, Ingress, Pod, or Node, or triage a whole namespace when no index is given (-n to pick one, -A for every namespace); alias: kx diag. |
kx drain <index> |
Evict the pods from an indexed Node (prompts for confirmation unless --yes). |
kx edit <index> |
Open an indexed resource in your editor via kubectl edit. |
kx events <index>... |
Show Kubernetes events for one or more indexed resources. |
kx exec <index> [<command>...] |
Open an interactive shell in an indexed Pod, Deployment, ReplicaSet, StatefulSet or DaemonSet (bash, falling back to sh). |
kx get <resource> [<index>...] |
List resources and assign index numbers for use with other commands; shorthand: kx (e.g. kx pods, kx po 3). |
kx label <index> [<key=value>...] |
Set or remove labels on an indexed resource. |
kx labels <index>... |
Show labels for one or more indexed resources; --selector formats output as a label selector. |
kx logs <index>... |
Stream logs for an indexed resource; aggregates across pods for Deployments, StatefulSets, DaemonSets, and Services. |
kx namespace [<index>] |
List namespaces, or switch to an indexed one; alias: kx ns. |
kx port-forward <index> <port> |
Forward a local port to an indexed resource (Pod, Deployment, ReplicaSet, StatefulSet, DaemonSet, Service). |
kx rollout <action> <index> |
Run a rollout action (status, restart, pause, resume, history, undo) on a Deployment, StatefulSet, or DaemonSet. |
kx scale <index> <replicas> |
Scale an indexed Deployment, StatefulSet, or ReplicaSet to a given replica count. |
kx scan [<index>] |
Scan the unique container images of an indexed workload for vulnerabilities, or a whole namespace when no index is given (-n to pick one, -A for every namespace); prints a severity summary table by default, or the raw scanner output with --full. Requires the CLI for the selected scan engine (Docker Scout by default; Trivy or Grype via --engine — see kx engine). |
kx secret [<index>...] |
List Secrets like kx get, or show an indexed Secret's data with --decode; alias: kx secrets. |
kx top [<resource>] |
List CPU/memory usage for pods (default) or nodes and assign index numbers, like kx get; shows usage as a percent of limits (pods) or capacity (nodes) unless --no-limits. |
kx tree [<index>] |
Show the ownership graph for an indexed resource, or the whole current namespace when no index is given (-n to pick one, -A for every namespace); assigns indexes to tree nodes by default. A Namespace index graphs that namespace. |
kx uncordon <index>... |
Mark one or more indexed Nodes schedulable again. |
kx yaml <index>... |
Print the raw YAML manifest for one or more indexed resources; --show filters to specific top-level fields. |
kx state [<position>] |
Show current state, jump to a history position, list all entries with --all, or expand the switch targets with --targets. |
kx engine [<name>] |
List available scan engines or persist a default choice by name or index. |
kx theme [<name>] |
List available color themes or persist a choice by name or index. |
kx completion |
Generate a shell completion script for kx (bash, zsh, fish, powershell). |
Development
Go, at the version pinned by the go directive in go.mod. Nothing else is
required to build or run.
go build ./...
go run ./cmd/kx --help              # run the CLI directly
gofmt -l ./cmd ./internal ./tools   # must print nothing
go vet ./...
go test -race ./...
pre-commit run --all-files runs gofmt and go vet, and regenerates the command
table above from the command tree — it fails if the table has drifted from the
commands it documents. Tests are not in the hook — run them yourself.
The demo GIFs are rendered from VHS
tapes — see demo/README.md for seeding the demo namespace
and re-recording.
1 maintainer

Metadata
1 maintainer
Release files for kx-cli 0.5.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Built distributions (wheels)
| File | Reset | |||
|---|---|---|---|---|
| kx_cli-0.5.1-py3-none-win_arm64.whl | Python 3 | none | Windows ARM64 | Details |
| kx_cli-0.5.1-py3-none-win_amd64.whl | Python 3 | none | Windows x86-64 | Details |
| kx_cli-0.5.1-py3-none-musllinux_1_2_x86_64.whl | Python 3 | none | Linux musl 1.2+ x86-64 | Details |
| kx_cli-0.5.1-py3-none-musllinux_1_2_aarch64.whl | Python 3 | none | Linux musl 1.2+ ARM64 | Details |
| kx_cli-0.5.1-py3-none-manylinux_2_17_x86_64.whl | Python 3 | none | Linux glibc 2.17+ x86-64 | Details |
| kx_cli-0.5.1-py3-none-manylinux_2_17_aarch64.whl | Python 3 | none | Linux glibc 2.17+ ARM64 | Details |
| kx_cli-0.5.1-py3-none-macosx_11_0_arm64.whl | Python 3 | none | macOS 11.0+ ARM64 | Details |
| kx_cli-0.5.1-py3-none-macosx_10_9_x86_64.whl | Python 3 | none | macOS 10.9+ x86-64 | Details |
Total release size: 410.6 MB
Release files / kx_cli-0.5.1-py3-none-win_arm64.whl
| Download URL | kx_cli-0.5.1-py3-none-win_arm64.whl |
|---|---|
| Size | 49.6 MB |
| Tags | Python 3 Windows ARM64 |
|
SHA-256 checksum How to use checksums |
fcd1b3c5a02a0bc0186227aa8c6ebac6372727214dc5ffc052b19c2f2ca47742
|
|
BLAKE2b-256 checksum How to use checksums |
ebafc772027c688d9630cfb41c35aab6e7d0ace22f7a362258be958b2f17379f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Release files / kx_cli-0.5.1-py3-none-win_amd64.whl
| Download URL | kx_cli-0.5.1-py3-none-win_amd64.whl |
|---|---|
| Size | 53.8 MB |
| Tags | Python 3 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
b3555d3c1b06a5491de1afa9f89f9342a8ded2b9c25aa0dfe64370cd7b9603d9
|
|
BLAKE2b-256 checksum How to use checksums |
26b3d690cb722730e0cbfa6d536c549efe4f38a227601b9b11e038855f8817eb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Release files / kx_cli-0.5.1-py3-none-musllinux_1_2_x86_64.whl
| Download URL | kx_cli-0.5.1-py3-none-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 52.5 MB |
| Tags | Linux musl 1.2+ x86-64 Python 3 |
|
SHA-256 checksum How to use checksums |
f5098f56c1a3393bcac803c58050c4657b02a5eafe1d10b4557c405f22735fc9
|
|
BLAKE2b-256 checksum How to use checksums |
9c730eca2541917bfd607191fee869d8f256c8d8b25e59cb3155c828b25f090d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Release files / kx_cli-0.5.1-py3-none-musllinux_1_2_aarch64.whl
| Download URL | kx_cli-0.5.1-py3-none-musllinux_1_2_aarch64.whl |
|---|---|
| Size | 49.1 MB |
| Tags | Linux musl 1.2+ ARM64 Python 3 |
|
SHA-256 checksum How to use checksums |
6ed5a00ace2ae494365bf3d3325f7598186c777c5b98fd6b0df284b96a766a8d
|
|
BLAKE2b-256 checksum How to use checksums |
e457493e47da81acc476fee976b7d933bea1402b6ad6298a19ea6fd0e803edac
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Release files / kx_cli-0.5.1-py3-none-manylinux_2_17_x86_64.whl
| Download URL | kx_cli-0.5.1-py3-none-manylinux_2_17_x86_64.whl |
|---|---|
| Size | 52.5 MB |
| Tags | Linux glibc 2.17+ x86-64 Python 3 |
|
SHA-256 checksum How to use checksums |
dce18365dddcc8e3bc0671c140489f7706381c56fb8cd940fa649bc99a3f4ac4
|
|
BLAKE2b-256 checksum How to use checksums |
fa203dbc633c60667e73124030fa79c1dba2c4b5c0dcbfbc05a40926ee2d1a50
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Release files / kx_cli-0.5.1-py3-none-manylinux_2_17_aarch64.whl
| Download URL | kx_cli-0.5.1-py3-none-manylinux_2_17_aarch64.whl |
|---|---|
| Size | 49.1 MB |
| Tags | Linux glibc 2.17+ ARM64 Python 3 |
|
SHA-256 checksum How to use checksums |
780cb077befdbbcf3fb954e115db25dd8b03ab72e63448757723786f62fccdae
|
|
BLAKE2b-256 checksum How to use checksums |
065c3c98ad37c70404d57d27e14f6527cad2609bfc7590238d5791855a9f9ec6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Release files / kx_cli-0.5.1-py3-none-macosx_11_0_arm64.whl
| Download URL | kx_cli-0.5.1-py3-none-macosx_11_0_arm64.whl |
|---|---|
| Size | 50.5 MB |
| Tags | Python 3 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
767d9f1ccde4f635fcd49b32a535ca7be6484b0db7e01d071b2dfbb97aafa9eb
|
|
BLAKE2b-256 checksum How to use checksums |
d6b20b018b6b4f3b05e9844c916aaa03c680463ed96797a5f4ceb941d13c61e8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Release files / kx_cli-0.5.1-py3-none-macosx_10_9_x86_64.whl
| Download URL | kx_cli-0.5.1-py3-none-macosx_10_9_x86_64.whl |
|---|---|
| Size | 53.6 MB |
| Tags | Python 3 macOS 10.9+ x86-64 |
|
SHA-256 checksum How to use checksums |
9d5063ed77000e78e3176e42f3afd7efeb3150fb5559aa789cc42c14d518192a
|
|
BLAKE2b-256 checksum How to use checksums |
ab414fe5f39c1ba4557fd2d1c1028b7732c205aa10fba8eda6fa30fe9e85dc5a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.3
|
Security for kx-cli 0.5.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














