
liquiphy_gui
A quick and dirty GUI interface to the liquidsfz command-line using python's subprocess.
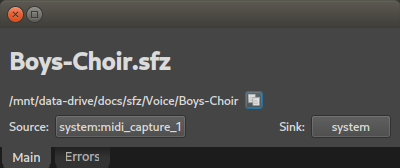
Need to listen to an .sfz file without a lot of hassle? Use liquiphy_gui!
$ liquiphy-gui <path-to-sfz>
The above command loads the given .sfz file in a liquidsfz instance and
automatically connects the Jack MIDI input and Jack audio outputs to the first
available (physical) ports, displaying the SFZ name and ports connected in a
simple dialog.
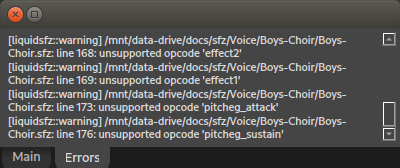
Errors that liquidsfsz reported during parsing show up in the "Errors" tab:
Hit the Escape key or ctrl-Q to exit.
Install
Install liquidsfz
You must install liquidsfz first for this package to work. To install:
- Make sure you have all the build dependencies:
$ sudo apt install \
	automake autoconf autoconf-archive libtool \
	libjack-jackd2-dev libreadline-dev lv2-dev libsndfile1-dev \
	libgl-dev libxrandr-dev libxcursor-dev libxext-dev
- Clone the repo:
$ git clone https://github.com/swesterfeld/liquidsfz.git
- Ensure the repo's submodules exist and are up-to-date. Enter the repo dir and update:
$ cd liquidsfz
$ git submodule update --init --recursive
- Run the autogen script found in the repo directory:
$ ./autogen.sh
- Then, do the configure, make, install routine:
./configure
make
make install
Install liquiphy_gui
Install this package (liquiphy_gui) using python pip:
$ pip install liquiphy_gui
...or...
$ python3 -m pip install liquiphy_gui
File associations
If you would like to open .sfz files in liquiphy-gui by double-clicking them in your file explorer, you can add an association.
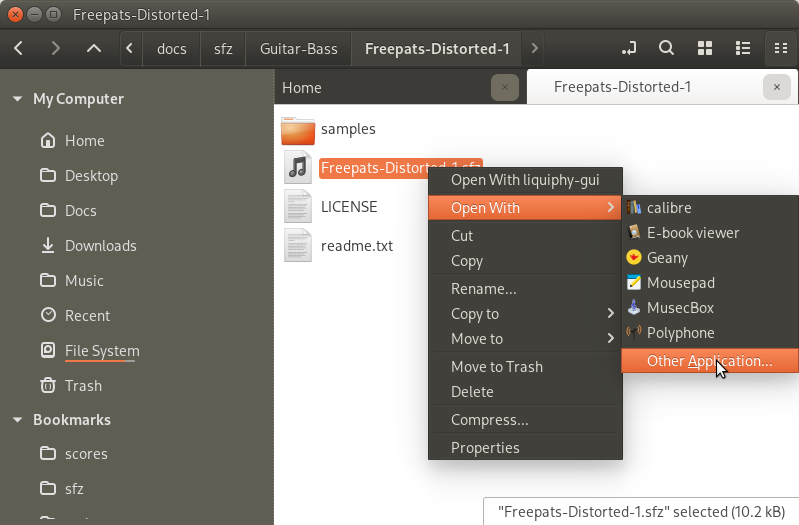
-
Right click on an .sfz file to bring up the context menu.
-
Select "Open With", and then "Other Application"
- In the dialog show, look for "liquiphy-gui" in the list of applications, and then click "Set as default".
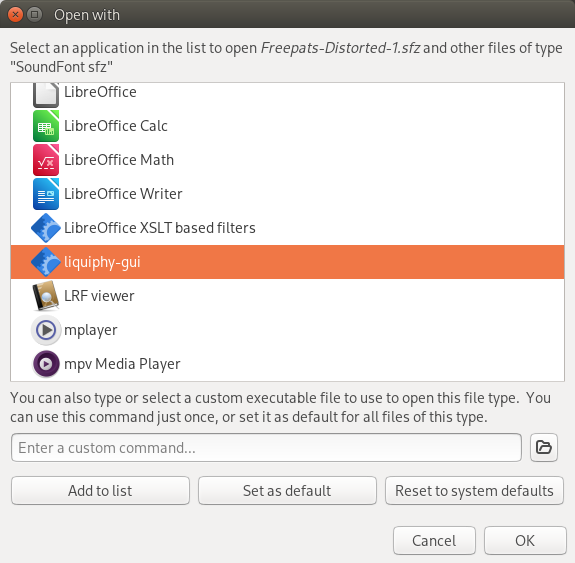
Now, all it takes to preview an .sfz is double-clicking on it. Jack ports are instantly connected, and you have your live preview.
1 maintainer

Metadata
1 maintainer
Release files for liquiphy-gui 1.5.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| liquiphy_gui-1.5.2.tar.gz | 16.8 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| liquiphy_gui-1.5.2-py2.py3-none-any.whl | Python 3, Python 2 | none | any | Details |
Total release size: 34.4 kB
Release files / liquiphy_gui-1.5.2.tar.gz
| Download URL | liquiphy_gui-1.5.2.tar.gz |
|---|---|
| Size | 16.8 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
7964c3abf6701f303c2760cbfefdb086ebefe181a956e59119f0ccc1fa22e4cc
|
|
BLAKE2b-256 checksum How to use checksums |
09ad6b99395d4ab837e11d0c49bcd17027587aafee286d20f2bb7236253ce775
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/6.2.0 CPython/3.14.4
|
Release files / liquiphy_gui-1.5.2-py2.py3-none-any.whl
| Download URL | liquiphy_gui-1.5.2-py2.py3-none-any.whl |
|---|---|
| Size | 17.6 kB |
| Tags | Python 2 Python 3 |
|
SHA-256 checksum How to use checksums |
3678b240f94301e0a24a78400954331f5c4a23c45ffbd057c6d3b95cc69a5951
|
|
BLAKE2b-256 checksum How to use checksums |
44475ae3dad683edf3087f117520eb2bb74701131184744900120e8bef495b17
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/6.2.0 CPython/3.14.4
|
Security for liquiphy-gui 1.5.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














