
LocalDeploy
Choose, run, and compare local AI models on your own hardware.


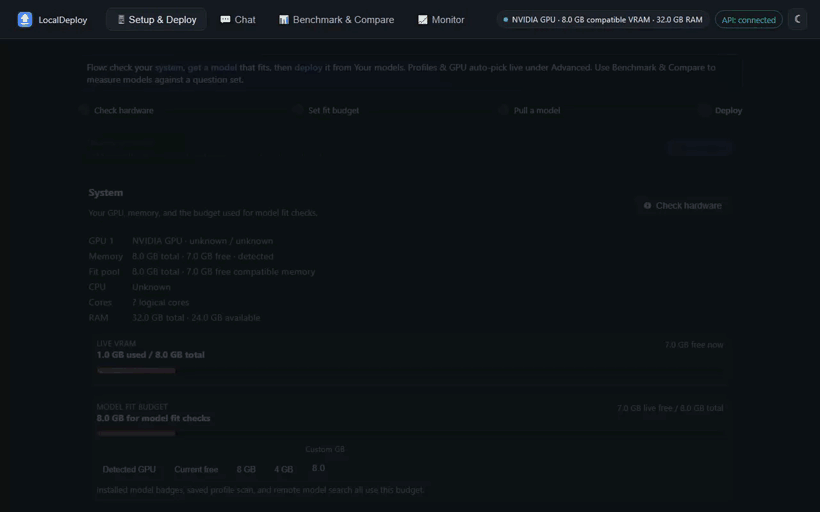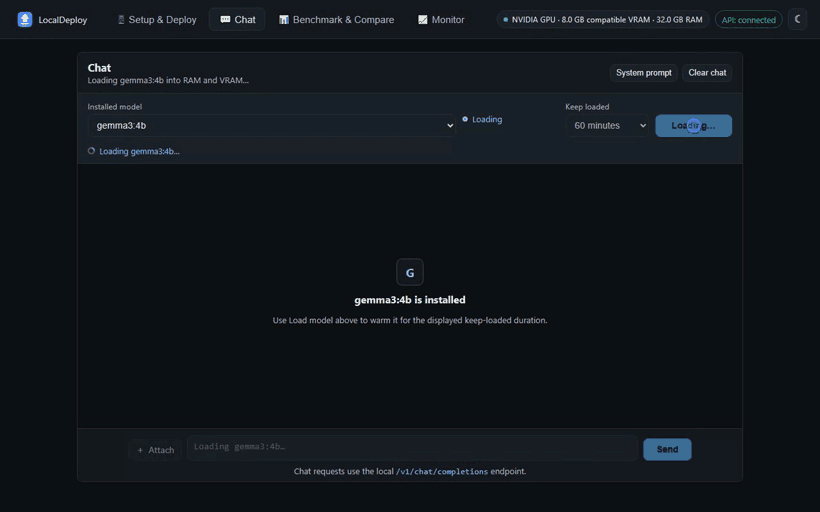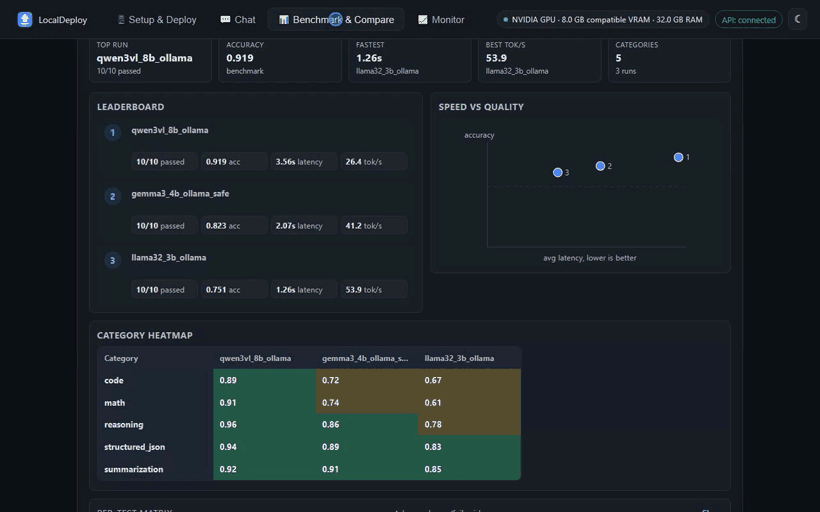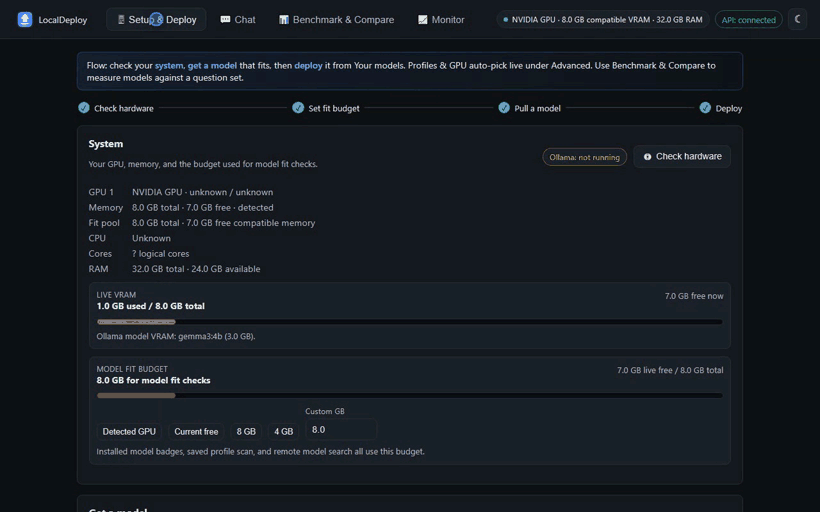
LocalDeploy helps you answer a practical question before you download a model: will it fit and run well on this machine? It detects hardware, estimates memory use, manages local models, records benchmarks, and serves the deployed model through an OpenAI-compatible API. It runs locally, has no telemetry, and does not provide cloud inference.
Quick start
With Python 3.10+ and Ollama installed:
pip install localdeploy
localdeploy        # opens http://localhost:8000/ui
The UI guides you through hardware detection, model search, a fit estimate,
deployment, chat, and benchmarking. If you use uv, uvx localdeploy runs it
without a permanent install.
Need help setting up Python or Ollama? Clone the repository and run its launcher:
git clone https://github.com/oney-erge/LocalDeploy.git
cd LocalDeploy
./run.sh           # Linux; macOS: ./run.command
On Windows, use run.bat. The launchers can prepare the environment and open
the UI; Installation covers prerequisites, Docker, and the
Windows setup script. Desktop builds are experimental and unsigned; see
Packaging.
What it helps with
- Find models from Ollama, Hugging Face, ModelScope GGUF repositories, local GGUF files, or direct URLs.
- Estimate model fit before download, including likely CPU offload.
- Pull, deploy, switch, unload, and remove local models.
- Chat with text, images, and documents, then compare installed models using measured latency, throughput, memory, and accuracy results.
- Monitor CPU, RAM, VRAM, model placement, and request timing while a model runs.
- Connect compatible tools through
/v1/chat/completions,/v1/responses,/v1/embeddings, and/v1/models.
If you already know which Ollama model you want and only need terminal chat, Ollama may be enough. LocalDeploy is for selecting and evaluating models on a particular machine.
What to expect
Fit estimates are guidance, not guarantees. Driver versions, context length, quantization, desktop GPU use, and the runtime all affect actual memory use. LocalDeploy records what happened after deployment so later estimates can be adjusted for that machine.
It works with Ollama, llama.cpp, LM Studio, vLLM, and other loopback
OpenAI-compatible runtimes. Runtime URLs must remain local. An API_TOKEN
is an optional shared token, not full authentication. Keep the service on
localhost; it has no TLS, user isolation, or rate limiting. Tool calls are
returned to clients and are never executed by LocalDeploy.
Model search and the UI's release check can contact external services.
Set OFFLINE=true to disable those requests. Separately installed runtimes
have their own network settings; see Security.
Documentation
| Guide | Use it for |
|---|---|
| Installation | Launcher commands, Docker, and setup alternatives |
| UI guide | Choosing, deploying, chatting with, and benchmarking models |
| API options | OpenAI-compatible API and local integrations |
| CLI | Commands and automation |
| Models | Runtimes, model discovery, and fit estimates |
| Screenshots | The complete UI tour |
| Packaging | Experimental desktop builds and signing limitations |
| Contributing | Development setup and verification |
MIT licensed. Built by Oney Erge.
1 maintainer

Metadata
1 maintainer
Release files for localdeploy 0.6.3
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| localdeploy-0.6.3.tar.gz | 272.9 kB | With provenance | Details for localdeploy-0.6.3.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| localdeploy-0.6.3-py3-none-any.whl | Python 3 | none | any | Details for localdeploy-0.6.3-py3-none-any.whl |
Total release size: 547.0 kB
Release files / localdeploy-0.6.3.tar.gz
| Download URL | localdeploy-0.6.3.tar.gz |
|---|---|
| Size | 272.9 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
78be6edc04cabff400725d5c1977c1eea826d7cd9630528b2af9a83edde1ca1e
|
|
BLAKE2b-256 checksum How to use checksums |
f1f8339ecdf17c2c75ecf511b108442aaf4a0594a93fa127efb594eed6a7807b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 22, 2026.
Transparency logRelease files / localdeploy-0.6.3-py3-none-any.whl
| Download URL | localdeploy-0.6.3-py3-none-any.whl |
|---|---|
| Size | 274.0 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
22d0789f8ee37798ffb1af727ec67302d359b764c37a8aeac8e5d95b737fd6b7
|
|
BLAKE2b-256 checksum How to use checksums |
e1208d3edac7a2bef8bbbdb23bf7ee69283dc995fe639d867dc6ce3b2caefb00
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 22, 2026.
Transparency logSecurity for localdeploy 0.6.3
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for localdeploy-0.6.3.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 22, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














