
macuse
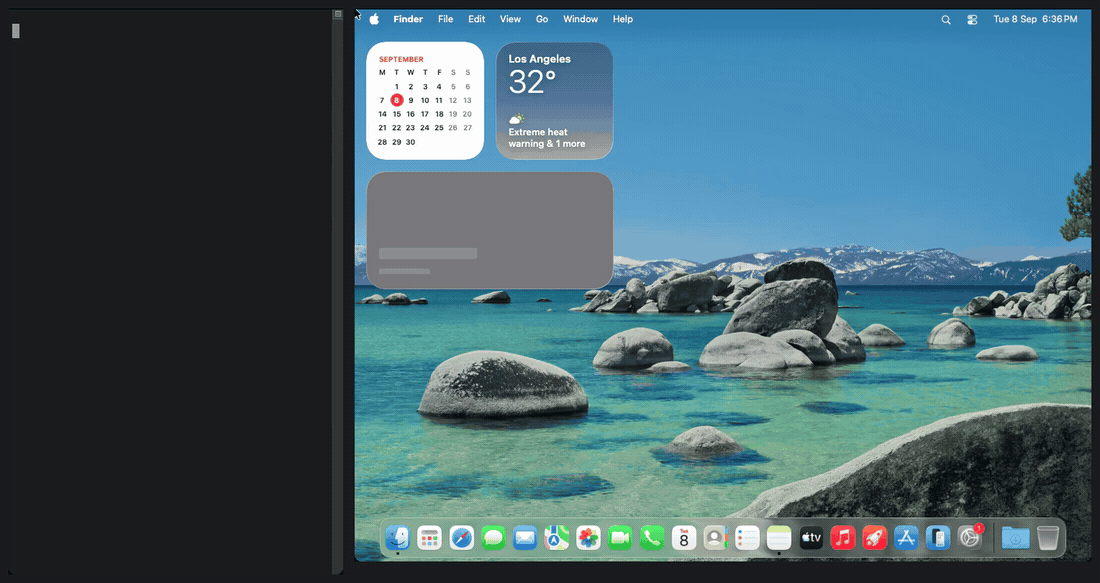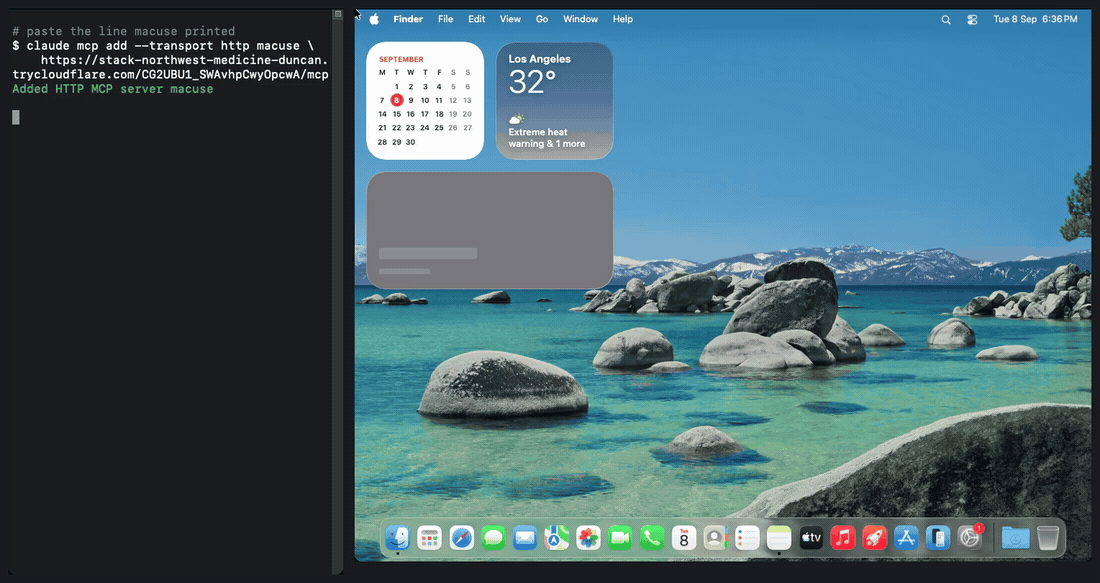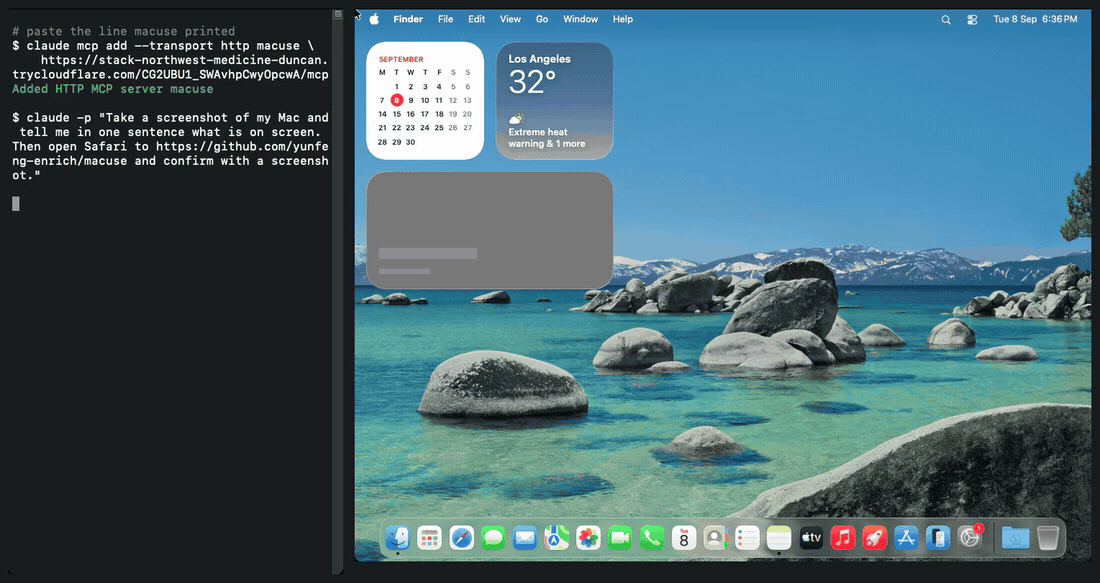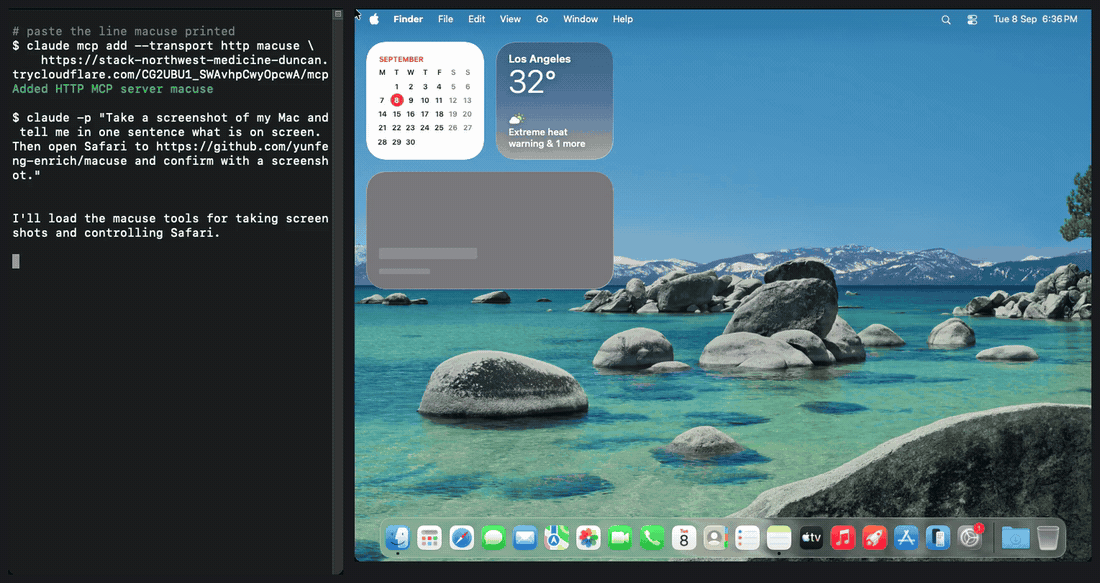
Left: Claude Code, anywhere. Right: a Mac running macuse up. The agent reaches it only through the printed URL.
Turn your Mac into a remote computer-use host. One command on the Mac, one paste into Claude Code or Codex, and the agent can see your screen, click, type, and open apps.
Built on CUA's computer-server for the macOS driver.
macuse adds the parts that make it safe to reach from outside: a bearer token, a tool
allowlist that hides shell and filesystem access by default, a Cloudflare quick tunnel,
keep-awake, and a permissions preflight.
Quick start
uvx macuse up
Or without uv installed:
curl -fsSL https://raw.githubusercontent.com/yunfeng-enrich/macuse/main/install.sh | sh
Either way macuse fetches cloudflared on first run and starts the server. It prints one line to paste into your agent, plus the one-line commands:
claude mcp add --transport http macuse https://<host>/<token>/mcp
codex mcp add macuse --url https://<host>/<token>/mcp
The token lives in the URL so no client needs custom headers. Authorization: Bearer <token>
against https://<host>/mcp works too.
Permissions
macOS grants Screen Recording and Accessibility per app, and the app is whichever
terminal launched macuse. The first run triggers both prompts. Screen Recording only
takes effect after that terminal is fully quit and reopened. Without it, screenshots
are black and window titles are empty. Check with:
macuse check
What is exposed
By default: screenshot, mouse, keyboard, clipboard, windows, app launch, and the accessibility tree. Not exposed unless you ask:
--allow-shelladdscomputer_run_command--allow-filesadds file read, write, and delete tools
Other flags: --no-tunnel for LAN or SSH-forwarded use, --width/--height to scale
screenshots and coordinates for the model, --port, --token.
Security
This is your real desktop on a public URL. The token is the only lock, and it is in the
URL, so treat the URL like a password. Both the hostname and the token are new on every
run, so a leaked URL stops working the moment you Ctrl-C. Keep the terminal visible while
an agent is connected. Pass --token only if you need a fixed one.
Status
Spike. Works end to end on macOS 15 with Claude Code over a Cloudflare tunnel. Not yet: signed menu bar app, persistent tunnel hostnames, per-app allowlists, Lume VM sandbox mode.
1 maintainer

Metadata
1 maintainer
Release files for macuse 0.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| macuse-0.1.0.tar.gz | 1.3 MB | Without provenance | Details for macuse-0.1.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| macuse-0.1.0-py3-none-any.whl | Python 3 | none | any | Details for macuse-0.1.0-py3-none-any.whl |
Total release size: 1.3 MB
Release files / macuse-0.1.0.tar.gz
| Download URL | macuse-0.1.0.tar.gz |
|---|---|
| Size | 1.3 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
d6e46db987e90cd2bae33cf1bb893f89559cdde758f986c5182b1dee827321da
|
|
BLAKE2b-256 checksum How to use checksums |
2f34fd325c8127bcfaff519db3a81964e71d57cf3b12051b9b30fe8d83663ba6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
uv/0.8.22
|
Release files / macuse-0.1.0-py3-none-any.whl
| Download URL | macuse-0.1.0-py3-none-any.whl |
|---|---|
| Size | 10.8 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
43753a723b0749c9a856bda10282c376a3b5c74116754e06068ef0443352a21b
|
|
BLAKE2b-256 checksum How to use checksums |
d7b0d2db5e947b80bc6ae1f0087b1d2c6d360c86e00d7997626ac9312f625526
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
uv/0.8.22
|
Security for macuse 0.1.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













