
Mara Mondrian


A python interface for Mondrian Server, a Mondrian XMLA server combined with the Saiku ad hoc analysis tool. Comes with
-
A Makefile for running Mondrian Server locally.
-
Mondrian schema generation from a Mara Schema definition.
-
Mondrian cache flushing.
-
Saiku authentication via Mara ACL.
Installation
To use the library directly, use pip:
pip install mara-mondrian
or
pip install git+https://github.com/mara/mara-mondrian.git
For an example of an integration into a flask application, have a look at the mara example project 1.
Running Saiku
From within a project, include .scripts/mondrian-server.mk in your project Makefile (as for example in https://github.com/mara/mara-example-project-1/blob/master/Makefile).
Running make setup-mondrian-server will create the required mondrian-server.properties file. And then running make run-mondrian-server will start Saiku and the XMLA server on port 8080:
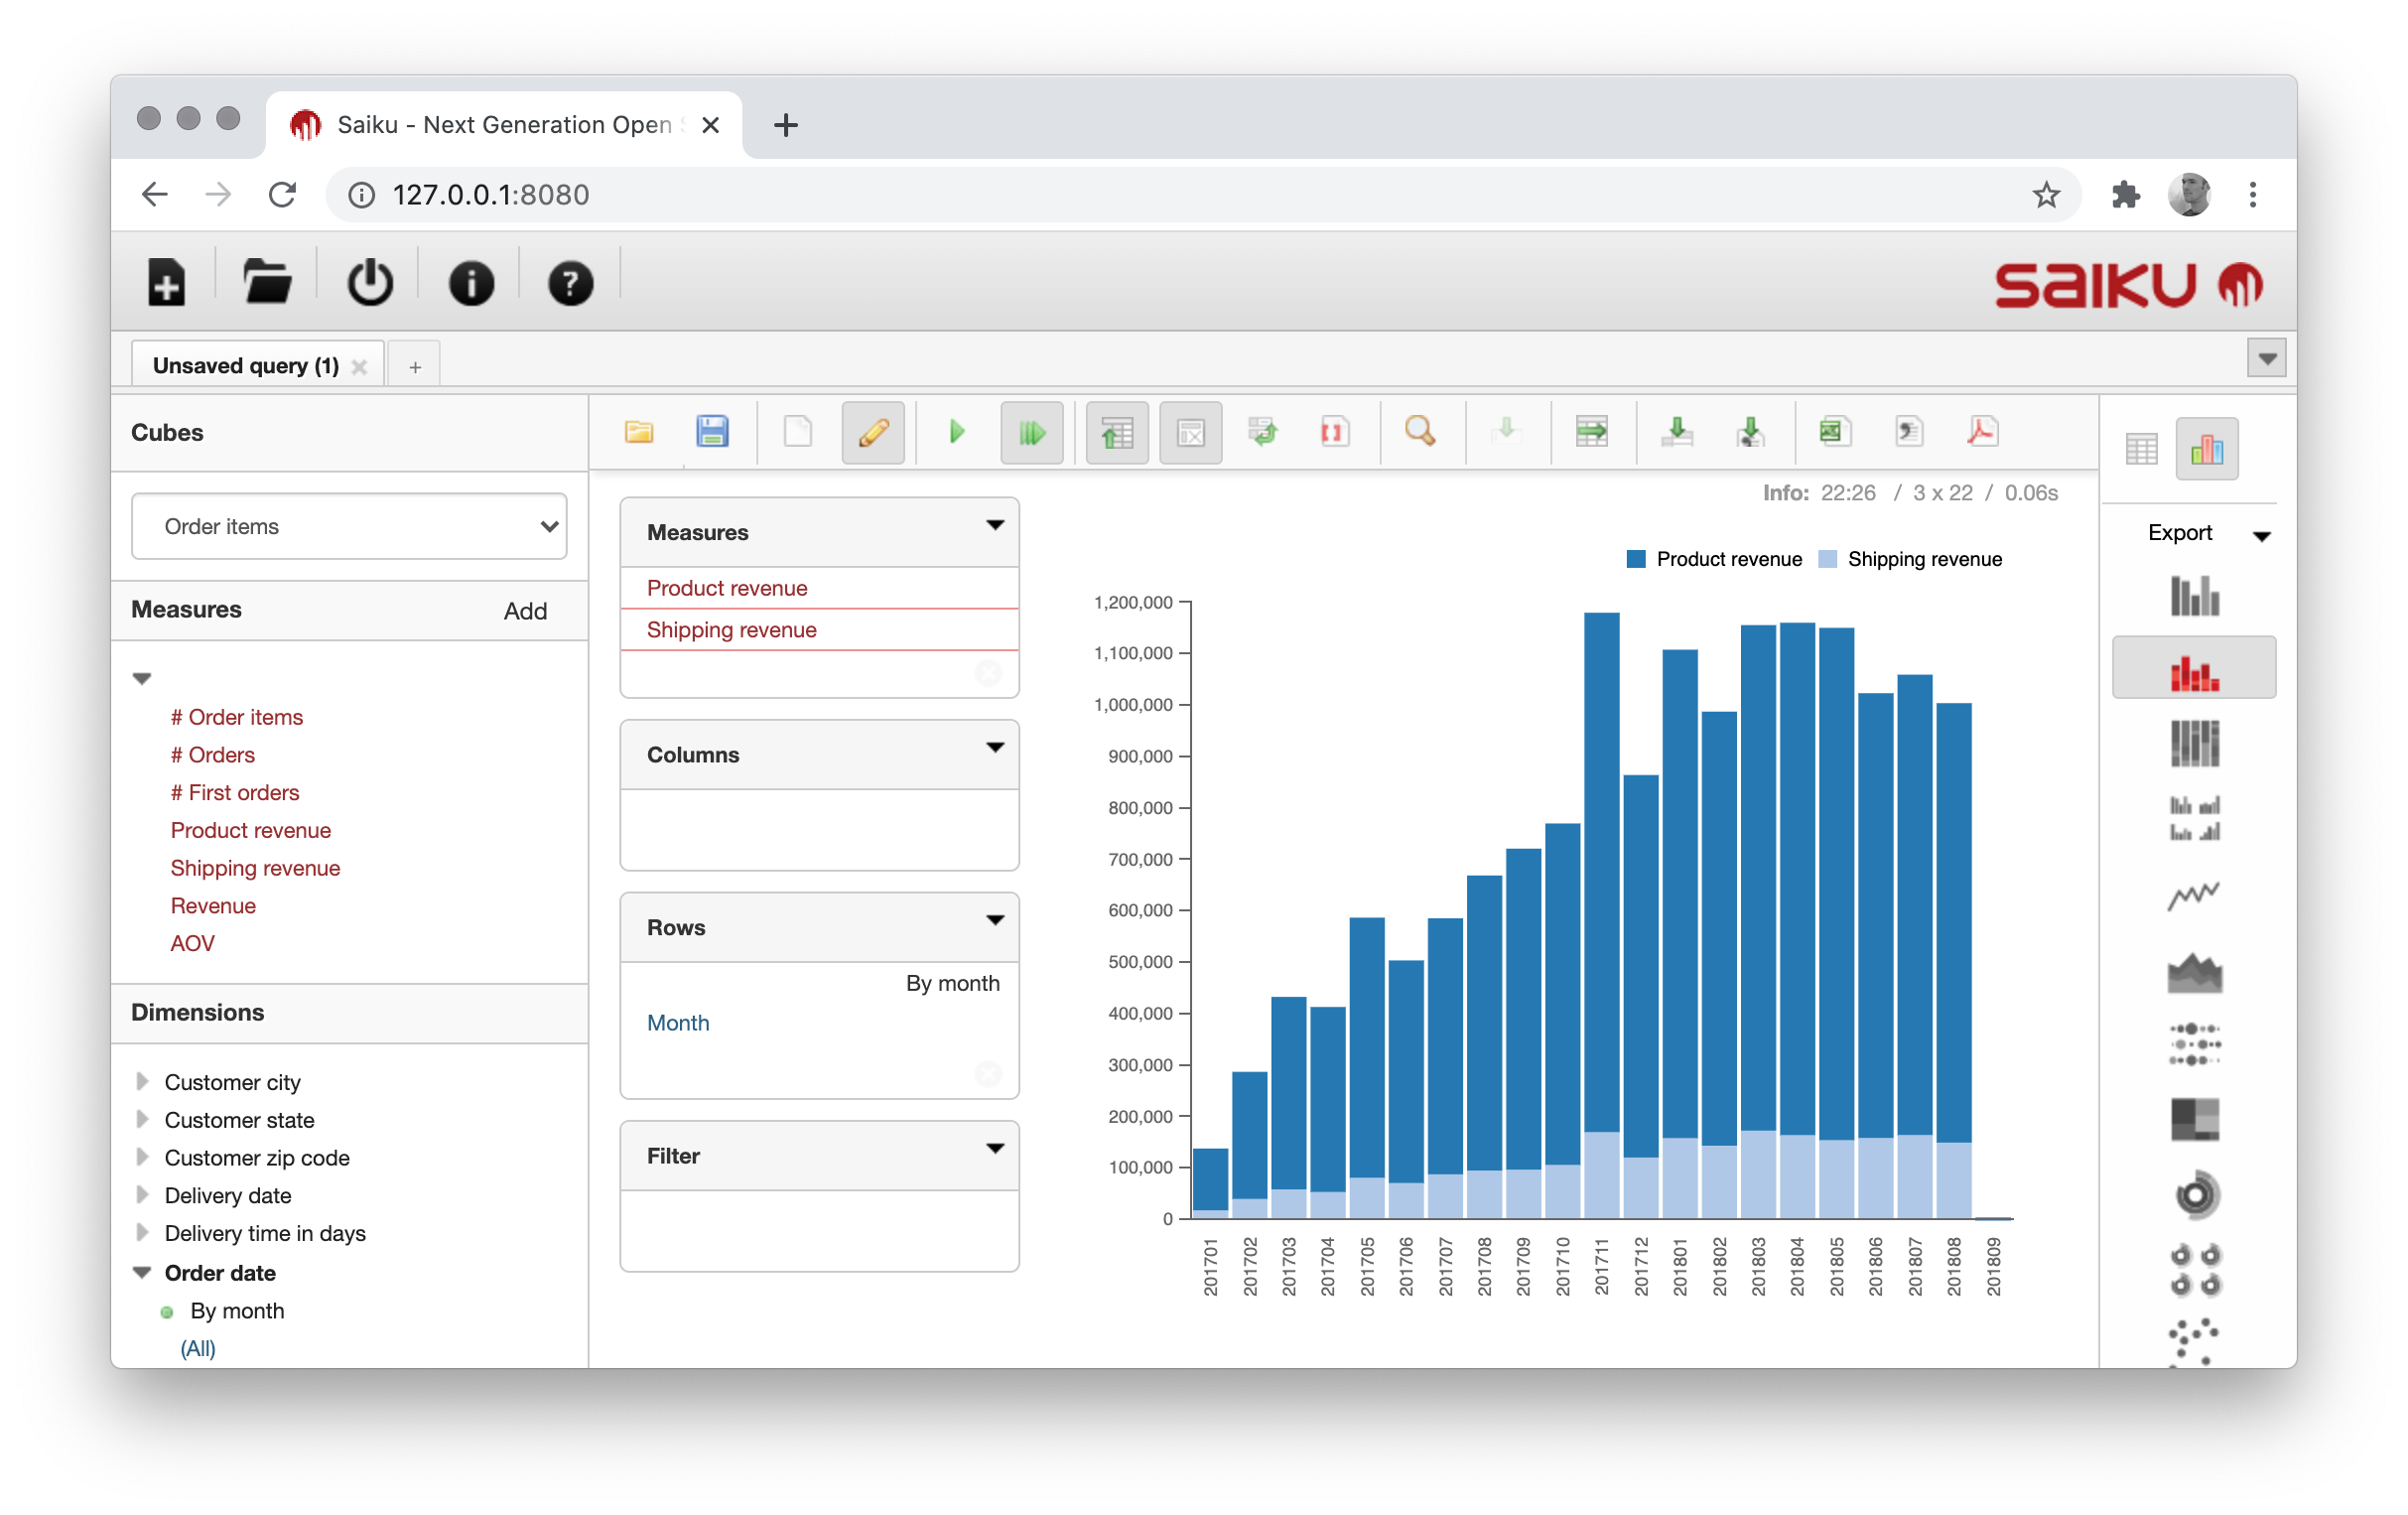
For running Mondrian Server in production, please have a look at https://github.com/project-a/mondrian-server/blob/master/README.md.
Features
Mondrian schema generation
If you have a data warehouse schema defined in Mara Schema, then you can automatically create a Mondrian schema file using the function write_mondrian_schema in mara_mondrian/schema_generation.py.
Have a look at https://github.com/mara/mara-example-project-1/blob/master/app/pipelines/update_frontends/__init__.py for an example.
Mondrian cache flushing
The function flush_mondrian_cache in mara_mondrian/connection.py triggers a reload of the schema and a flushing of all caches in Mondrian Server.
This file also contains functions for making XMLA requests.
Saiku authentication via Mara ACL
Once you add the Saiku ACL resource in mara_mondrian/views.py to your project, you can easily control which users can query which cubes:
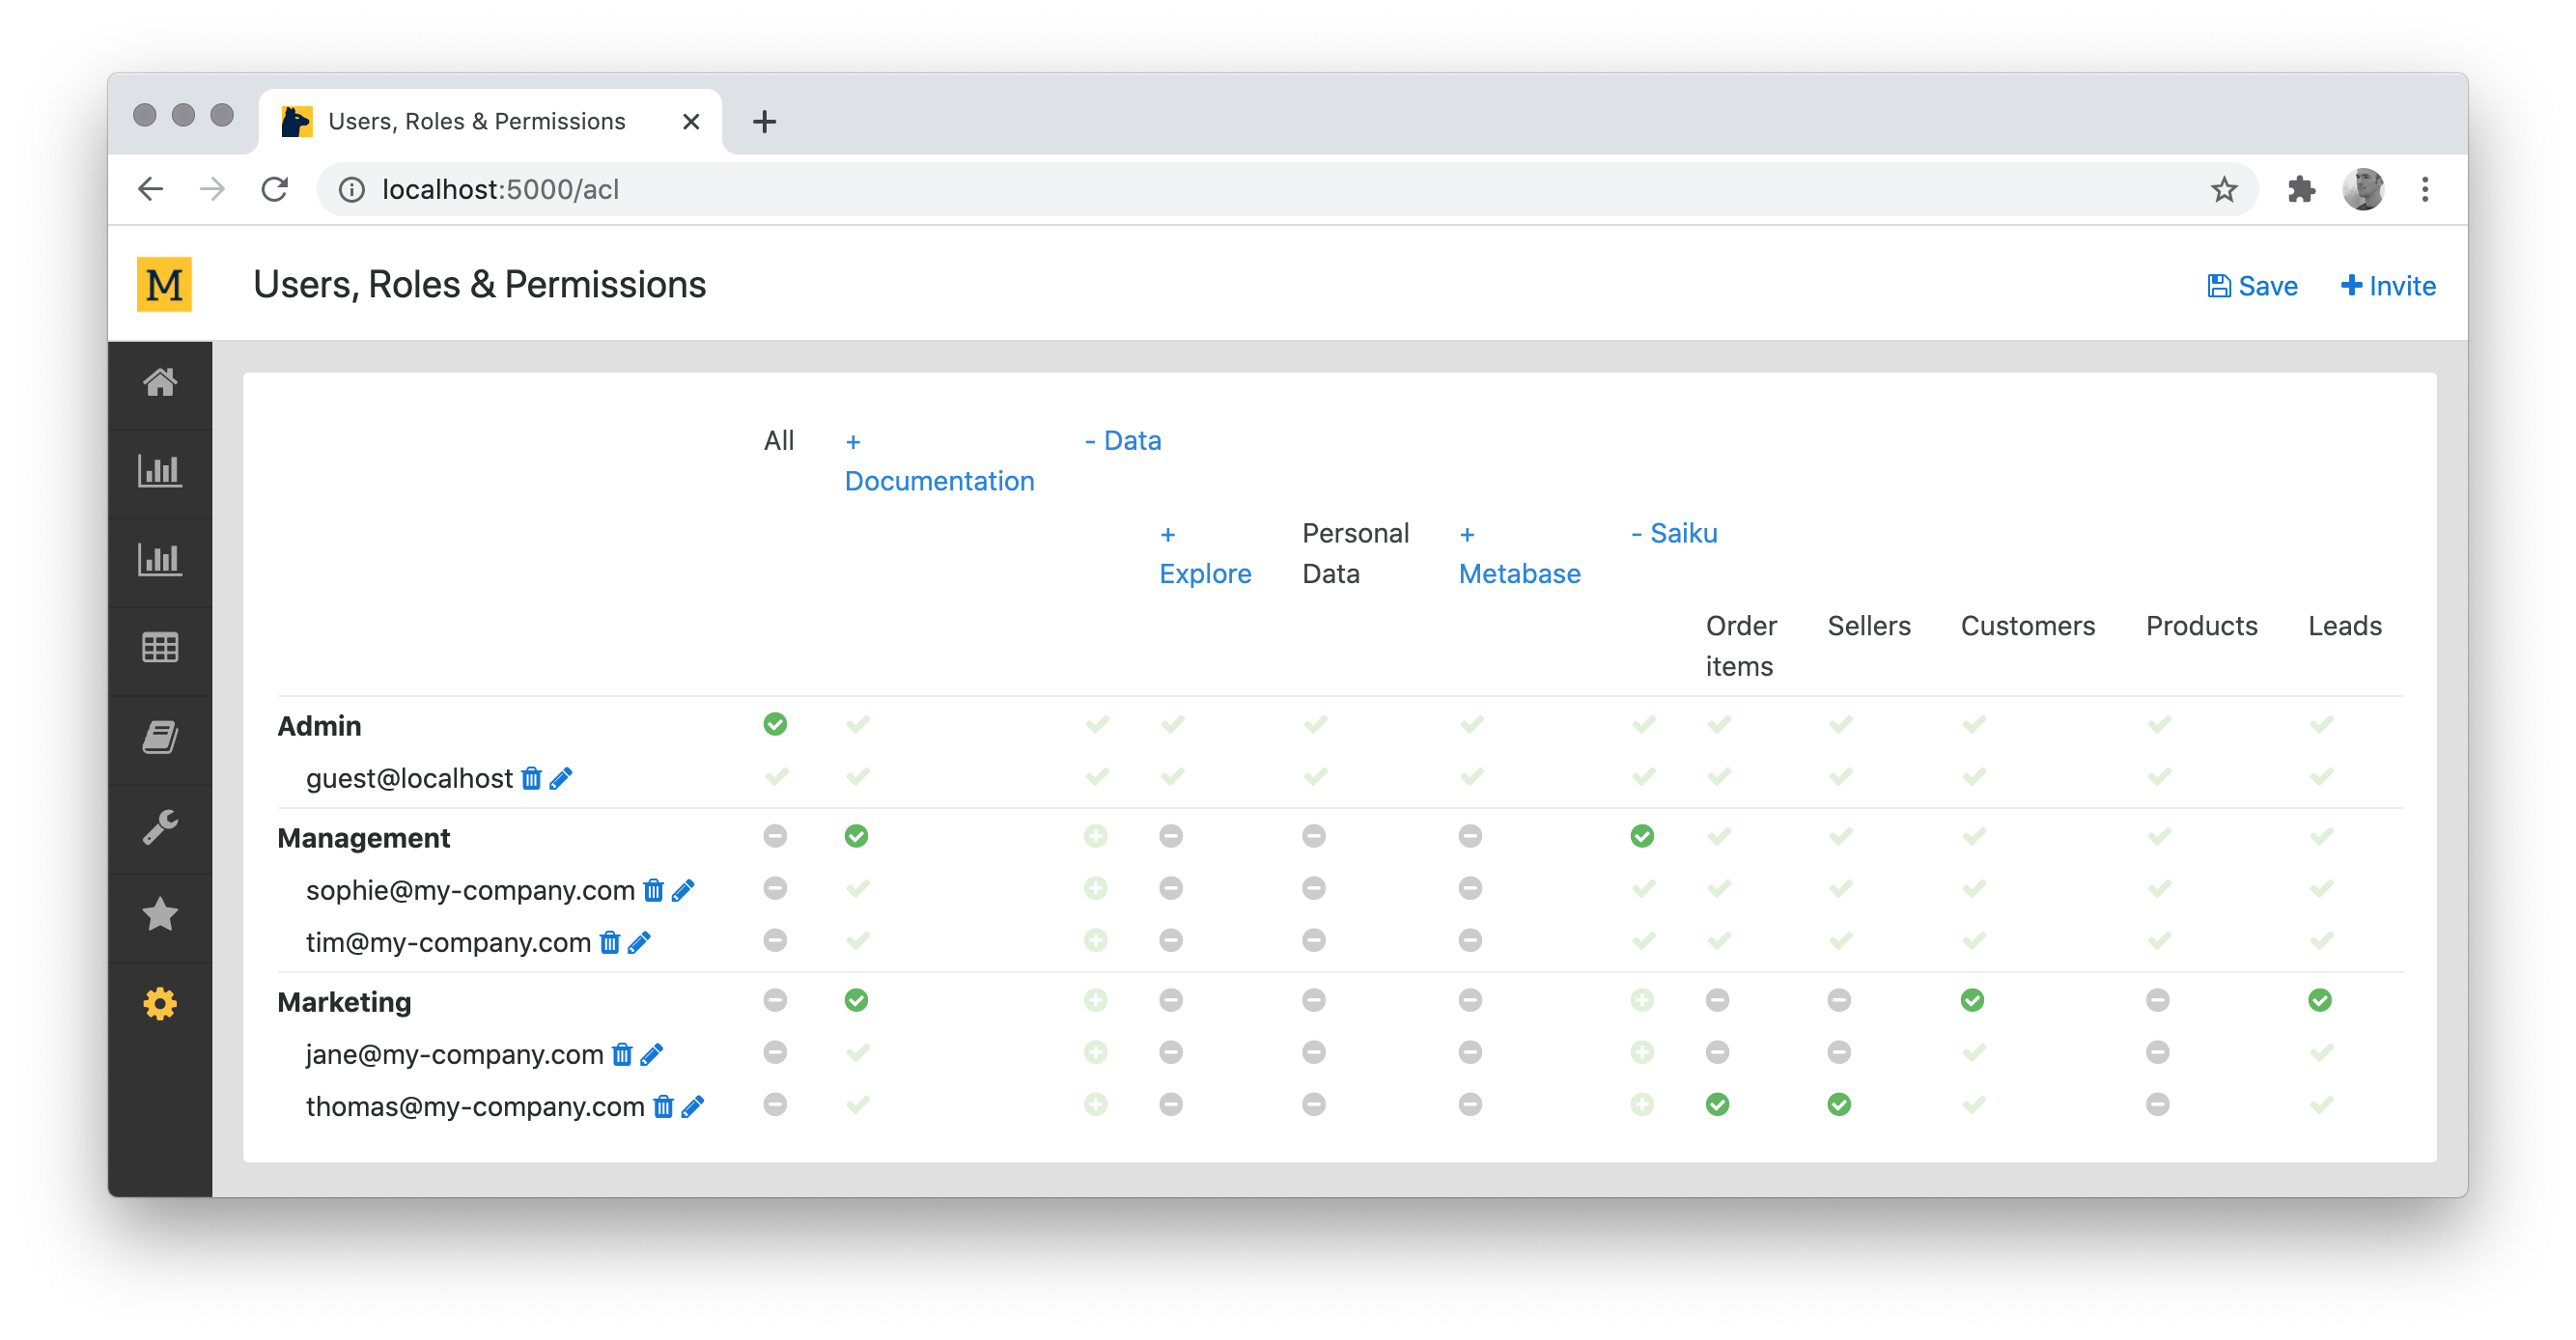
In this example, users from the "Management" group can query all cubes, and users from "Marketing" only "Customers" and "Leads" (with the exception of Thomas who can also query "Order items" and "Sellers").
Please have a look at https://github.com/project-a/mondrian-server/blob/master/README.md for how to set this up.
Please make sure that the /mondrian/saiku/authorize endpoint is white-listed from the Mara ACL, as for example in https://github.com/mara/mara-example-project-1/blob/master/app/ui/__init__.py:
monkey_patch.patch(mara_acl.config.whitelisted_uris)(lambda: ['/mara-app/navigation-bar', '/mondrian/saiku/authorize'])
The easiest way to try out Mara Mondrian is to run the mara example project 1.
2 maintainers


Metadata
2 maintainers
Release files for mara-mondrian 2.0.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| mara-mondrian-2.0.2.tar.gz | 81.2 MB | Without provenance | Details for mara-mondrian-2.0.2.tar.gz |
Release files / mara-mondrian-2.0.2.tar.gz
| Download URL | mara-mondrian-2.0.2.tar.gz |
|---|---|
| Size | 81.2 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
8625bf384e7f41db46e6ac483fafae61c1f96dad92ff461bef6df87542f08d16
|
|
BLAKE2b-256 checksum How to use checksums |
10e77fc246b97784cccabbd7d6389fcf5c8363edf3ba0d814d5d091c7d989119
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.3.0 pkginfo/1.7.0 requests/2.25.1 setuptools/51.3.3 requests-toolbelt/0.9.1 tqdm/4.56.0 CPython/3.7.1
|
Security for mara-mondrian 2.0.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














