

🕵️ MEDS-Inspect




MEDS (Medical Event Data Standard) is "the simplest possible standard for health AI" (https://medical-event-data-standard.github.io/).
But after building your own MEDS ETL you might be wondering:
- Is my ETL missing data?
- What codes are contained in my dataset?
- How does my data compare to other MEDS datasets?
- What preprocessing steps are still needed in order to train models?
.. and many more questions related to data exploration.
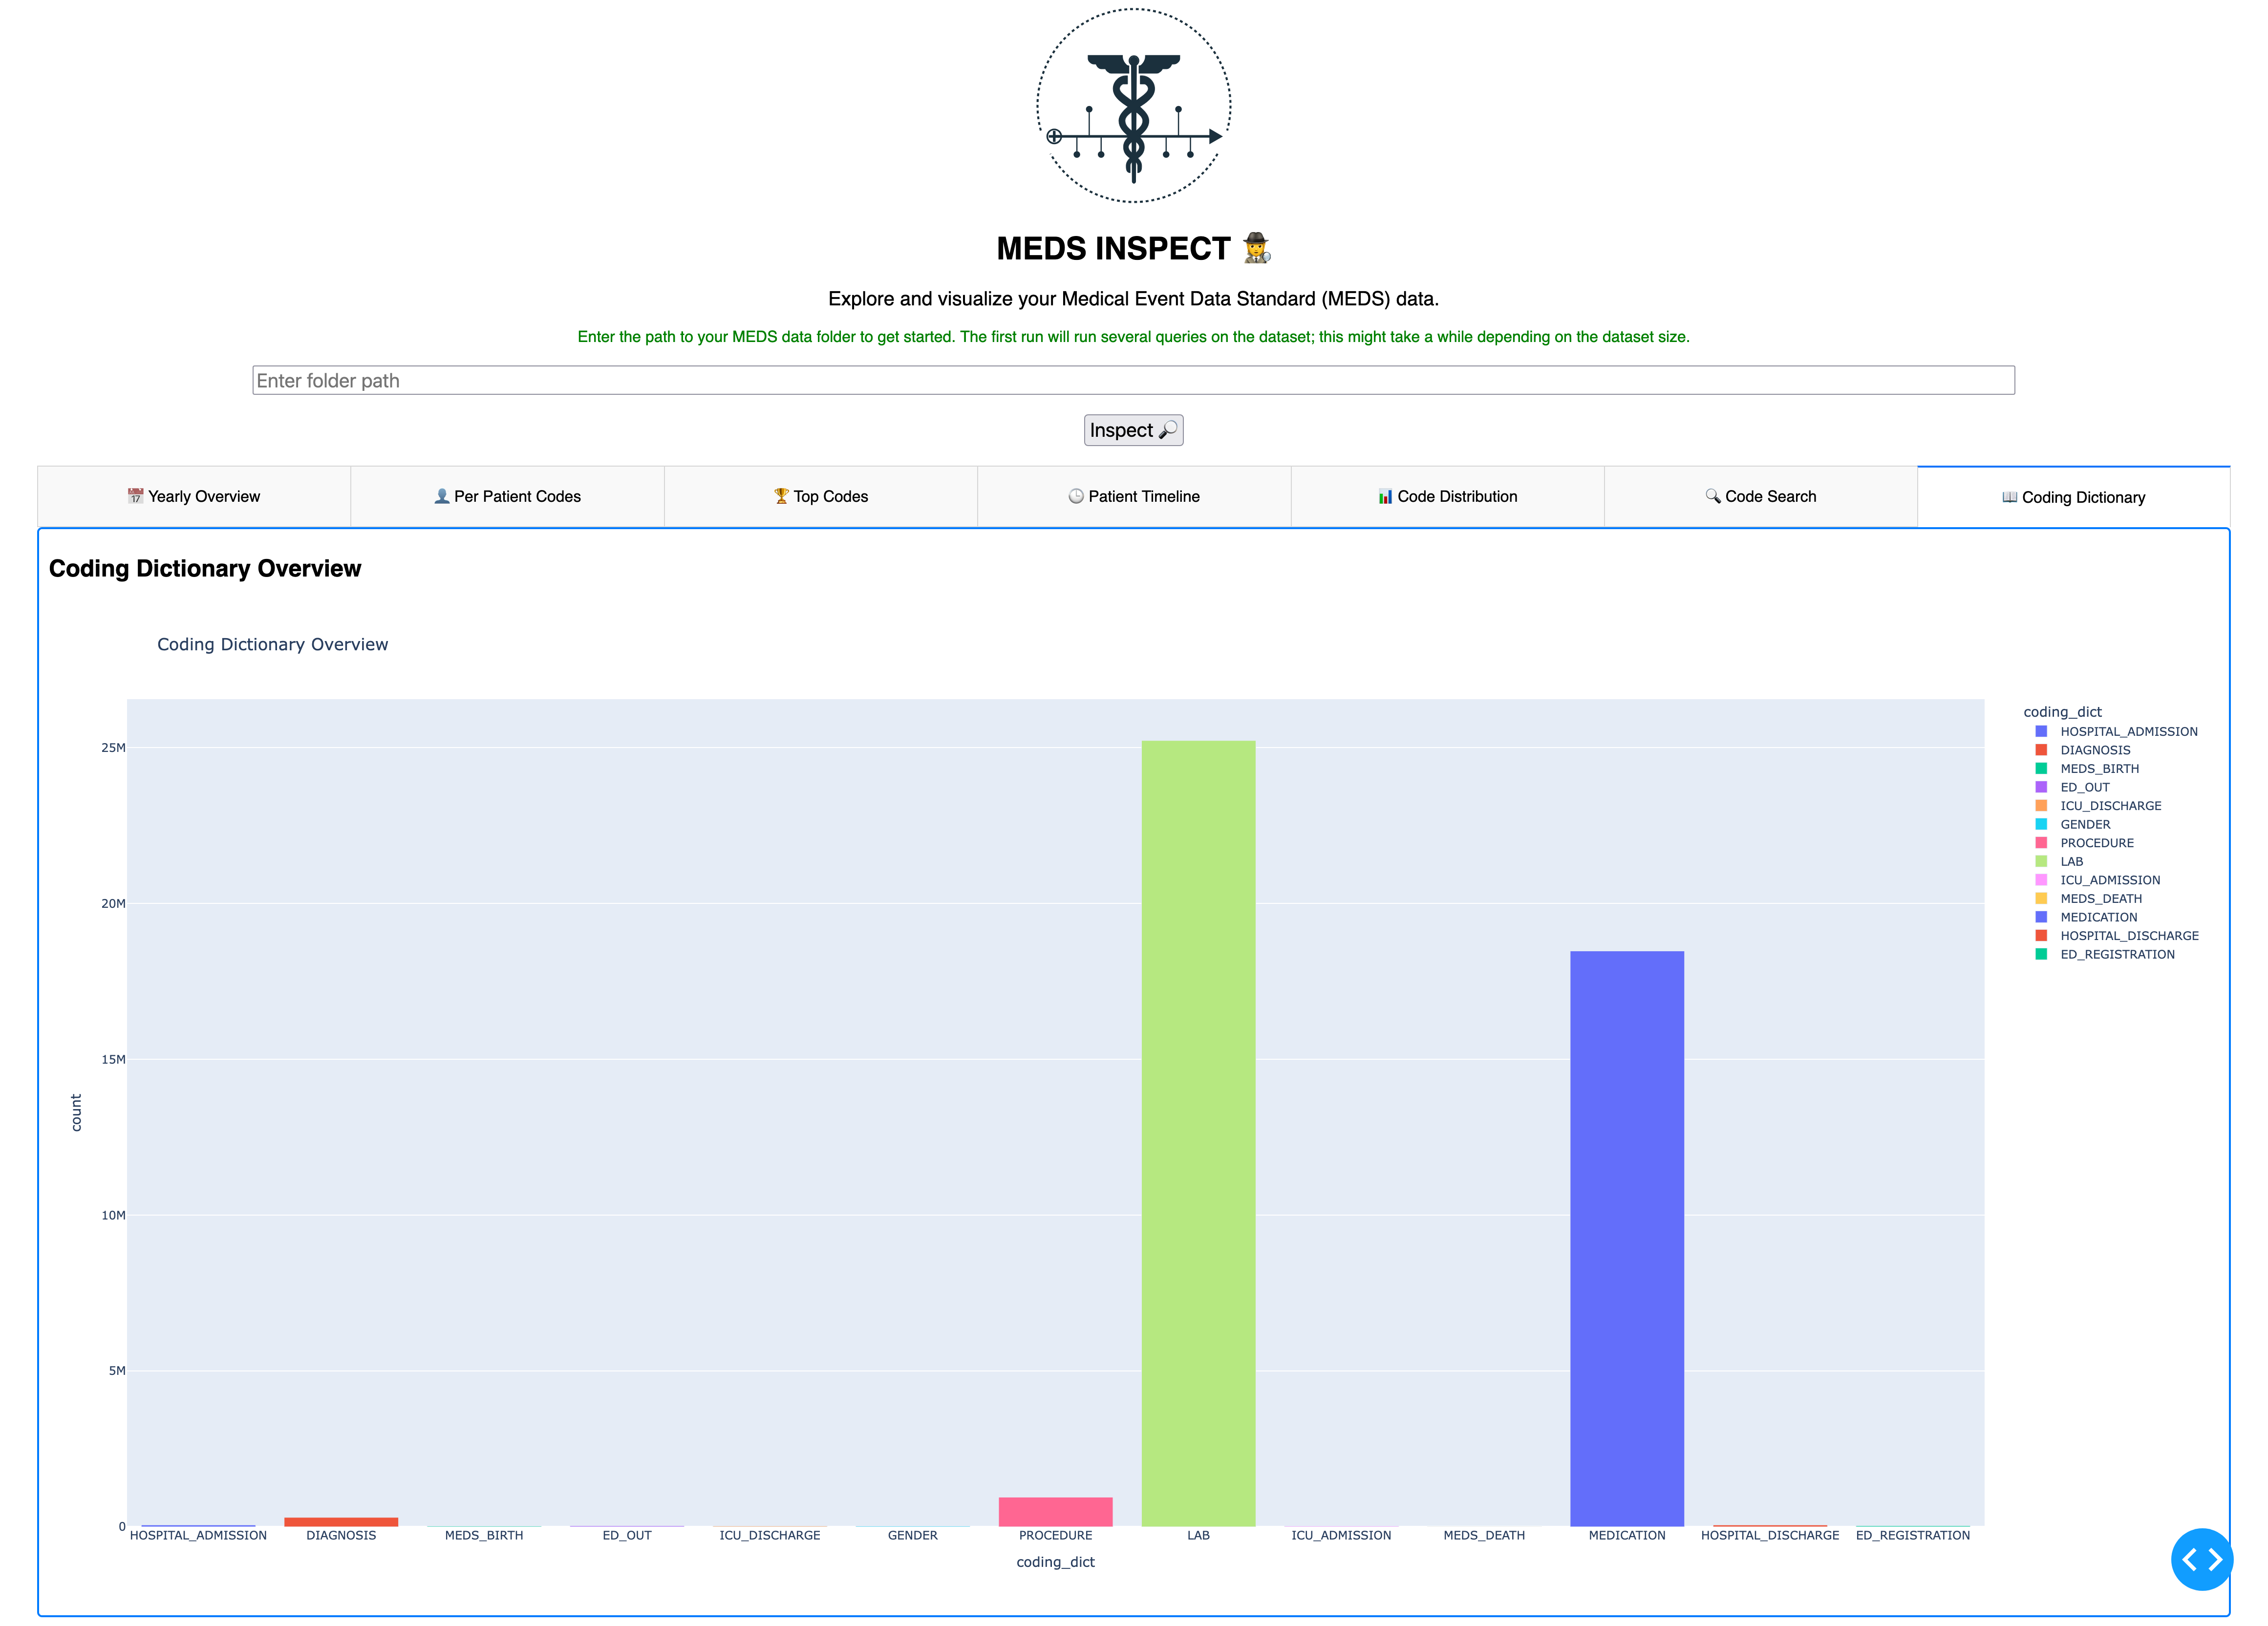
MEDS-Inspect is an interactive data visualization app that supports you in your data quest.
Getting started
You can use any of the ETLs available in the MEDS ecosystem to create your own MEDS dataset, see here for an updated list.
pip install MEDS-Inspect
Then start a server with the following:
MEDS_Inspect port=8052 +initial_path="path/to/your/meds/dataset"
This will start a local web app that you can access in your browser. Running this command without a file path will default to the MIMIC-IV Demo data in MEDS
You should also be able to enter an arbitrary filepath from the GUI.
On HPC systems you might need to forward the port, for example with SSH tunneling:
ssh -N -f -L localhost:8090:localhost:8090 remote_user@remote_host
Then access the app at localhost:8090 in your browser. For any problems, please refer to your
system administrator.
Getting started (development)
Clone repository:
git clone https://github.com/rvandewater/MEDS-Inspect.git
cd MEDS-Inspect
Create environment:
conda create -n "meds-inspect" python=3.12
conda activate meds-inspect
Install requirements:
pip install -r requirements.txt
Launch app:
python src/MEDS_Inspect/__main__.py
This should start a locally hosted web app.
Functionality
You can start the caching directly from the command line. Caching creates the folder .meds-inspect-cache
python MEDS_Inspect_cache path/to/your/favorite/meds/dataset
Impression:
1 maintainer

Metadata
1 maintainer
Release files for MEDS-Inspect 0.0.11
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| meds_inspect-0.0.11.tar.gz | 5.1 MB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| meds_inspect-0.0.11-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 10.0 MB
Release files / meds_inspect-0.0.11.tar.gz
| Download URL | meds_inspect-0.0.11.tar.gz |
|---|---|
| Size | 5.1 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
52b6313a1e170628ac75449730282c372977b73dcb42ca96afd38e148eec519a
|
|
BLAKE2b-256 checksum How to use checksums |
8396c428575b17613d4b0fb6810404a550b844990cf8d27451f78fdecc193af1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 27, 2025.
Transparency logRelease files / meds_inspect-0.0.11-py3-none-any.whl
| Download URL | meds_inspect-0.0.11-py3-none-any.whl |
|---|---|
| Size | 4.9 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
c96007ca3c846ebf51c60a1b30bbeb01302d3c6c12a552b12ddcaa6cd863e16d
|
|
BLAKE2b-256 checksum How to use checksums |
54258ccec63077eb24d11183c15bc9f172560f84c8ec84f3ae4047738b357bb4
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 27, 2025.
Transparency logSecurity for MEDS-Inspect 0.0.11
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for meds_inspect-0.0.11.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 27, 2025.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














