
njsscan
njsscan is a static application testing (SAST) tool that can find insecure code patterns in your node.js applications using simple pattern matcher from libsast and syntax-aware semantic code pattern search tool semgrep.
Made with 


Support njsscan
- Donate via Paypal:
- Sponsor the Project:


e-Learning Courses & Certifications

Installation
pip install njsscan
Requires Python 3.6+ and supports only Mac and Linux
Command Line Options
$ njsscan
usage: njsscan [-h] [--json] [--sarif] [--sonarqube] [-o OUTPUT] [-c CONFIG] [--missing-controls] [-w] [-v] [path ...]

positional arguments:
  path                  Path can be file(s) or directories with source code

optional arguments:
  -h, --help            show this help message and exit
  --json                set output format as JSON
  --sarif               set output format as SARIF 2.1.0
  --sonarqube           set output format compatible with SonarQube
  -o OUTPUT, --output OUTPUT
                        output filename to save the result
  -c CONFIG, --config CONFIG
                        Location to .njsscan config file
  --missing-controls    enable missing security controls check
  -w, --exit-warning    non zero exit code on warning
  -v, --version         show njsscan version
Example Usage
$ njsscan test.js
- Pattern Match ████████████████████████████████████████████████████████████ 1
- Semantic Grep ███████████████████████████ 160

njsscan: v0.1.9 | Ajin Abraham | opensecurity.in
╒═════════════╤═══════════════════════════════════════════════════════════════════════════════════════════════╕
│ RULE ID     │ express_xss                                                                                   │
├─────────────┼───────────────────────────────────────────────────────────────────────────────────────────────┤
│ OWASP       │ A1: Injection                                                                                 │
├─────────────┼───────────────────────────────────────────────────────────────────────────────────────────────┤
│ CWE         │ CWE-79: Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting')  │
├─────────────┼───────────────────────────────────────────────────────────────────────────────────────────────┤
│ DESCRIPTION │ Untrusted User Input in Response will result in Reflected Cross Site Scripting Vulnerability. │
├─────────────┼───────────────────────────────────────────────────────────────────────────────────────────────┤
│ SEVERITY    │ ERROR                                                                                         │
├─────────────┼───────────────────────────────────────────────────────────────────────────────────────────────┤
│ FILES       │ ╒════════════════╤═══════════════════════════════════════════════╕                            │
│             │ │ File           │ test.js                                       │                            │
│             │ ├────────────────┼───────────────────────────────────────────────┤                            │
│             │ │ Match Position │ 5 - 46                                        │                            │
│             │ ├────────────────┼───────────────────────────────────────────────┤                            │
│             │ │ Line Number(s) │ 7: 8                                          │                            │
│             │ ├────────────────┼───────────────────────────────────────────────┤                            │
│             │ │ Match String   │ const { name } = req.query;                   │                            │
│             │ │                │     res.send('<h1> Hello :' + name + "</h1>") │                            │
│             │ ╘════════════════╧═══════════════════════════════════════════════╛                            │
╘═════════════╧═══════════════════════════════════════════════════════════════════════════════════════════════╛
nodejsscan SAST
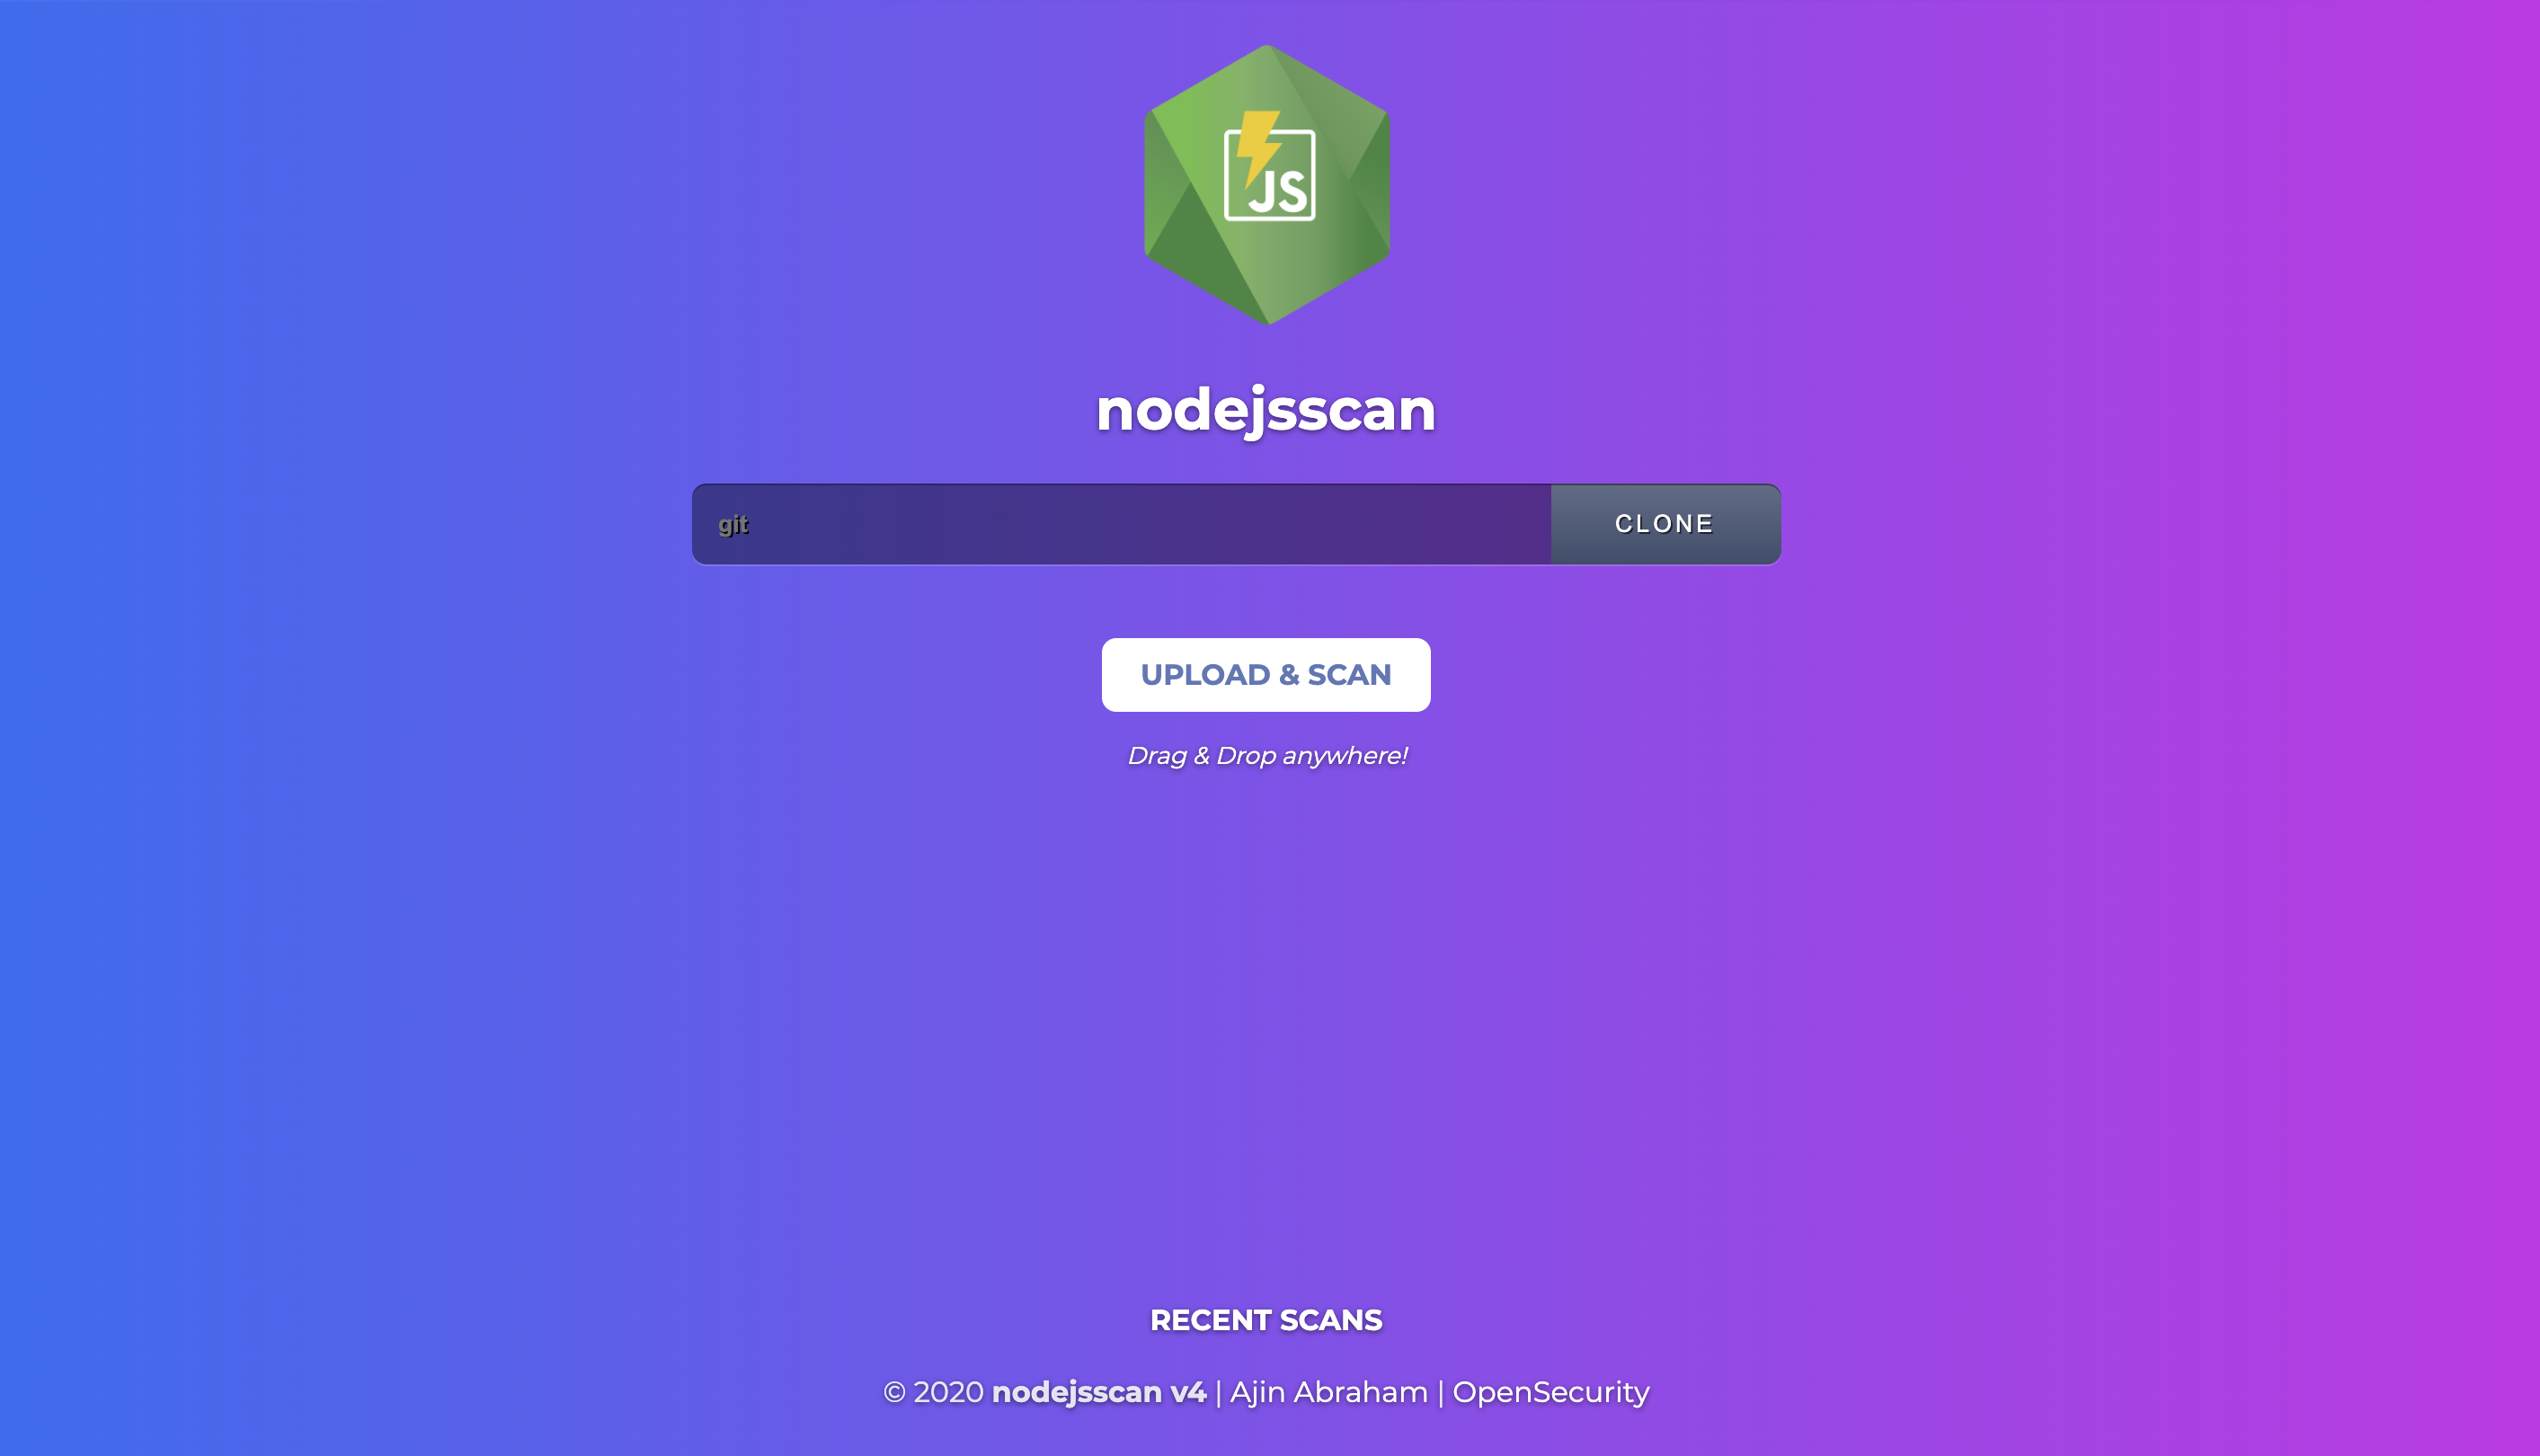
nodejsscan, built on top of njsscan provides a full fledged vulnerability management user interface along with other nifty integrations.
See nodejsscan
Python API
>>> from njsscan.njsscan import NJSScan
>>> node_source = '/node_source/true_positives/sqli_node.js'
>>> scanner = NJSScan([node_source], json=True, check_controls=False)
>>> scanner.scan()
{
    'templates': {},
    'nodejs': {
        'node_sqli_injection': {
            'files': [{
                'file_path': '/node_source/true_positives/sqli_node.js',
                'match_position': (1, 24),
                'match_lines': (4, 11),
                'match_string': 'var employeeId = req.foo;\n\nvar sql = "SELECT * FROM trn_employee WHERE employee_id = " + employeeId;\n\n\n\nconnection.query(sql, function (error, results, fields) {\n\n    if (error) {\n\n        throw error;\n\n    }\n\n    console.log(results);'
            }],
            'metadata': {
                'owasp': 'A1: Injection',
                'cwe': "CWE-89: Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection')",
                'description': 'Untrusted input concatinated with raw SQL query can result in SQL Injection.',
                'severity': 'ERROR'
            }
        }
    },
    'errors': []
}
Configure njsscan
A .njsscan file in the root of the source code directory allows you to configure njsscan.
---
- nodejs-extensions:
  - .js

  template-extensions:
  - .new
  - .hbs
  - ''

  ignore-filenames:
  - skip.js

  ignore-paths:
  - __MACOSX
  - skip_dir
  - node_modules

  ignore-extensions:
  - .jsx

  ignore-rules:
  - regex_injection_dos
  - pug_jade_template
Suppress Findings
You can suppress findings from javascript source files by adding the comment // njsscan-ignore: rule_id1, rule_id2 to the line that trigger the findings.
Example:
app.get('/some/redirect', function (req, res) {
    var target = req.param("target");
    res.redirect(target); // njsscan-ignore: express_open_redirect
});
CI/CD Integrations
You can enable njsscan in your CI/CD or DevSecOps pipelines.
Github Action
Add the following to the file .github/workflows/njsscan.yml.
name: njsscan
on:
  push:
    branches: [ master ]
  pull_request:
    branches: [ master ]
jobs:
  njsscan:
    runs-on: ubuntu-latest
    name: njsscan check
    steps:
    - name: Checkout the code
      uses: actions/checkout@v2
    - name: nodejsscan scan
      id: njsscan
      uses: ajinabraham/njsscan-action@master
      with:
        args: '.'
Example: dvna with njsscan github action
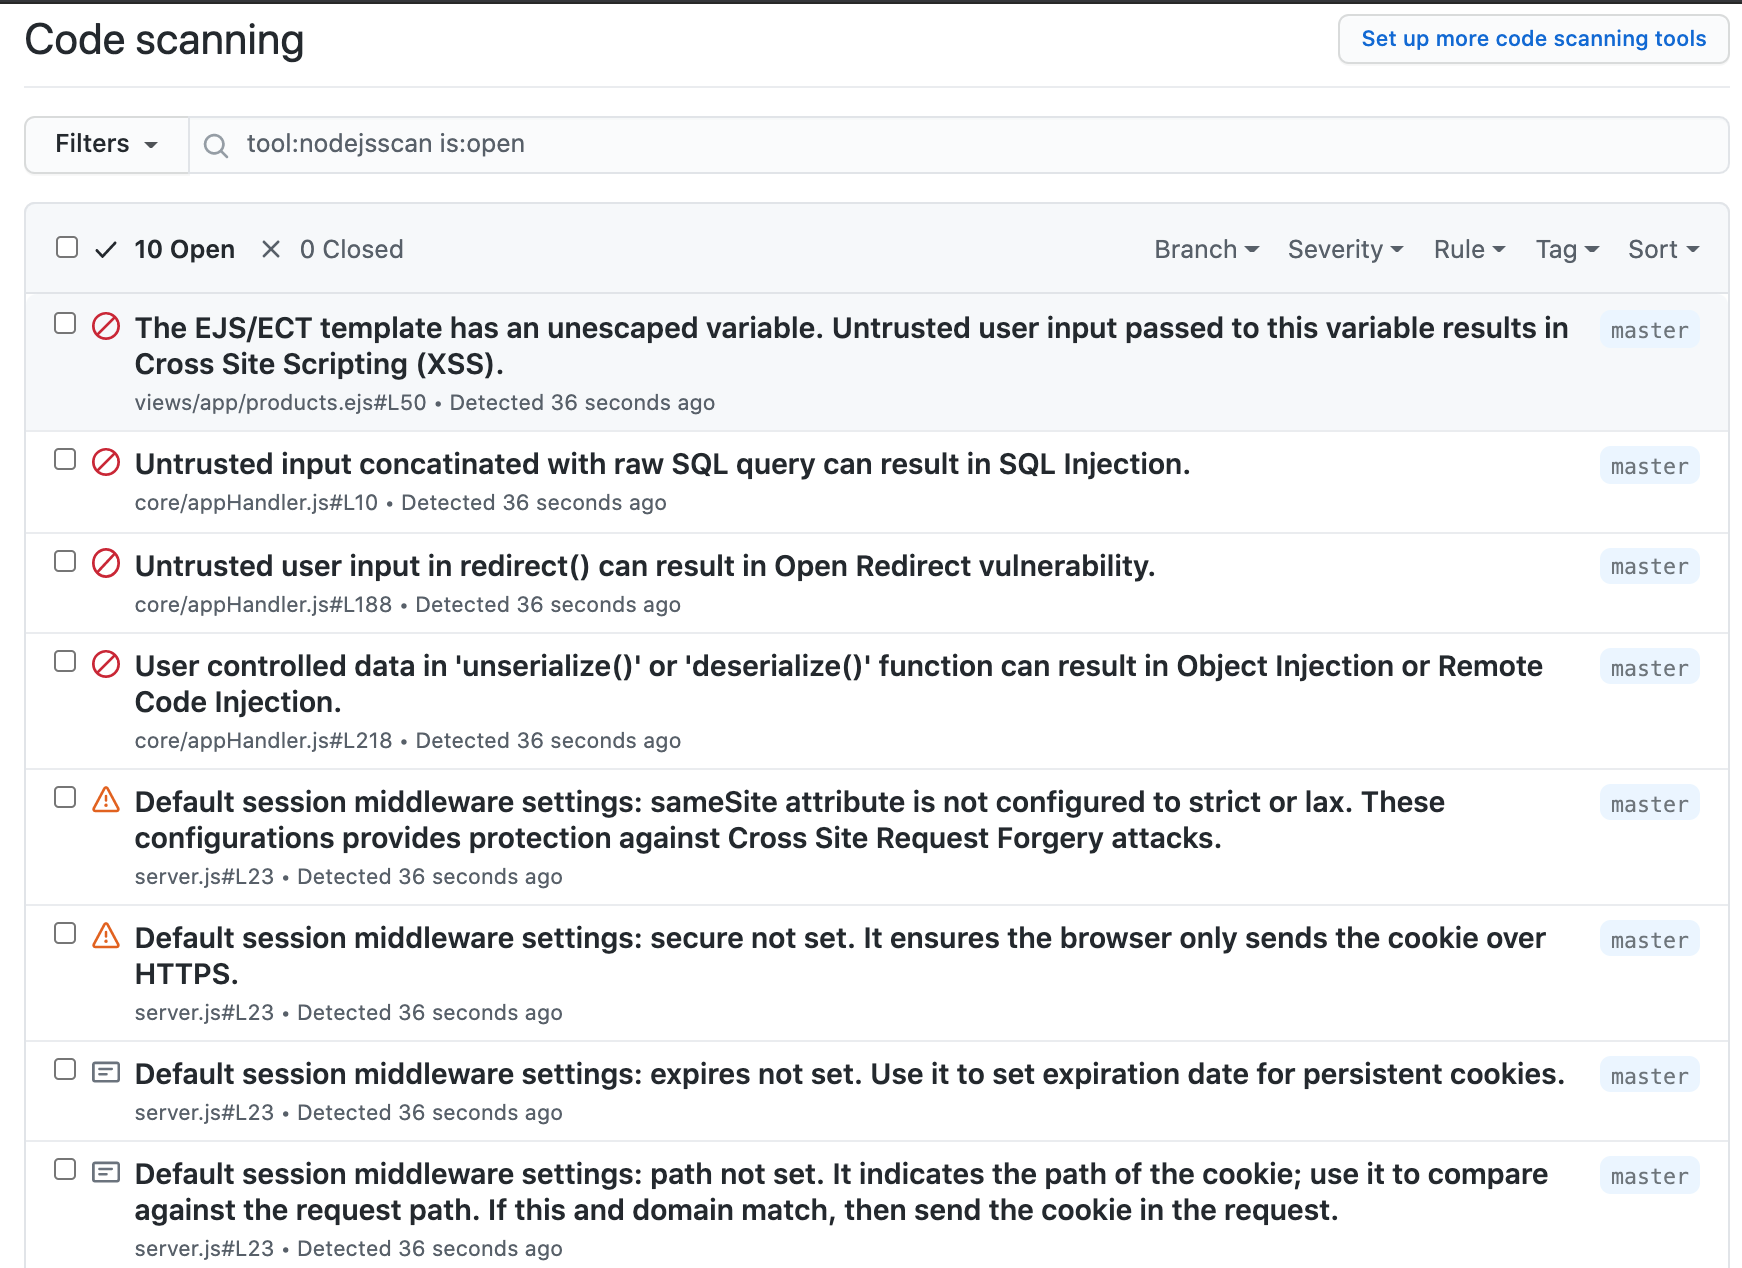
Github Code Scanning Integration
Add the following to the file .github/workflows/njsscan_sarif.yml.
name: njsscan sarif
on:
  push:
    branches: [ master ]
  pull_request:
    branches: [ master ]
jobs:
  njsscan:
    runs-on: ubuntu-latest
    name: njsscan code scanning
    steps:
    - name: Checkout the code
      uses: actions/checkout@v2
    - name: nodejsscan scan
      id: njsscan
      uses: ajinabraham/njsscan-action@master
      with:
        args: '. --sarif --output results.sarif || true'
    - name: Upload njsscan report
      uses: github/codeql-action/upload-sarif@v1
      with:
        sarif_file: results.sarif
Gitlab CI/CD
Add the following to the file .gitlab-ci.yml.
stages:
    - test
njsscan:
    image: python
    before_script:
        - pip3 install --upgrade njsscan
    script:
        - njsscan .
Example: dvna with njsscan gitlab
Travis CI
Add the following to the file .travis.yml.
language: python
install:
    - pip3 install --upgrade njsscan
script:
    - njsscan .
Docker
Prebuilt image from DockerHub
docker pull opensecurity/njsscan
docker run -v /path-to-source-dir:/src opensecurity/njsscan /src
Build Locally
docker build -t njsscan .
docker run -v /path-to-source-dir:/src njsscan /src
1 maintainer

Metadata
1 maintainer
Release files for njsscan 0.2.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| njsscan-0.2.2.tar.gz | 39.5 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| njsscan-0.2.2-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 112.9 kB
Release files / njsscan-0.2.2.tar.gz
| Download URL | njsscan-0.2.2.tar.gz |
|---|---|
| Size | 39.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
d4f305c2c1faee57660ab3655557bae3d7668a0e4129ea01e14c0a8a086018a6
|
|
BLAKE2b-256 checksum How to use checksums |
eae02b0855b441ac2ac8f29560621a36928fa8003efd3a4f9e823d52be0871b9
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.3.0 pkginfo/1.7.0 requests/2.25.1 setuptools/49.2.1 requests-toolbelt/0.9.1 tqdm/4.56.0 CPython/3.9.1
|
Release files / njsscan-0.2.2-py3-none-any.whl
| Download URL | njsscan-0.2.2-py3-none-any.whl |
|---|---|
| Size | 73.4 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
5f0e540ea04c3295baf1907076a11298cb146acc5fd9284bf23c6b440858d19d
|
|
BLAKE2b-256 checksum How to use checksums |
a0fe1c4a74498a1c6fa8eb3c848db6aa327457b0c7665b5f00388dc692282e28
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.3.0 pkginfo/1.7.0 requests/2.25.1 setuptools/49.2.1 requests-toolbelt/0.9.1 tqdm/4.56.0 CPython/3.9.1
|














