
njsscan
njsscan is a static application testing (SAST) tool that can find insecure code patterns in your node.js applications using simple pattern matcher from libsast and syntax-aware semantic code pattern search tool semgrep.
Made with 


Support njsscan
- Donate via Paypal:
- Sponsor the Project:


e-Learning Courses & Certifications

Installation
pip install njsscan
Requires Python 3.10+ and supports only Mac and Linux
Command Line Options
$ njsscan
usage: njsscan [-h] [--json] [--sarif] [--sonarqube] [--defectdojo] [--gitlab-sast] [--html] [-o OUTPUT] [-c CONFIG] [--missing-controls] [-w] [-v] [path ...]

positional arguments:
  path                  Path can be file(s) or directories with source code

optional arguments:
  -h, --help            show this help message and exit
  --json                set output format as JSON
  --sarif               set output format as SARIF 2.1.0
  --sonarqube           set output format compatible with SonarQube
  --defectdojo          set output format compatible with DefectDojo Generic Findings Import
  --gitlab-sast         set output format as GitLab SAST report
  --html                set output format as HTML
  -o OUTPUT, --output OUTPUT
                        output filename to save the result
  -c CONFIG, --config CONFIG
                        Location to .njsscan config file
  --missing-controls    enable missing security controls check
  -w, --exit-warning    non zero exit code on warning
  -v, --version         show njsscan version
Example Usage
$ njsscan test.js
- Pattern Match ████████████████████████████████████████████████████████████ 1
- Semantic Grep ███████████████████████████ 160

njsscan: v0.1.9 | Ajin Abraham | opensecurity.in
╒═════════════╤═══════════════════════════════════════════════════════════════════════════════════════════════╕
│ RULE ID     │ express_xss                                                                                   │
├─────────────┼───────────────────────────────────────────────────────────────────────────────────────────────┤
│ OWASP       │ A1: Injection                                                                                 │
├─────────────┼───────────────────────────────────────────────────────────────────────────────────────────────┤
│ CWE         │ CWE-79: Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting')  │
├─────────────┼───────────────────────────────────────────────────────────────────────────────────────────────┤
│ DESCRIPTION │ Untrusted User Input in Response will result in Reflected Cross Site Scripting Vulnerability. │
├─────────────┼───────────────────────────────────────────────────────────────────────────────────────────────┤
│ SEVERITY    │ ERROR                                                                                         │
├─────────────┼───────────────────────────────────────────────────────────────────────────────────────────────┤
│ FILES       │ ╒════════════════╤═══════════════════════════════════════════════╕                            │
│             │ │ File           │ test.js                                       │                            │
│             │ ├────────────────┼───────────────────────────────────────────────┤                            │
│             │ │ Match Position │ 5 - 46                                        │                            │
│             │ ├────────────────┼───────────────────────────────────────────────┤                            │
│             │ │ Line Number(s) │ 7: 8                                          │                            │
│             │ ├────────────────┼───────────────────────────────────────────────┤                            │
│             │ │ Match String   │ const { name } = req.query;                   │                            │
│             │ │                │     res.send('<h1> Hello :' + name + "</h1>") │                            │
│             │ ╘════════════════╧═══════════════════════════════════════════════╛                            │
╘═════════════╧═══════════════════════════════════════════════════════════════════════════════════════════════╛
nodejsscan SAST
nodejsscan, built on top of njsscan provides a full fledged vulnerability management user interface along with other nifty integrations.
See nodejsscan
Python API
>>> from njsscan.njsscan import NJSScan
>>> node_source = '/node_source/true_positives/sqli_node.js'
>>> scanner = NJSScan([node_source], json=True, check_controls=False)
>>> scanner.scan()
{
    'templates': {},
    'nodejs': {
        'node_sqli_injection': {
            'files': [{
                'file_path': '/node_source/true_positives/sqli_node.js',
                'match_position': (1, 24),
                'match_lines': (4, 11),
                'match_string': 'var employeeId = req.foo;\n\nvar sql = "SELECT * FROM trn_employee WHERE employee_id = " + employeeId;\n\n\n\nconnection.query(sql, function (error, results, fields) {\n\n    if (error) {\n\n        throw error;\n\n    }\n\n    console.log(results);'
            }],
            'metadata': {
                'owasp': 'A1: Injection',
                'cwe': "CWE-89: Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection')",
                'description': 'Untrusted input concatinated with raw SQL query can result in SQL Injection.',
                'severity': 'ERROR'
            }
        }
    },
    'errors': []
}
Configure njsscan
A .njsscan file in the root of the source code directory allows you to configure njsscan. You can also use a custom .njsscan file using --config argument.
---
- nodejs-extensions:
  - .js

  template-extensions:
  - .new
  - .hbs
  - ''

  ignore-filenames:
  - skip.js

  ignore-paths:
  - __MACOSX
  - skip_dir
  - node_modules

  ignore-extensions:
  - .jsx

  ignore-rules:
  - regex_injection_dos
  - pug_jade_template

  severity-filter:
  - WARNING
  - ERROR

  severity-overrides:
    express_xss: WARNING
    node_secret: ERROR
Suppress Findings
You can suppress findings from javascript source files by adding the comment // njsscan-ignore: rule_id1, rule_id2 to the line that trigger the findings.
Example:
app.get('/some/redirect', function (req, res) {
    var target = req.param("target");
    res.redirect(target); // njsscan-ignore: express_open_redirect
});
CI/CD Integrations
You can enable njsscan in your CI/CD or DevSecOps pipelines.
Github Action
Add the following to the file .github/workflows/njsscan.yml.
name: njsscan
on:
  push:
    branches: [ master, main ]
  pull_request:
    branches: [ master, main ]
jobs:
  njsscan:
    runs-on: ubuntu-latest
    name: njsscan check
    steps:
    - name: Checkout the code
      uses: actions/checkout@3d3c42e5aac5ba805825da76410c181273ba90b1 # v7.0.1
    - uses: actions/setup-python@5fda3b95a4ea91299a34e894583c3862153e4b97 # v7.0.0
      with:
        python-version: '3.12'
    - name: nodejsscan scan
      id: njsscan
      uses: ajinabraham/njsscan-action@231750a435d85095d33be7d192d52ec650625146 # v9
      with:
        args: '.'
Example: dvna with njsscan github action
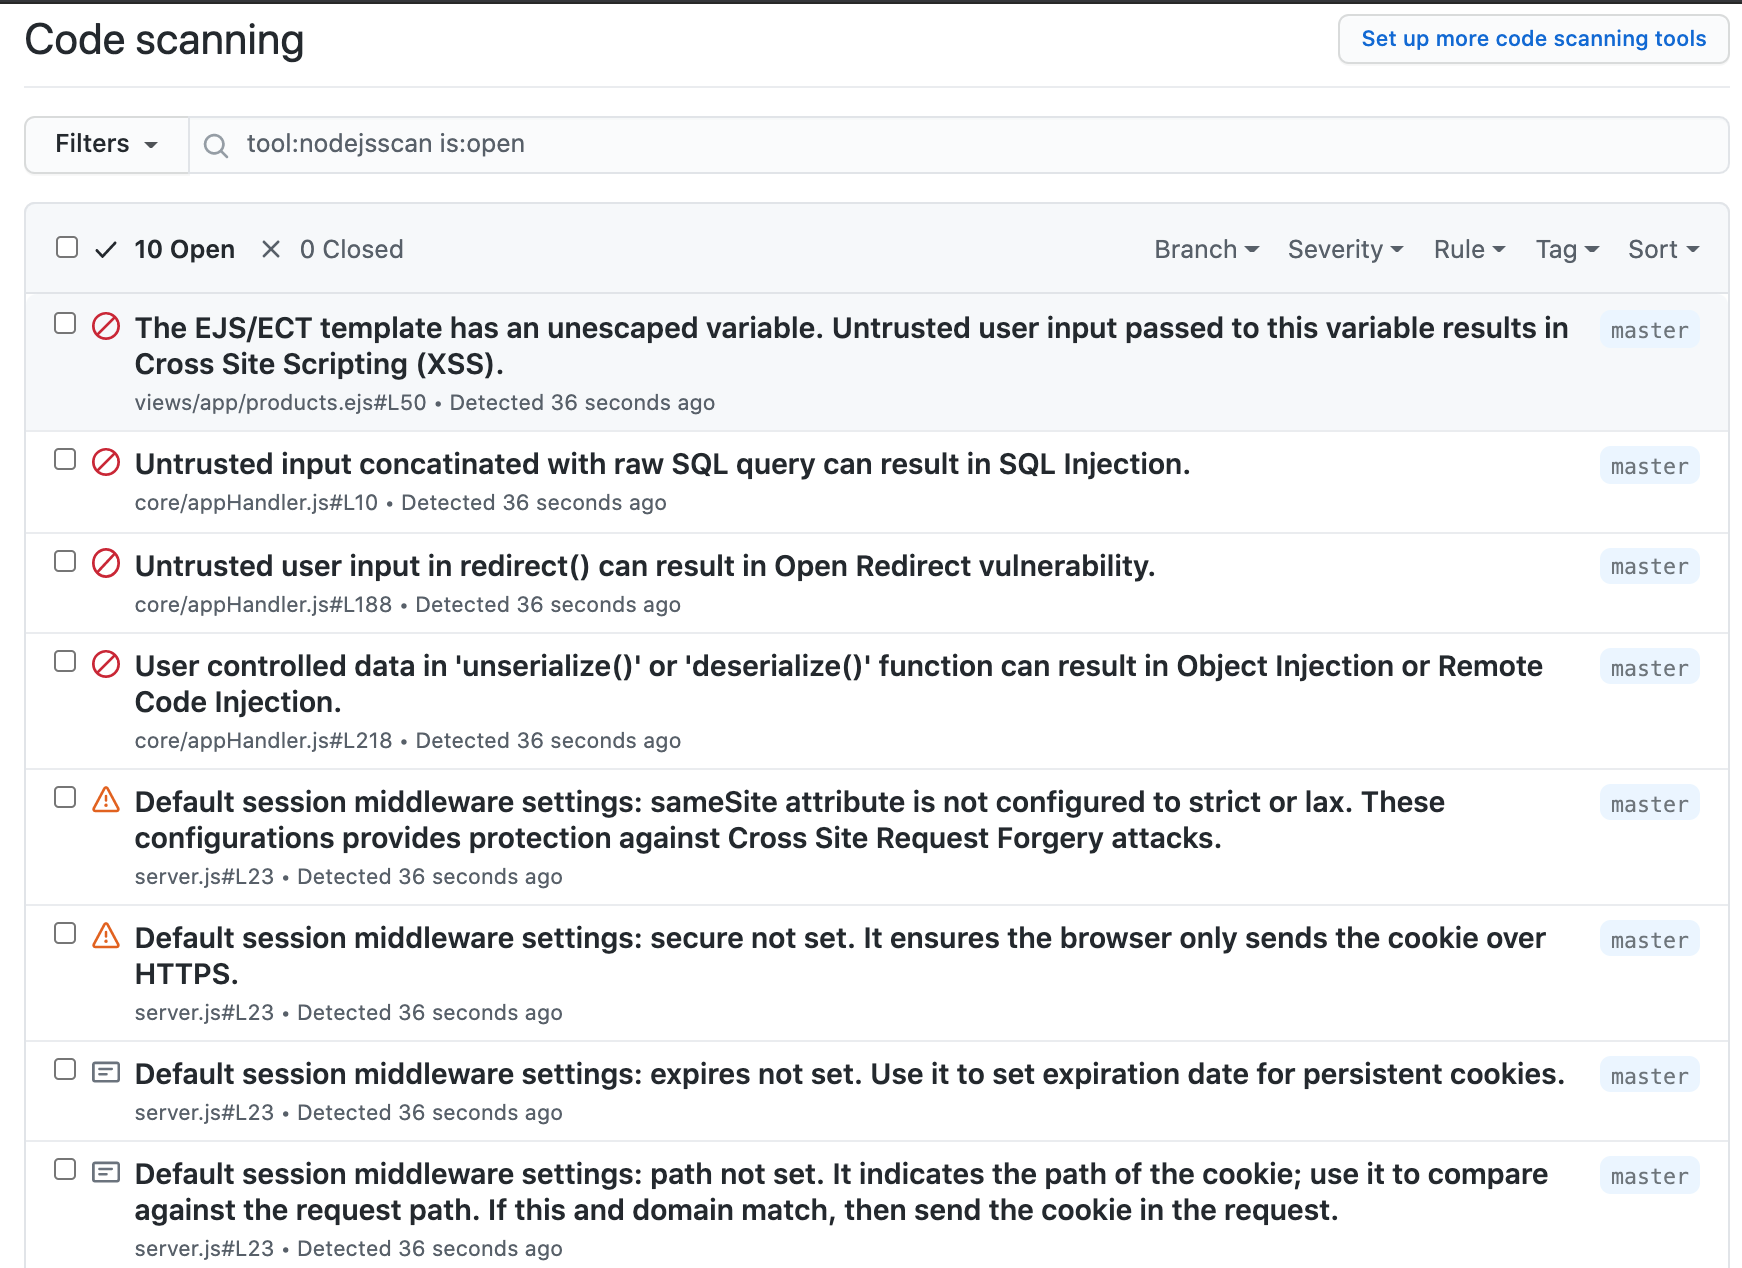
Github Code Scanning Integration
Add the following to the file .github/workflows/njsscan_sarif.yml.
name: njsscan sarif
on:
  push:
    branches: [ master, main ]
  pull_request:
    branches: [ master, main ]
jobs:
  njsscan:
    runs-on: ubuntu-latest
    name: njsscan code scanning
    steps:
    - name: Checkout the code
      uses: actions/checkout@3d3c42e5aac5ba805825da76410c181273ba90b1 # v7.0.1
    - uses: actions/setup-python@5fda3b95a4ea91299a34e894583c3862153e4b97 # v7.0.0
      with:
        python-version: '3.12'
    - name: nodejsscan scan
      id: njsscan
      uses: ajinabraham/njsscan-action@231750a435d85095d33be7d192d52ec650625146 # v9
      with:
        args: '. --sarif --output results.sarif || true'
    - name: Upload njsscan report
      uses: github/codeql-action/upload-sarif@1c5b675653bb5c22dbe9b12b556ec555138e09fd # v4.38.1
      with:
        sarif_file: results.sarif
Gitlab CI/CD
Add the following to the file .gitlab-ci.yml.
stages:
  - test

njsscan:
  image: python:3.12
  stage: test
  before_script:
    - pip3 install --upgrade njsscan
  script:
    - njsscan . --gitlab-sast -o gl-sast-report.json
  artifacts:
    when: always
    reports:
      sast: gl-sast-report.json
Example command (local):
njsscan . --gitlab-sast -o gl-sast-report.json
This writes a native GitLab SAST report so findings appear in the Vulnerability Report / MR security widget without a SARIF converter.
Example: dvna with njsscan gitlab
Travis CI
Add the following to the file .travis.yml.
language: python
install:
    - pip3 install --upgrade njsscan
script:
    - njsscan .
Circle CI
Add the following to the file .circleci/config.yaml
version: 2.1
jobs:
  njsscan:
    docker:
      - image: cimg/python:3.9.6
    steps:
      - checkout
      - run:
          name: Install njsscan
          command: pip install --upgrade njsscan
      - run:
           name: njsscan check
           command: njsscan .
Docker
Prebuilt image from DockerHub
docker pull opensecurity/njsscan
docker run -v /path-to-source-dir:/src opensecurity/njsscan /src
Build Locally
docker build -t njsscan .
docker run -v /path-to-source-dir:/src njsscan /src
1 maintainer

Metadata
1 maintainer
Release files for njsscan 1.0.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| njsscan-1.0.2.tar.gz | 48.3 kB | With provenance | Details for njsscan-1.0.2.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| njsscan-1.0.2-py3-none-any.whl | Python 3 | none | any | Details for njsscan-1.0.2-py3-none-any.whl |
Total release size: 123.1 kB
Release files / njsscan-1.0.2.tar.gz
| Download URL | njsscan-1.0.2.tar.gz |
|---|---|
| Size | 48.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
7d7361822e61cbf2ccab1999bd9596d71503f1042b270e1227989b40f9f69ddc
|
|
BLAKE2b-256 checksum How to use checksums |
742174f9263c70e40f91e7b51e0bc3243f896a489dd42766059e834603dcf77a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 27, 2026.
Transparency logRelease files / njsscan-1.0.2-py3-none-any.whl
| Download URL | njsscan-1.0.2-py3-none-any.whl |
|---|---|
| Size | 74.8 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
616830830cd67ddde89dcca8f8f8c2e81073e96b0e8e8b27b3c6a0bf53ec0f4d
|
|
BLAKE2b-256 checksum How to use checksums |
336b42ca4d33397cb241a1695dc759adda5c71cc940df87e02b42ea121221cd8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 27, 2026.
Transparency logSecurity for njsscan 1.0.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for njsscan-1.0.2.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 27, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














