
nmapvulners2csv


Table of Contents
Getting Started
Run nmap with enabled script Vulners and save xml output, for example:
nmap -sV --script vulners -oX <nmap_output.xml>
Example
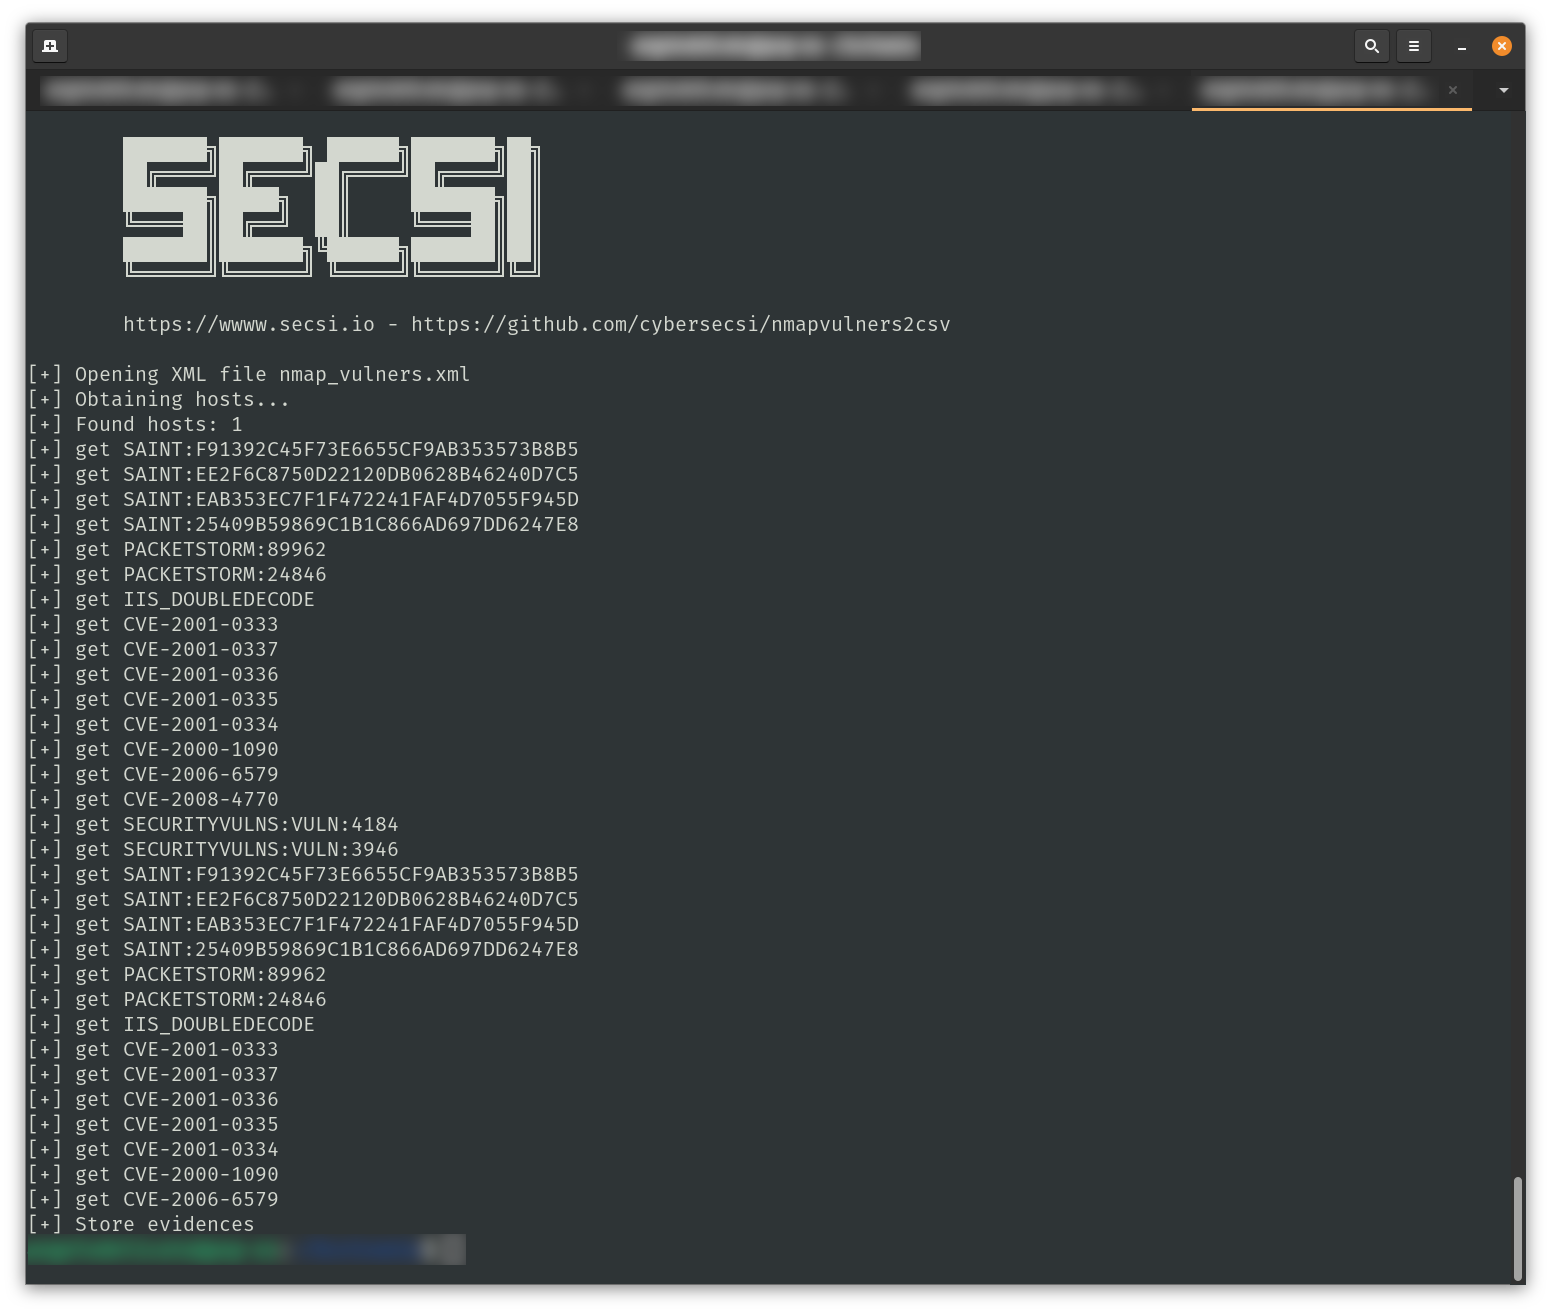
The output of the tool is like the following:
Install & Run
To install it you just need to run:
pip install nmapvulners2csv
Run without installing
Prerequisites
Install dependencies by using the following command:
pip install -r requirements.txt
chmod +x nmapvulners2csv/nmapvulners2csv.py
Usage: nmapvulners2csv.py NMAP_XML_FILE <flags>
  optional flags:        --output | --descr
To run the converter:
nmapvulners2csv.py <nmap_output.xml>
the script will generate a file output.csv in output dir. If you want to set the output file:
nmapvulners2csv.py <nmap_output.xml> --output <output_csv_file> --dir <output_directory>
For multiple data:
for i in `ls -1 vulners*`; do python nmapvulners2csv.py $i ${i%%.xml}.csv ; done
Evidences Description
nmapvulners2csv does not generate descriptions for vulnerabilities. You can add --descr flag to add descriptions in CSV. The script scrapes description information from Vulners site. The command is more time-expensive and send several HTTP requests against Vulners website. Not tested for IP ban and network issues.
Contributing
Contributions are what make the open source community such an amazing place to be learn, inspire, and create. Any contributions you make are greatly appreciated.
- Fork the Project
- Create your Feature Branch (
git checkout -b feature/AmazingFeature) - Commit your Changes (
git commit -m 'Add some AmazingFeature') - Push to the Branch (
git push origin feature/AmazingFeature) - Open a Pull Request
Credits
nmapvulners2csv is proudly developed @SecSI by:
License
Distributed under Apache 2 License. See LICENSE for more information.
1 maintainer

Metadata
1 maintainer
Release files for nmapvulners2csv 1.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| nmapvulners2csv-1.2.0.tar.gz | 8.4 kB | Without provenance | Details for nmapvulners2csv-1.2.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| nmapvulners2csv-1.2.0-py3-none-any.whl | Python 3 | none | any | Details for nmapvulners2csv-1.2.0-py3-none-any.whl |
Total release size: 18.0 kB
Release files / nmapvulners2csv-1.2.0.tar.gz
| Download URL | nmapvulners2csv-1.2.0.tar.gz |
|---|---|
| Size | 8.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
cf0957a595488259a0993ab555a2d5ff99e4800441fcbdfdec6a88b5c2dfa9f1
|
|
BLAKE2b-256 checksum How to use checksums |
56137f33c800d9fd107aff385be28b142c94ff543575156404285623a98d69b0
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
poetry/2.5.1 CPython/3.11.0 Linux/6.17.0-1022-azure
|
Release files / nmapvulners2csv-1.2.0-py3-none-any.whl
| Download URL | nmapvulners2csv-1.2.0-py3-none-any.whl |
|---|---|
| Size | 9.6 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
f3855b6d29c0957f0fcfece3073c2d81c4b4e4c5e0a88c5196d9334ad9aaf0ab
|
|
BLAKE2b-256 checksum How to use checksums |
f9175519f78501d74ec88fbdbc0ee430f8d8e25f989699bc046852780973c133
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
poetry/2.5.1 CPython/3.11.0 Linux/6.17.0-1022-azure
|
Security for nmapvulners2csv 1.2.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














