
 ██████╗ ██████╗ ███████╗███████╗██████╗ ██╗   ██╗ █████╗ ██╗
██╔═══██╗██╔══██╗██╔════╝██╔════╝██╔══██╗██║   ██║██╔══██╗██║
██║   ██║██████╔╝███████╗█████╗  ██████╔╝██║   ██║███████║██║
██║   ██║██╔══██╗╚════██║██╔══╝  ██╔══██╗╚██╗ ██╔╝██╔══██║██║
╚██████╔╝██████╔╝███████║███████╗██║  ██║ ╚████╔╝ ██║  ██║███████╗
 ╚═════╝ ╚═════╝ ╚══════╝╚══════╝╚═╝  ╚═╝  ╚═══╝  ╚═╝  ╚═╝╚══════╝
Observal is the control plane and system of record for internal coding agent resources
Set up once, and let your coding agent use Observal through observal-cli.





If you find Observal useful, please consider giving it a star. It helps others discover the project and keeps development going.
What is Observal and what does it solve?
Observal is the control plane and system of record for internal internal coding agent resources. Every tech-forward organization today creates internal Skills, Agents files, MCP clients. Though the creation of these coding agent resources has been prolific, peer adoption and usage is sparse. Coding agent users today end up creating their own version of such resouces without reusing existing packages.
The cause is largely due to two problems:
-
Lack of a discoverability layer
Organizations store their coding agent resources in siloed git repositories with little to no documentation. Users are not able to locate existing coding agent resources and this results in multiple developers creating the same/similar resources again.
-
Missing feedback loop
Any software where usage patterns are not understood and the principle of user-centric development is violated tends to fade out. Such is the problem with development of MCP clients, Skills and Agent files. Authors publish and maintain these resources with little visibility into how they're actually used. Additionally, Coding agent failures don't trigger static error codes: they hallucinate or provide subtly incorrect answers. This leaves users clueless about what went wrong compounding the feedback problem.
Observal solves this by providing a centralized discovery layer for coding agent resources alongside useful insights into usage patterns. It turns silent failures into actionable feedback, ensuring internal resources are continuously optimized for the people using them.
Observal supports Claude Code, Cursor, Kiro, Pi, Copilot, Codex, OpenCode, and other tools.
Why teams use Observal
- Centralize resources into one platform: Store Skills, MCP clients, hooks, prompts, agent files and sandboxes in one registry.
- Run a governed registry: Review submissions, approve internal agents, inspect version diffs, and give developers one trusted place to install from.
- Render across multiple Coding IDE/CLI: Generate the correct config for each supported harness instead of maintaining separate setup instructions for every harness.
- Let agents use each other: Every approved resource is discoverable over the open ARD standard, and a running agent can hand part of its task to another approved agent, whether it lives in the registry or is a remote A2A service.
- Learn what works: Use real adoption and session data to find which agents, tools, prompts, and workflows are helping teams.
- Replay sessions when needed: Use traces as evidence for debugging, review, audits, and deeper analysis.
Supported harnesses



One command to install any agent into any supported harness. The config files are generated per-harness automatically.
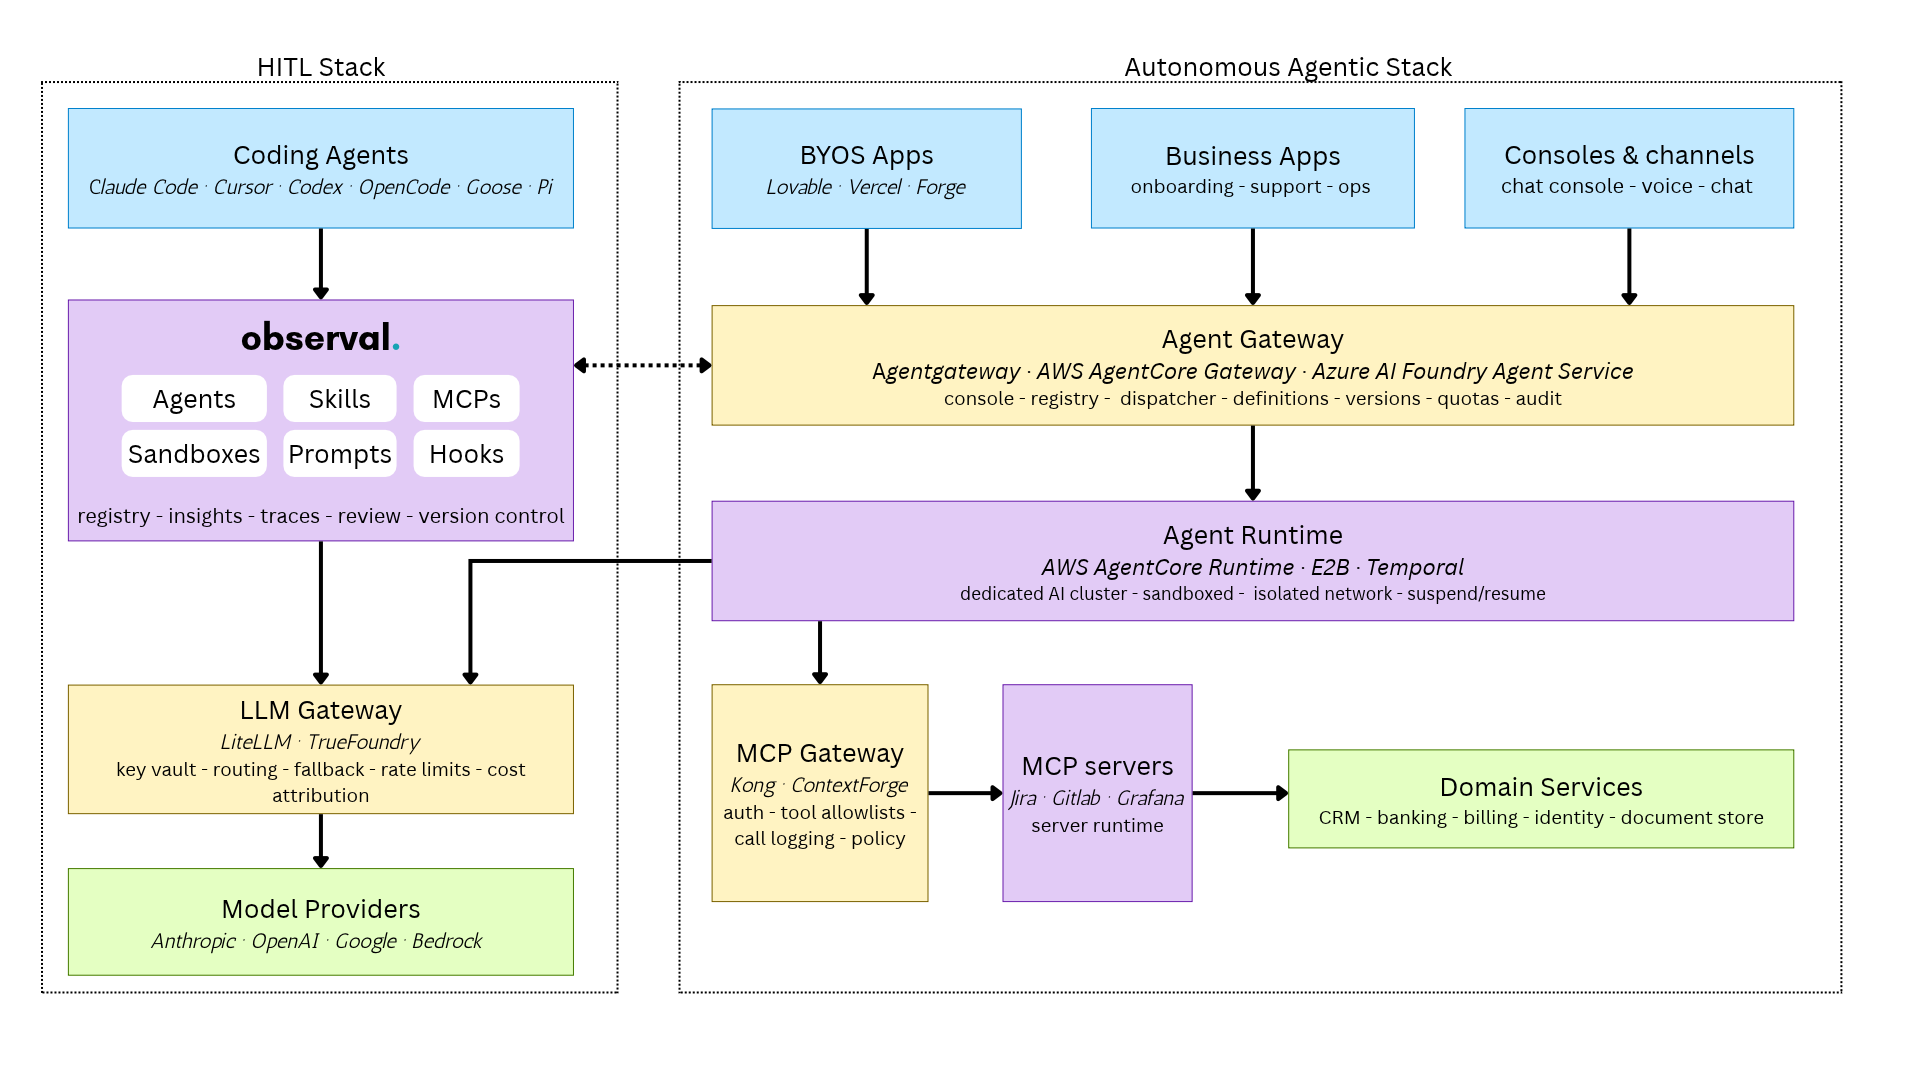
Where does observal fit in your modern enterprise infrastructure?
Quick Start
Observal has two parts: a server (API + web UI + databases) you self-host, and a CLI you install on each developer machine.
1. Deploy the server
One-line install (requires Docker Engine ≥ 24.0 with Compose v2):
curl -fsSL https://raw.githubusercontent.com/Observal/Observal/main/install-server.sh | bash
This downloads a Docker Compose package, generates operator-owned secret files with restricted container-group access, binds published ports to loopback by default, pulls container images from GHCR, and starts the stack. With a terminal it runs guided setup; without a terminal the same command applies safe defaults automatically.
Deployment docs are linked directly from this README:
- Setup guide: fastest path from zero to a working stack
- Self-hosting overview: deployment models and operator docs
- Production deployment: hardened production topology
- Databases: Postgres, ClickHouse, migrations, retention
- Upgrades: safe upgrade and rollback flow
- Release verification: verify checksums, provenance, and signed tags
- Backup and restore: backup plan before upgrades
From source (for contributors):
git clone https://github.com/Observal/Observal.git && cd Observal
cp .env.example .env
make up
2. Install the CLI
Standalone binary (no Python required):
# macOS / Linux
curl -fsSL https://raw.githubusercontent.com/Observal/Observal/main/install.sh | bash
# Windows (PowerShell)
irm https://raw.githubusercontent.com/Observal/Observal/main/install.ps1 | iex
Connecting to an existing server? See the Setup guide.
Python (3.11+):
uv tool install observal-cli
# or: pipx install observal-cli
3. Connect your harness
observal auth login
observal doctor --patch
This authenticates with your server, detects your harness, installs telemetry hooks, starts capturing sessions automatically, and prepares it for agent installs and registry commands.
Once logged in, run /observal inside your harness and it takes the wheel. Pull agents, submit resources, browse the registry, run diagnostics:
/observal pull security-auditor
/observal scan
/observal doctor
Or just tell your agent what you want and it figures out the right commands.
How Observal works
The registry is the distribution layer
The registry is where agents live. Admins review submissions, version diffs keep changes auditable, and one command installs an agent into any supported harness.
Insights close the loop
Real usage data flows back as reports: what's helping, what's getting in the way, and where to improve. Session traces provide the underlying evidence for debugging and auditing.
Coding agent resource registry
Browse and search by teamspace, publisher, category, or harness; each card shows its supported harnesses and pull count:

Build agent files in four steps (identity, behavior, components, review) with a live summary and draft readiness checks:

Component library with tabs for MCP servers, skills, hooks, prompts, and sandboxes:

Fork an approved release
Fork an agent or component into an independent draft in your personal namespace or an eligible teamspace. The source stays unchanged; agent forks retain pinned component references rather than copying components. Reviewers can compare the draft with its approved upstream using Diff vs upstream. Public approved direct forks appear on the source's Forks tab; private forks and unpublished drafts do not. Fork and customize guide.
| Registry fork API | Action |
|---|---|
POST /api/v1/agents/{id}/fork |
Create an agent draft from an approved release |
POST /api/v1/{type}/{id}/fork |
Create a component draft (type: mcps, skills, hooks, prompts, sandboxes) |
GET /api/v1/agents/{id}/forks, GET /api/v1/{type}/{id}/forks |
List public approved direct forks |
GET /api/v1/agents/{id}/fork-diff?version=…, GET /api/v1/{type}/{id}/fork-diff?version=… |
Compare a visible fork version to its approved, accessible base |
Discovery and Delegation (ARD + A2A)
ARD: one search across everything approved. Observal implements Agentic Resource Discovery (v0.91). Every approved agent, MCP server, skill, hook, prompt and sandbox is published as an ARD entry with a permanent urn:air: identifier, a public manifest at /.well-known/ard.json, and the spec's search API at /api/v1/ard/search. Results are ranked by relevance only; approval, visibility, harness support and whether the resource can be used right now are separate fields. The same visibility rules as the registry apply, so a team-private agent is only found by that team.
A2A: agents hand tasks to agents. Observal speaks the Agent2Agent protocol (v1.0, with v0.3 compatibility). Every delegation is an A2A Task, whoever runs it:
- Registry agents run headless in a harness that supports it (Claude Code, Kiro, Cursor, Codex, OpenCode, Copilot CLI, Antigravity, Pi) inside a throwaway copy of your repository. Their answer comes back as a result, and any file changes come back as a patch that is never applied for you.
- Remote A2A agents (a service another team runs, built with any framework) are registered by their Agent Card URL, reviewed like any submission, and then called directly with the card the reviewer approved. Observal never proxies the traffic or stores their credentials.
flowchart LR
    A["Agent in your harness"] -- "find_agents" --> R["Observal registry<br/>(ARD search)"]
    A -- "delegate" --> T{"A2A Task"}
    T -- "registry agent" --> H["Headless harness<br/>in a throwaway copy"]
    T -- "remote agent" --> S["A2A service<br/>(approved Agent Card)"]
    H -- "answer + patch" --> A
    S -- "artifacts" --> A
Every agent you pull gets an observal-agents MCP server with four tools, find_agents, delegate, get_task and cancel_task, so it can do this without being told how. Delegation is limited to approved agents, stops after two levels, lets a delegated agent start at most three tasks of its own, and refuses loops. Each delegation is recorded against the calling session, so traces show which agents a session relied on.
Discover shows registry agents that can take a task and remote A2A agents side by side:

Delegate from any terminal or script. Here a remote A2A agent answers directly; a registry agent also hands back its file changes as a patch for you to review:

observal delegate find "review this branch for auth bugs"
observal delegate run acme/security-reviewer "Review src/auth on this branch for token leaks"
git apply ~/.observal/delegations/<task-id>/changes.patch     # only if you agree with it

observal registry a2a submit https://agents.acme.com --visibility team --team platform
observal discover inspect urn:air:agents.acme.com:a2a:incident-triage     # shows the card's Digest
observal registry a2a review urn:air:agents.acme.com:a2a:incident-triage --approve --digest sha256:...
Design decisions: ADR 0001 (ARD), ADR 0002 (A2A delegation). API: Discovery endpoints.
Coding Agent Insights
AI-powered insight reports analyze usage patterns across all sessions, what's working, what's hindering, and quick wins. Powered by LiteLLM, works with any provider (Anthropic, OpenAI, Bedrock, Gemini, Azure, Ollama).

See Insights LLM Setup for configuration.
Session Replay
Full session overview with token counts, models, tools, and turn-by-turn timeline:

Every turn captured: user prompt, tool calls, thinking block, assistant response:

Drill into any span to see exact tool inputs and outputs:

Review and Governance
Authors submit agent and component versions for review. Participants can inspect the submitted revision's redacted files and diffs, discuss changes in conversations, and submit approvals or change requests. Publishing is separate from approval: once the review policy and required checks are satisfied, a reviewer can publish the version, or policy can publish it automatically.
Open-source features
Audit logs, SAML SSO, SCIM provisioning, and the executive dashboard are included in the Apache-2.0 distribution.
Audit log with filter syntax (actor:, action:, outcome:, sensitivity:) and CSV export:

Documentation
Full docs at docs.observal.io.
Start here for deployment and operations:
| Need | Link |
|---|---|
| Fast local or source setup | SETUP.md |
| Self-hosting overview | docs/self-hosting/README.md |
| Production deployment | docs/self-hosting/production-deploy.md |
| Single-node deployment | docs/self-hosting/single-node-deploy.md |
| Docker Compose setup | docs/self-hosting/docker-compose.md |
| Databases and migrations | docs/self-hosting/databases.md |
| Upgrades | docs/self-hosting/upgrades.md |
| Backup and restore | docs/self-hosting/backup-and-restore.md |
Tech Stack
| Layer | Technology |
|---|---|
| Frontend | Vite 8, React 19, TanStack Router, Tailwind CSS 4, shadcn/ui |
| Backend | Python 3.11+, FastAPI, Strawberry GraphQL |
| Databases | PostgreSQL 16 (registry), ClickHouse (telemetry) |
| Queue | Redis + arq |
| CLI | Python, Typer, Rich |
| Telemetry | Session hooks, local transcript reconciliation, push-based ingest |
| Deployment | Docker Compose (10 services), Kubernetes (Helm) |
Contributing
See CONTRIBUTING.md. The short version:
- Fork and clone
make hooksto install pre-commit hooks- Create a feature branch
- Run
make lintandmake test - Open a PR
See AGENTS.md for internal codebase context.
Community
GitHub Discussions for questions and ideas. Discord for chat. Open Issues for confirmed bugs.
Reporting Issues
observal doctor support bundle
Produces a redacted diagnostic archive. Review before sharing: observal doctor support inspect observal-support-*.tar.gz
For live debugging, Observal uses loguru-based dev logging (internally called "optic"). Stream logs with:
observal ops logs
Logs are written to ~/.observal/logs/dev.log and include structured context for every request, background job, and telemetry event.
Security
Report vulnerabilities via GitHub Private Vulnerability Reporting or email contact@observal.io. Do not open a public issue. See SECURITY.md.
License
Observal is licensed under the Apache License 2.0. See LICENSE.
1 maintainer

Metadata
1 maintainer
Release files for observal-cli 1.15.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| observal_cli-1.15.0.tar.gz | 9.5 MB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| observal_cli-1.15.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 10.3 MB
Release files / observal_cli-1.15.0.tar.gz
| Download URL | observal_cli-1.15.0.tar.gz |
|---|---|
| Size | 9.5 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
fac09a4df4495ff08d324adbaa9d915cb33ae5f455ba9db3b0f758e7652cb852
|
|
BLAKE2b-256 checksum How to use checksums |
d0775cfd2db975354b65aca46ab5a5df3967d9647d5c58ac46325591d8edc6a7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 13, 2026.
Transparency logRelease files / observal_cli-1.15.0-py3-none-any.whl
| Download URL | observal_cli-1.15.0-py3-none-any.whl |
|---|---|
| Size | 734.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
f493821dfdc6adb498eed658ce84760785a68805053136c0b21cb58bfbcc08ed
|
|
BLAKE2b-256 checksum How to use checksums |
2bec9388fea355fb9bdb3395d21ff5701d24975c9b578034b9ed1e9752032991
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 13, 2026.
Transparency log













