
Offenders — Fail2Ban investigation and diagnostics TUI



Offenders is a terminal-first investigation and diagnostics tool for Fail2Ban.
Combine historical ban activity with current jail state, investigate IPs and jails,
and explore IP/ASN/Country summaries over SSH or in a local Linux terminal.
Use explicit Registration/RDNS lookups, optional GeoIP, manual Coverage and
validation, CSV Export, and global contextual ? Help.
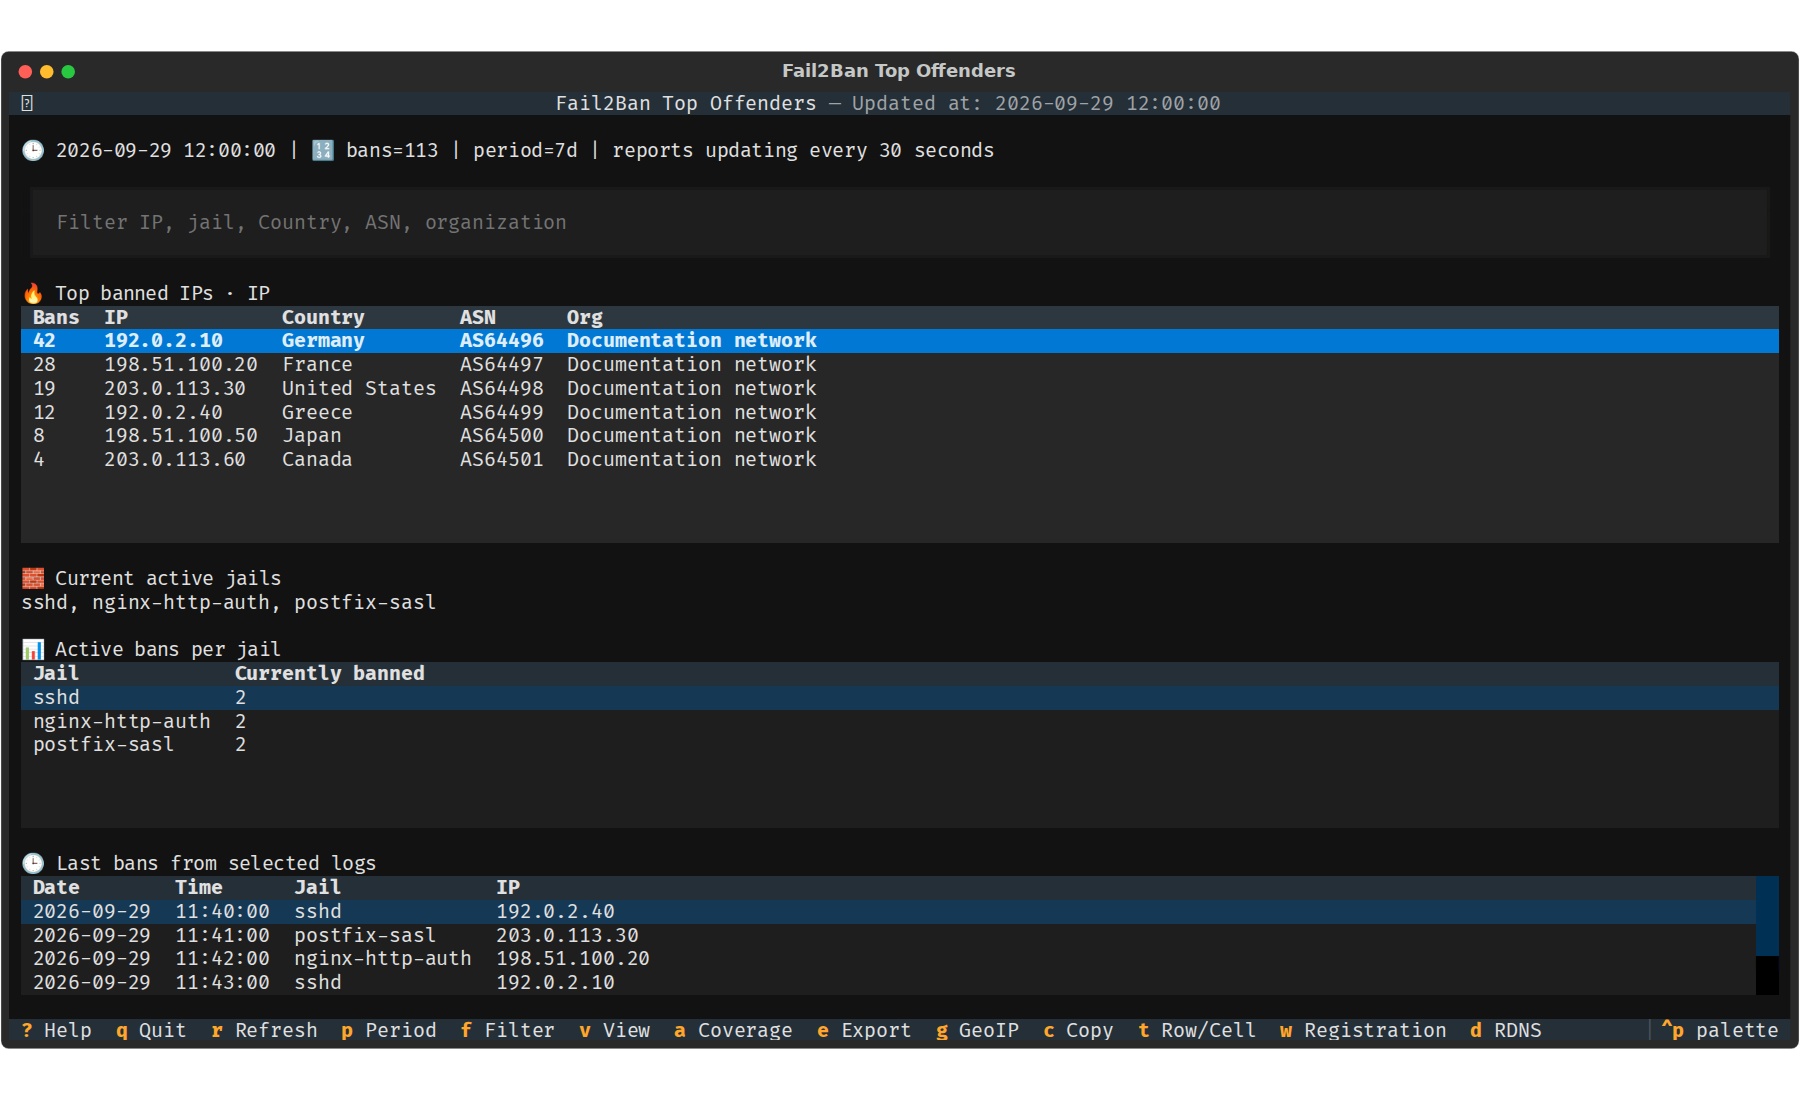
Current Offenders dashboard using synthetic documentation data.
- Export a committed report with
e, or acquire one fresh CSV bundle withoffenders export --period 30d(see Usage). - Press
? Helpfrom any product screen for contextual controls and a concise in-app guide;Esc/qreturns to your place. - Explore rolling history periods, live jail status, and IP/ASN/Country summaries.
- Filter loaded results and investigate individual jails and IPs.
- Review Coverage evidence and explicitly validate copy-only filter candidates.
- Open manual
n Enforcementto compare fresh current bans with supported nftables, iptables or UFW rule evidence; direct observation is not packet or reachability proof (see Usage).
Reports and investigation are read-only with respect to Fail2Ban configuration and bans. There is no ban/unban action or automatic Fail2Ban mutation. Coverage never installs filters/jails or enables/reloads Fail2Ban. Persistent application changes are limited to explicit or opt-in GeoIP data/policy under your XDG data root; validation also uses temporary local sample files.
Quick start
Supported baseline: Ubuntu 24.04 / Python >=3.12 / Fail2Ban 1.0.2. Qualified stock Enforcement action versions: 1.0.2, 1.1.0 and 1.1.1; support remains limited to recognized runtime shapes and fails closed. Fail2Ban, readable logs, and narrowly scoped noninteractive sudo permissions must be supplied separately; see installation and permissions.
Install from PyPI and run:
pipx install offenders
offenders
Run offenders --help (or -h) to discover commands and their option help;
offenders --version (or -V) reports the installed version. These standalone
forms exit without launching the TUI or acquiring data.
GeoIP enrichment is optional. Installation downloads no databases; an explicit update fetches DB-IP Lite, and automatic updates require opt-in. See the GeoIP guide for lifecycle and attribution. Coverage analysis and validation are explicit, manual, and copy-only; a sample match never establishes filter safety. See Coverage.
Documentation
Operator documentation · PyPI · Releases · Changelog · Development · MIT license
1 maintainer

Metadata
1 maintainer
Release files for offenders 0.4.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| offenders-0.4.0.tar.gz | 203.6 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| offenders-0.4.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 329.8 kB
Release files / offenders-0.4.0.tar.gz
| Download URL | offenders-0.4.0.tar.gz |
|---|---|
| Size | 203.6 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
3703af195fe3da0f9673e98c652957e336133e4d4418e29f3bb4c8ee81d86a0c
|
|
BLAKE2b-256 checksum How to use checksums |
da8aef7956c63a8c27e358994d10cbbd327acf3b22d7fa1f4abff63c72f6789a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 30, 2026.
Transparency logRelease files / offenders-0.4.0-py3-none-any.whl
| Download URL | offenders-0.4.0-py3-none-any.whl |
|---|---|
| Size | 126.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
9c587f541684b932a2b5dc6a5217db696ee430933eef04c7244735bd108ba005
|
|
BLAKE2b-256 checksum How to use checksums |
56430cda555009ddbd95e92a35e7fae1284c46550eb69ac9241b4d2344be7c95
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 30, 2026.
Transparency log













